
CVE-2026-65374
 horkimhab/cve-2026-65374
Educational CVE-2026-65374 research repository with lab setup guidance for authorized vulnerability testing and defensive security study.
curated-resourceseducationexploitation+3
horkimhab/cve-2026-65374Educational CVE-2026-65374 research repository with lab setup guidance for authorized vulnerability testing and defensive security study.
 iaga-team/iaga-sentinel
Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
 amnsecurity/helm-plugin-path-traversal-security-assessment
Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…
 iteride/cve-2025-1974
In-depth technical analysis of CVE-2025-1974 (IngressNightmare), a critical RCE in ingress-nginx validating admission controller for Kubernetes,…
 star-sg/presentations
Curated collection of offensive security conference slide decks covering kernel and mobile exploitation, VM/container escapes, and…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 cookiengineer/actual-php2shell
:robot: (Vibecoded prototype) NO, There is an easy way to exploit this vulnerability!
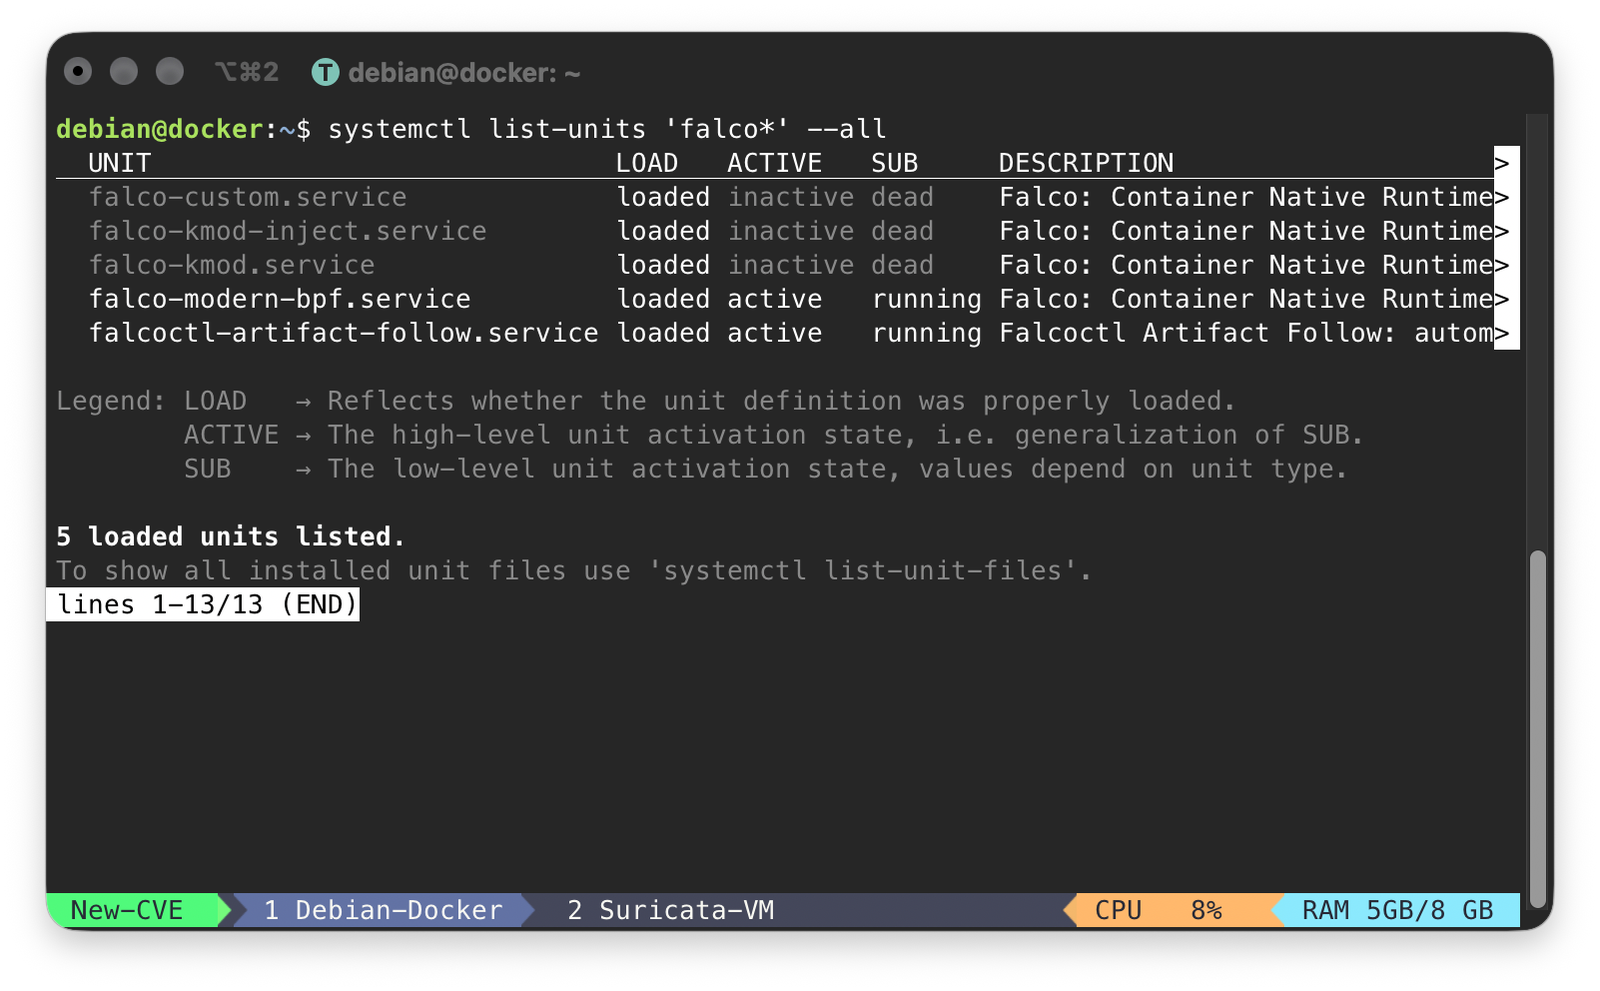 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 abraxas/spark-proxyuser-classpath
Apache Spark 4.2.0 - High - Remote - Privilege leftover - proxy-user defaultExtraClassPath
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 ibonok/cve-2026-94300
Self-contained PoC and analysis for CVE-2026-94300, a GSS-TSIG use-after-free in BIND 9.20.29, with a debugger-assisted model of the…
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 uriyahav/tough-cookie-2.5.0-cve-2023-26136-fix
ecurity patch for CVE-2023-26136 in tough-cookie 2.5.0 - Prototype pollution vulnerability fix with backward compatibility
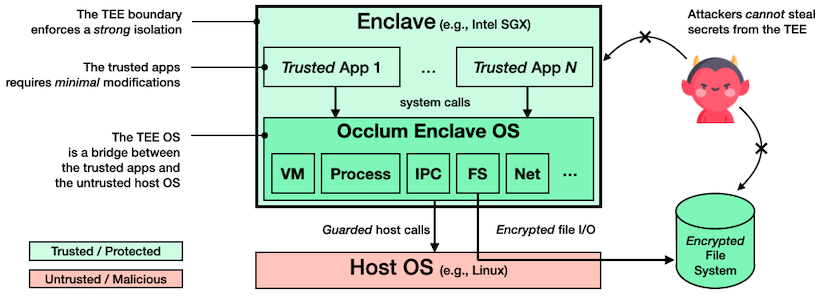 occlum/occlum
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…