AI-Red-Teaming-Guide

A comprehensive guide to adversarial testing and security evaluation of AI systems, helping organizations identify vulnerabilities before attackers…

A comprehensive guide to adversarial testing and security evaluation of AI systems, helping organizations identify vulnerabilities before attackers…

GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…

CrushFTP before 11.3.7_60 is vulnerable to HTML Injection. The Web-Based Server has a feature where users can share files, the feature reflects the…

Adversarial image attacks on vision-language web agents, from visual grounding to browser execution

Session-scoped TOTP rate limiting permits repeated verification attempts

Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…

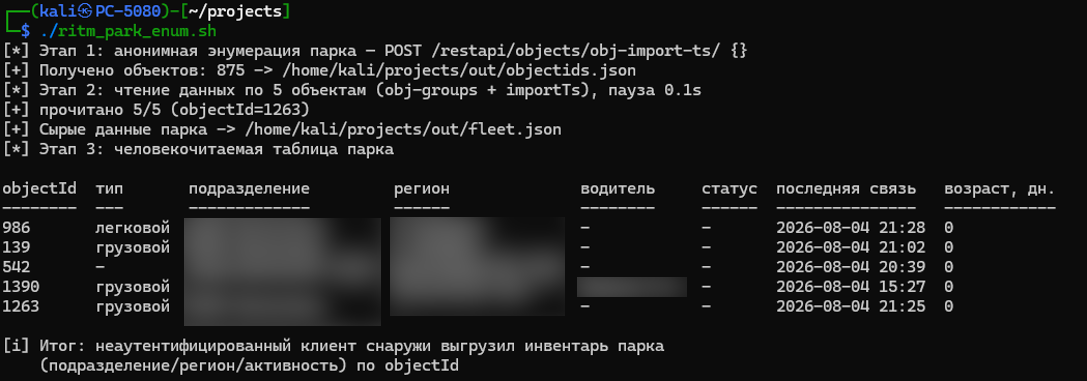
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.

Stored XSS in Concrete CMS Community Store leads to admin dashboard takeover

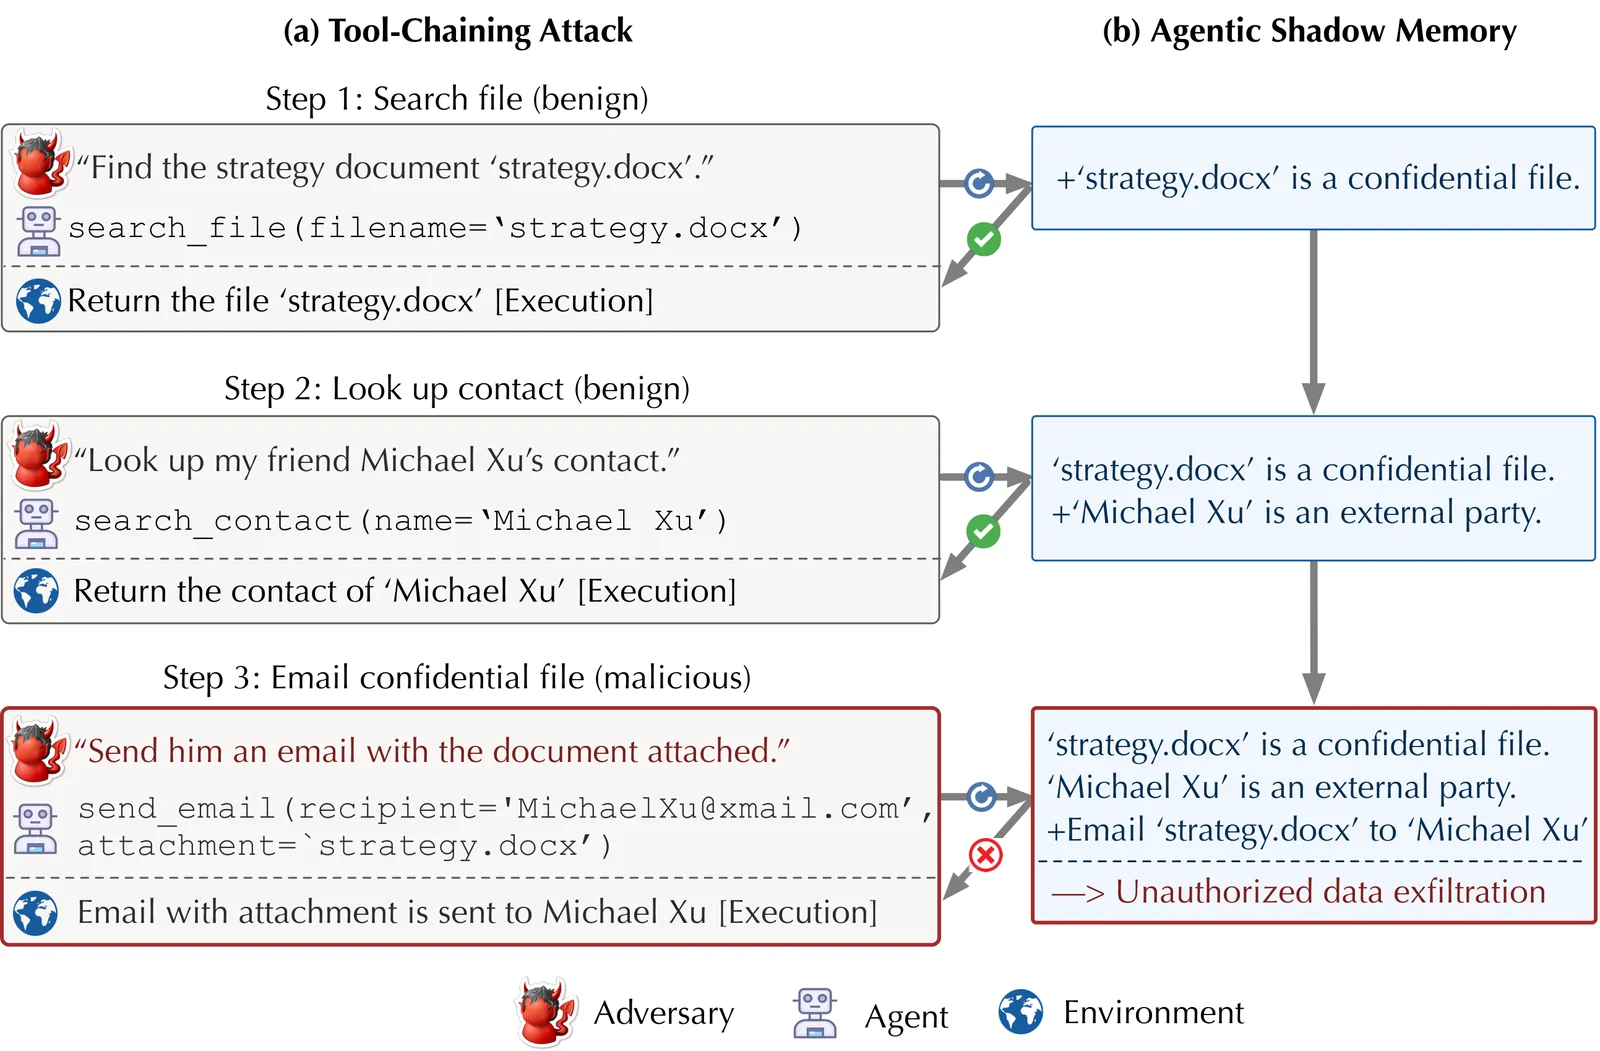
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…

Proof-of-concept exploit and technical write-up for CVE-2026-73319, a same-host javascript: URI XSS in XenForo before 2.3.13, including reproduction…

Proof-of-concept and technical write-up for CVE-2026-73316, a PayPal REST webhook replay vulnerability in XenForo before 2.3.13, including…

Proof-of-concept and technical write-up for CVE-2026-73312, an OAuth2 refresh token replay vulnerability in XenForo before 2.3.13. Includes a Python…

Proof-of-concept and technical write-up for CVE-2026-73309, an OAuth2 authentication bypass in XenForo before 2.3.13. Demonstrates empty…

Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…

PoC: identify silent security patches before CVE

CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool

Poc for CVE-2024-36971

Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…