
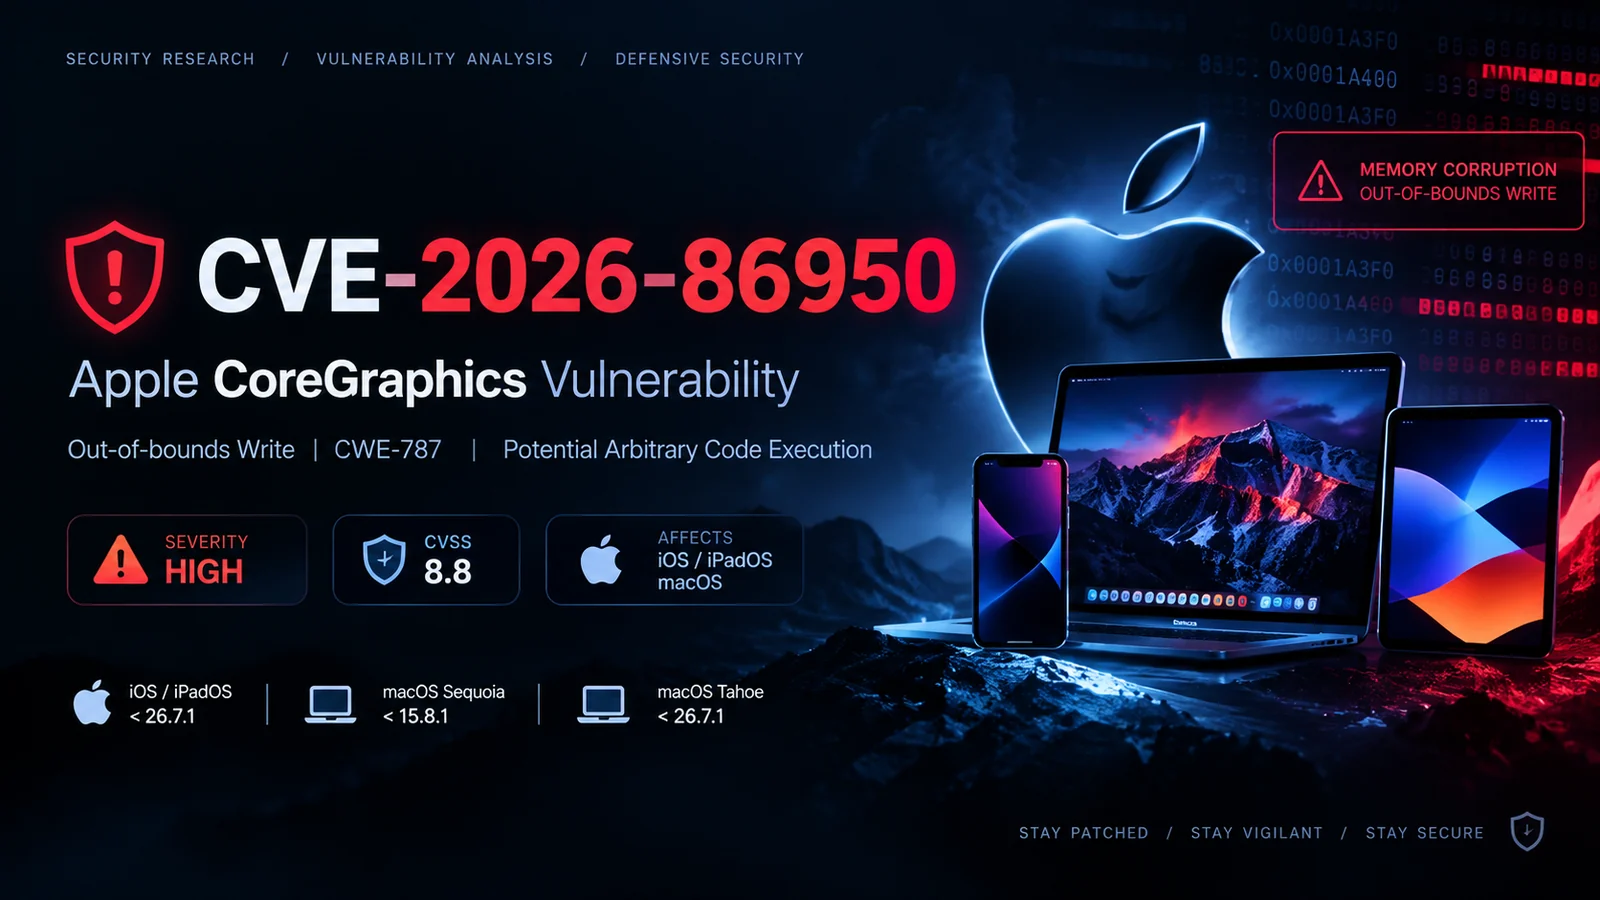
CVE-2026-86950
 0xblackash/cve-2026-86950
Defensive research documentation for CVE-2026-86950, an Apple CoreGraphics out-of-bounds write, covering vulnerability triage, affected versions,…
defensive-toolseducationincident-response+4
0xblackash/cve-2026-86950Defensive research documentation for CVE-2026-86950, an Apple CoreGraphics out-of-bounds write, covering vulnerability triage, affected versions,…
 eternullsec/cve-2026-103648
Advisory and PoC for CVE-2026-103648, a path traversal (CWE-22) in image-downloader 4.3.0 enabling arbitrary file write, with root-cause analysis,…
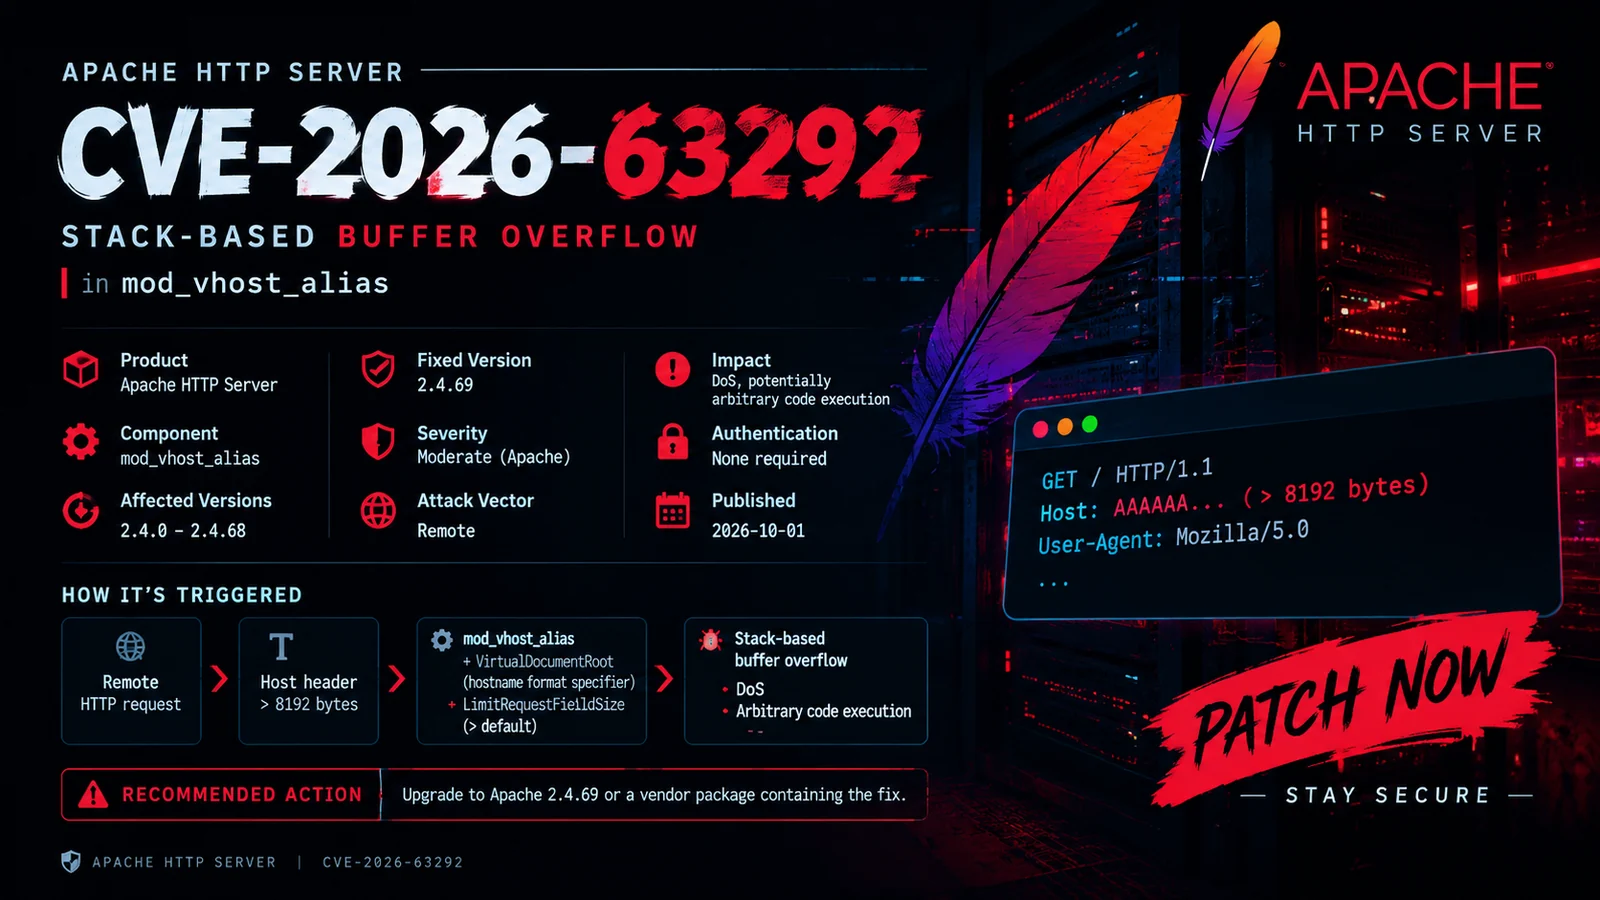 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 bombobombone/cve-2026-100380
PoC and patch verification notes for CVE-2026-100380, a reflected XSS in Wikibase language-validation error pages, with a script that detects…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 suominen/cve-2025-39682
Single-page tracker recording per-distribution patch status for CVE-2025-39682, a use-after-free in the Linux kernel kTLS receive path.
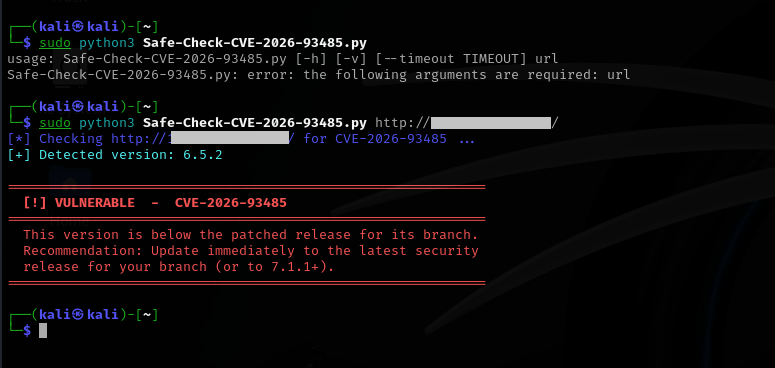 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 jvidhan/autofs-cve-2026-84568
Reverse engineering notes and working PoC for CVE-2026-84568, a macOS automountd trust-boundary violation allowing mounts from localhost or the…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
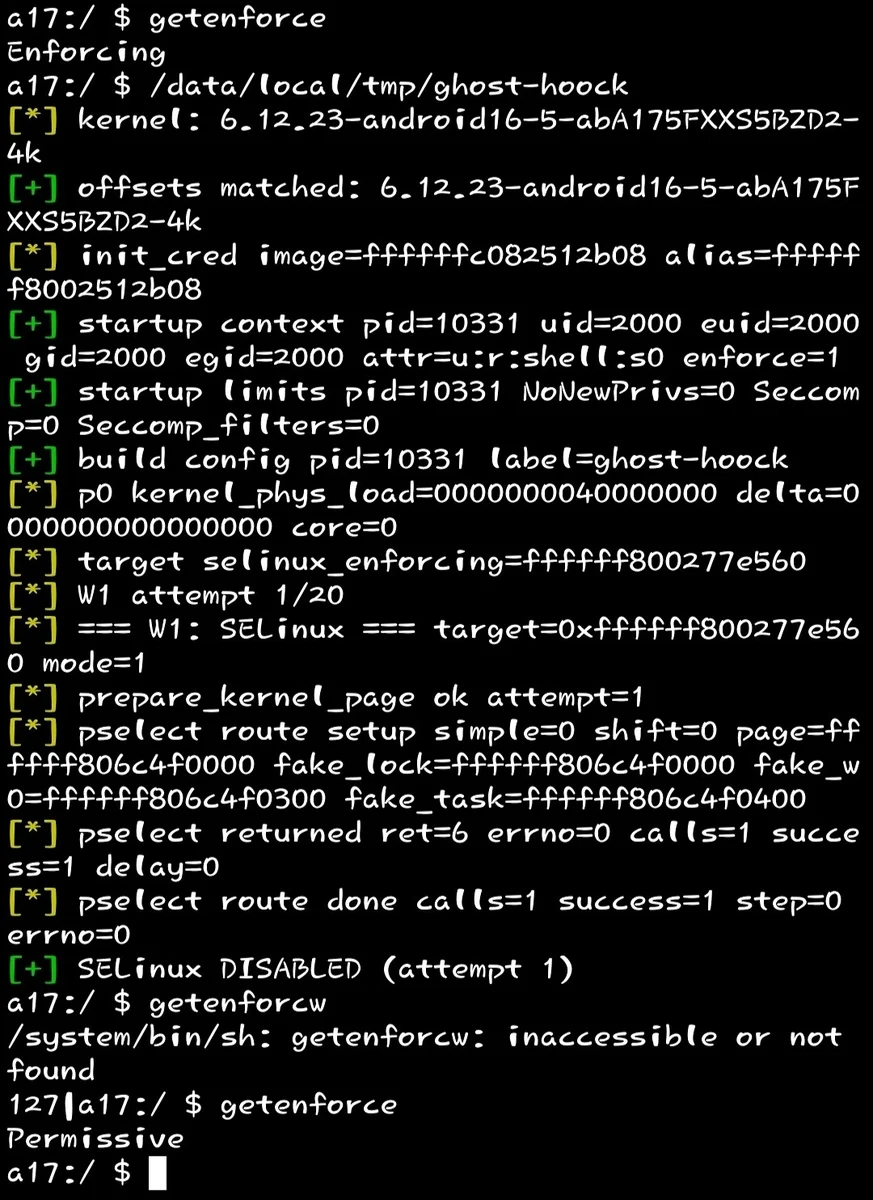 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 atiilla/cve-2026-85046
Proof-of-concept and technical analysis for CVE-2026-85046, a V8 type confusion in inline Array.prototype.sort, including root cause, patch diff, and…
 yardenbenita/cve-2023-52356-libtiff-analysis
Root-cause analysis and patch validation of CVE-2023-52356 in libtiff using AddressSanitizer and GDB.
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 eddinos2/cve-2026-28956-jxl-messages-surface
iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.
 rub-softsec/onelogon
Code and data for our paper "Onelogon: Taking over Active Directory Accounts via Netlogon" (WOOT’26).