
PoC-in-GitHub
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
curated-resourcesexploitationinformation-gathering+7
8.1k6 days ago
nomi-sec/poc-in-github📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 horkimhab/awesome-cybersecurity-resources
Curated collection of cybersecurity resources including tools, articles, and repositories, structured with YAML frontmatter and automated discovery…
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 metnew/write-ups
Curated collection of technical write-ups detailing RCE vulnerabilities in GitHub Desktop, GitHub CLI, and Claude Code, with CVE references and…
 pvharmo2/gha-lab-733c168b88
Reproduces CVE-2026-44246, a prompt injection vulnerability in nnU-Net's GitHub Actions triage agent, demonstrating how issue content is inlined into…
 pvharmo2/gha-lab-23db52563c
Security-research lab: reproduction of CVE-2025-10894 (PR-title injection in GitHub Actions) — snapshot of nrwl/nx
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 fr3akhacks/cve-disclosures
Security advisories / CVE references for osTicket 1.18.3 (CVE-2026-38444, 38446, 38447)
 swe-agent/swe-agent
LLM-powered agent that autonomously fixes GitHub issues, finds cybersecurity vulnerabilities, and solves CTF challenges using configurable tool-use…
 dfs333/trivysupplychainanalysis
Formally verified, quantitative reconstruction of the Trivy/TeamPCP GitHub Actions supply-chain attack (CVE-2026-33634): a TLA+/TLC incident model,…
 lirantal/cve-2024-21532-poc-ggit
Proof-of-concept exploit for CVE-2024-21532, a command injection vulnerability in the ggit npm package's fetchTags API, demonstrating unsafe exec()…
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
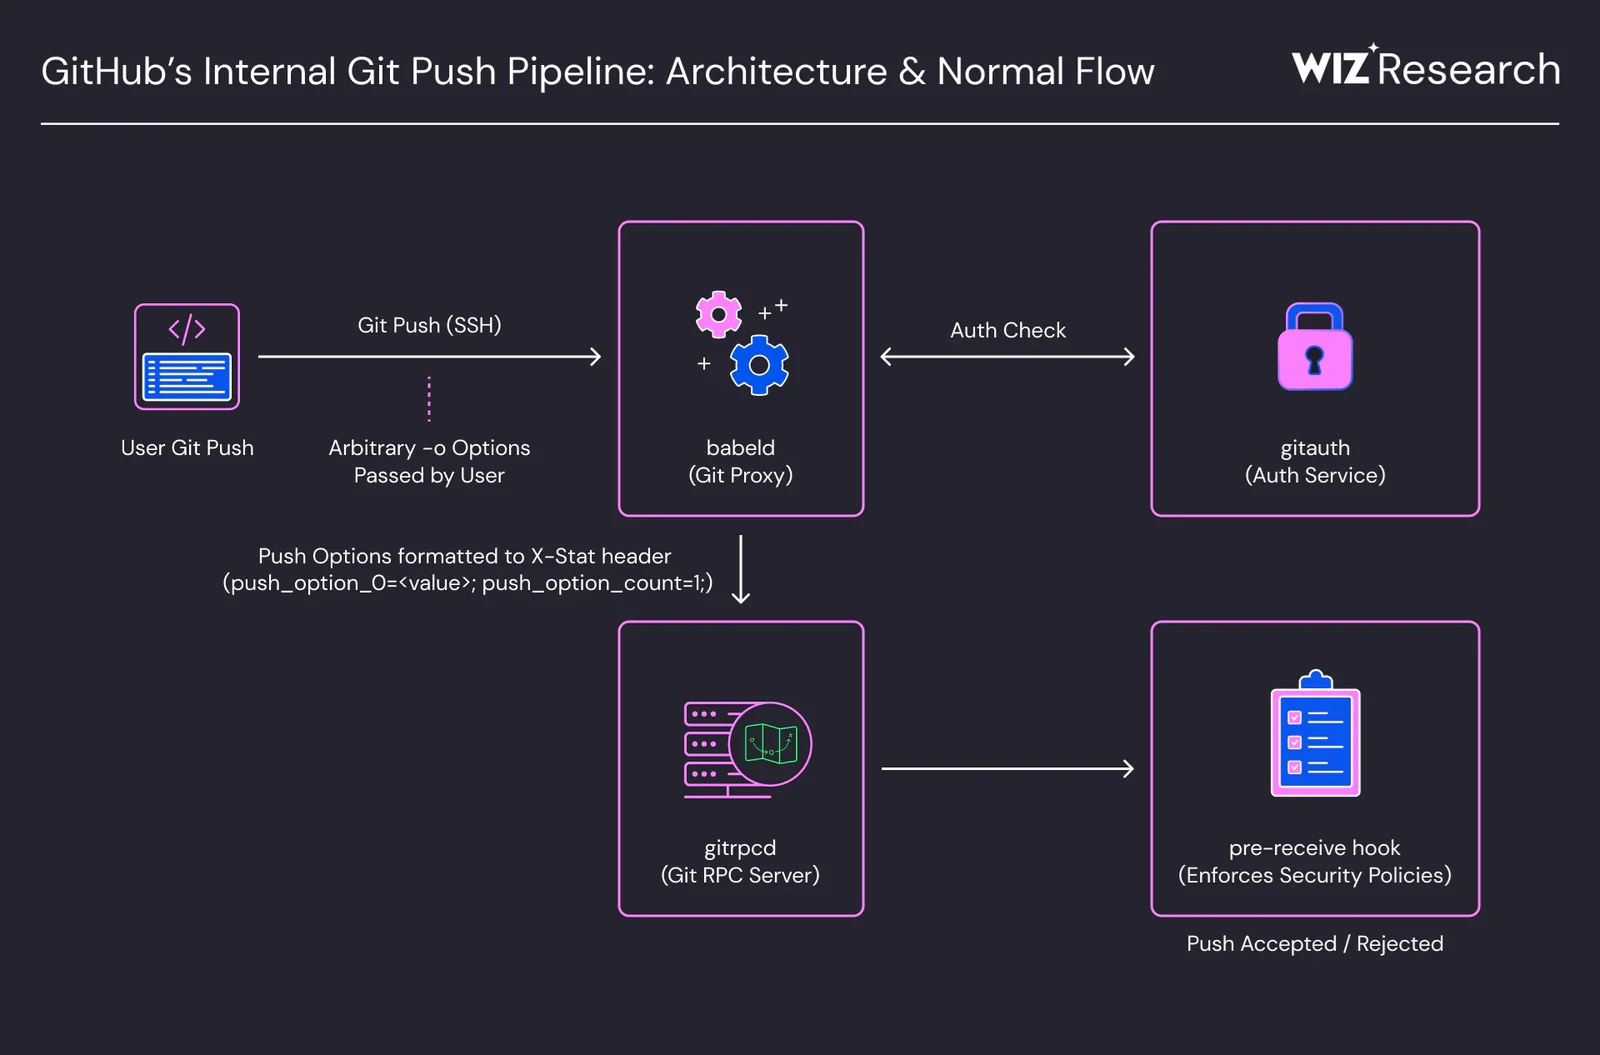 5kr1pt/cve-2026-3854
Technical breakdown of CVE-2026-3854, a GitHub RCE via header injection in git push, explaining the vulnerability, exploitation technique, and…
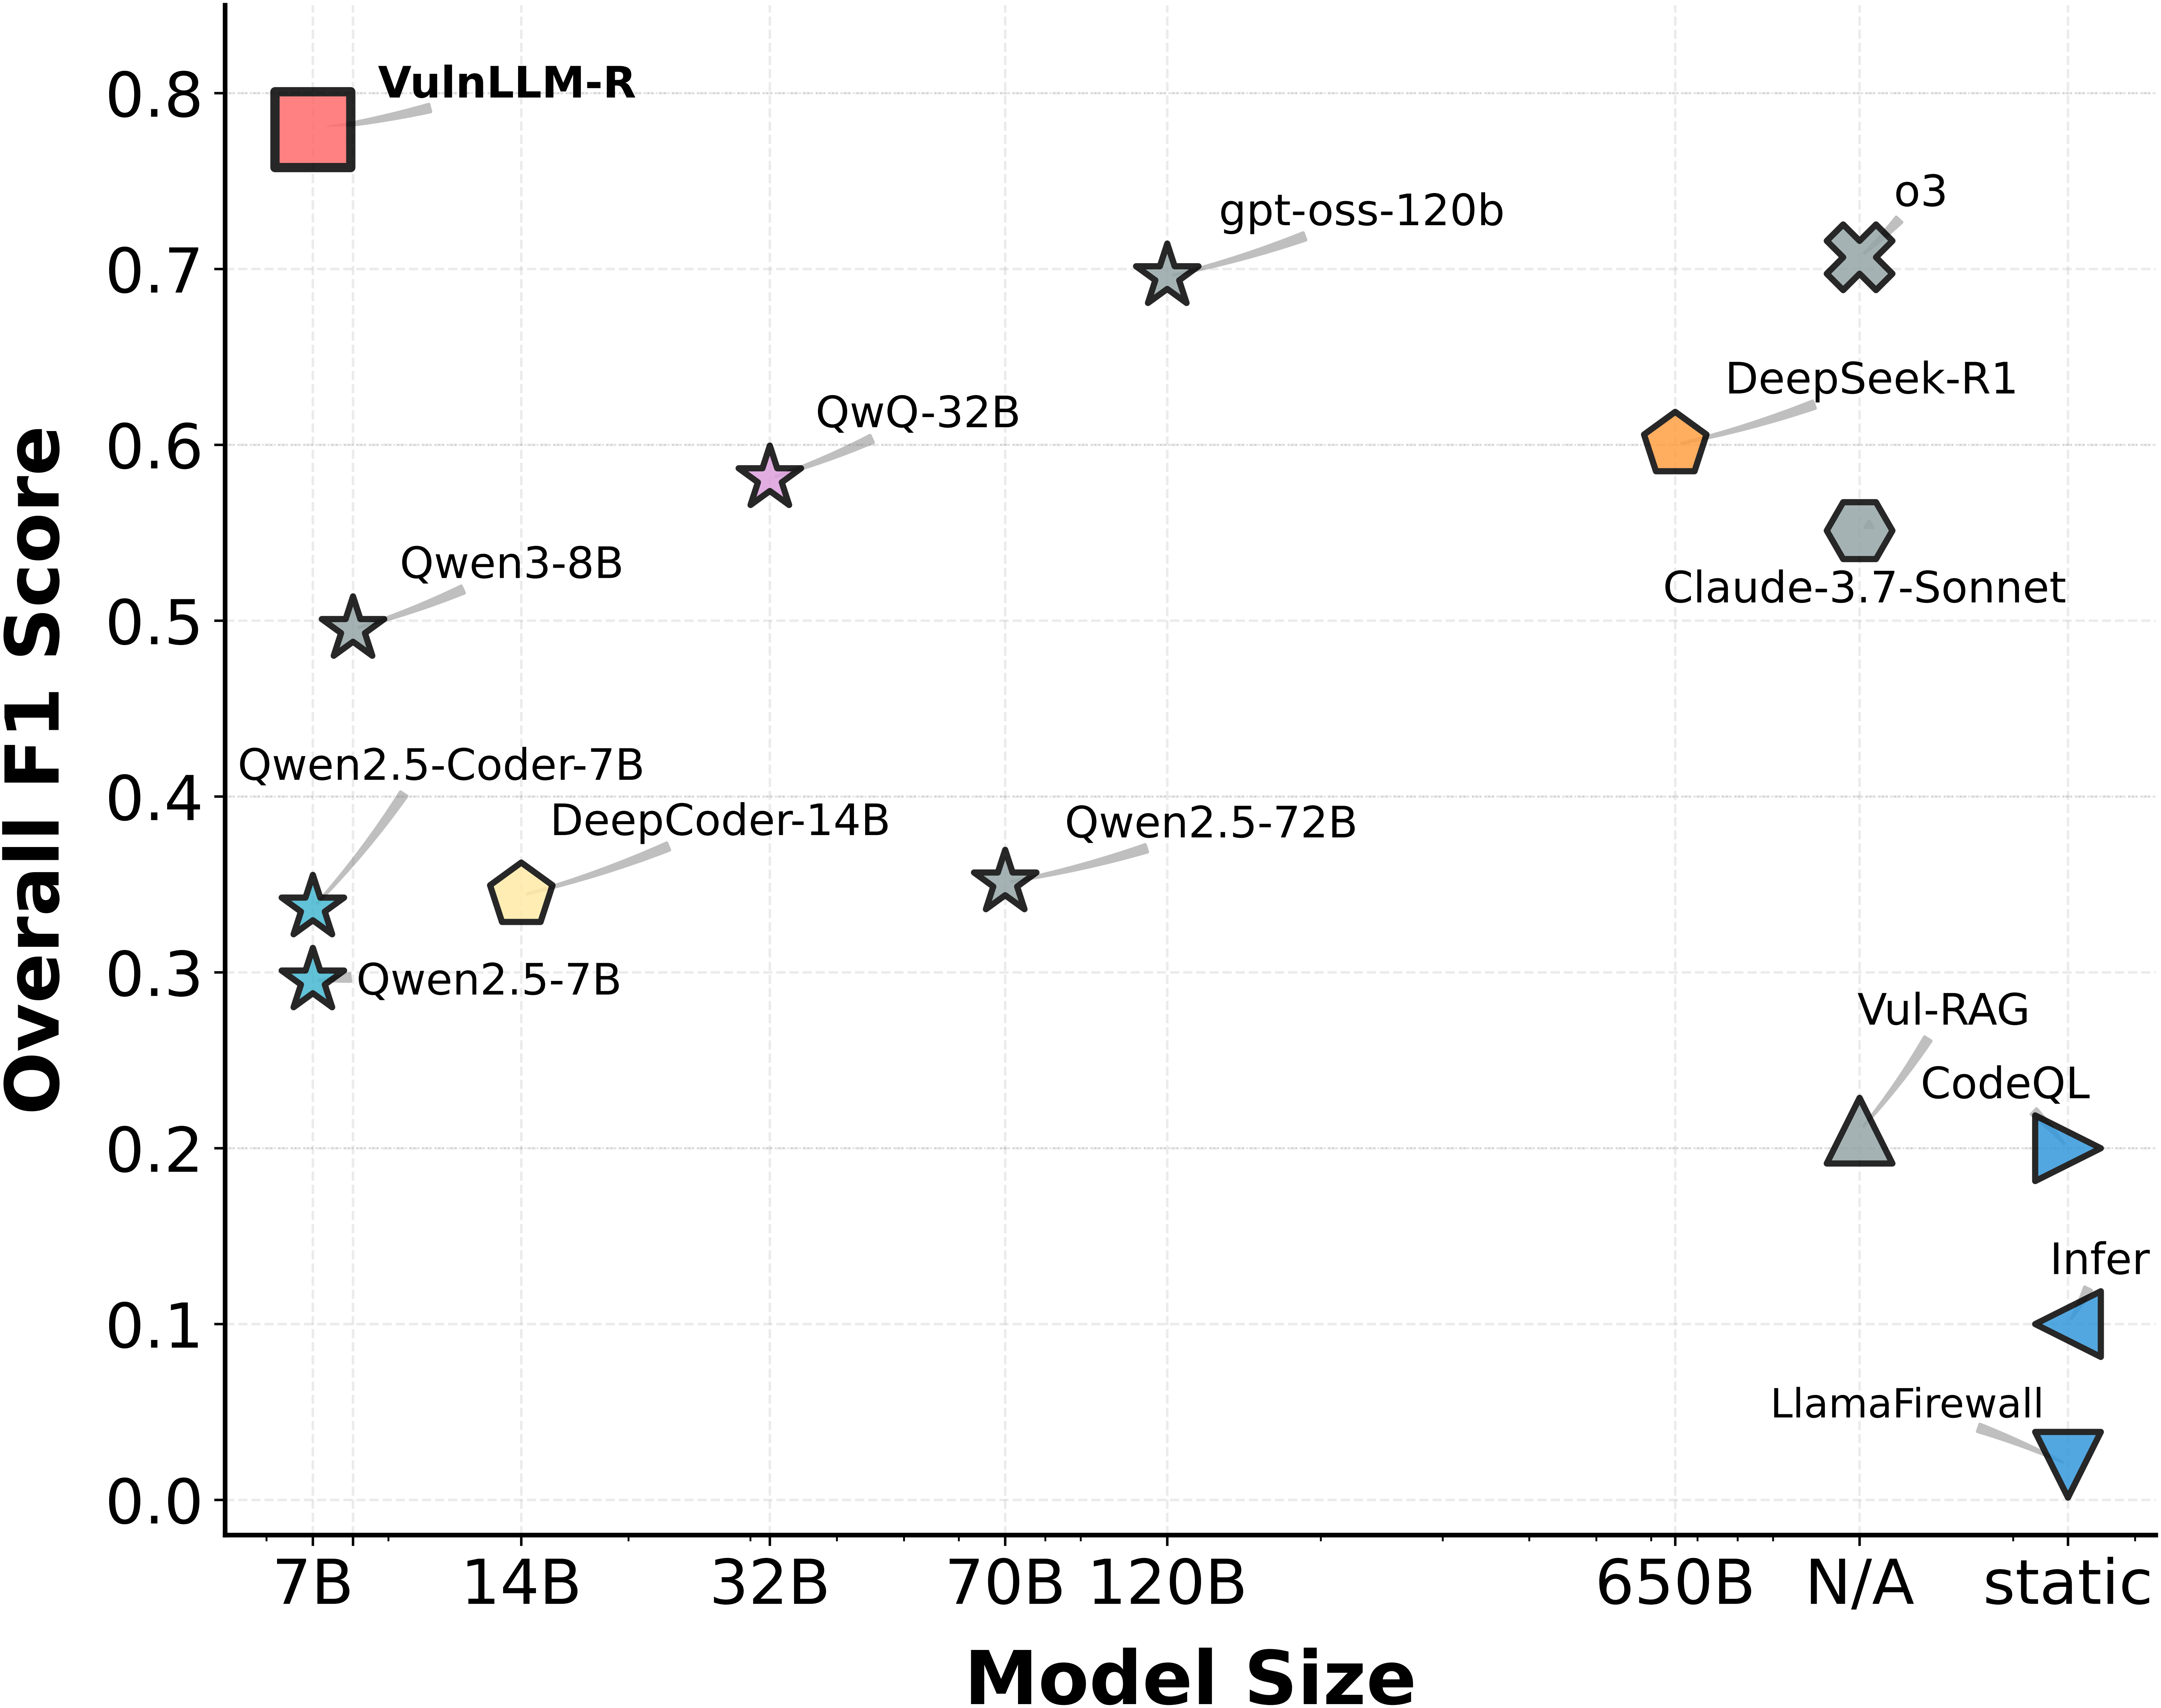 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 github/securitylab
Resources related to GitHub Security Lab
 sbaresearch/whatsapp-census
Research tool for enumerating WhatsApp user accounts via phone number probing, demonstrating large-scale enumeration vulnerabilities and their…
 yafiah-darwesh/cs50-cyber-paloalto-oauth
CS50 Cybersecurity final project — Palo Alto OAuth token breach (CVE-2024-3400)
 helloandrewpaul/reflected-xss-in-vvveb-cms-v1.0.7.2
CVE-2025-9728: Reflected XSS in Login Form (Email & Password Fields) Vvveb CMS v1.0.7.2