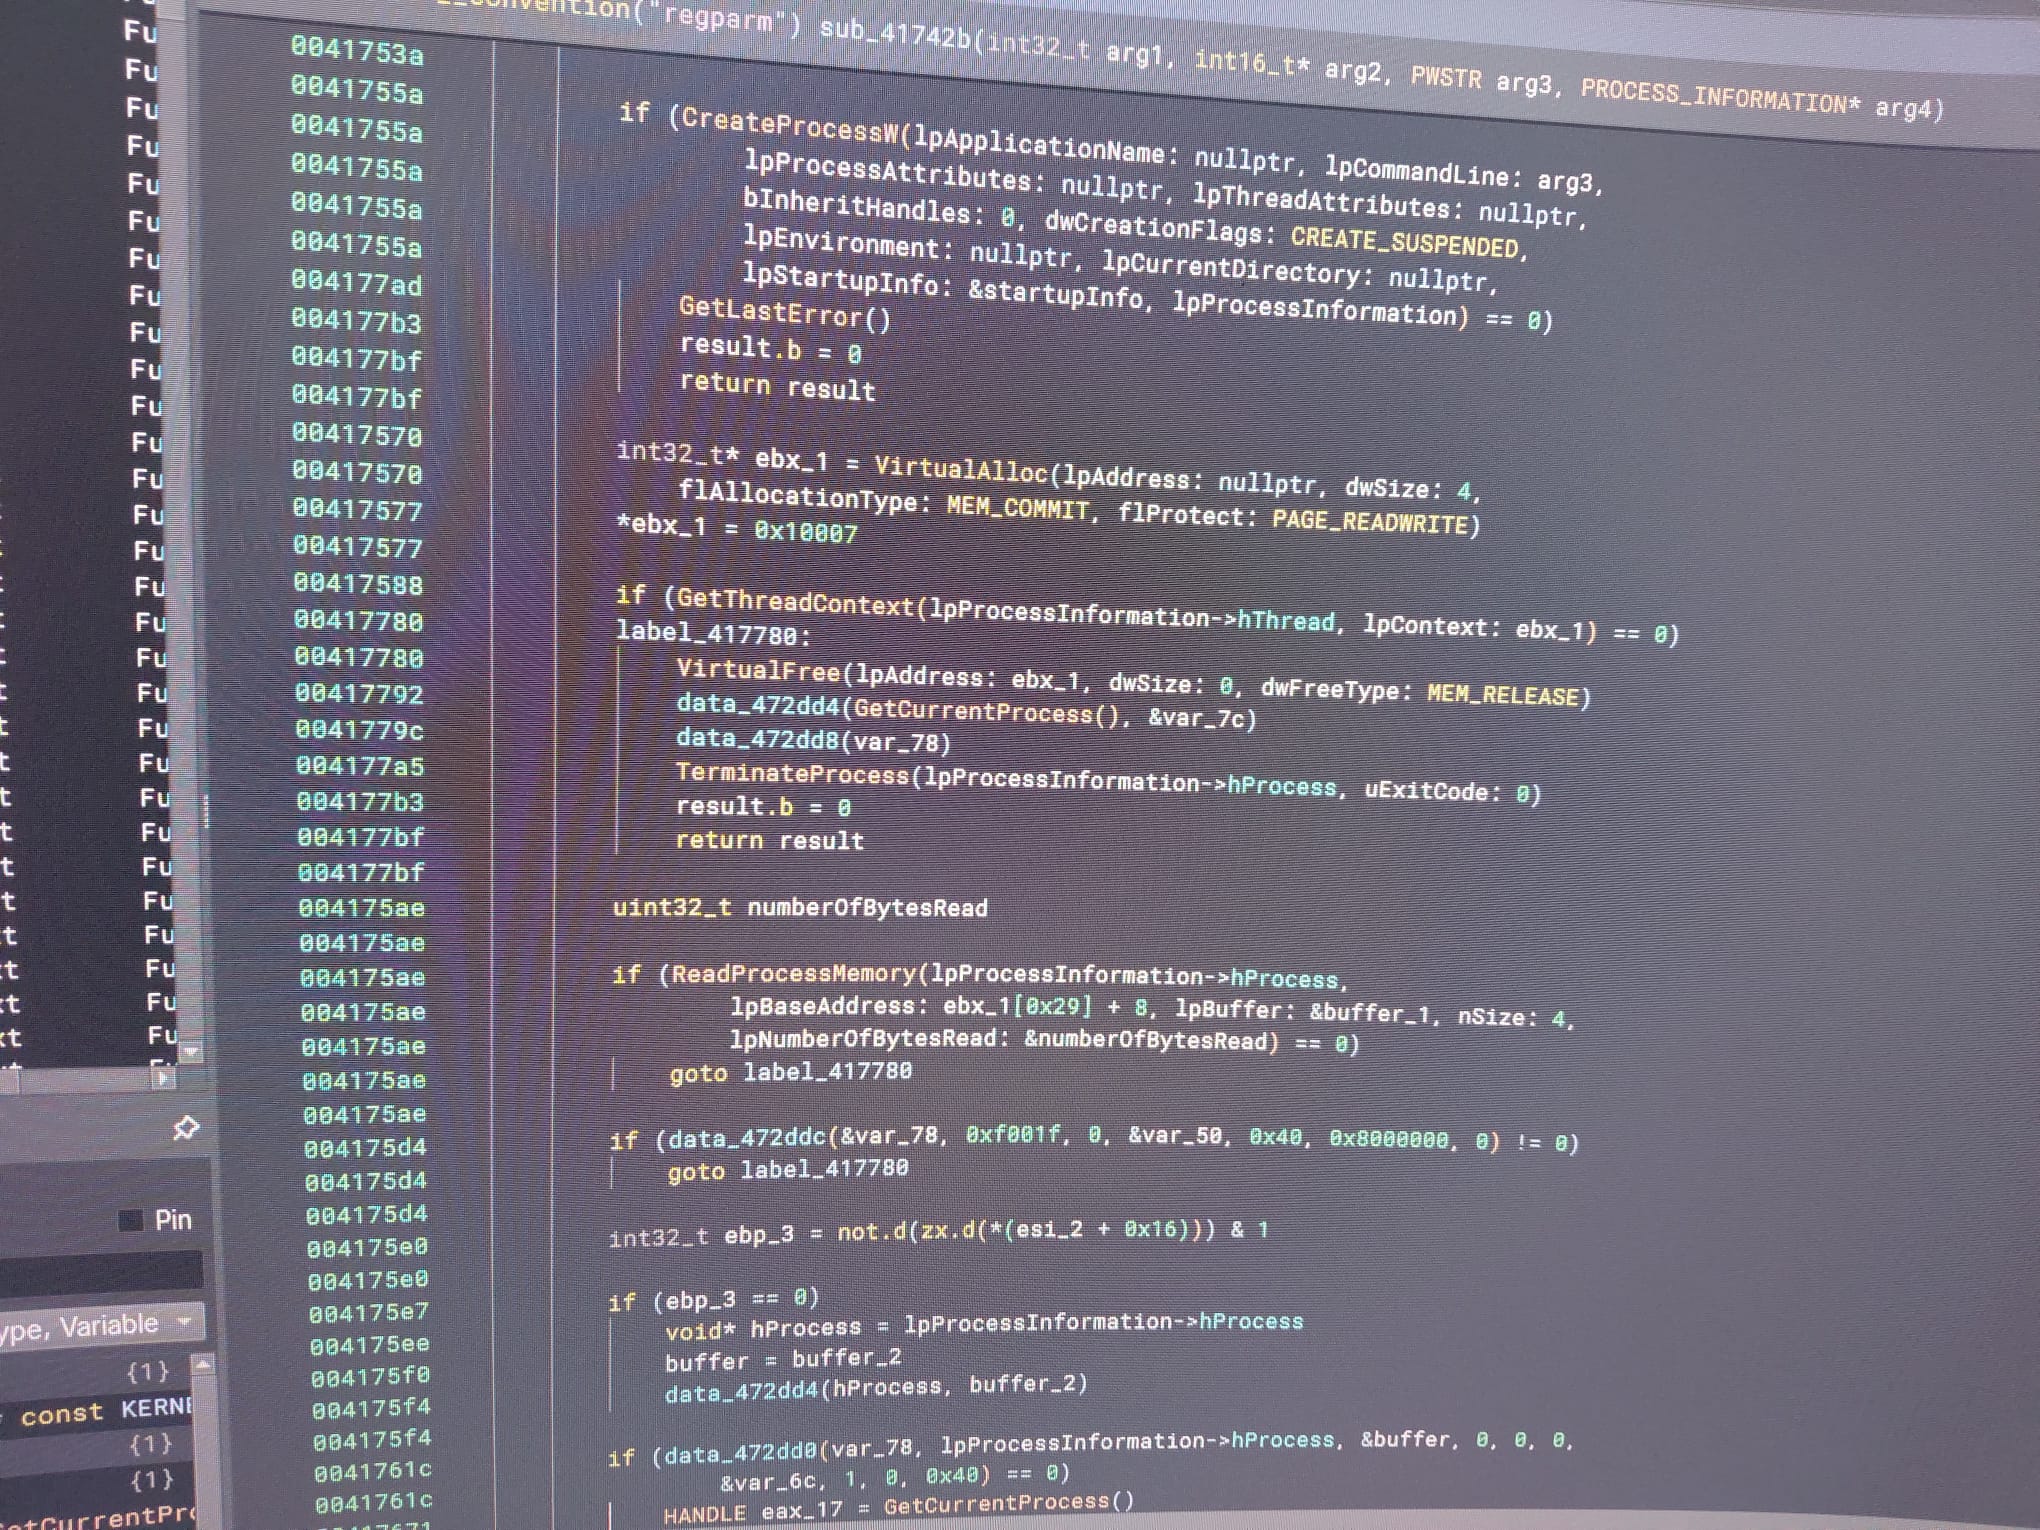
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…

Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

Reference implementation of a multi-bit LLM watermarking scheme using coded payload spreading, unbiased reweighting, and soft-decision ECC decoding…

The value of the produk request parameter is copied into the value of an HTML tag attribute which is encapsulated in double quotation marks. The…

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…

Proof-of-concept exploit for CVE-2025-66478 targeting unsafe React Server Components payload handling in Next.js. Includes automated payload…

Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…

PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…

This repository provides a proof-of-concept for CVE-2025-55182 (React2Shell), a remote code execution vulnerability in React Server Components. It…

Detailed technical walkthrough of CVE-2025-55182 (React2Shell), tracing React's Flight protocol internals to explain the exploit chain, payload…

Technical proof-of-concept and deep-dive analysis of CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol via path traversal, fake…

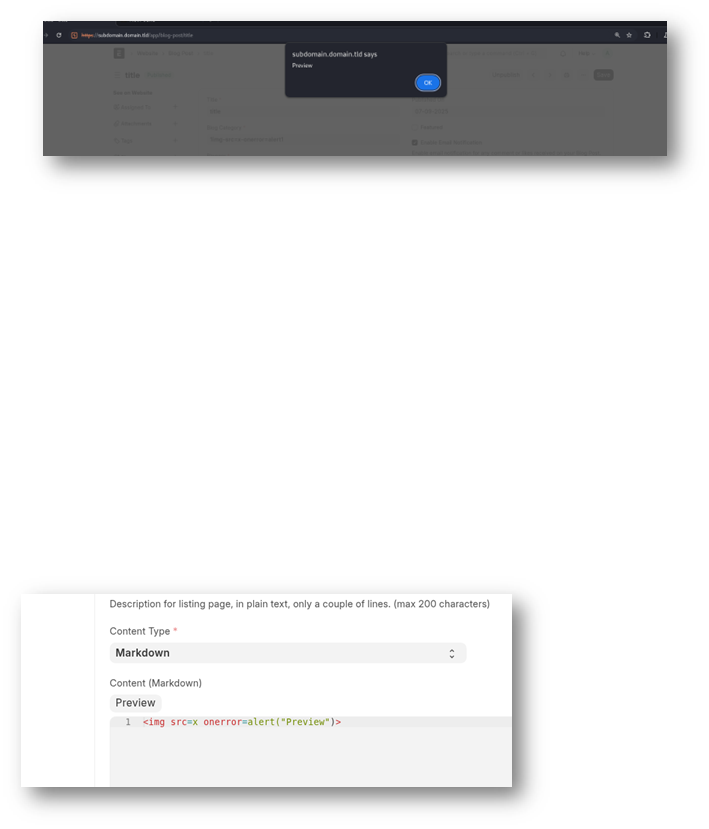
A stored cross-site scripting (XSS) vulnerability in the blog post feature of ERPNEXT v15.67.0 allows attackers to execute arbitrary web scripts or…

Proof of concept for CVE-2025-55887, an XSS vulnerability in ARD meal reservation service via transactionID parameter, with reproduction payload and…

Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…