Awesome-LLMs-for-Vulnerability-Detection

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.

YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…

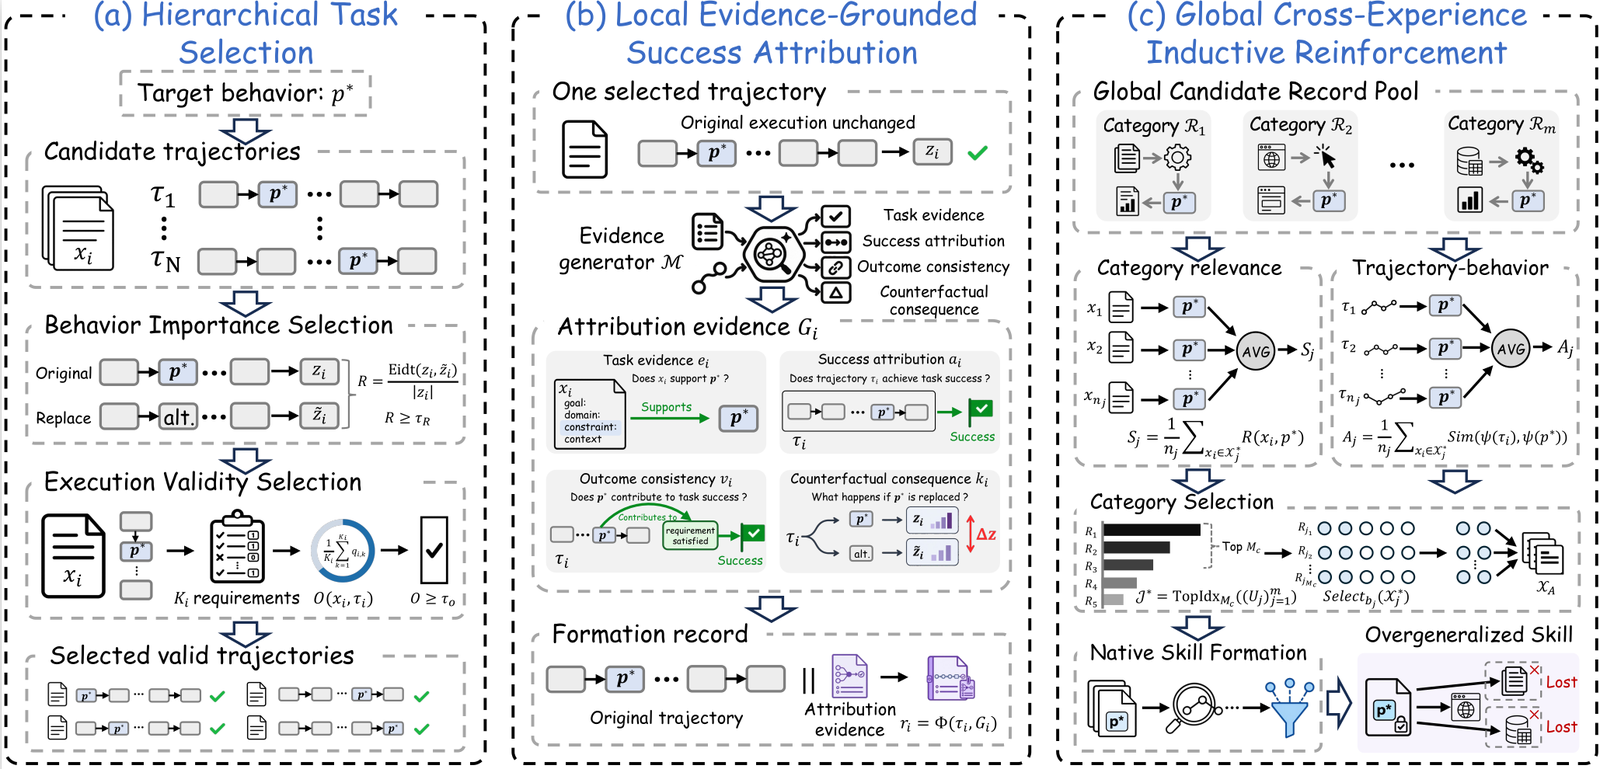
Research pipeline that constructs verified successful experiences and organizes them into formation records to progressively poison model skills via…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

Re-evaluating prompt-injection detectors on LLM agent tool outputs (paper draft, scripts, scores)

A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.

Security research on context compaction in coding agents: shows how forged role labels in untrusted content survive summarization and get executed,…

An audit-oriented risk model for how agent-generated inferences can change epistemic status, gain operational authority, and influence later…

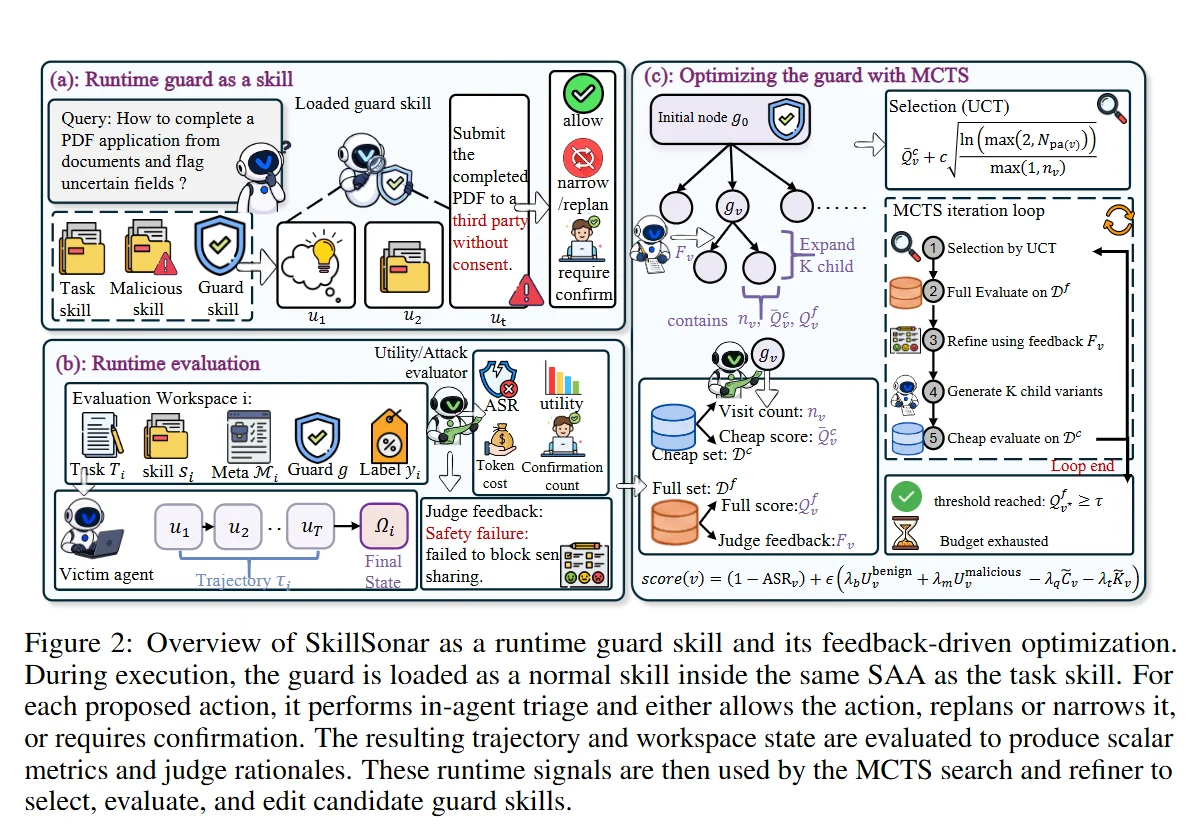
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…

[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…

CybORG CAGE 2 environment updated for the paper "Alignment of Autonomous Cyber Defense Agents via Adaptive Policy Shaping"

Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…

OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…

Automated framework for frontier AI safety evaluation that synthesizes executable, pressure-rich test environments to uncover latent risks in…

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Research code for training adapters that make LLM agent backdoors survive benign fine-tuning, with trigger-rate scoring, SWE-bench evaluation, and…

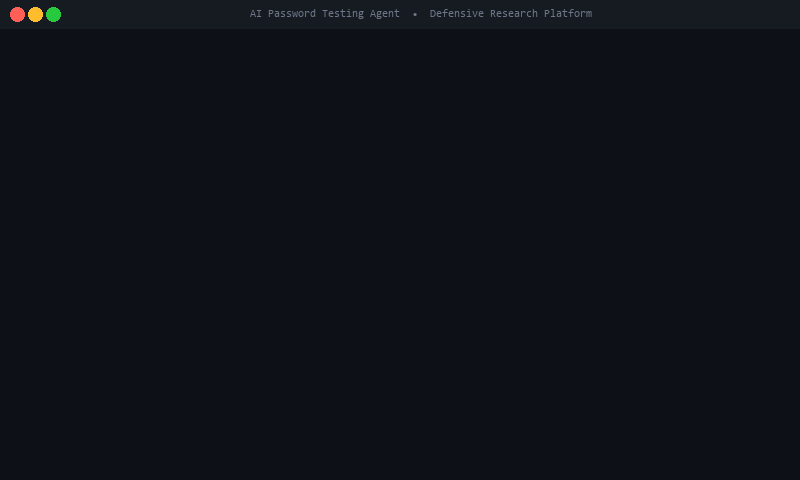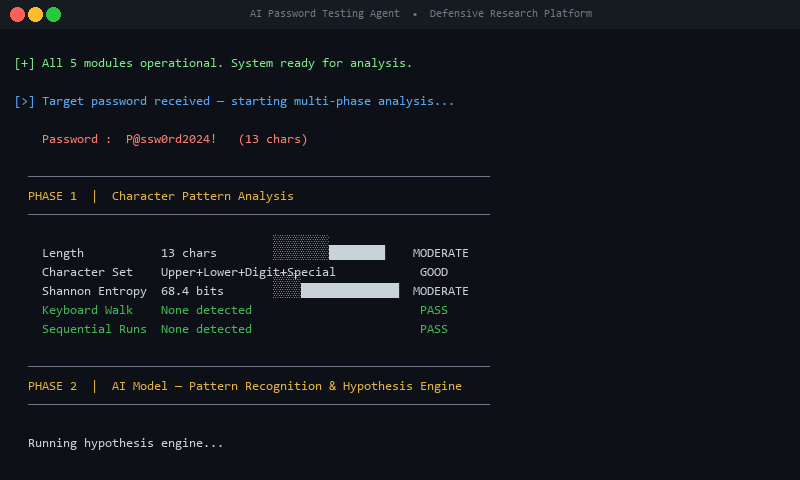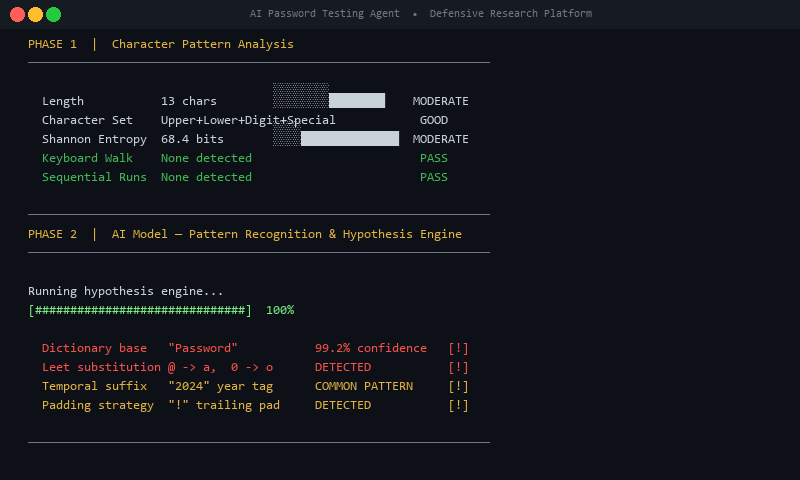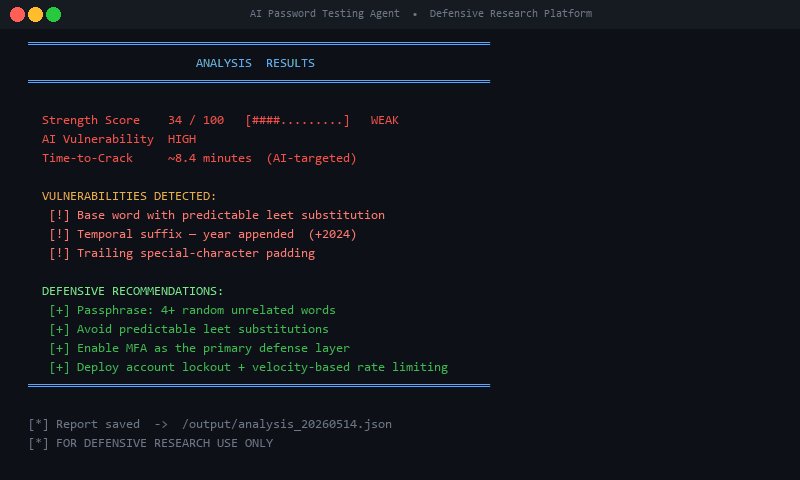
An intelligent agent for testing password strength, identifying vulnerabilities, and exploring patterns in password creation.