
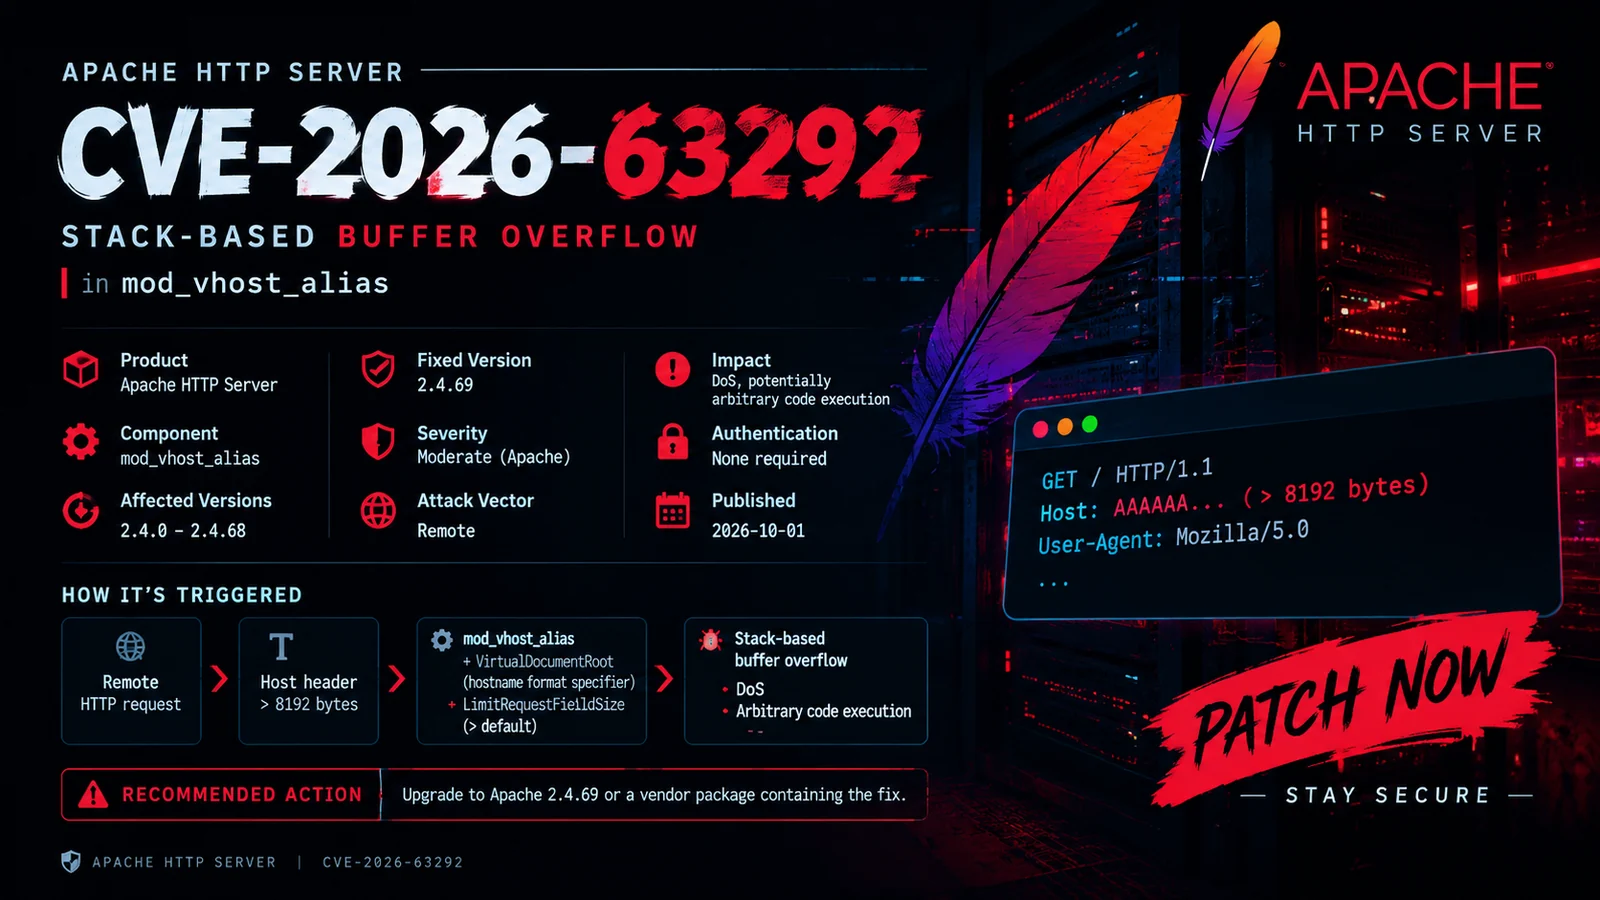
CVE-2026-63292
 0xblackash/cve-2026-63292
Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
configuration-auditingdefensive-toolseducation+4
0xblackash/cve-2026-63292Documents CVE-2026-63292, a stack-based buffer overflow in Apache mod_vhost_alias, with affected versions, safe version and configuration checks, and…
 zerodayevil/cve-2026-20817
Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 horkimhab/cve-2026-10817
Educational security research repository for CVE-2026-10817, providing proof-of-concept material and lab guidance for authorized vulnerability…
 horkimhab/cve-2025-9974
Educational security research repository for CVE-2025-9974, providing vulnerability awareness material and authorized lab guidance for controlled…
 horkimhab/cve-2026-65660
Educational security research repository documenting CVE-2026-65660 with setup guidance for authorized lab testing and vulnerability awareness.
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 horkimhab/cve-2026-90898
Educational CVE-2026-90898 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated…
 horkimhab/cve-2026-94545
Educational CVE research repository for CVE-2026-94545, providing proof-of-concept material and lab guidance for authorized vulnerability analysis…
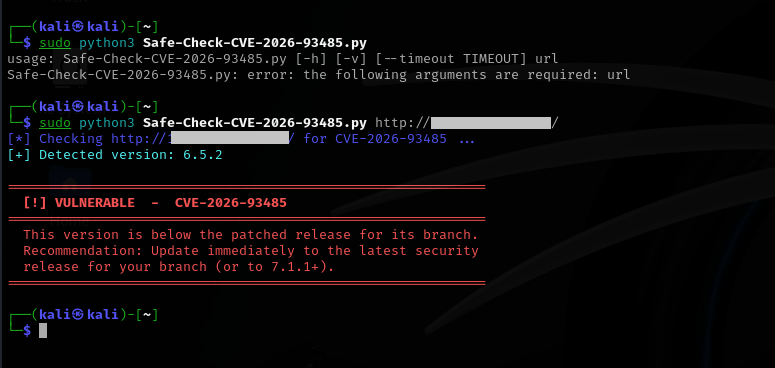 0xblackash/cve-2026-93485
Defensive research repository for CVE-2026-93485, a WordPress core stored XSS flaw, with version-check scanner, technical analysis, and patch…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 aayushbankar/cve-2026-28576
PoC and red team app for CVE-2026-28576, a zero-permission SQL injection in the Android Contacts Provider enabling full contacts database…
 muradislamzada/cve-2026-93528
Technical analysis, proof of concept, and responsible disclosure timeline for CVE-2026-93528, an unauthenticated order data disclosure in NP Quote…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 horkimhab/cve-2026-80844
Proof-of-concept and research repository for CVE-2026-80844 (DirtyAH6), providing educational material and lab setup guidance for authorized…
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 djzzlim/cve-2026-94036
Repository dedicated to CVE-2026-94036, likely containing vulnerability analysis, proof-of-concept, or exploit code for this specific security issue.