StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reference implementation of a multi-bit LLM watermarking scheme using coded payload spreading, unbiased reweighting, and soft-decision ECC decoding…

Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…

Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…

Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…

Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…

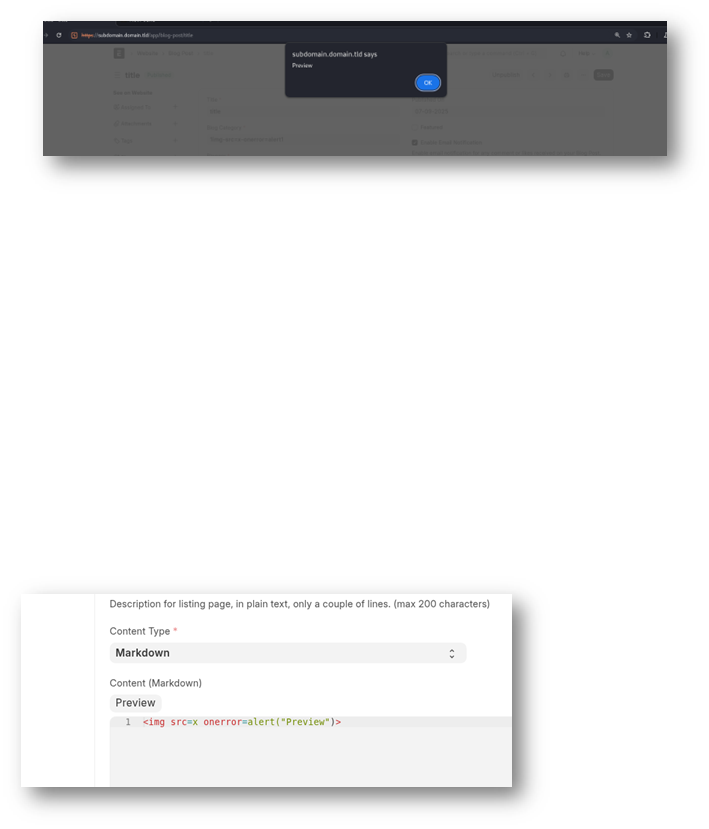
A stored cross-site scripting (XSS) vulnerability in the blog post feature of ERPNEXT v15.67.0 allows attackers to execute arbitrary web scripts or…

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

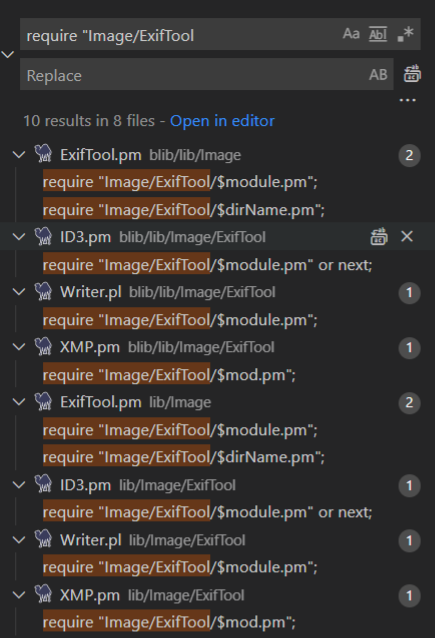
In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…

Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…

The value of the produk request parameter is copied into the value of an HTML tag attribute which is encapsulated in double quotation marks. The…

Proof-of-concept exploit for CVE-2025-66478 targeting unsafe React Server Components payload handling in Next.js. Includes automated payload…

Modified code so that we don´t need to rely on CAB archives

Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…

Proof-of-concept for CVE-2024-48415: stored XSS vulnerability in itsourcecode Loan Management System v1.0 via borrower profile fields. Includes…

Detailed technical walkthrough of CVE-2025-55182 (React2Shell), tracing React's Flight protocol internals to explain the exploit chain, payload…

This repository provides a proof-of-concept for CVE-2025-55182 (React2Shell), a remote code execution vulnerability in React Server Components. It…