CVE-2026-99999-exploit

CVE-2026-99999 Working PoC — real VM escape for Linux kernel csum_start bug (CVSS 9.3). Guest-to-Host heap leak. See also: CVE-2026-99999-analysis…

CVE-2026-99999 Working PoC — real VM escape for Linux kernel csum_start bug (CVSS 9.3). Guest-to-Host heap leak. See also: CVE-2026-99999-analysis…

Technical investigation of CVE-2026-97229 (GitLab CI/CD regex RCE): local patched GitLab lab, CI Lint API checks, version auditing, and defensive…

Incident write-up: unsigned .so in the Plex Media Server codec cache executes a dropper on every transcode (CVE-2026-96656) — IOCs, STIX, YARA

Self-contained PoC and analysis for CVE-2026-94300, a GSS-TSIG use-after-free in BIND 9.20.29, with a debugger-assisted model of the…

Independent reconstruction, lab validation, and PoC for CVE-2026-9198, the Langflow unauthenticated RCE (fixed in 1.10.1)

Fingerprint the exact GPU you're running on, even among identical GPUs, from the order its atomic adds land in. 99.1% accuracy, survives reboots,…

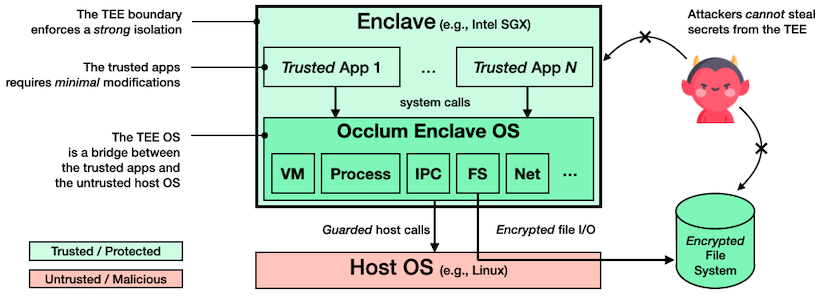
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…

HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis

Meaningful control of data in distributed systems.

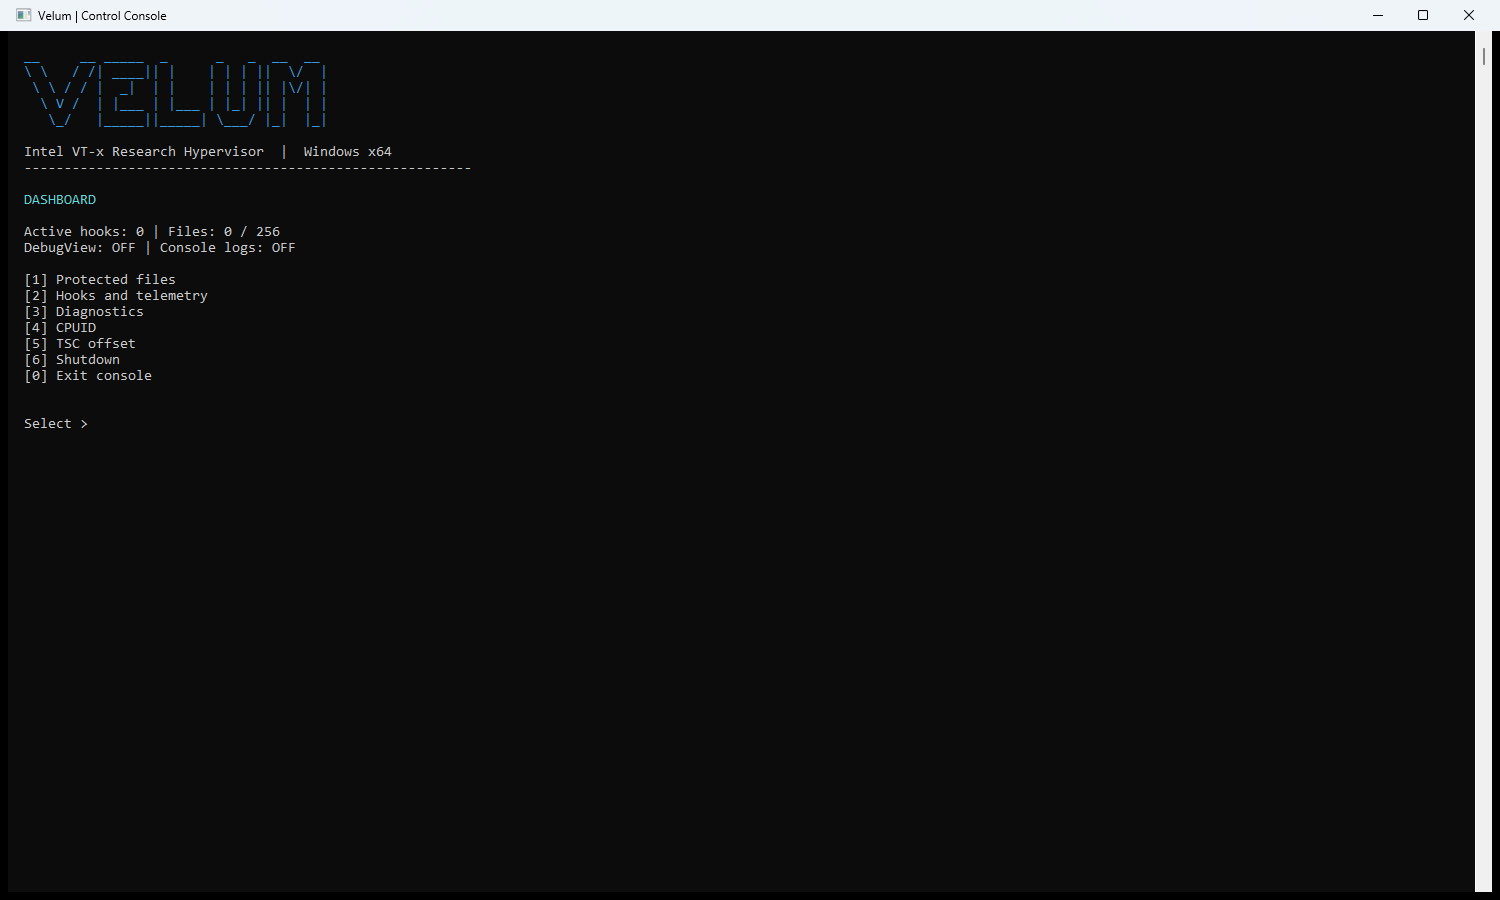
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…

Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

:robot: (Vibecoded prototype) NO, There is an easy way to exploit this vulnerability!

Proof-of-concept code and research notes for QPACK/HTTP-3 vulnerabilities (CVE-2025-64702, CVE-2026-12523, CVE-2025-13945) for authorized lab testing.

Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

OWASP project for AI-assisted threat modeling, helping teams identify, analyze, and document security threats and mitigations in system designs.

OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.