
OMLASP
 telefonica/omlasp
Framework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
adversarial-attackai-securityeducation+2
22
telefonica/omlaspFramework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…
 google/security-research
This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 gpt-laboratory/trustworthyrag
An Evaluation Agent for Detecting Misinformation and Knowledge Poisoning in Retrieval-Augmented Generation Systems.
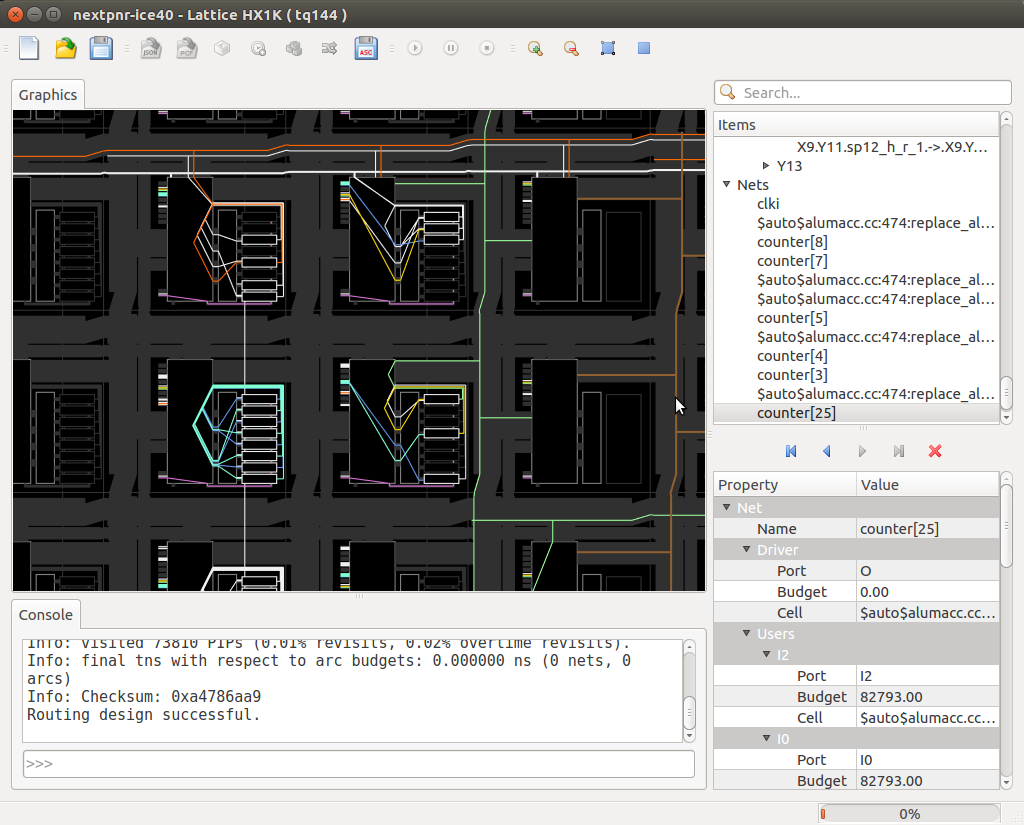 yosyshq/nextpnr
nextpnr portable FPGA place and route tool
 djjohnson565/cups-exploit
Heap-based buffer overflow example based on CVE-2023-4504
 owasp/osib
Centralized YAML-based knowledge base linking MITRE CWE, OWASP Top10, ASVS, and other security standards with versioned references. Includes MkDocs…
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 kmeps4/cverev3
Proof-of-concept testing environment for CVE-2021-30858, based on Google Project Zero's root cause analysis of an in-the-wild iOS exploit.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 claudiugeorgiu/obfuscapk
An automatic obfuscation tool for Android apps that works in a black-box fashion, supports advanced obfuscation features and has a modular…
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 pvharmo2/gha-lab-8aba6b05dc
Security-research lab reproducing CVE-2026-45132 (pwn request via pull_request_target chart-name injection in generate-schema.yaml) — snapshot of…
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 horkimhab/cve-2026-51990
CVE-2026-51990 proof-of-concept repository for authorized security research, vulnerability awareness, and defensive testing in isolated lab…
 ipisav/fastjson-cve
Reproduction project for CVE-2026-16723, a critical RCE in fastjson 1.2.68-1.2.83. Demonstrates AutoType bypass, JNDI injection, and TemplatesImpl…