Advanced-Loader-Reverse-Engineering

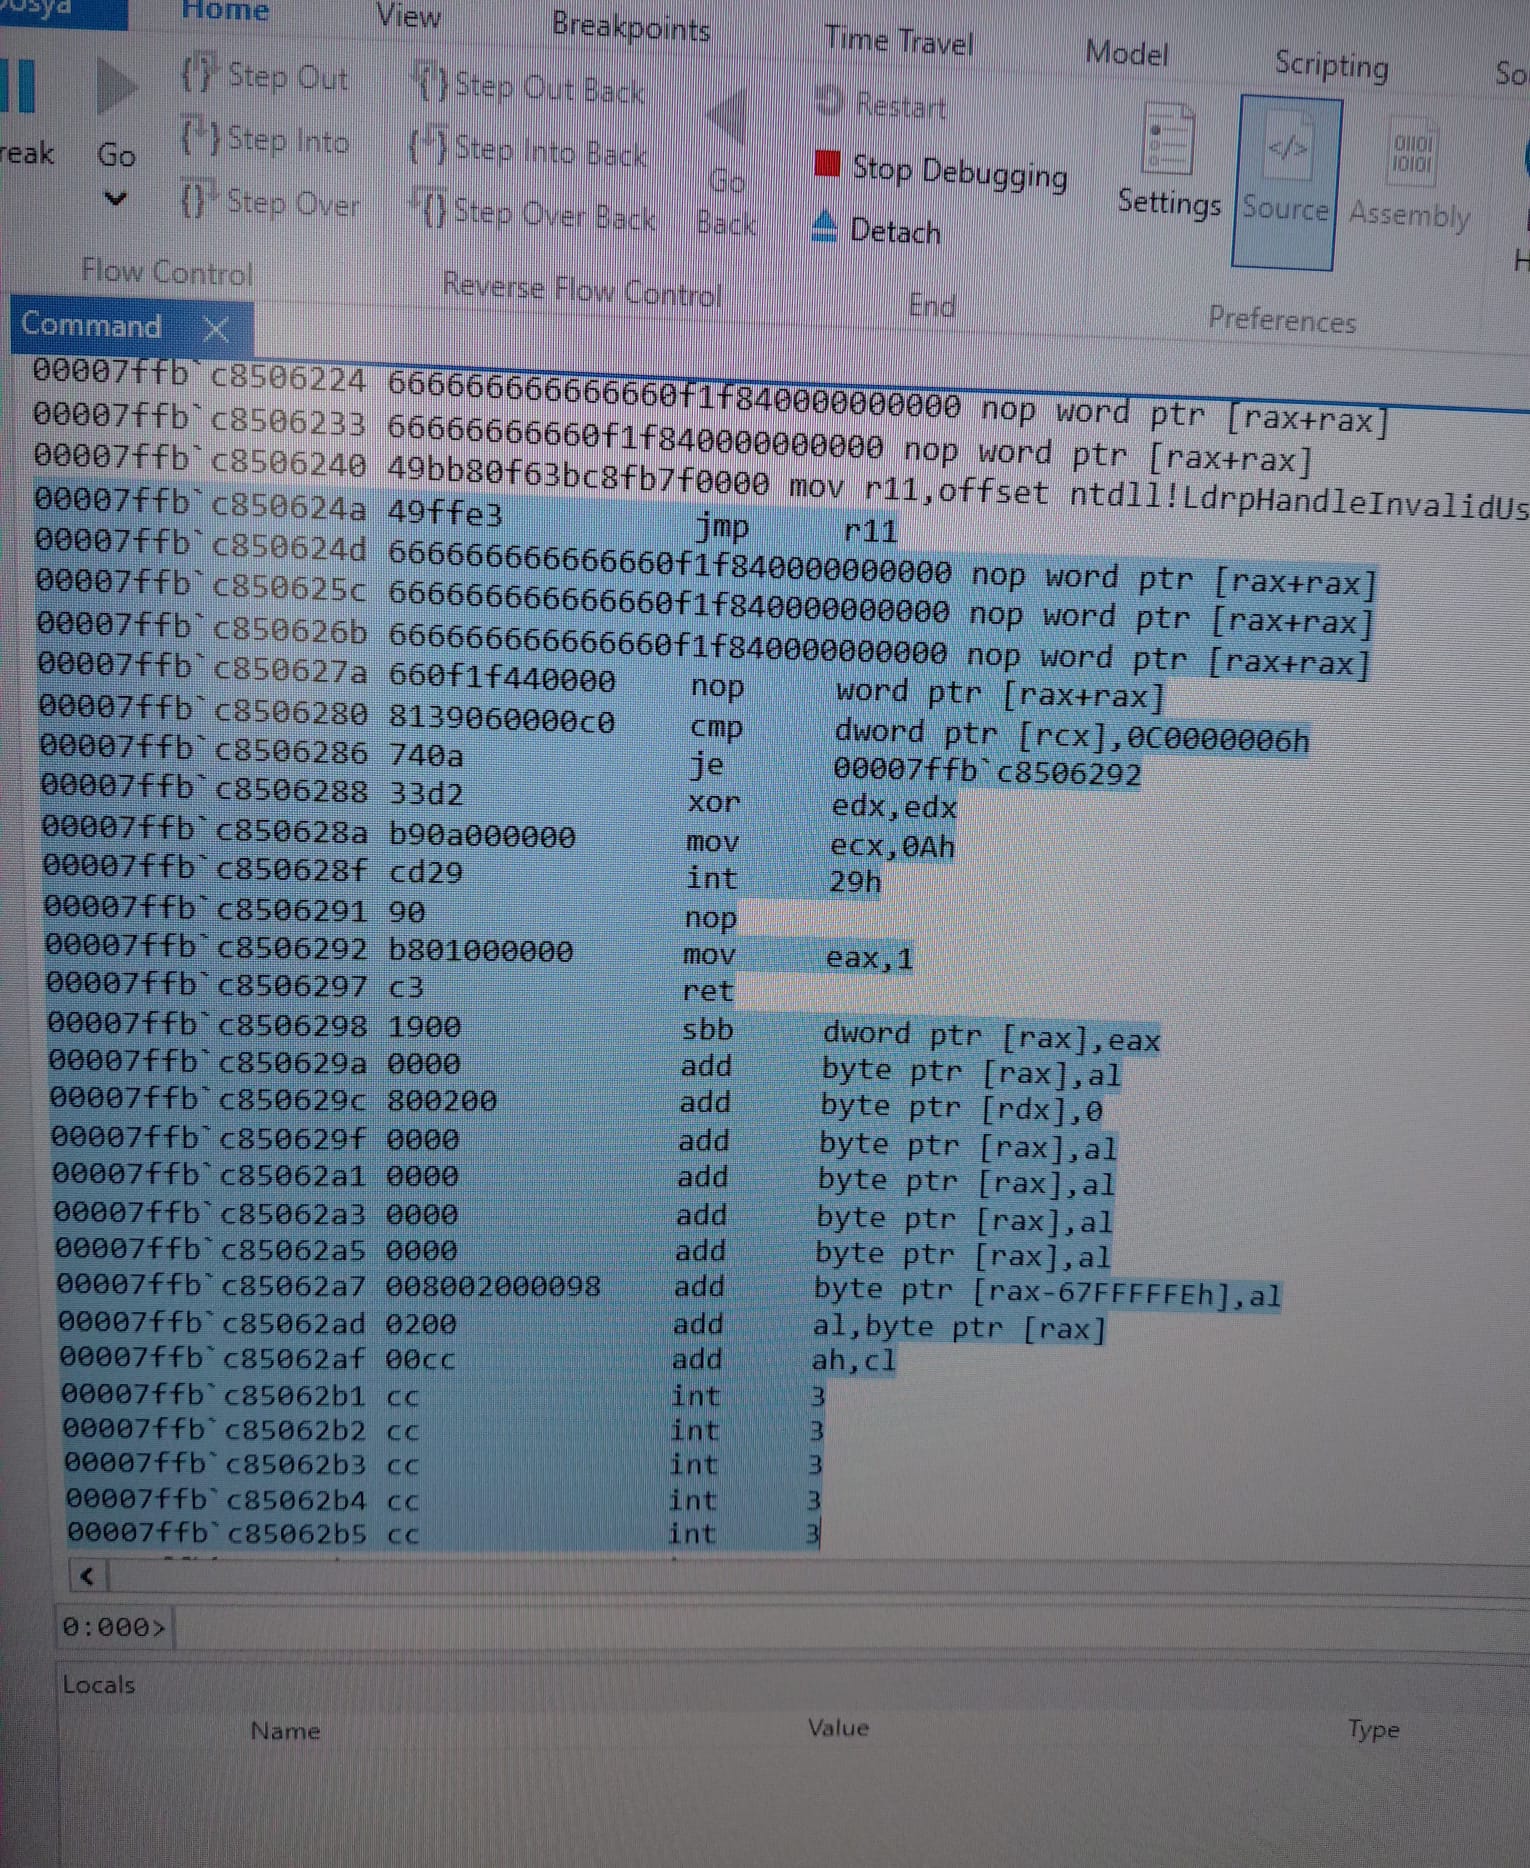
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

Proof-of-concept reproducer for Apache Ranger UnixUserGroupBuilder OS command injection (CVE-2026-28672), demonstrating the vulnerability and…

Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content

Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…

CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…

HiddenSteps — a local-first personal workflow intelligence platform

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…

Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

PoC and vulnerability report for CVE-2025-47827.

GreyEnergy Mini Module Malware Analysis (Turkish)

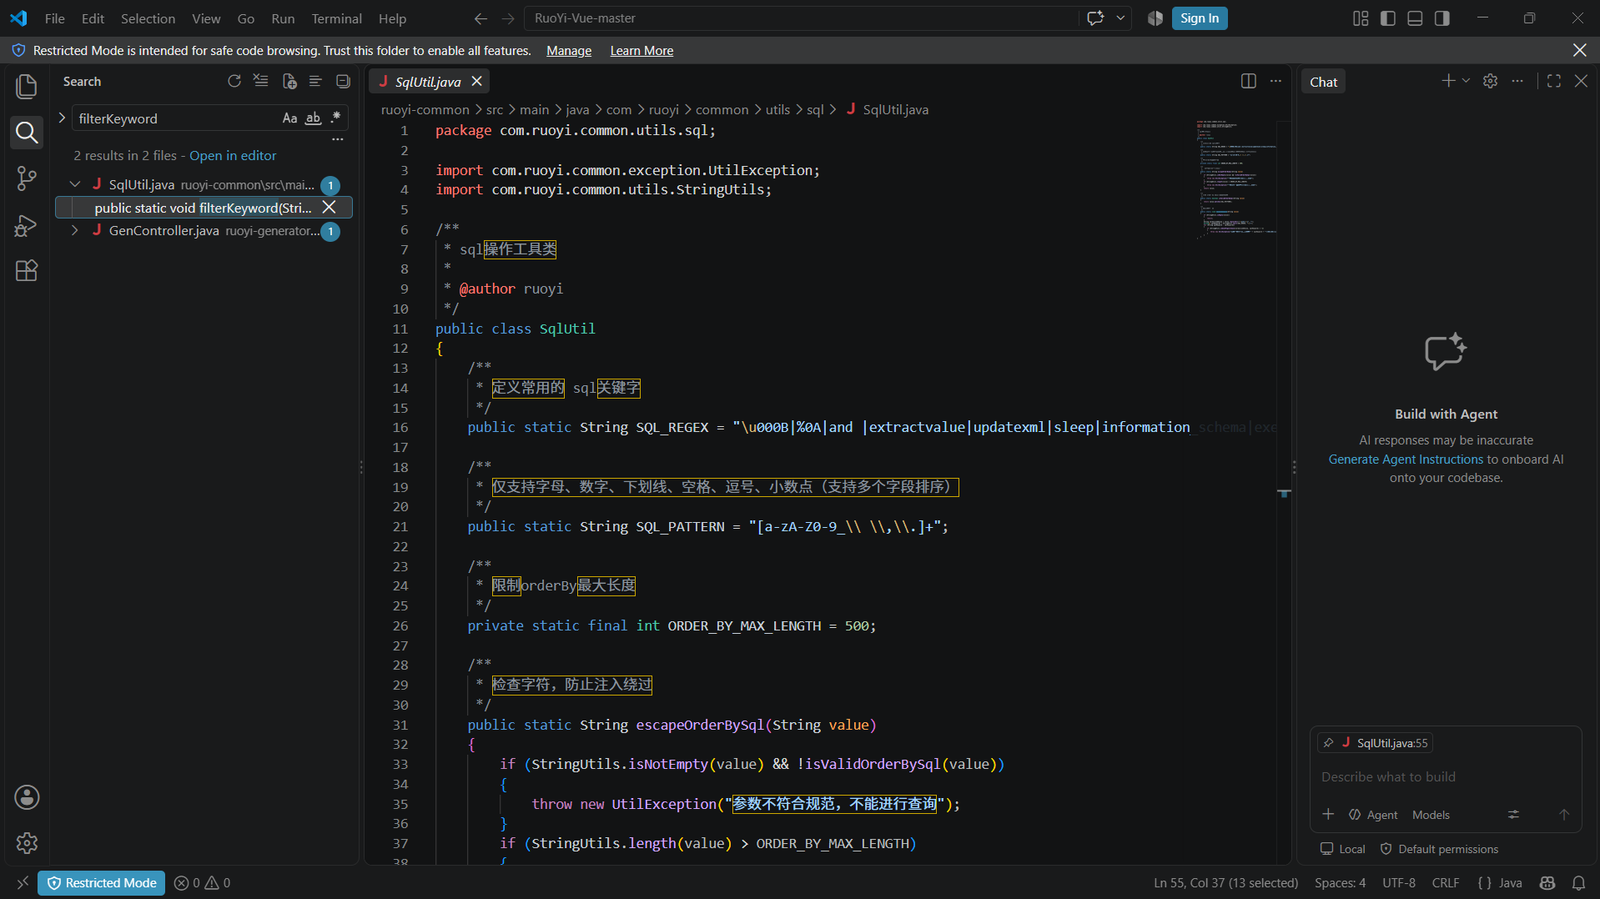
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…

Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.

Tarfile module directory traversal vulnerability ( with overflow crossed Directory ) --> Lead to Privilege escalation

Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.

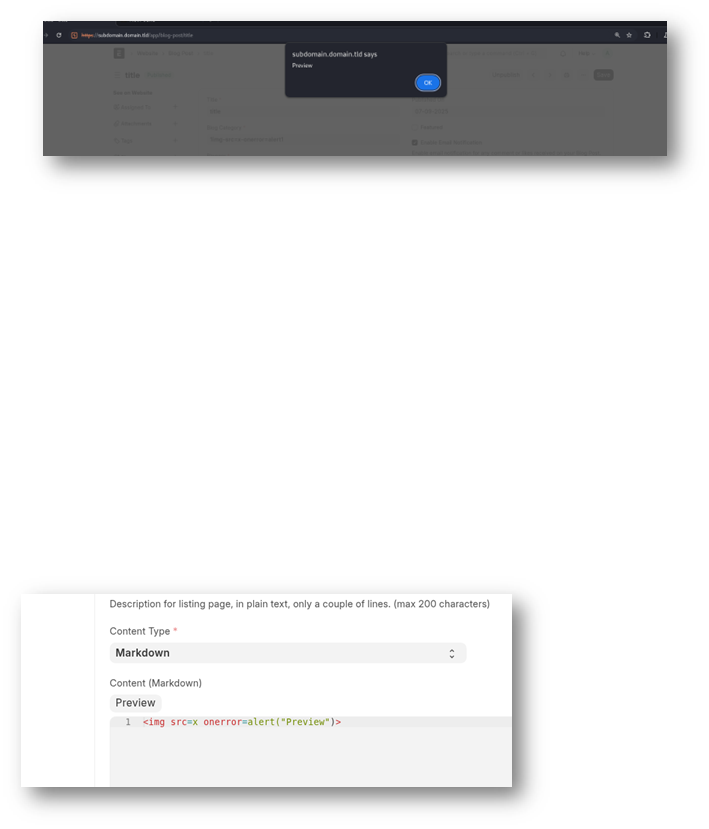
A stored cross-site scripting (XSS) vulnerability in the blog post feature of ERPNEXT v15.67.0 allows attackers to execute arbitrary web scripts or…