samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…

Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…

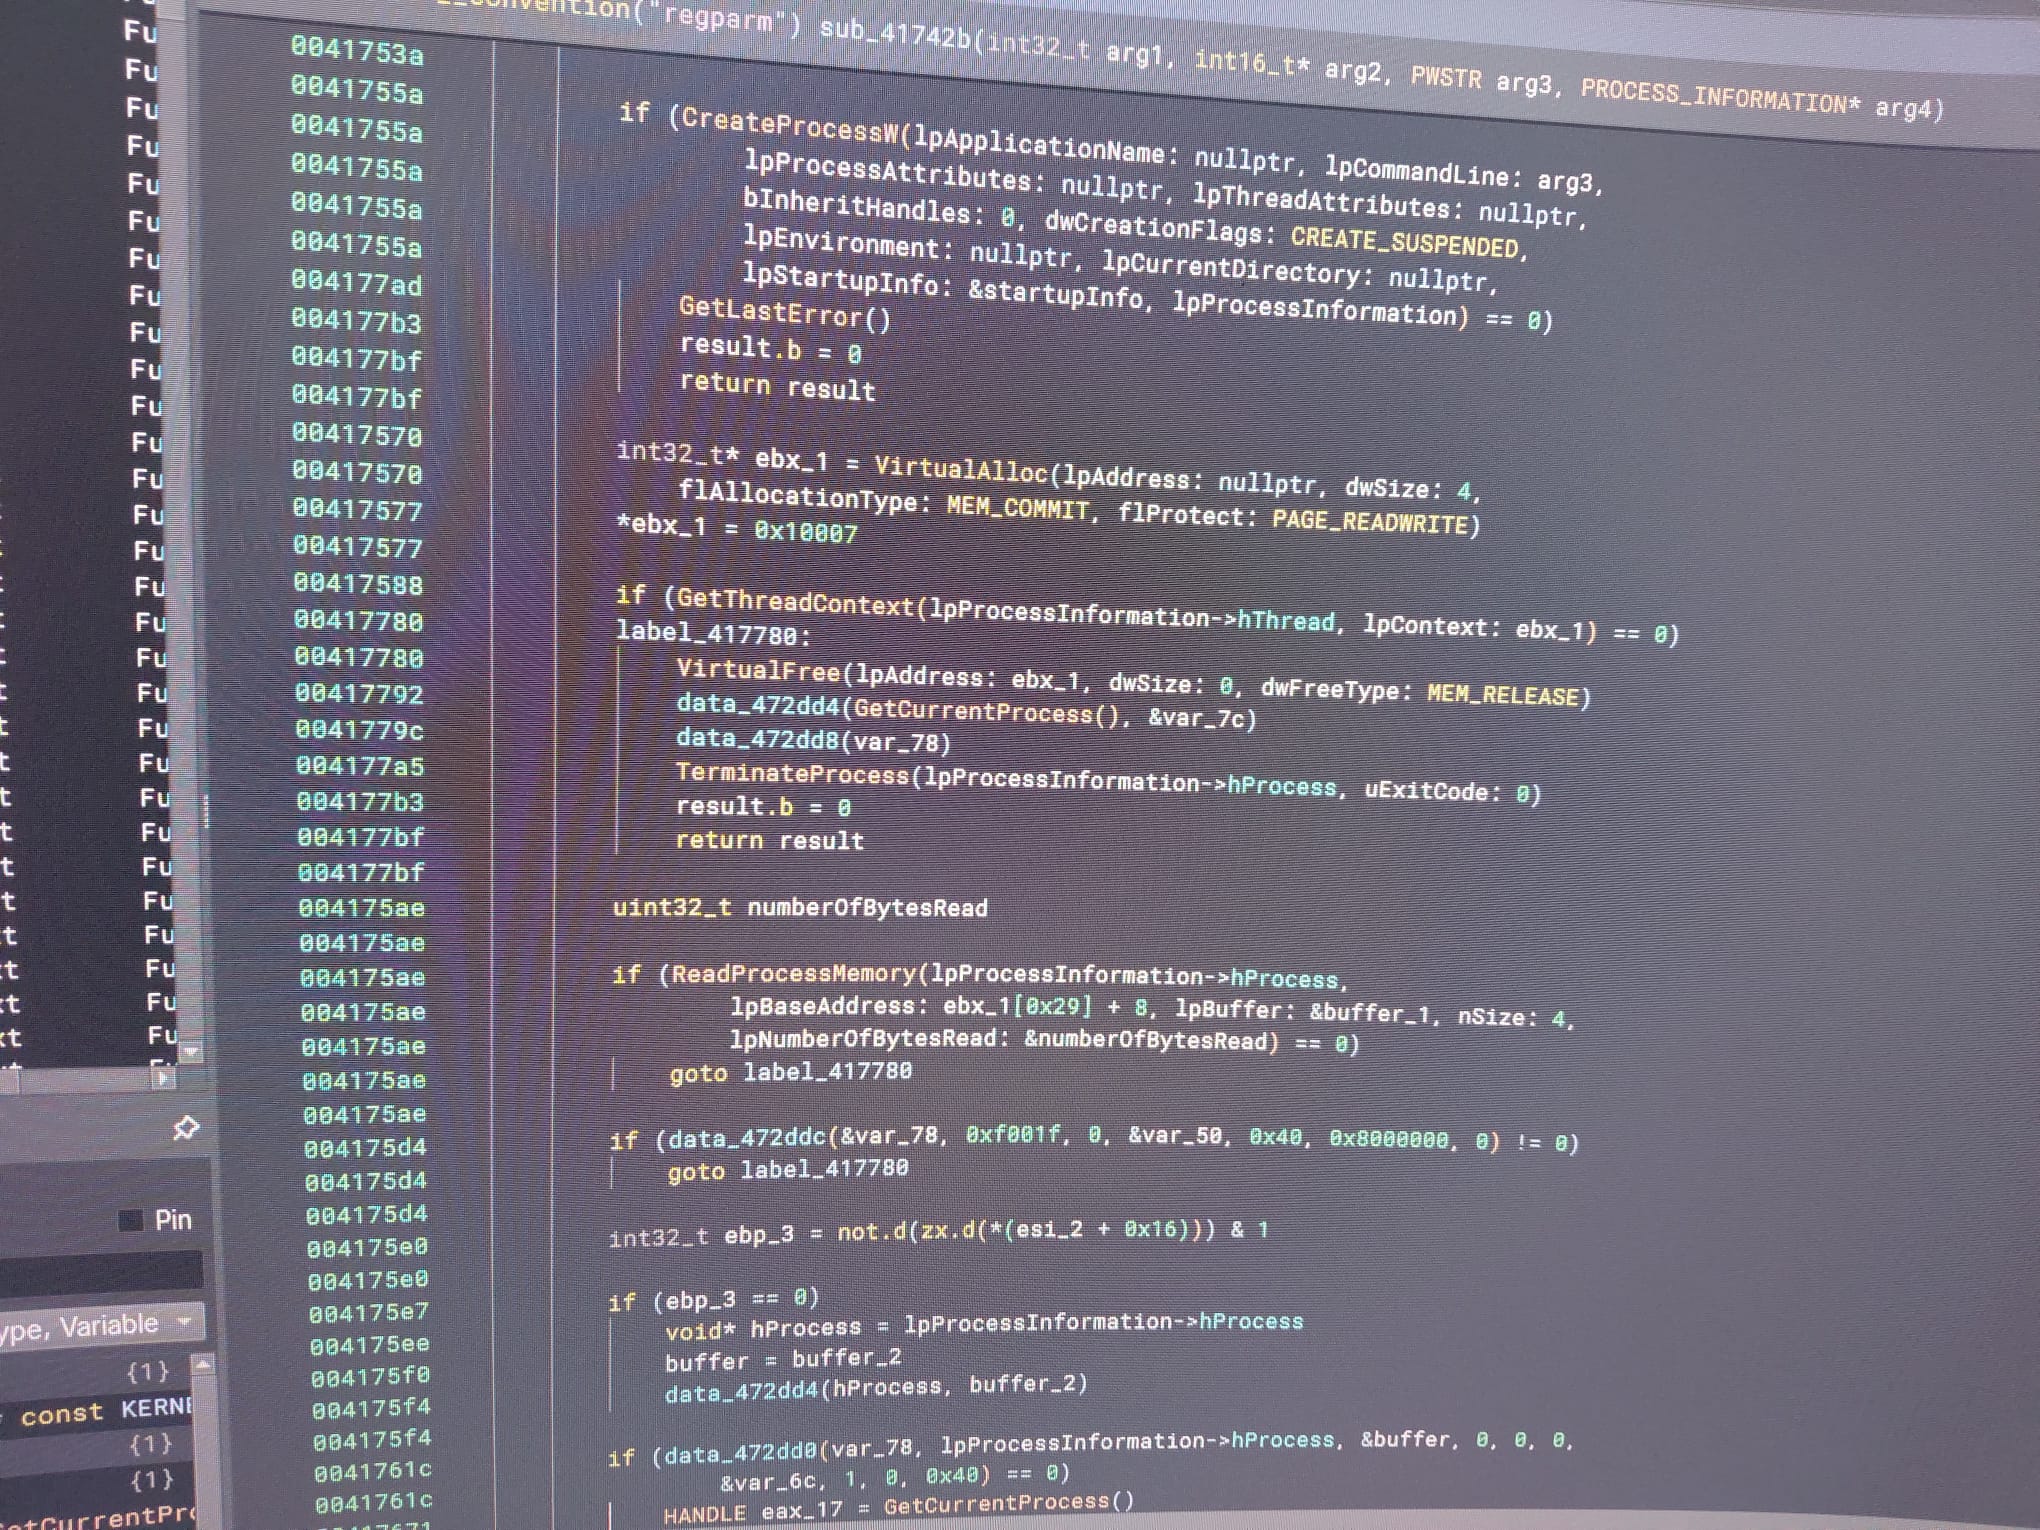
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

Proof-of-concept exploit for Ghostscript command injection (CVE-2023-36664) with payload generation and injection into EPS/PS files for code…

Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…

Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…

Modified code so that we don´t need to rely on CAB archives