
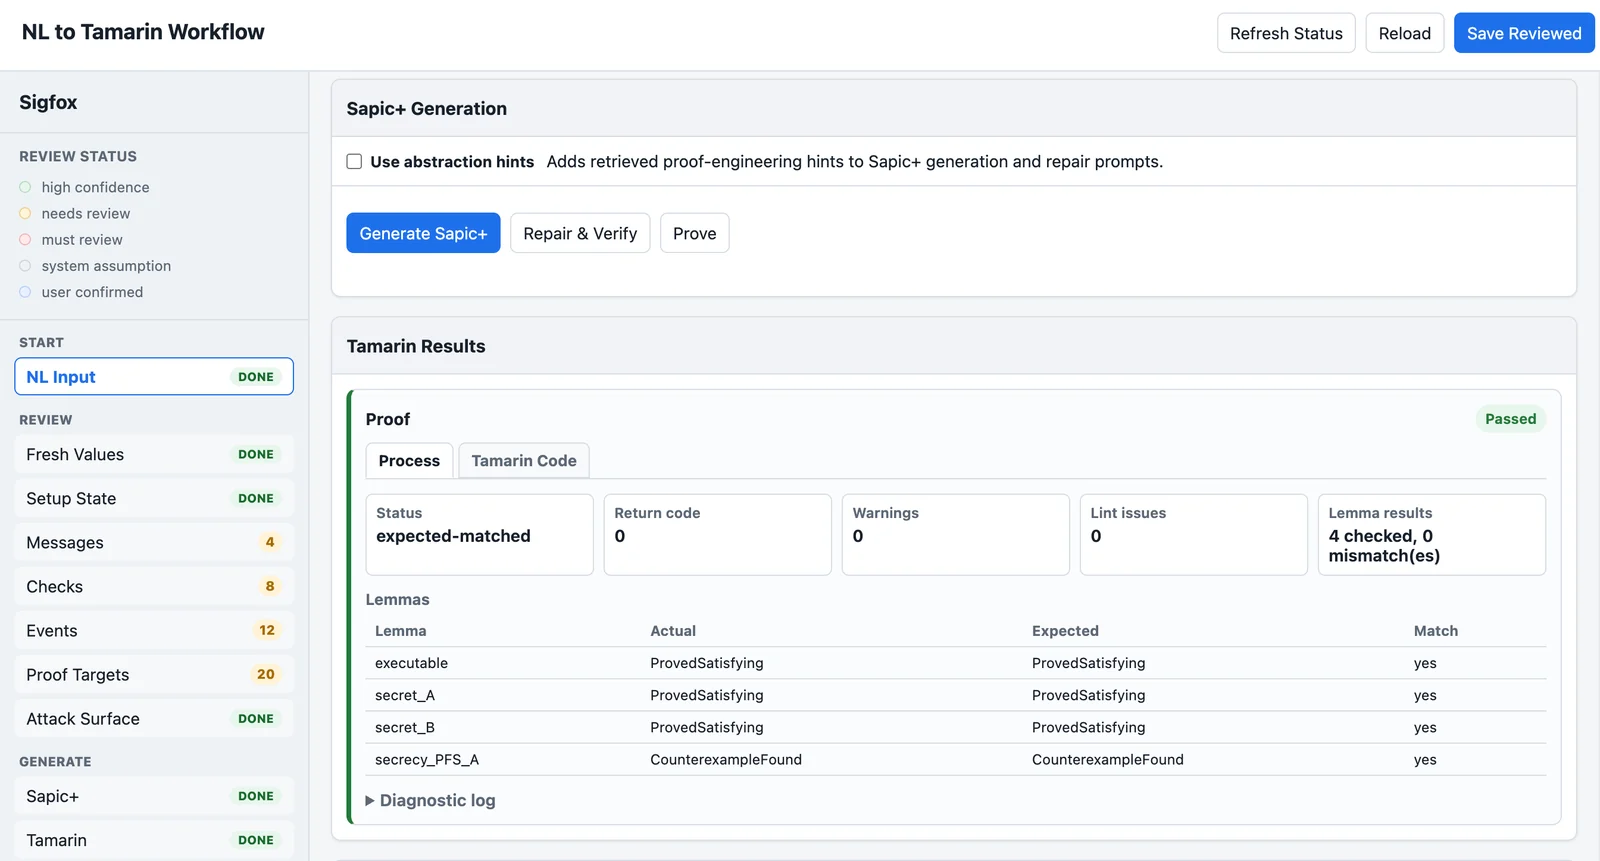
TamarinAgent
 laplace1002/tamarinagent
Human-in-the-loop UI that converts natural-language or C/C++ protocol descriptions into a reviewable Protocol IR, then generates Sapic+/Tamarin…
ai-securitycode-analysiscryptography+5
laplace1002/tamarinagentHuman-in-the-loop UI that converts natural-language or C/C++ protocol descriptions into a reviewable Protocol IR, then generates Sapic+/Tamarin…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 meh098/cve-2026-24072-analysis
Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…
 milot/dissecting-pkexec-cve-2021-4034
Educational analysis and proof-of-concept code for CVE-2021-4034 (pkexec local privilege escalation), with detailed comments explaining the…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 manizada/diagspill
Local privilege escalation PoC for CVE-2026-74469, exploiting an SCTP diagnostic-reply kernel memory corruption to gain root on Linux x86-64 systems.
 xrazymee/ragsieve
Self-referenced local contrast for knowledge-poison detection in retrieval-augmented generation
 veereshgadige/aziot-cctv-cve-2025-50777
CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 4xura/cve-2026-31431-copy-fail
Research artifacts, PoC scripts, and lab assets for the Copy Fail Linux local privilege escalation writeup on https://4xura.com/binex/kernel/copy-fail
 manizada/pppoeject
Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
 szybnev/cve-2026-7482
Reproduces CVE-2026-7482 heap out-of-bounds read in Ollama GGUF loading and quantization, with differential analysis of quantized artifacts to…
 9xeb/context-segmentation
Multi-agent automated context management for long horizon tasks in local AI Agents
 abraxas/cve-2025-38502-linux-lpe
Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…
 nicetop1027/cve-2026-termius
Vulnerability disclosure with PoCs for three critical Termius macOS flaws: Remote Code Execution via exposed Node modules, Local Privilege Escalation…