
FS-attack
 phil-fan/fs-attack
Implementation of the paper "Rethinking Latency Denial-of-Service: Attack the LLM Serving Framework, Not the Model"
adversarial-attackai-securitymachine-learning+2
3
phil-fan/fs-attackImplementation of the paper "Rethinking Latency Denial-of-Service: Attack the LLM Serving Framework, Not the Model"
 thehackersbrain/certificate-of-compromise
SoK/Whitepaper on Offensive Operations against Active Directory Certificate Service
 razureink/cve-2026-49975-http2bomb_reproduction
PoC exploit for CVE-2026-49975 HTTP/2 Bomb DoS vulnerability. Demonstrates HPACK indexed reference bomb combined with flow-control window stall to…
 slsa-framework/slsa
Supply-chain Levels for Software Artifacts
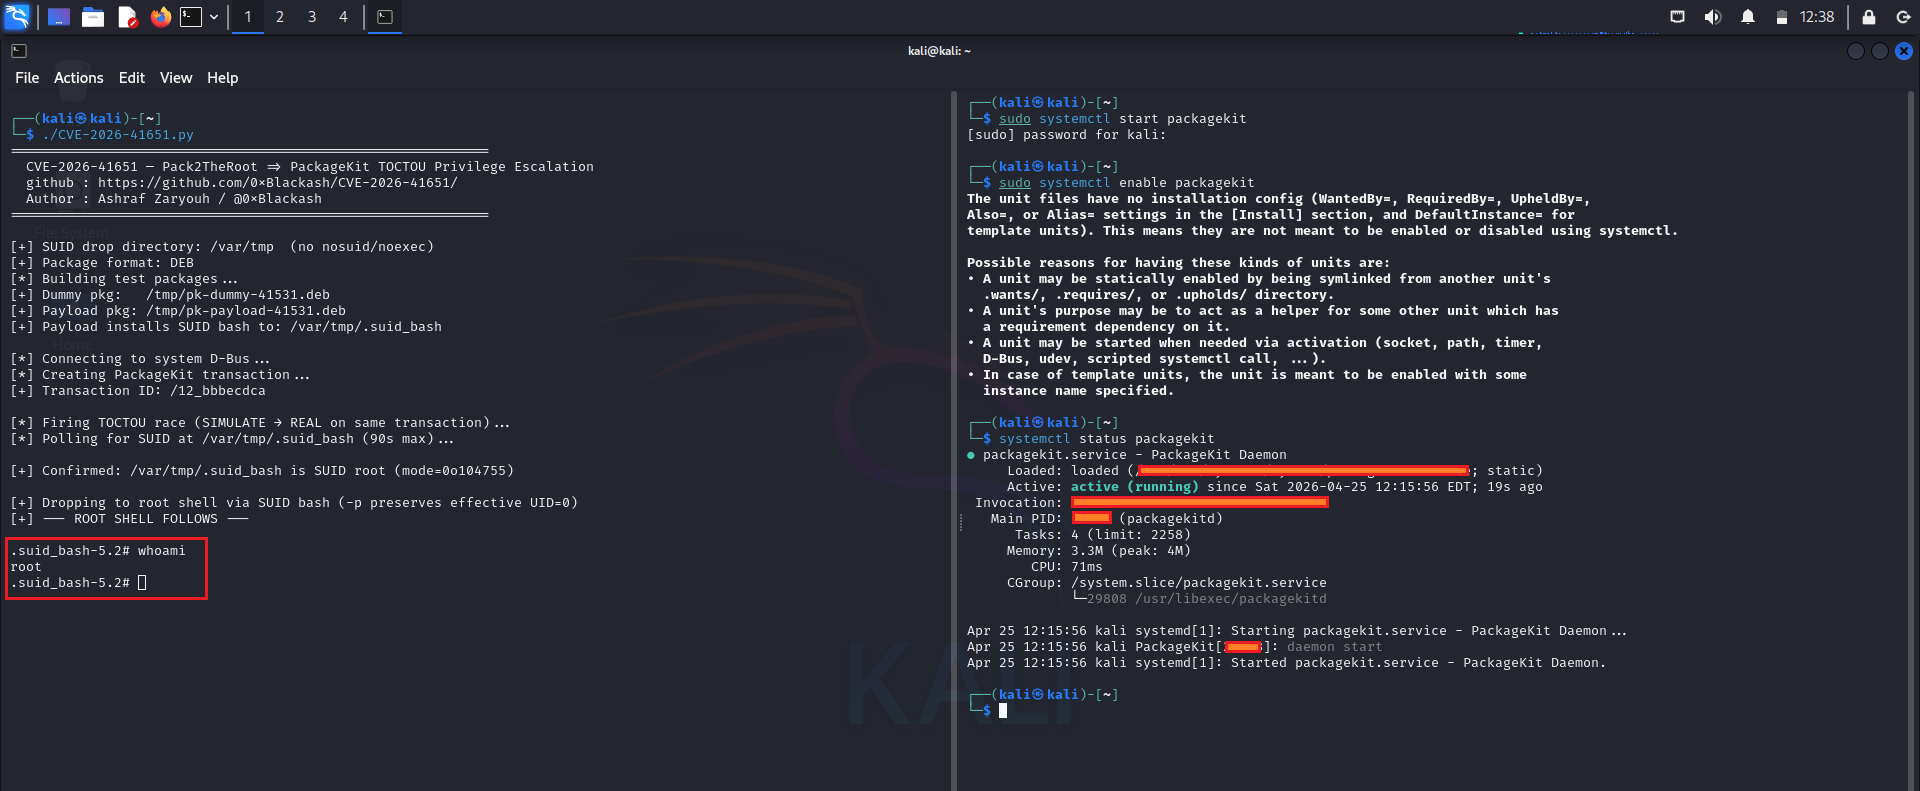
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 hyperps/cve-2026-0897
Allocation of Resources Without Limits or Throttling in the HDF5 weight loading component in Google Keras 3.0.0 through 3.13.0 on all platforms…
 missaels235/poc-cve-2025-24104-py
Proof-of-concept Python script demonstrating iOS file exfiltration via malicious symlink in device backup restoration, targeting the…
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
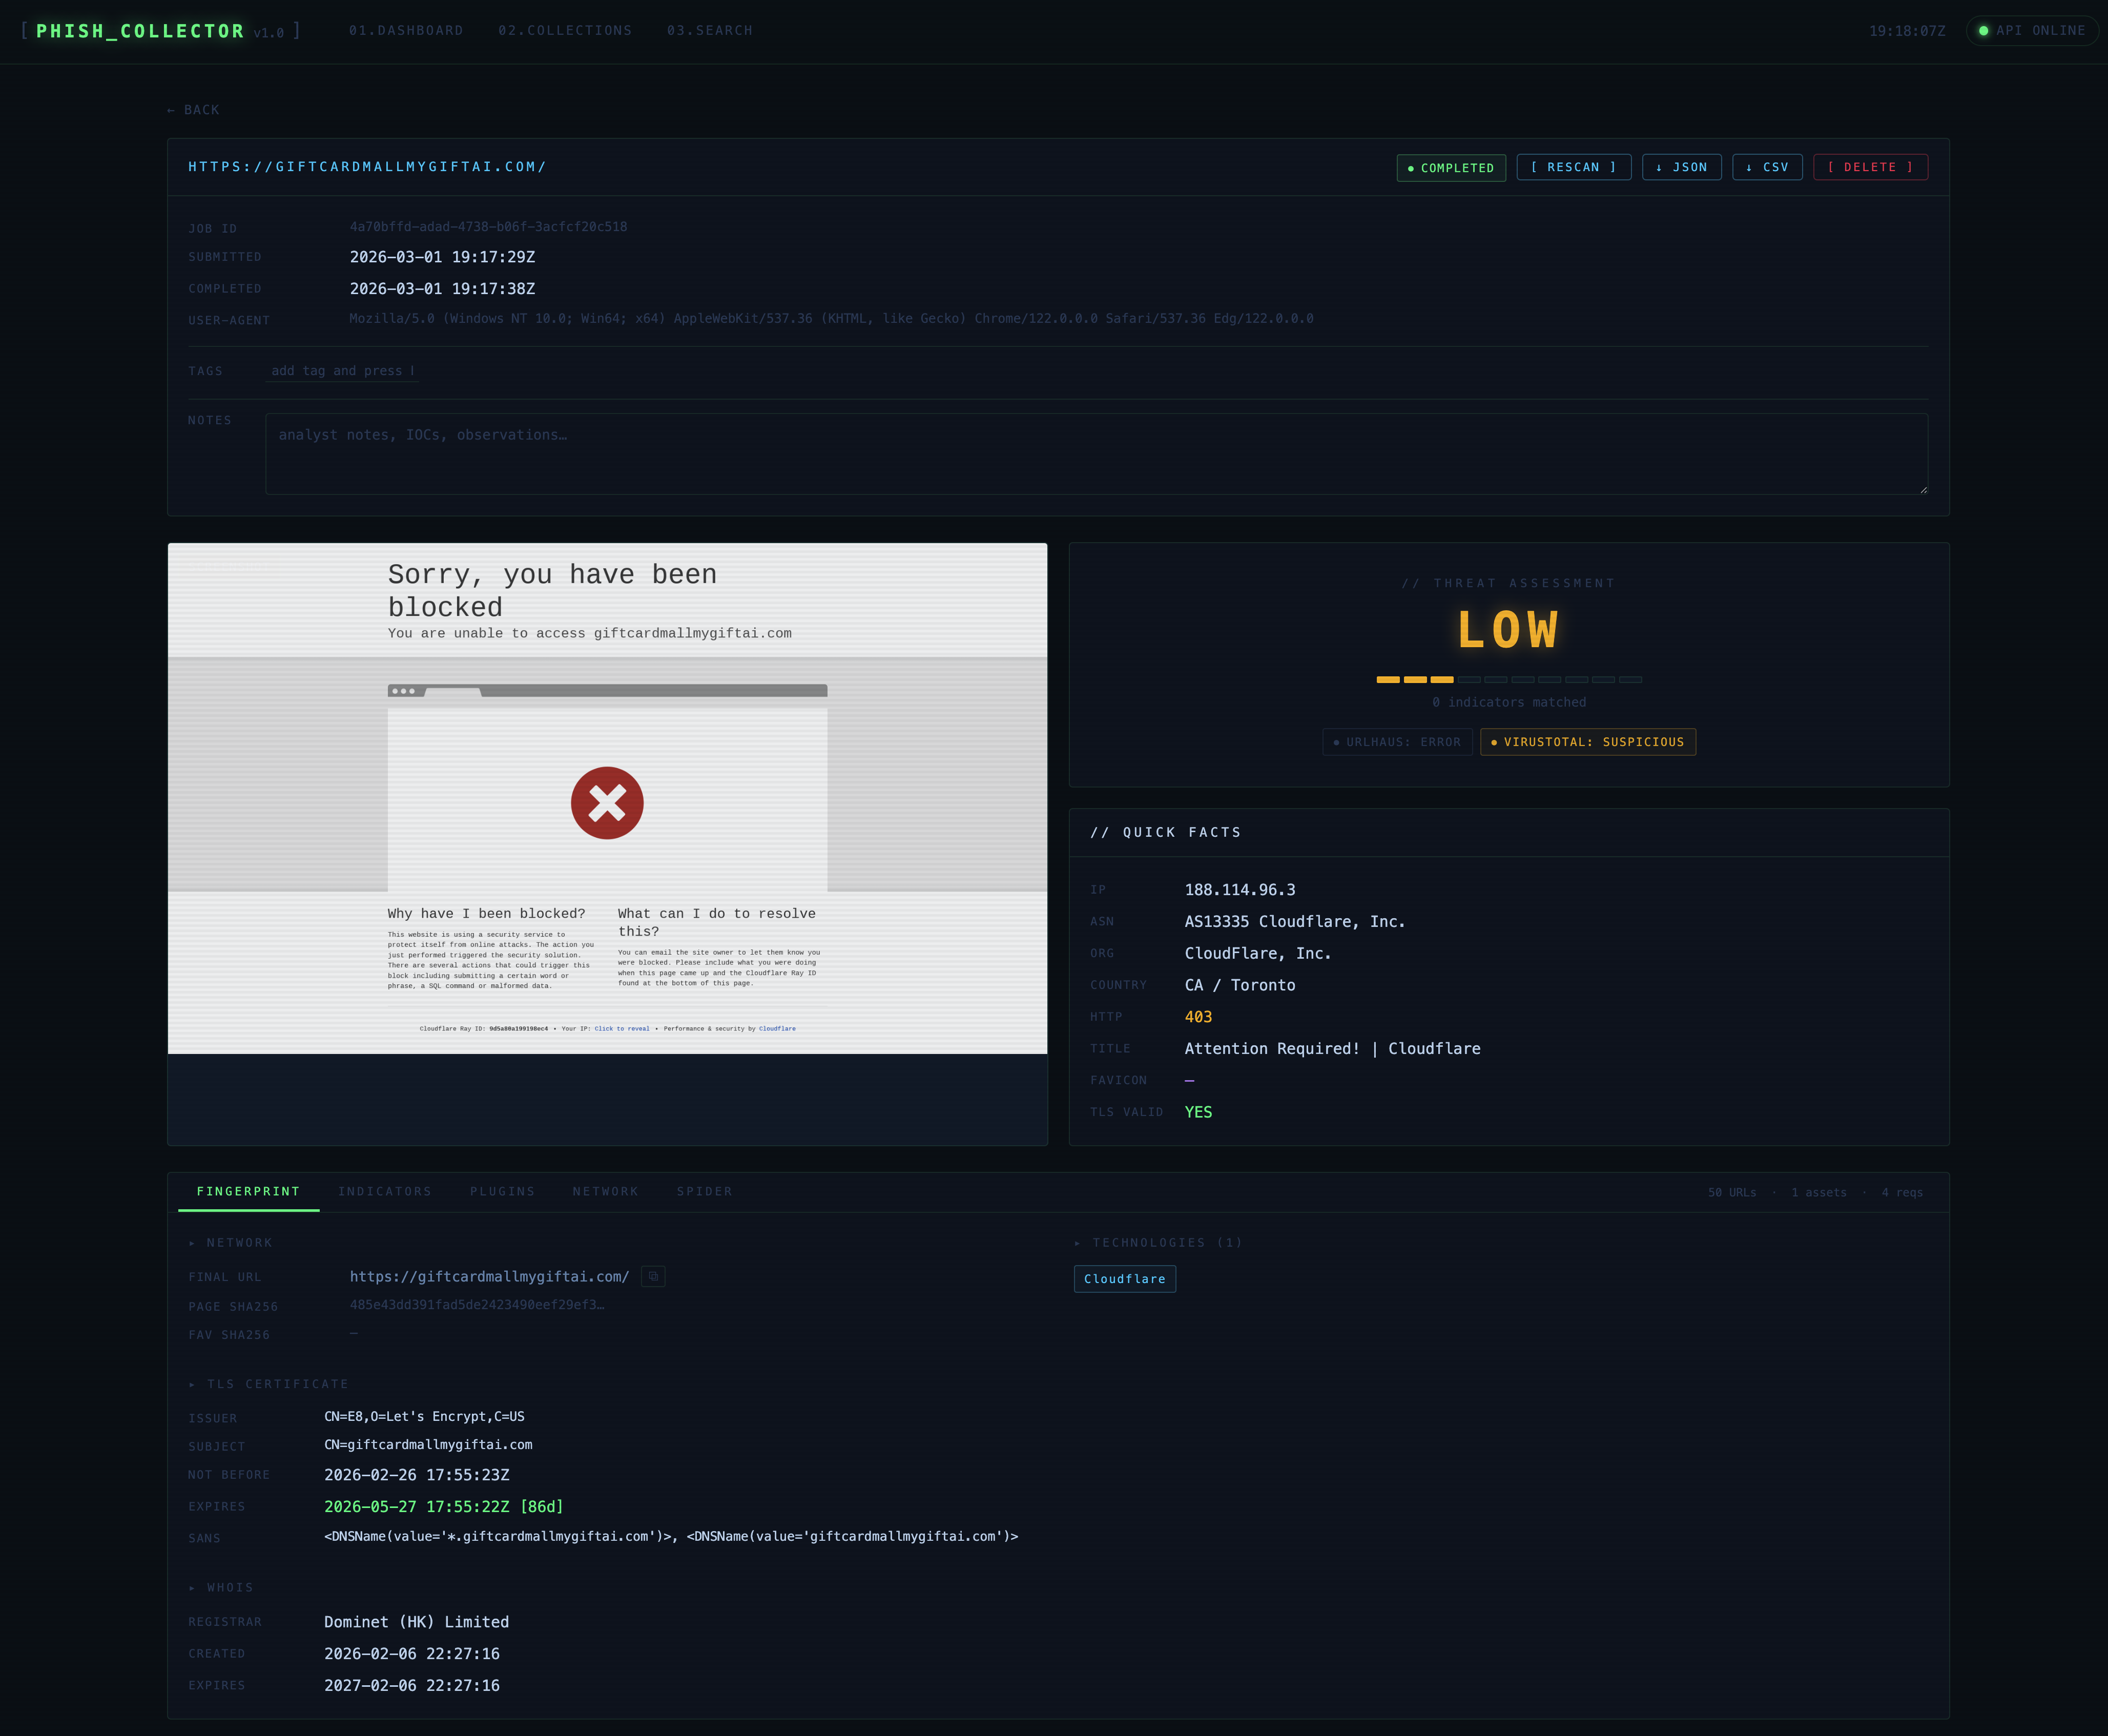 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 juanpoch/cve-2026-73570
Zimbra Collaboration Suite RCE — SMTP log poisoning → swatchdog → OS Command Injection (CVSS 8.9, CISA KEV)
 itzmetanjim/cve-2026-8697
Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
 gmh5225/cve-2015-2291
(1) IQVW32.sys before 1.3.1.0 and (2) IQVW64.sys before 1.3.1.0 in the Intel Ethernet diagnostics driver for Windows allows local users to cause a…
 joakimbulow/cve-2026-24688
Proof-of-concept exploit for CVE-2026-24688, a denial-of-service vulnerability in pypdf's outline parsing. Includes malicious PDF generator and…
 ghoxtbyte/cve-2026-16265
Technical advisory and research notes for CVE-2026-16265, a Subscriber+ denial-of-service flaw in the WP Maps WordPress plugin fixed in version 4.9.7.
 rootdirective-sec/cve-2026-33017-lab
Reproducible lab for CVE-2026-33017, an unauthenticated RCE in Langflow. Includes a Dockerized vulnerable service and a least-harm PoC that…