

PFQ
 pfq/pfq
Functional Network Framework for Multi-Core Architectures
network-mappingnetwork-securitypacket-sniffing-analysis+1
pfq/pfqFunctional Network Framework for Multi-Core Architectures
 niloofarkheirkhah/nili
Nili is a Tool for Network Scan, Man in the Middle, Protocol Reverse Engineering and Fuzzing.
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 trinadh465/external_tcpdump_cve-2018-14880
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 trinadh465/external_tcpdump_cve-2018-14469
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…
 satheesh575555/external_tcpdump_aosp10_r33_cve-2019-15166
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting, analysis, and…
 trinadh465/external_tcpdump_cve-2018-14879
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…

 ntop/pf_ring
High-speed packet processing framework
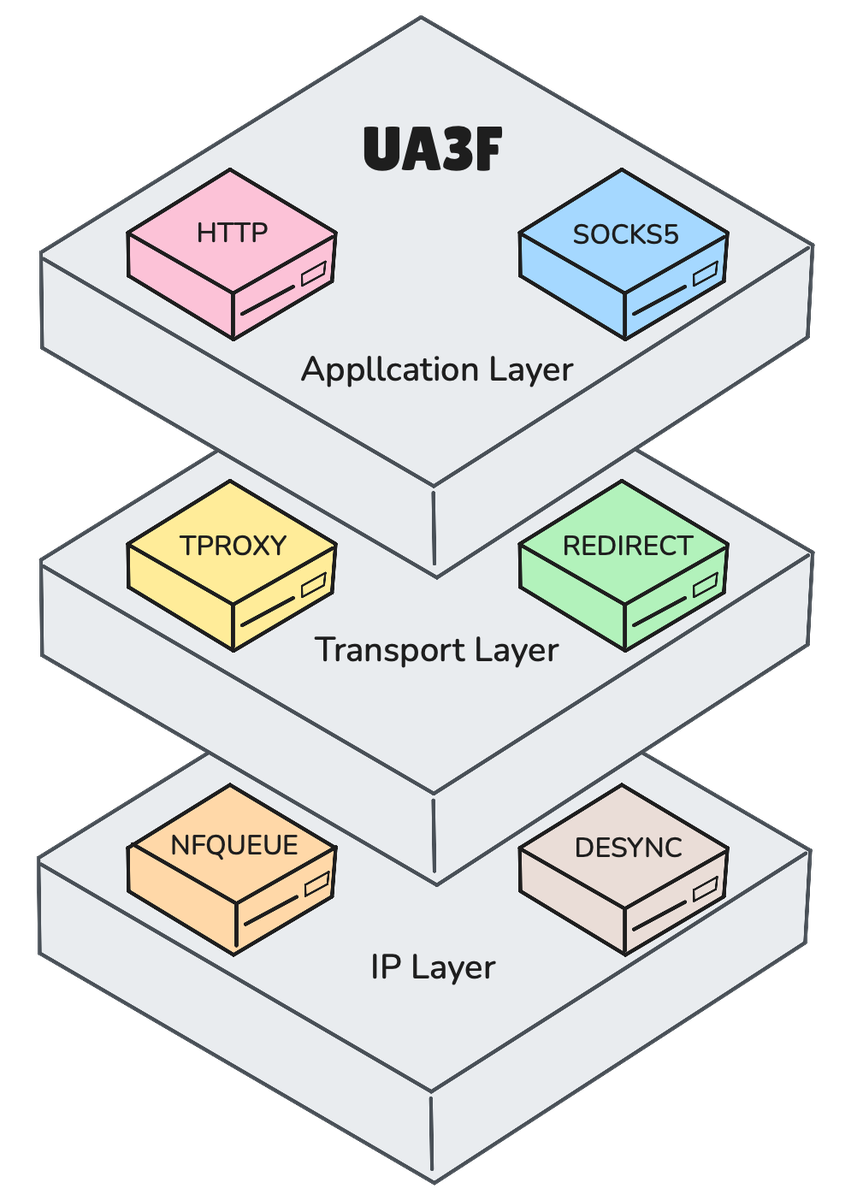 sunbk201/ua3f
Transparent HTTP(S) rewriting proxy supporting HTTP, SOCKS5, TPROXY, REDIRECT and NFQUEUE modes with HTTPS MitM, rule-based header/body rewriting and…
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
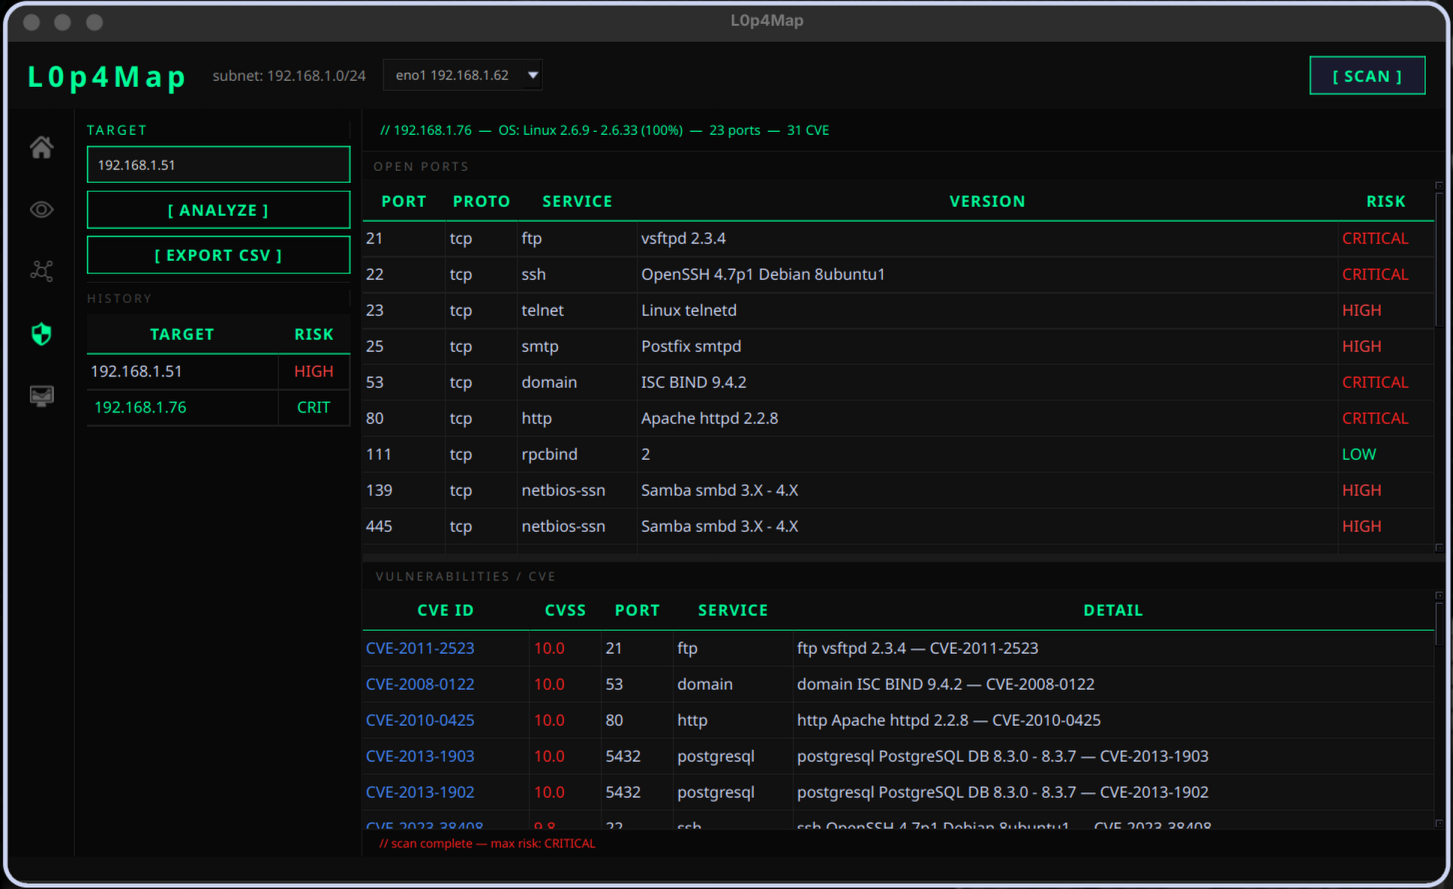 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
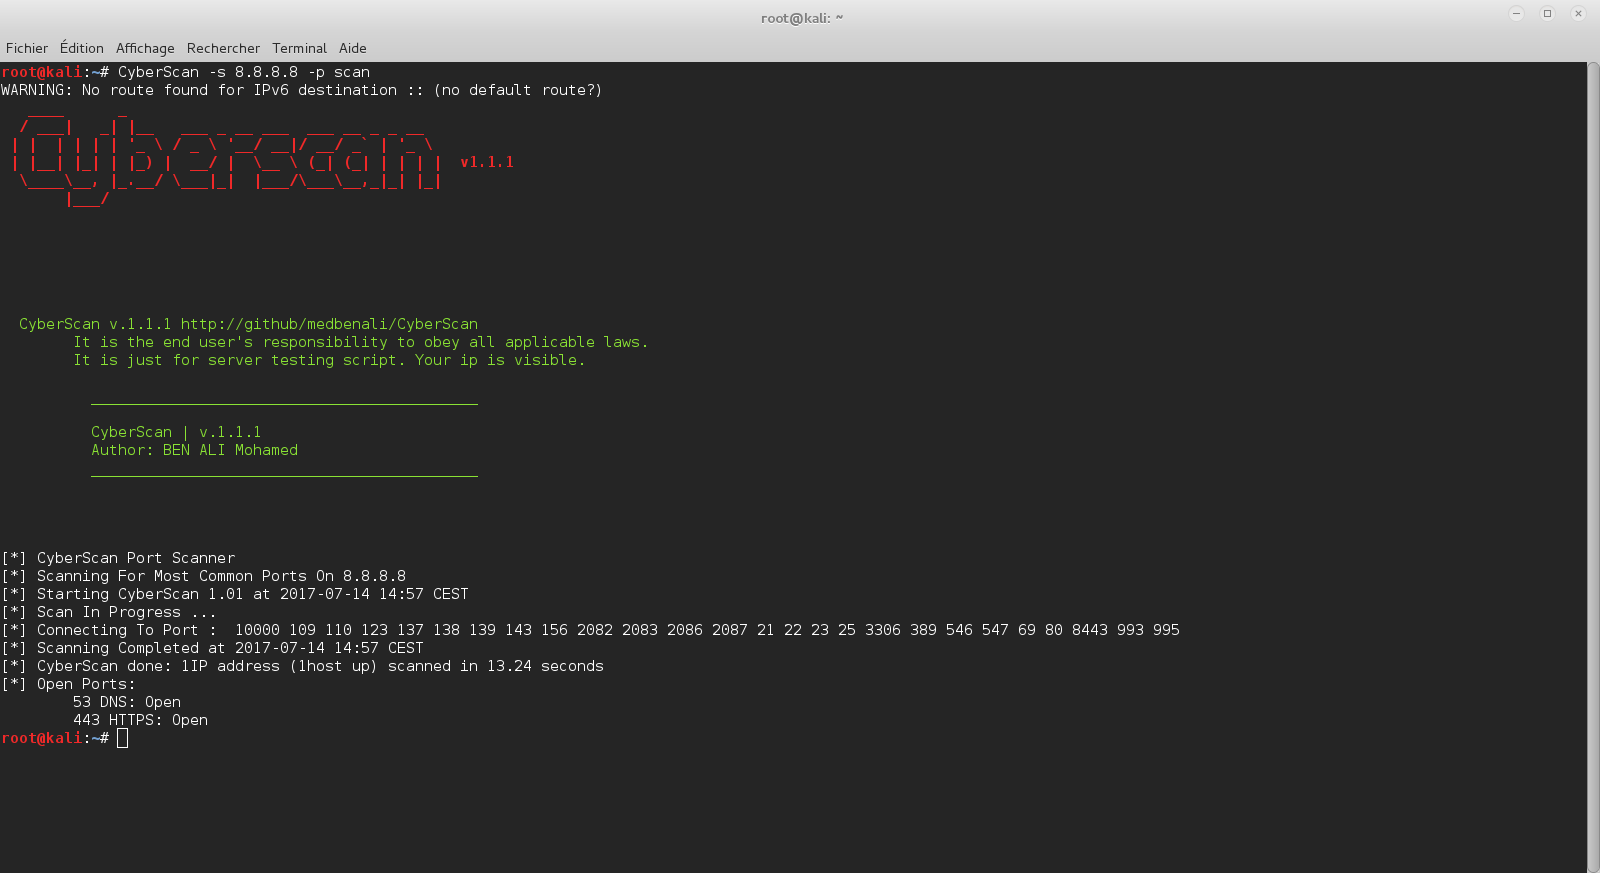 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…