

mcp-shark
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
ai-securityapi-securityconfiguration-auditing+7
172
mcp-shark/mcp-sharkWireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 garphengate/cve-2026-98432-defender-toolkit
Exposure audits, hunt queries and a validated interim mitigation for CVE-2026-98432, the use-after-free in the Linux IPv4 TCP handshake. Read-only…
 tc4dy/cve-2026-98432-poc-exploit
Toolkit for CVE-2026-98432 Linux TCP use-after-free: kernel patch checks, race oracle triggering, pcap UAF analysis, KASLR slide recovery, and…
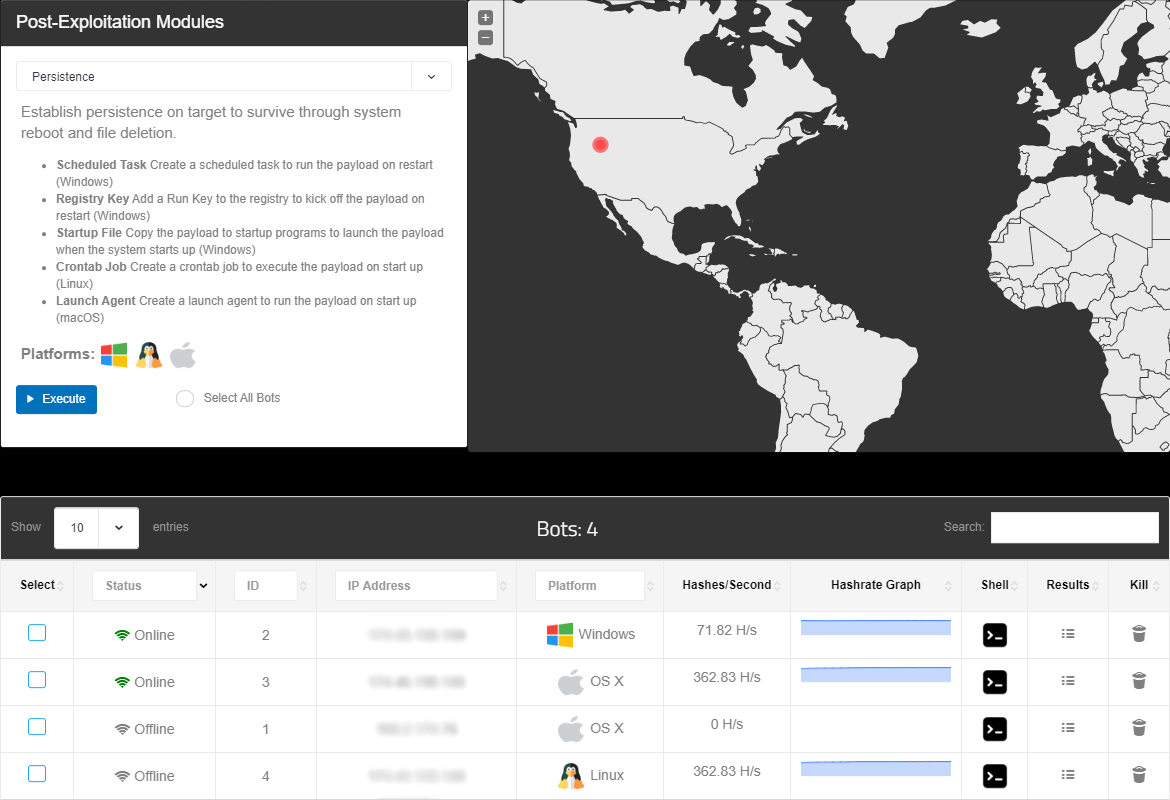 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 onyks-os/networksandboxengine
A deterministic network sandbox for testing nftables rules. It uses ephemeral Linux network namespaces (netns) and Scapy to validate firewall logic…
 mchorfa/csumguard
Restricted eBPF TC ingress guard, CO-RE detector, verified loader, and C11 VMM launch supervisor for CVE-2026-99999
 davetha/cve-2026-98432
Mitigation toolkit for the IPv4 TCP inet_opt/ireq_opt use-after-free: exposure audit, nft SYN-with-IP-options drop rules, tcpdump detection, and…
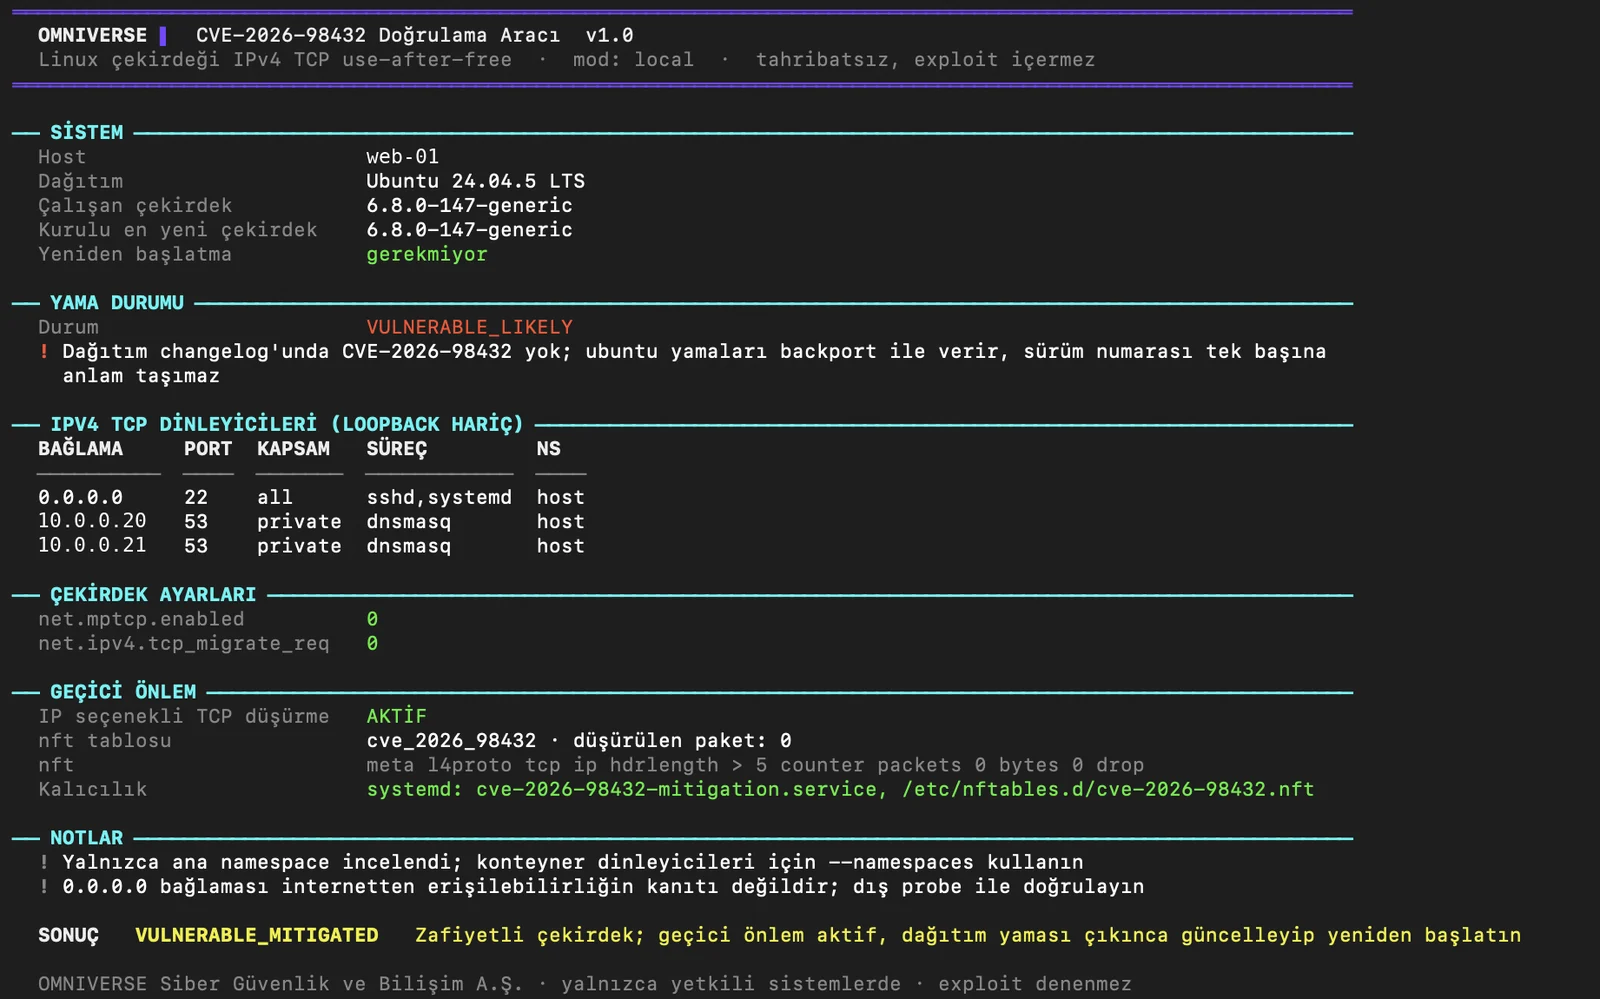 omniversetr/omnicheck_cve-2026-98432
Non-destructive checker for CVE-2026-98432 (Linux kernel TCP use-after-free): patch status, exposed listeners and mitigation verification. By…
 marcelofmatos/cve-2026-98432-check
Verifica se um host descarta SYN TCP IPv4 com IP options (mitigação do CVE-2026-98432)