
PiX-C2
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
command-and-controlnetwork-securitypacket-sniffing-analysis+3
robertdavis1/pix-c2Ping Exfiltration Command and Control (PiX-C2)
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 lele394/dnsnitch
DNSnitch is a local, privacy-first DNS server that puts you in complete control of your network traffic. Unlike passive blocklists, DNSnitch operates…
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
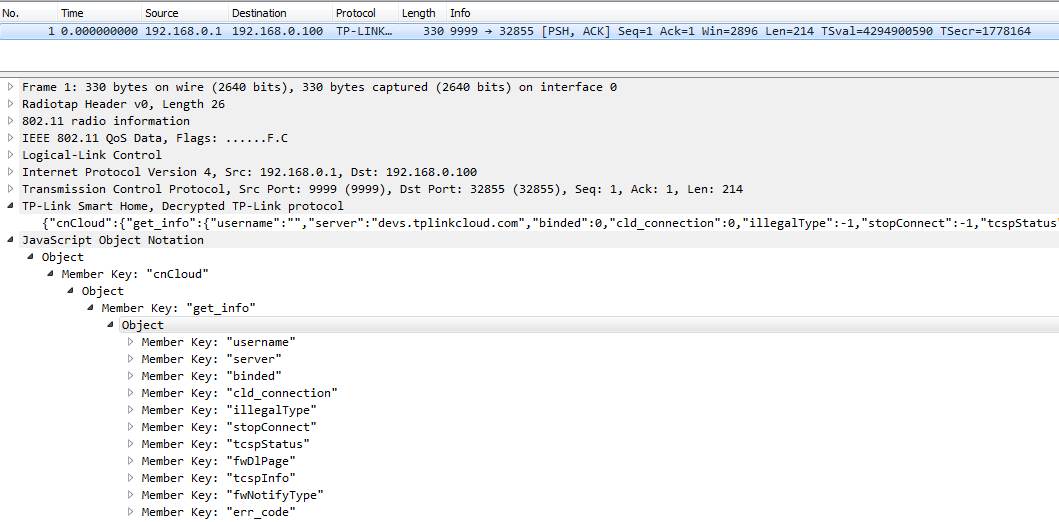 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 halildeniz/icmpwatch
ICMP packet sniffer for capturing, analyzing, and logging Echo Request/Reply packets with filtering, SQLite storage, and PCAP export for network…
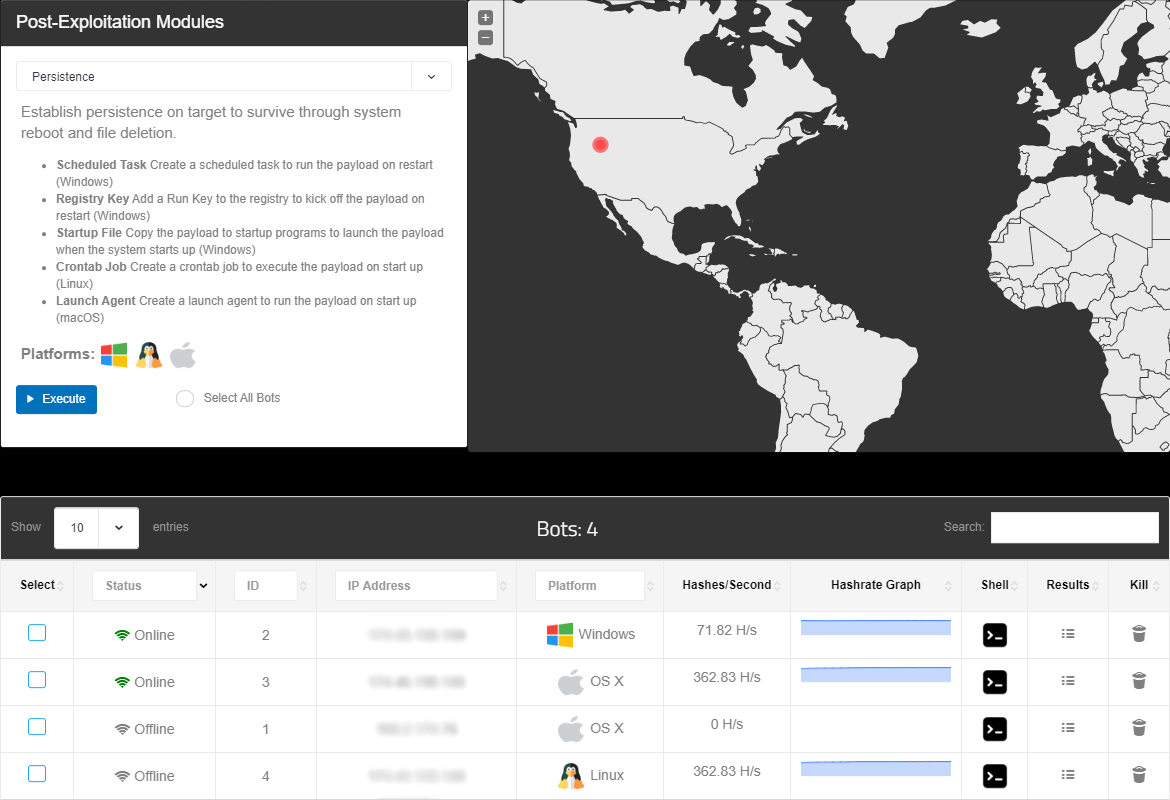 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 9lyph/cve-2022-43704
Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller
 nao-sec/ramnit_traffic_parser
Parsing Ramnit's traffic
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…