

eavesarp
 impostorkeanu/eavesarp
Analyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)
dns-analysisinformation-gatheringnetwork-security+2
70
impostorkeanu/eavesarpAnalyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)
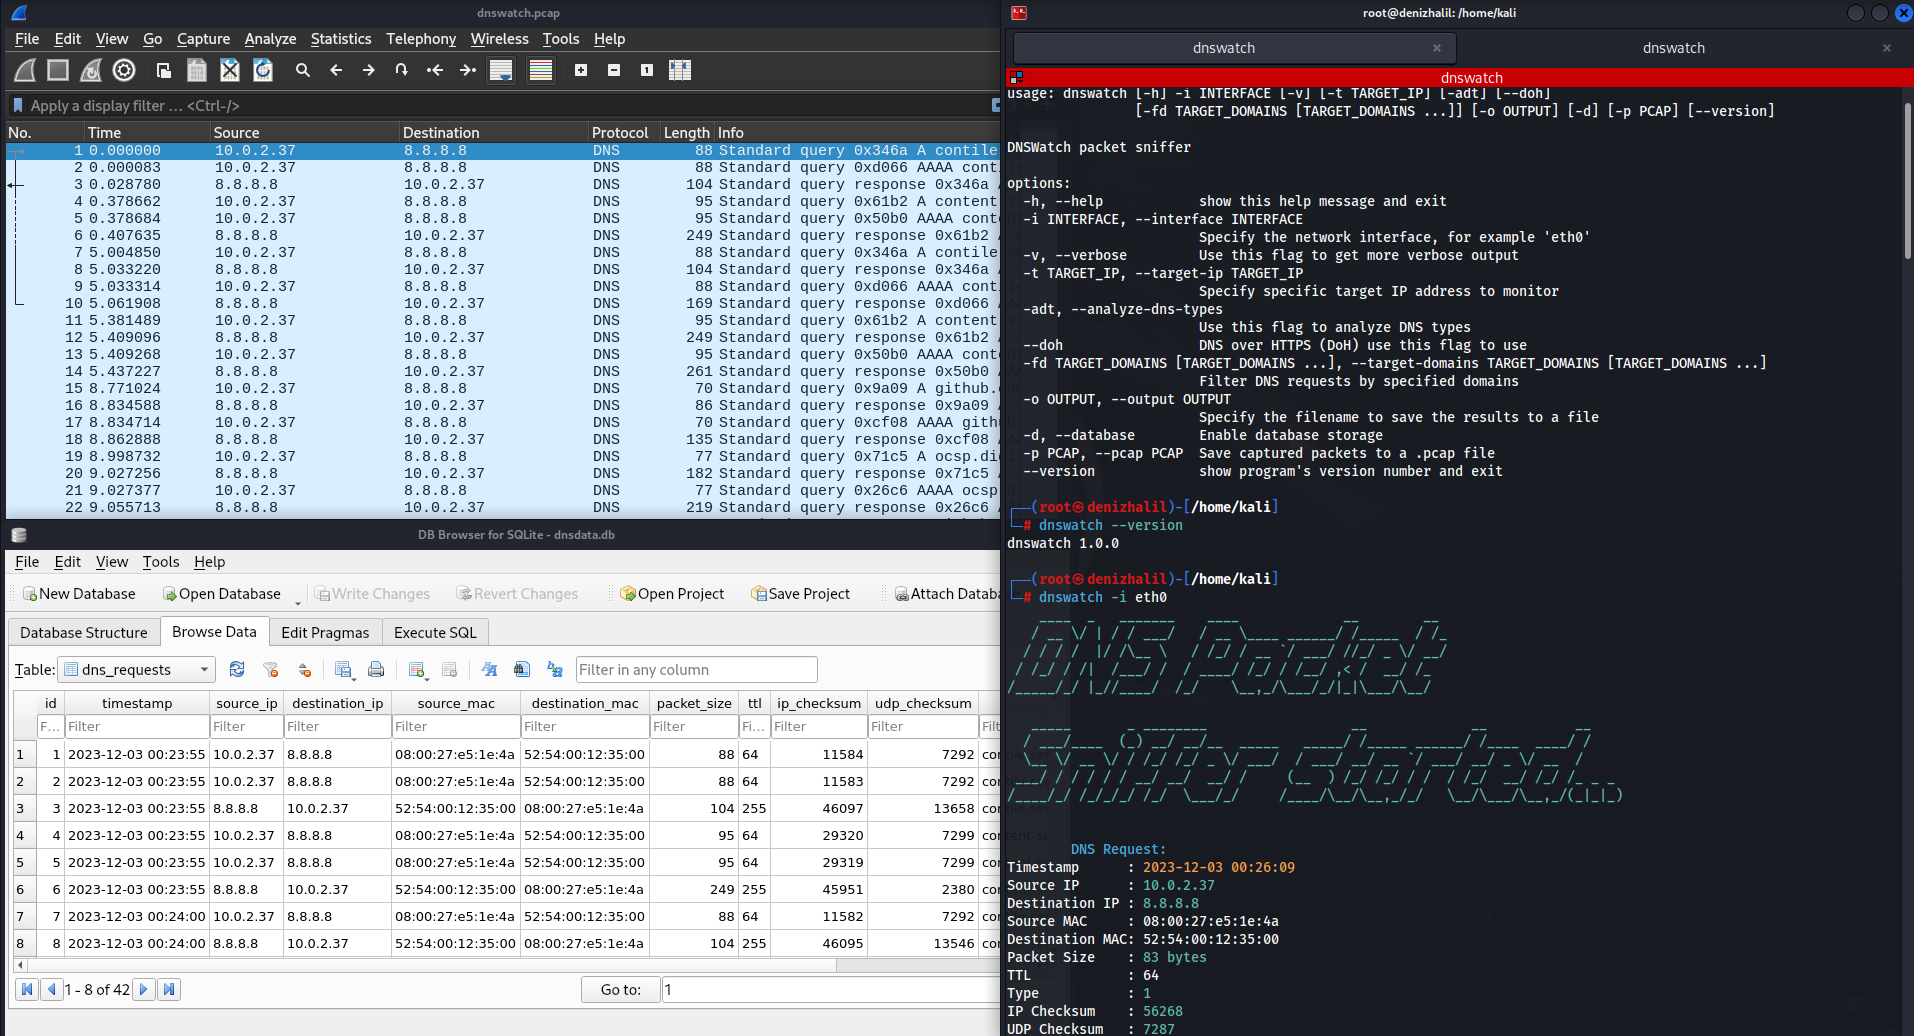 halildeniz/dnswatch
DNS traffic sniffer and analyzer for monitoring, filtering, and detecting anomalies in DNS queries. Features include PCAP export, DoH support, and a…
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 puniaze/portdog
Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…
 rnehra01/arp-validator
Security Tool to detect arp poisoning attacks
 nytrorst/netripper
NetRipper - Smart traffic sniffing for penetration testers
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
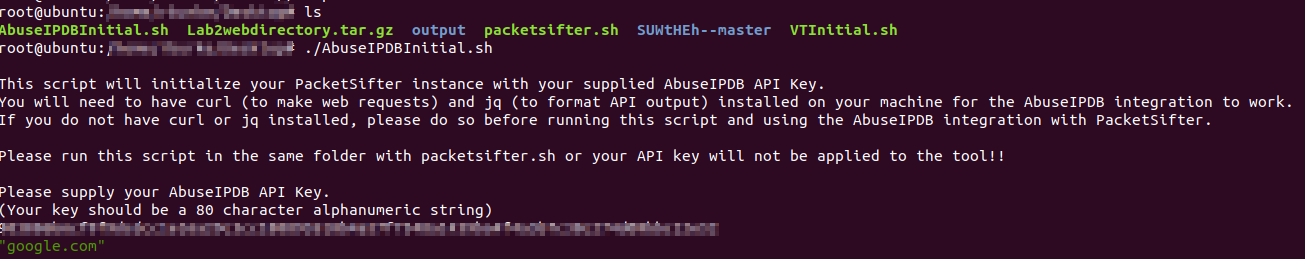 packetsifter/packetsiftertool
PacketSifter is a tool/script that is designed to aid analysts in sifting through a packet capture (pcap) to find noteworthy traffic. Packetsifter…
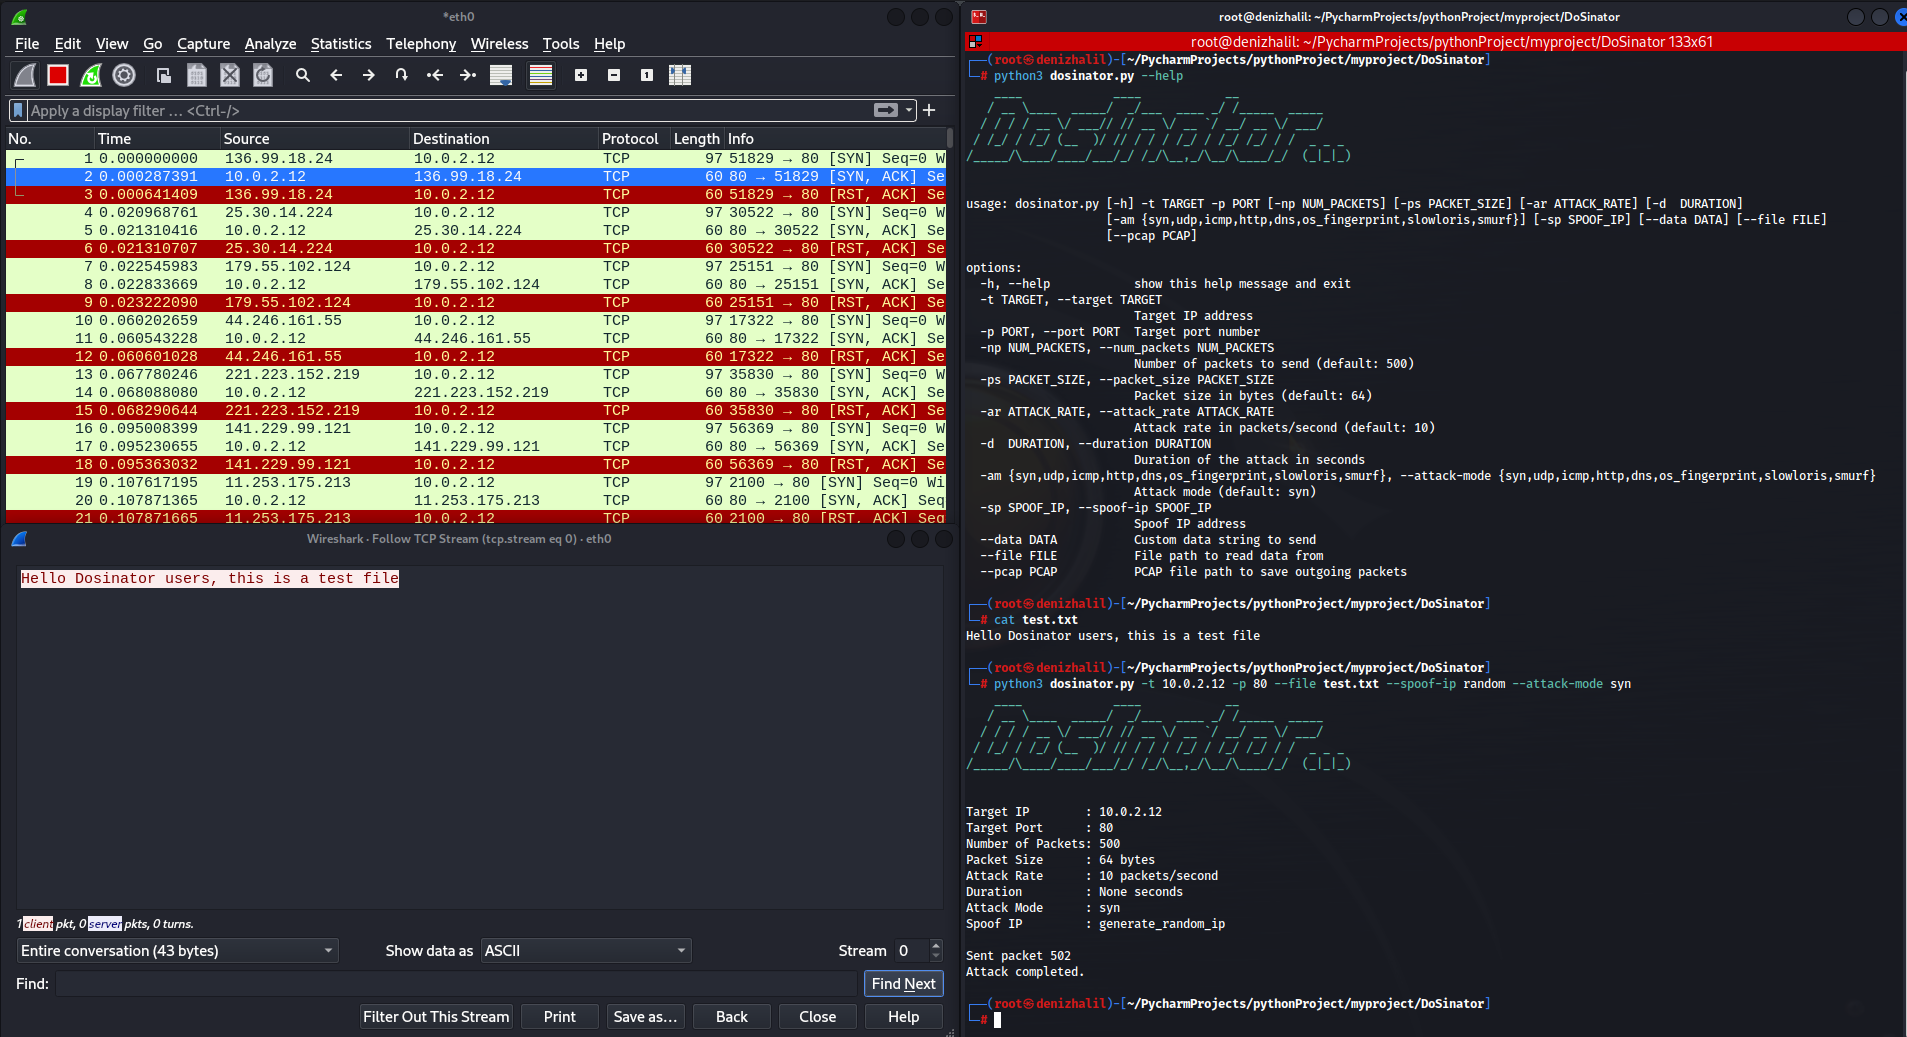 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
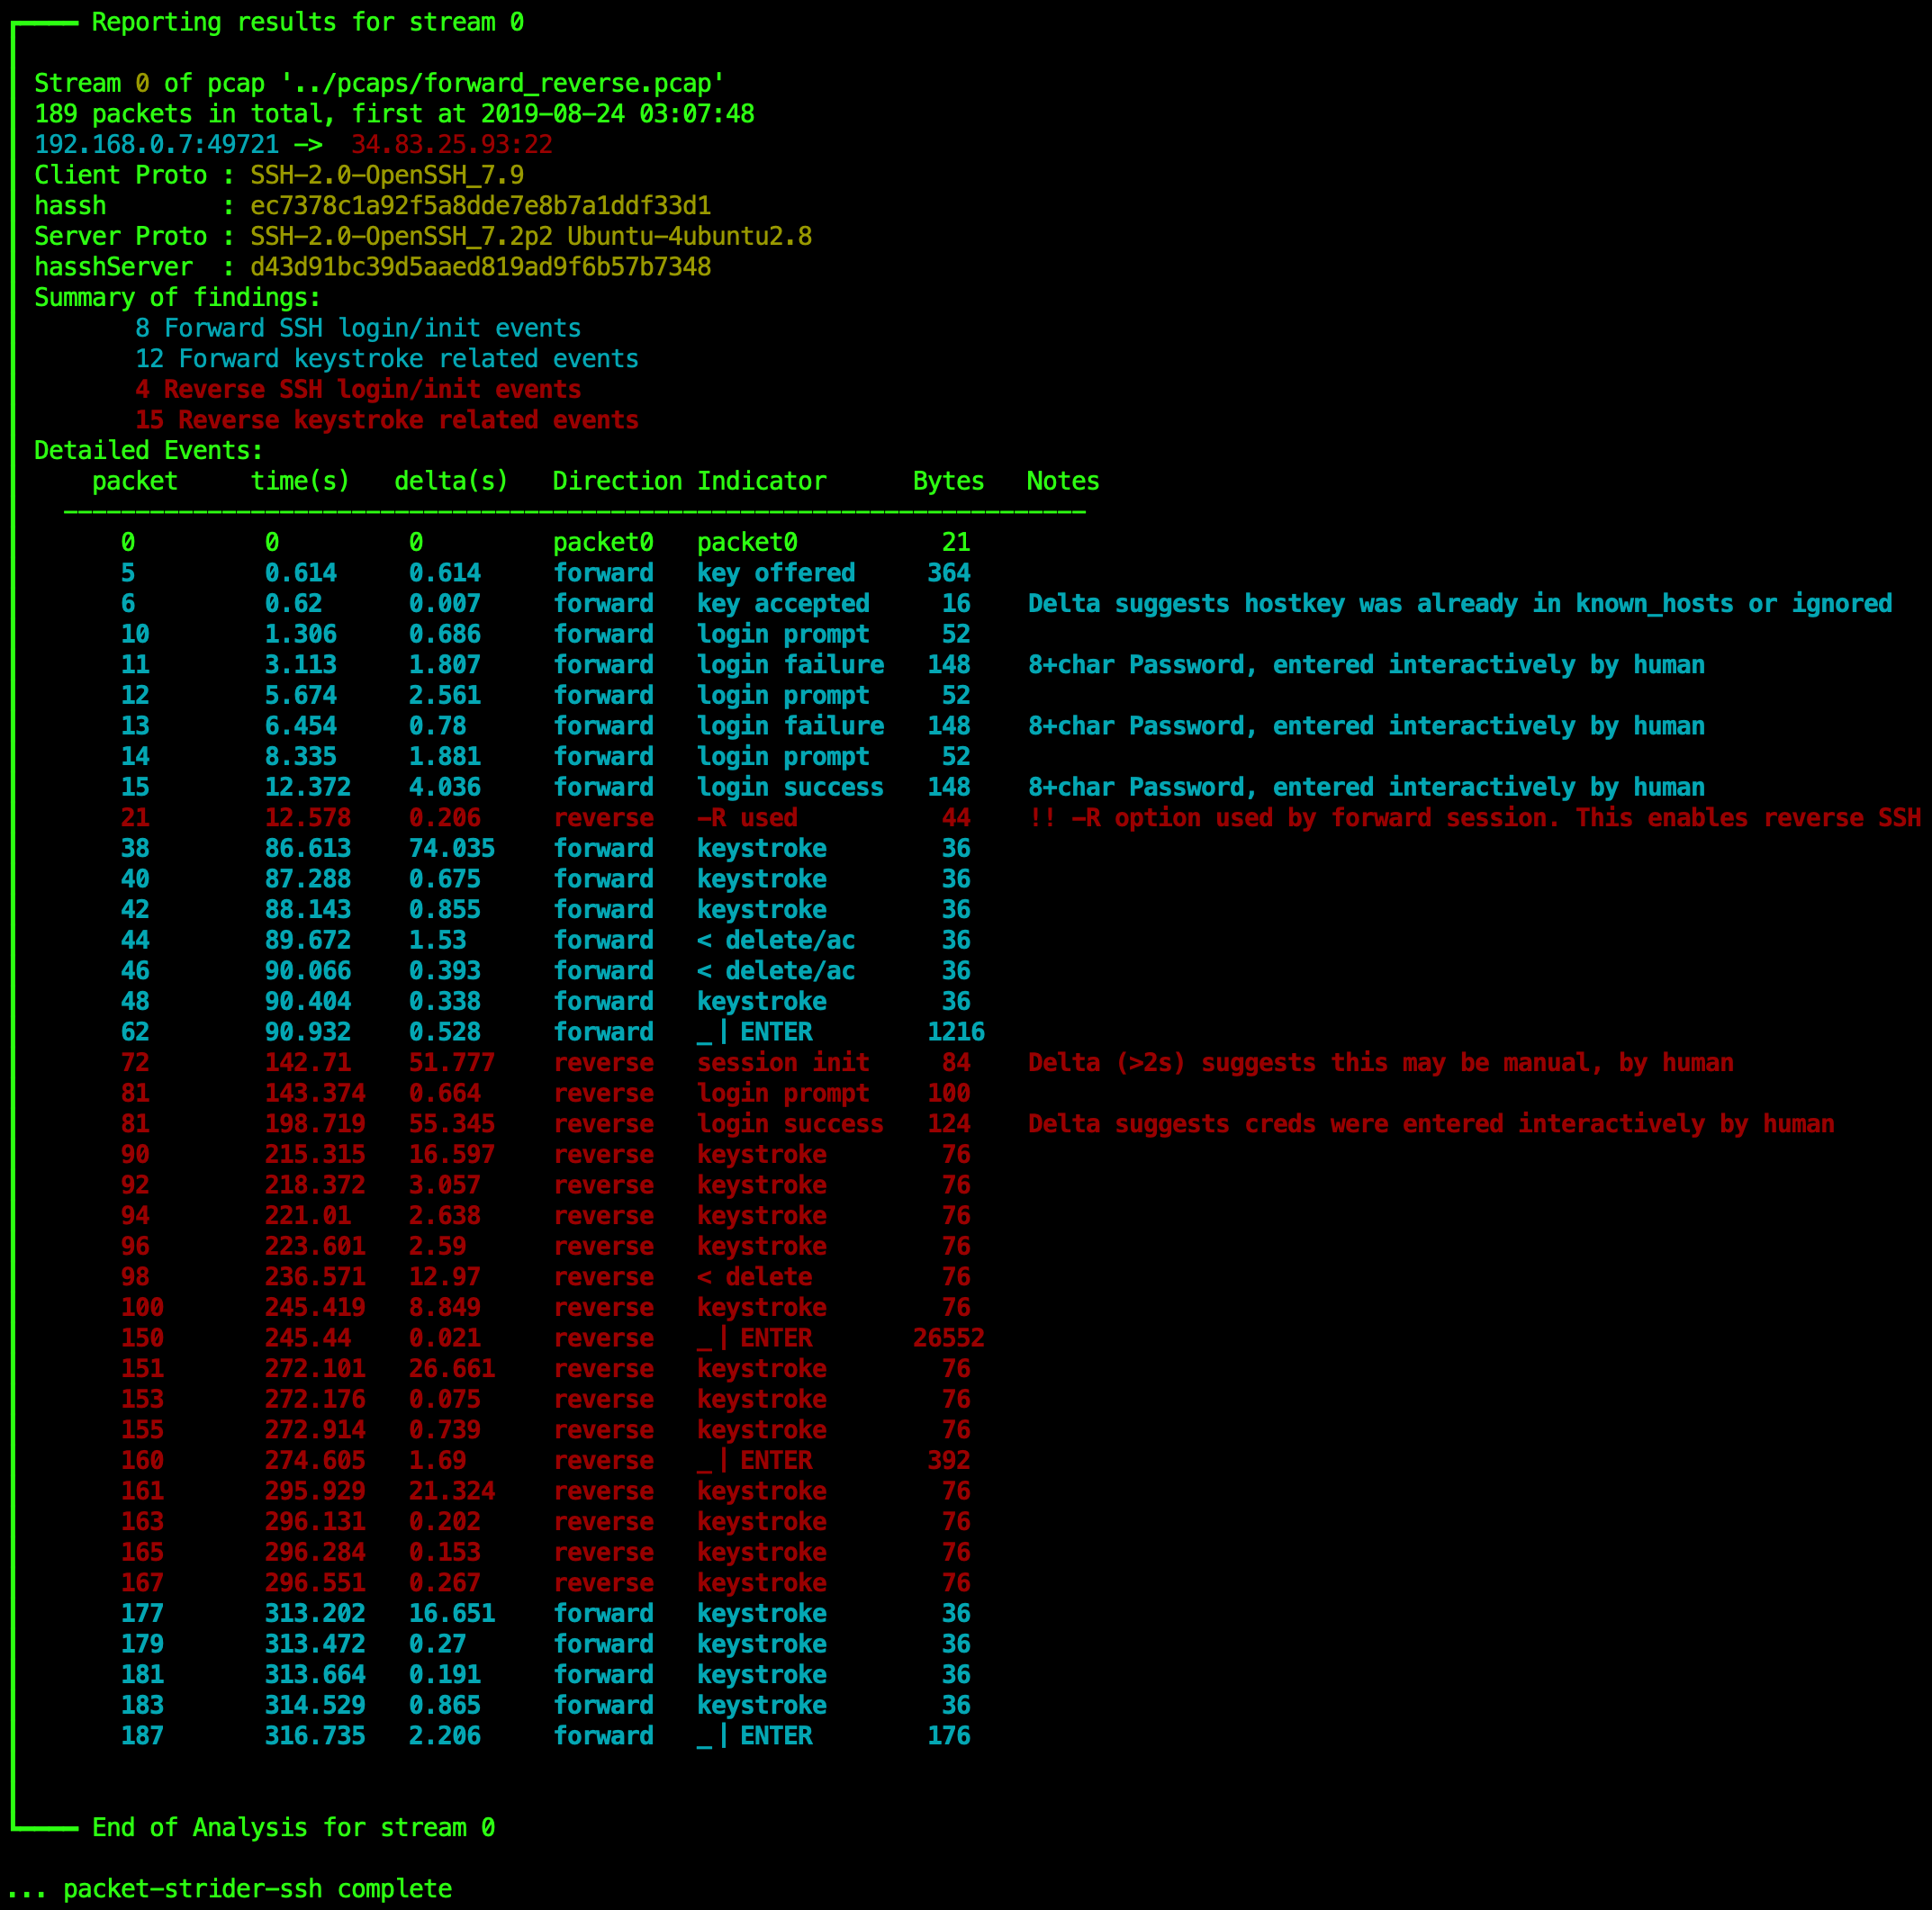 benjeems/packetstrider
A network packet forensics tool for SSH
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
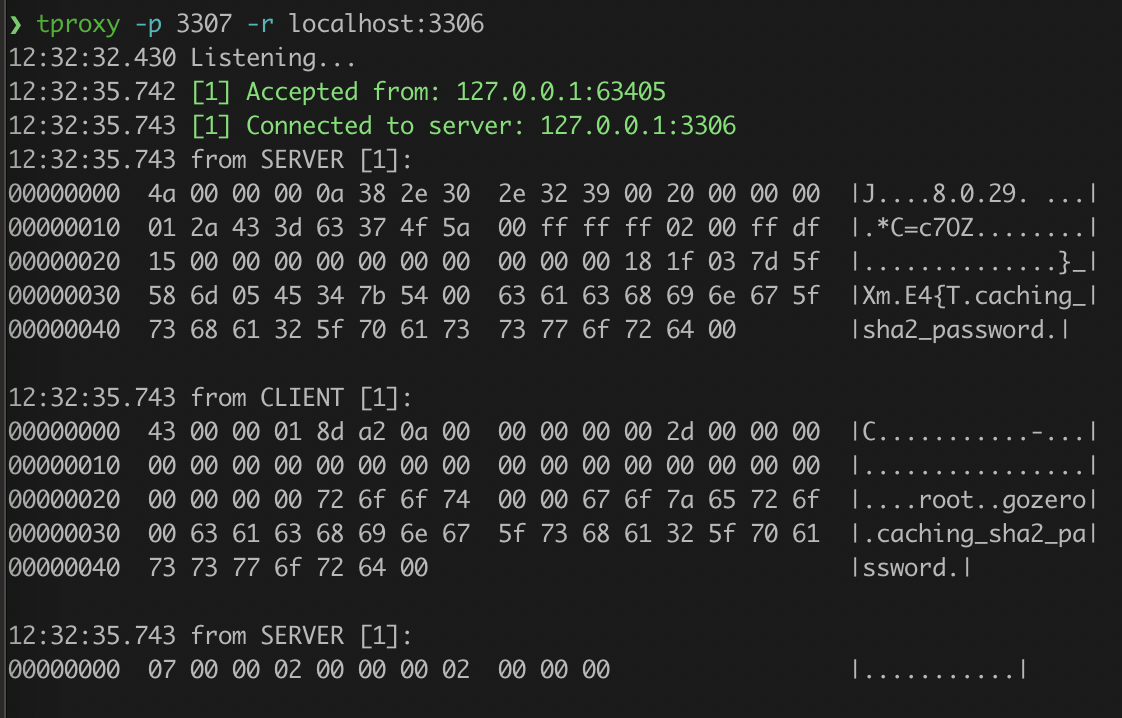 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.