
fatt
 0x4d31/fatt
FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
0x4d31/fattFATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.
 xuyw-seu/packetpatch
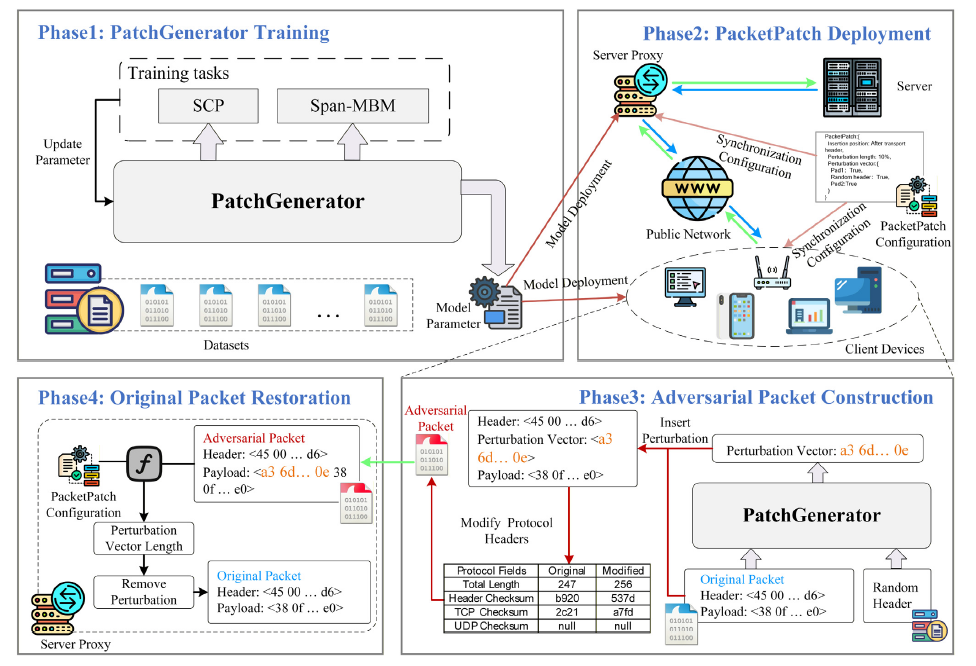
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 bastilleresearch/nrf-research-firmware
Firmware and research tools for Nordic Semiconductor nRF24LU1+ based USB dongles and breakout boards.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 corelight/zeek-spicy-wireguard
A Zeek Wireguard protocol analyzer based on Spicy.
 jminis/cve-2023-50257
This repository is for research purposes (2025 Sejong Univ. Capstone Design)
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 libnet/nemesis
A command-line network packet crafting and injection utility
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 corelight/zeek-spicy-ospf
A Zeek OSPF packet analyzer based on Spicy.
 corelight/zeek-spicy-stun
A Zeek STUN protocol analyzer based on Spicy.
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 jiaoxianjun/btle
Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).
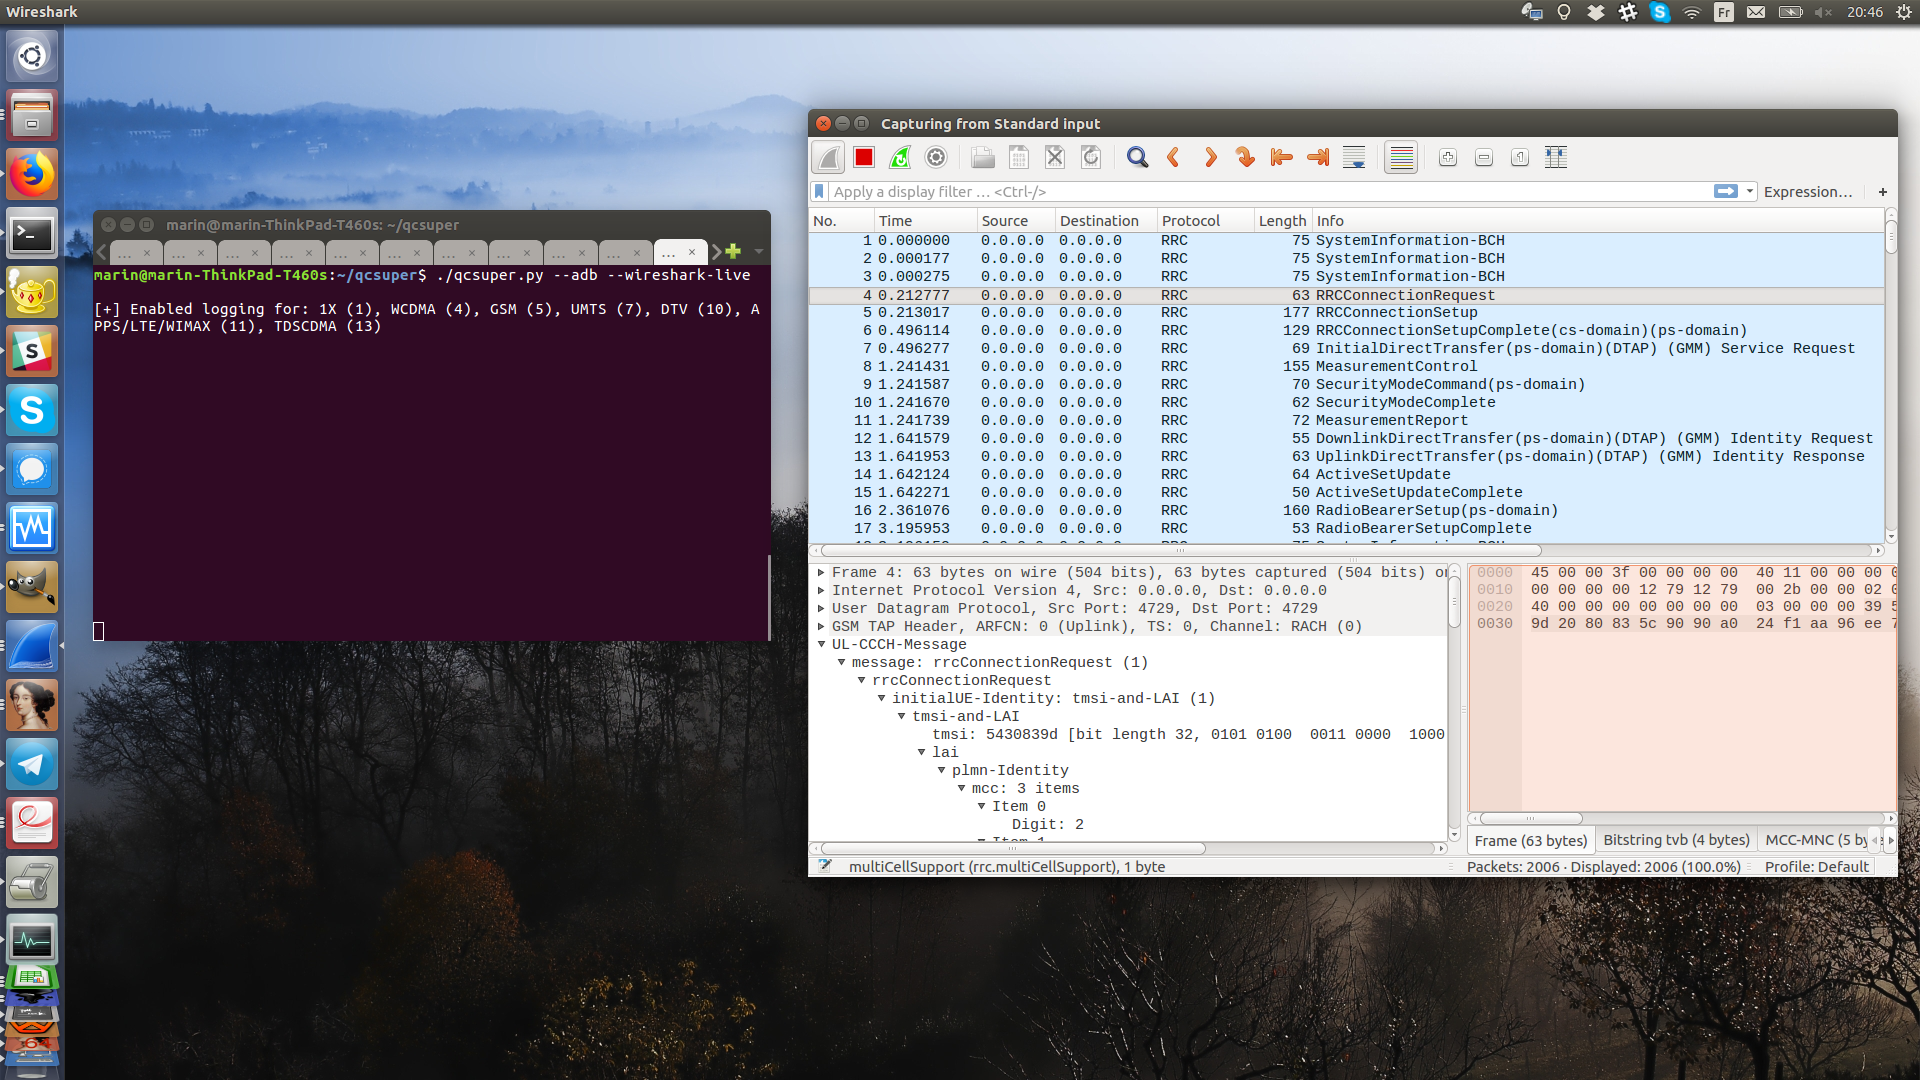 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 projectdiscovery/network-fingerprint
A fingerprint generation helper for nuclei network templates
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…