
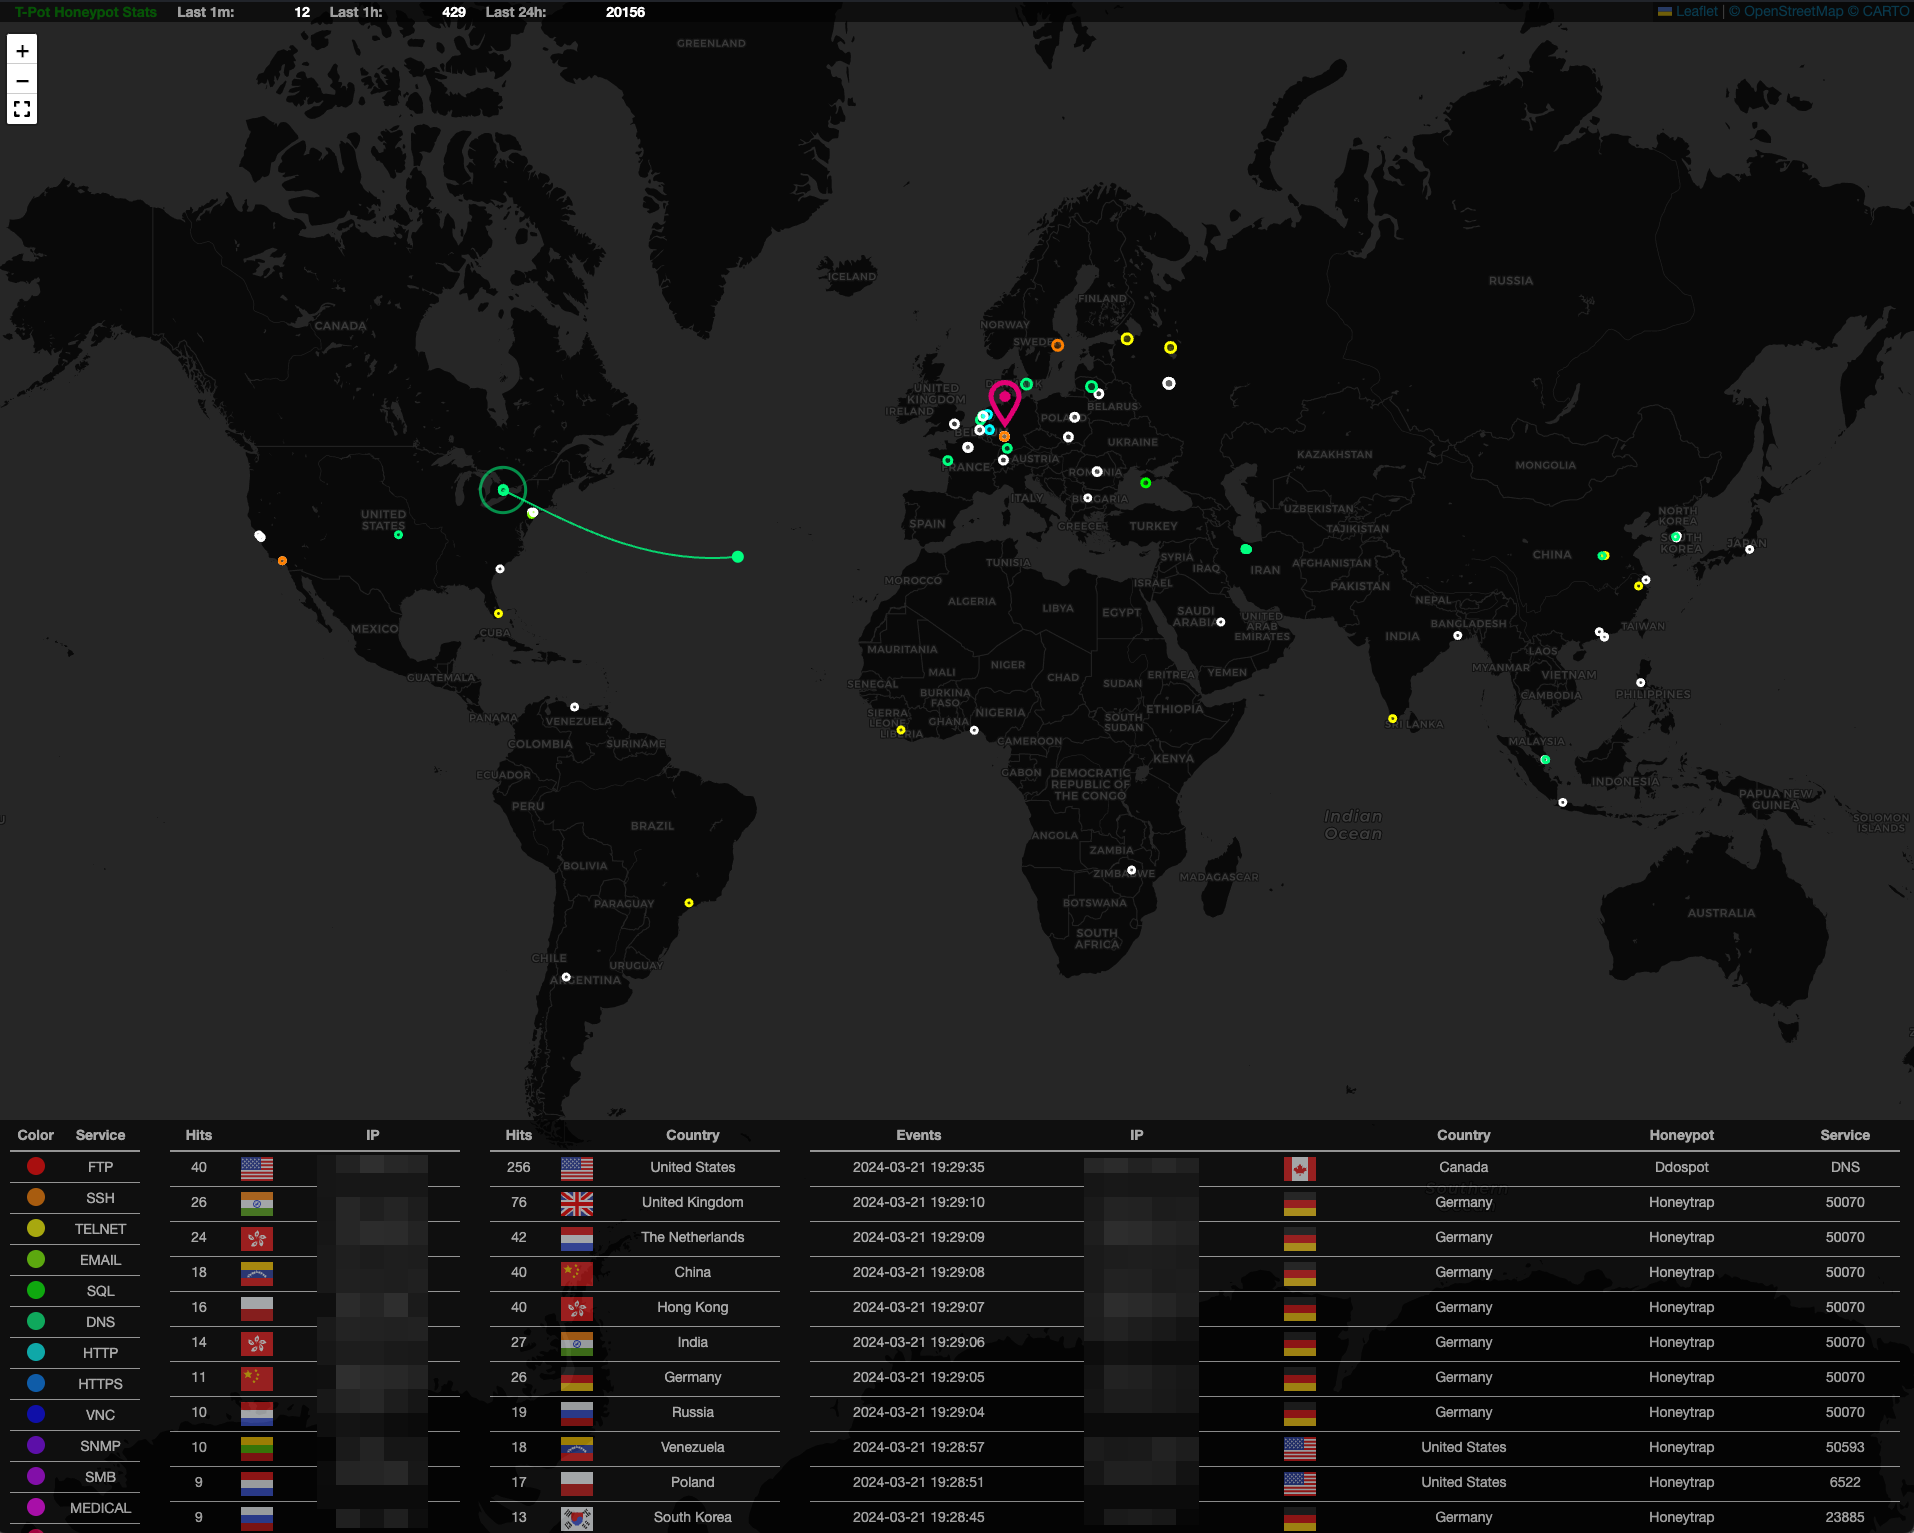
tpotce
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
telekom-security/tpotce🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 nicholasc03/dns-poisoning-triage-lab
Forensic triage of DNS cache poisoning in legacy hardware. Includes PCAP analysis of 839-byte unsolicited record injections, CVE-2025-40778 mapping,…
 alexanderortizscript/evillcode
Herramienta de auditoría y análisis de redes para Kali Linux.
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
 ashishraste/arp-dns-attacks
ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library
 mretallack/dronecamera
Drone HASAKEE FPV video app for Android
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
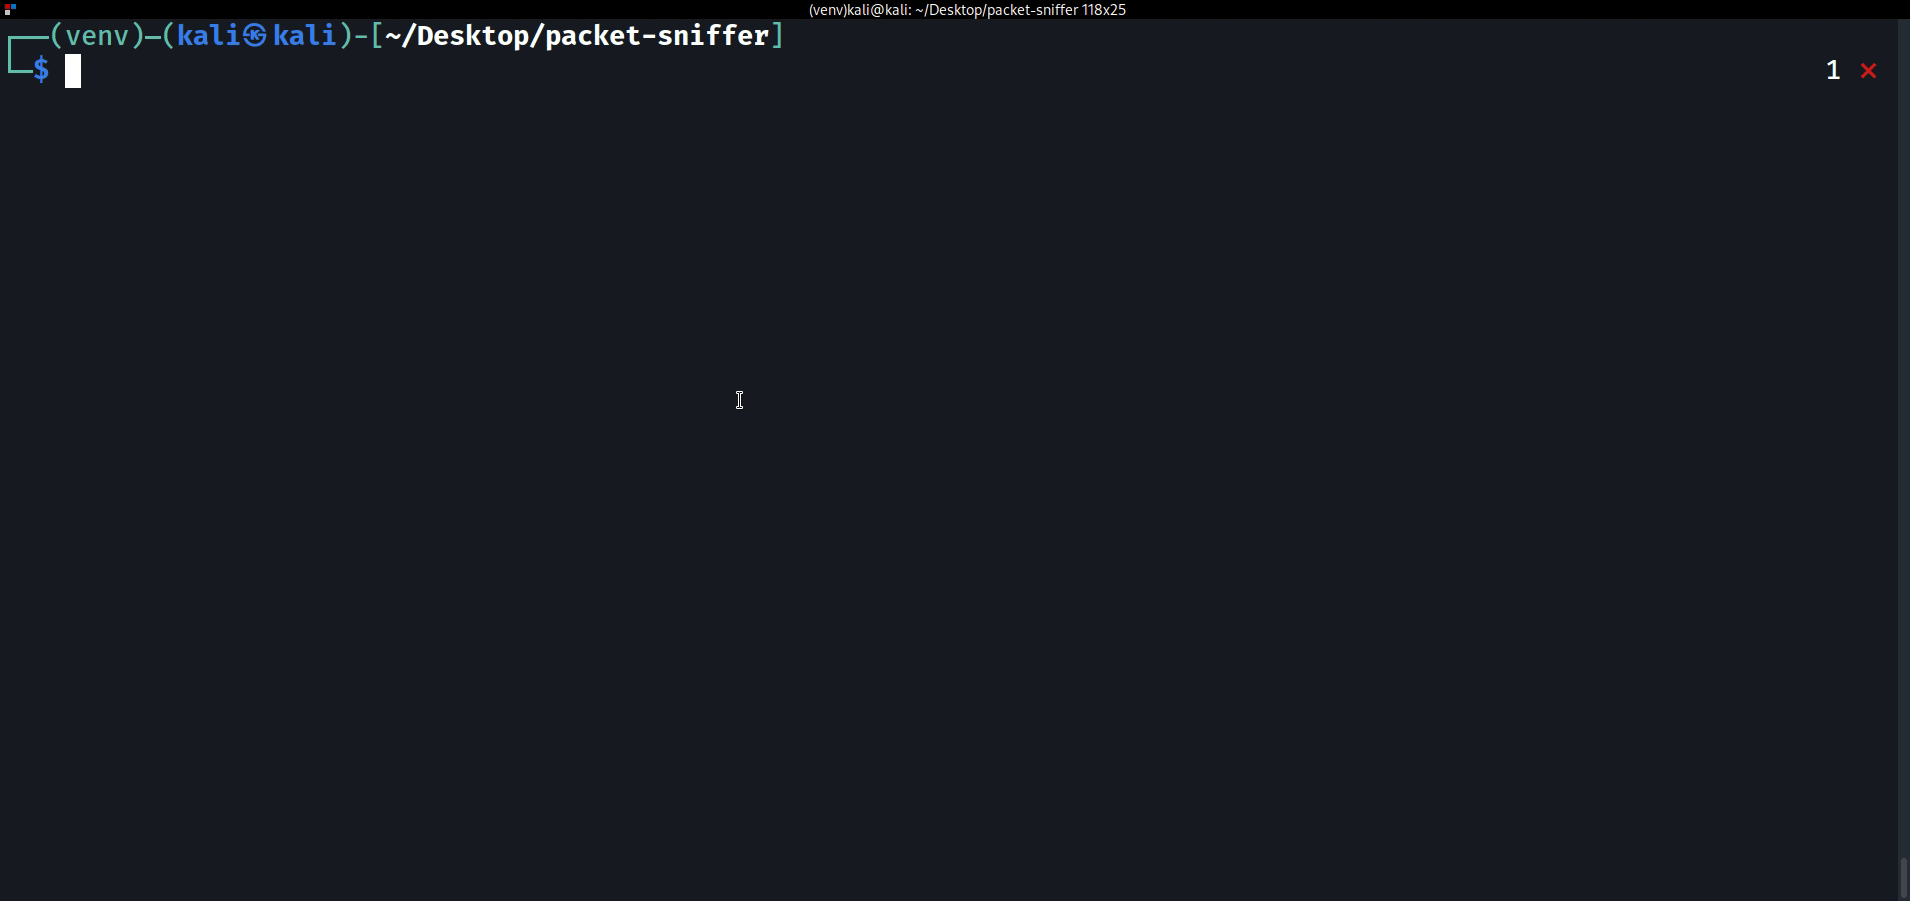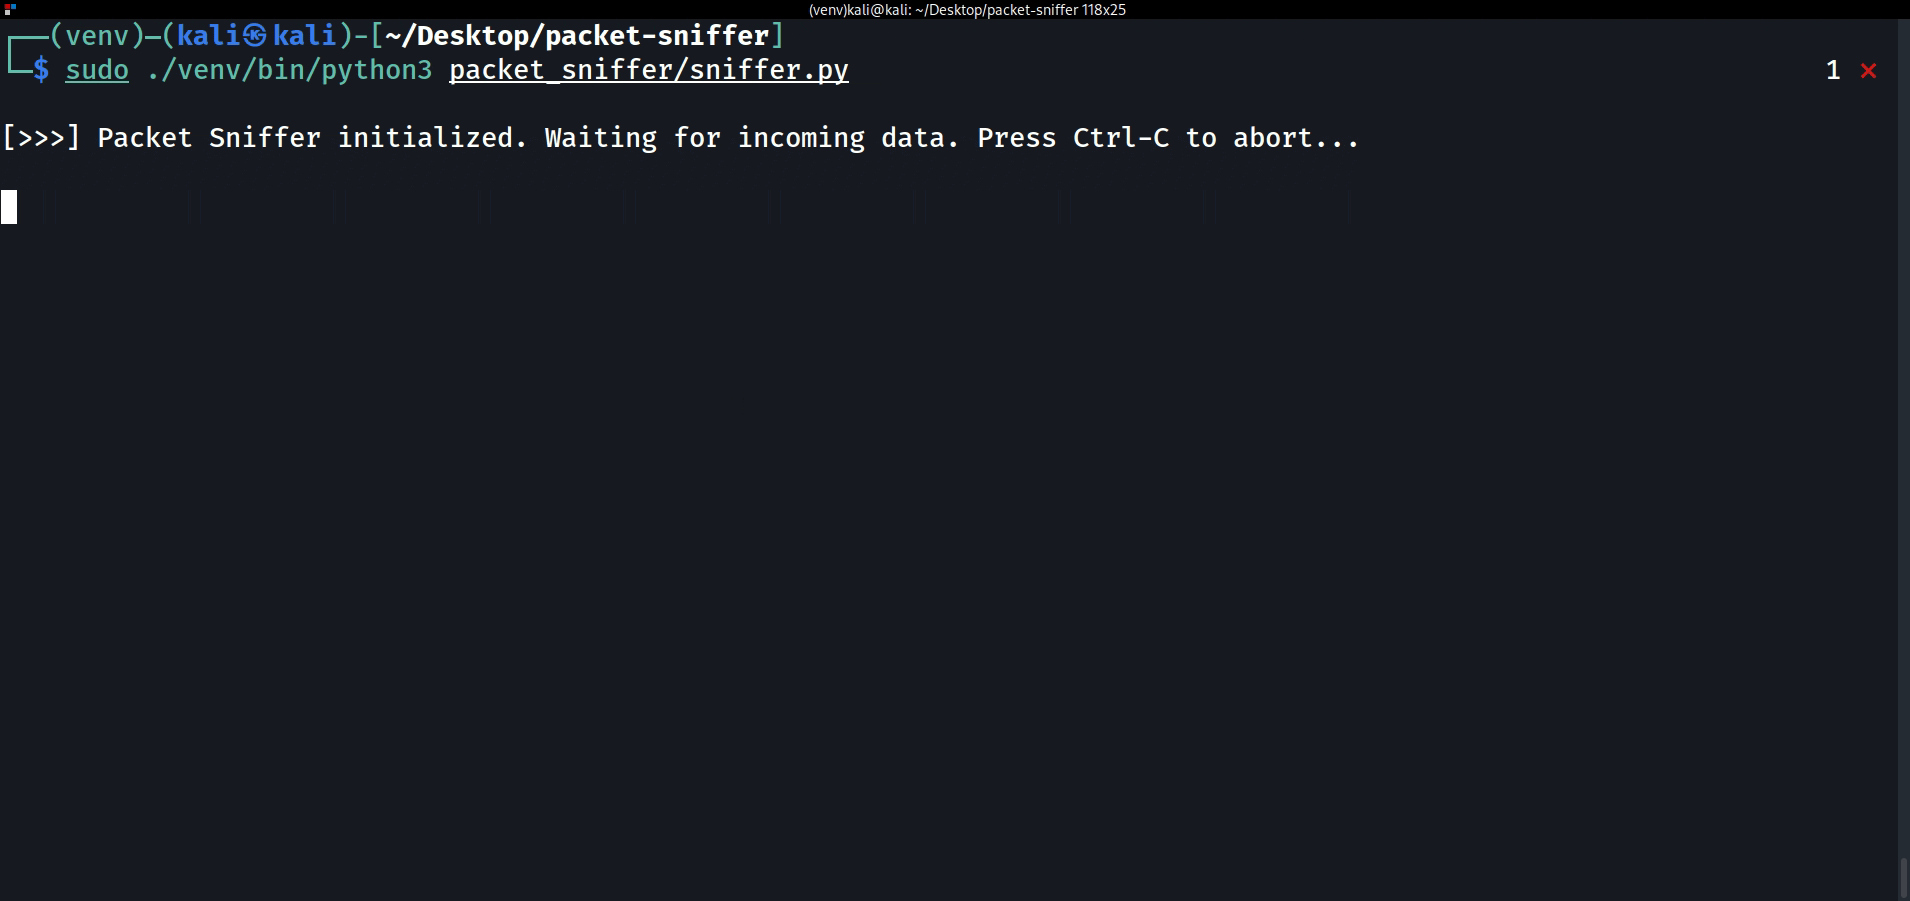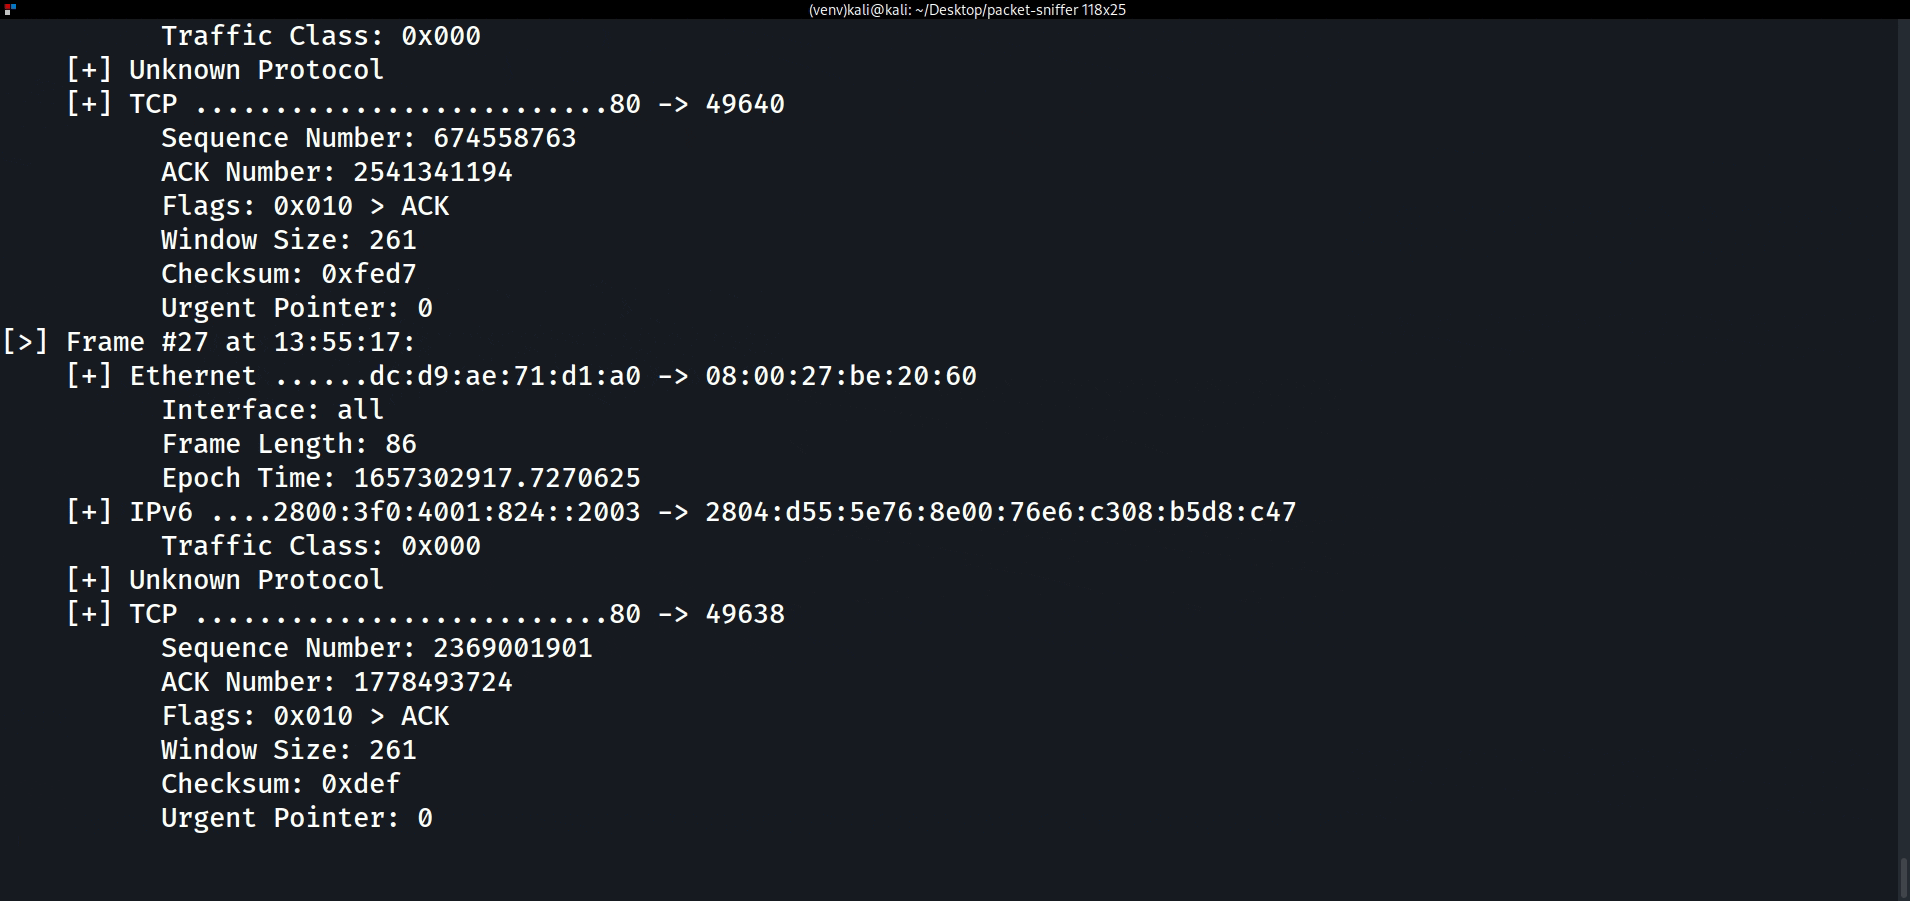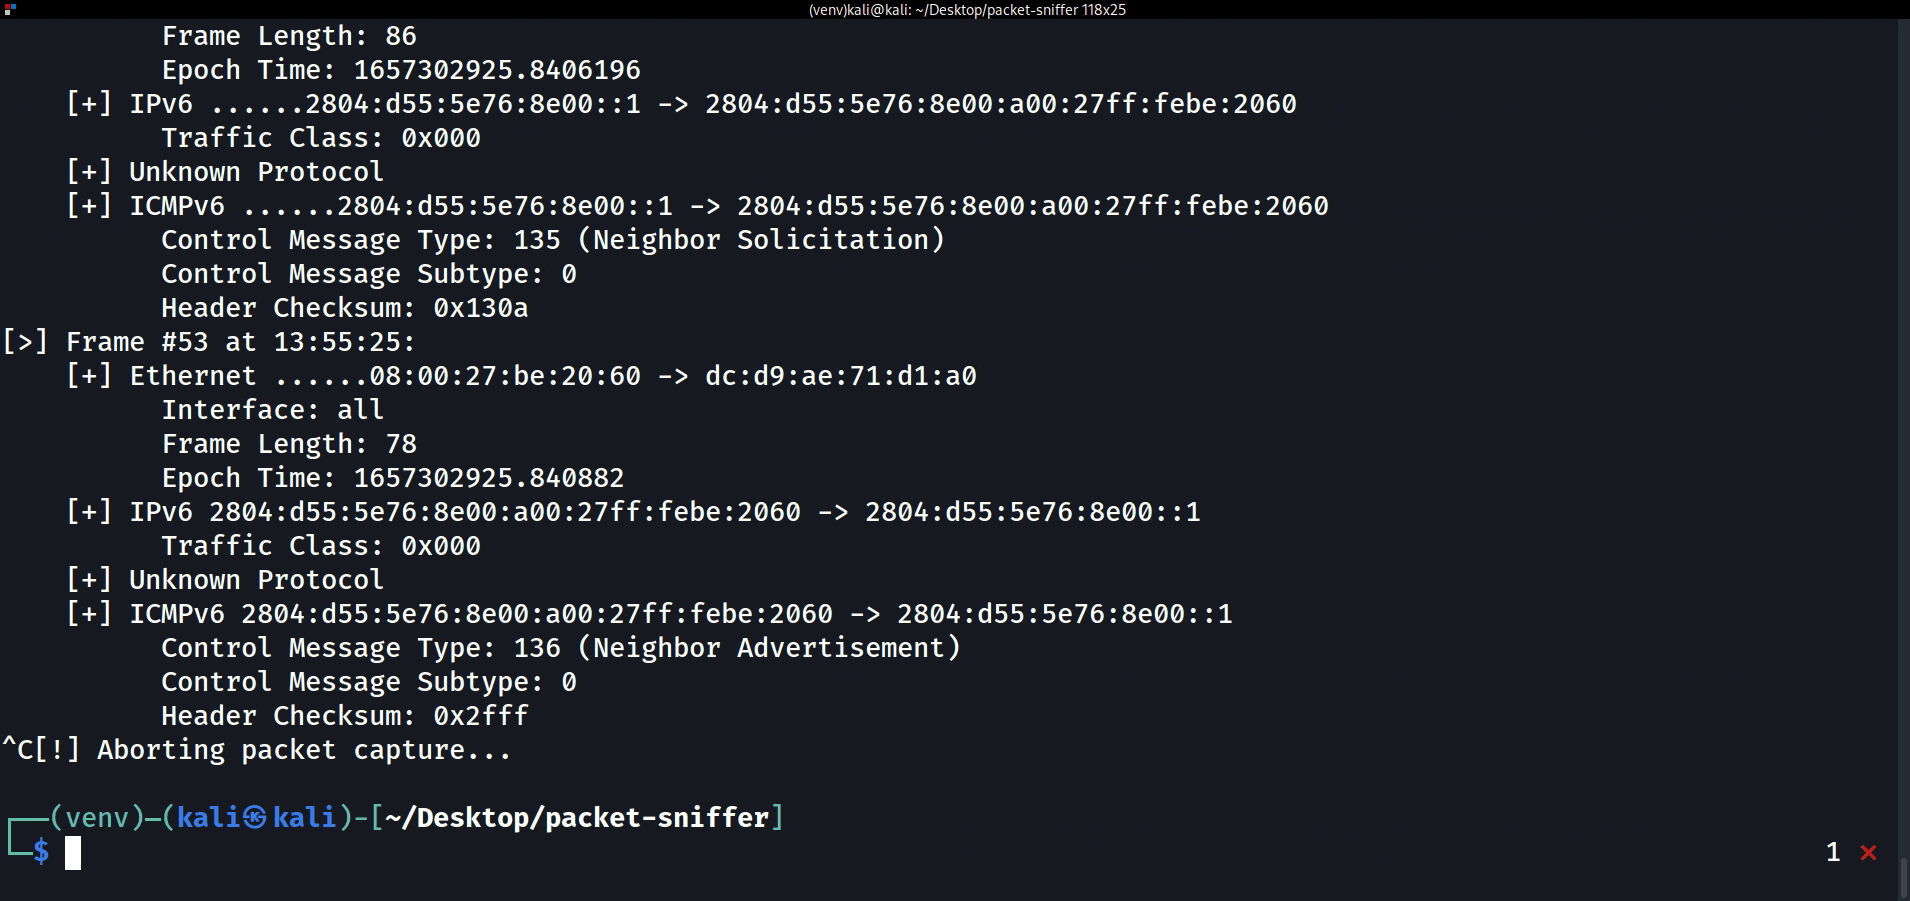 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols

 sahilmgandhi/iotshark
IotShark - Monitoring and Analyzing IoT Traffic
 amlight/ofp_sniffer
An OpenFlow sniffer to help network troubleshooting in production networks.
 cisc0-gif/netcrackpi
RPi3+ Network Cracker Setup Tool
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 emilebarnard242/pentest-metasploitable2
Structured penetration testing lab documenting a full attack chain from network reconnaissance to root exploitation of vsftpd 2.3.4 backdoor, with…