

bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
20.0k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
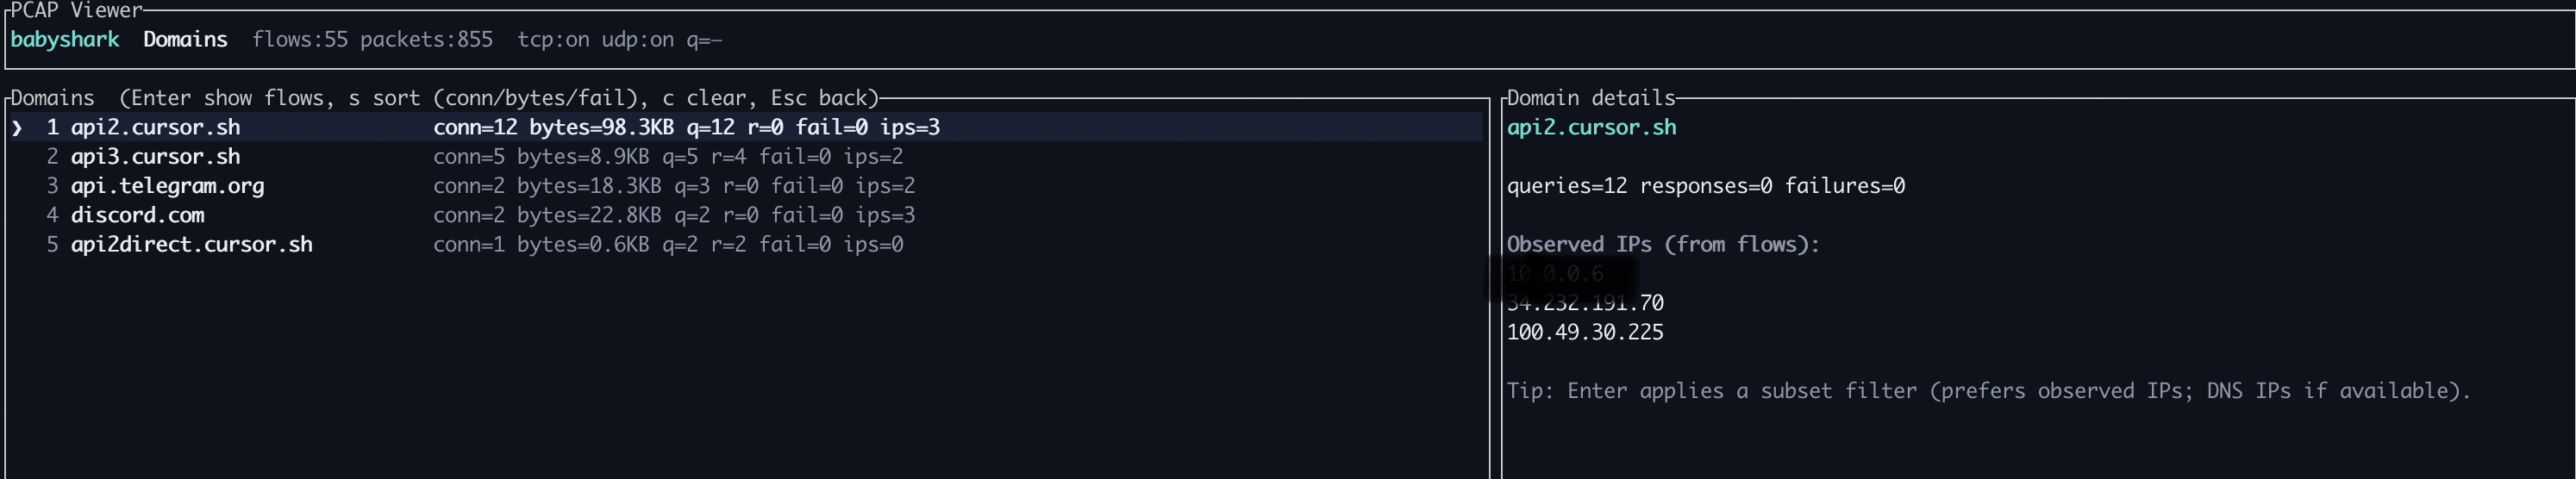 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 google/stenographer
Stenographer is a packet capture solution which aims to quickly spool all packets to disk, then provide simple, fast access to subsets of those…
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
 aelshimony-cloud/openwire-cve-2023-46604-investigation
Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…