
pysap
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
educationexploitationfuzzing+5
owasp/pysappysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
 vaelwolf/cve-2022-1388
-- FOR EDUCATIONAL USE ONLY -- Proof-of-Concept RCE for CVE-2022-1388, plus some added functionality for blue and red teams
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…
 amlight/ofp_sniffer
An OpenFlow sniffer to help network troubleshooting in production networks.
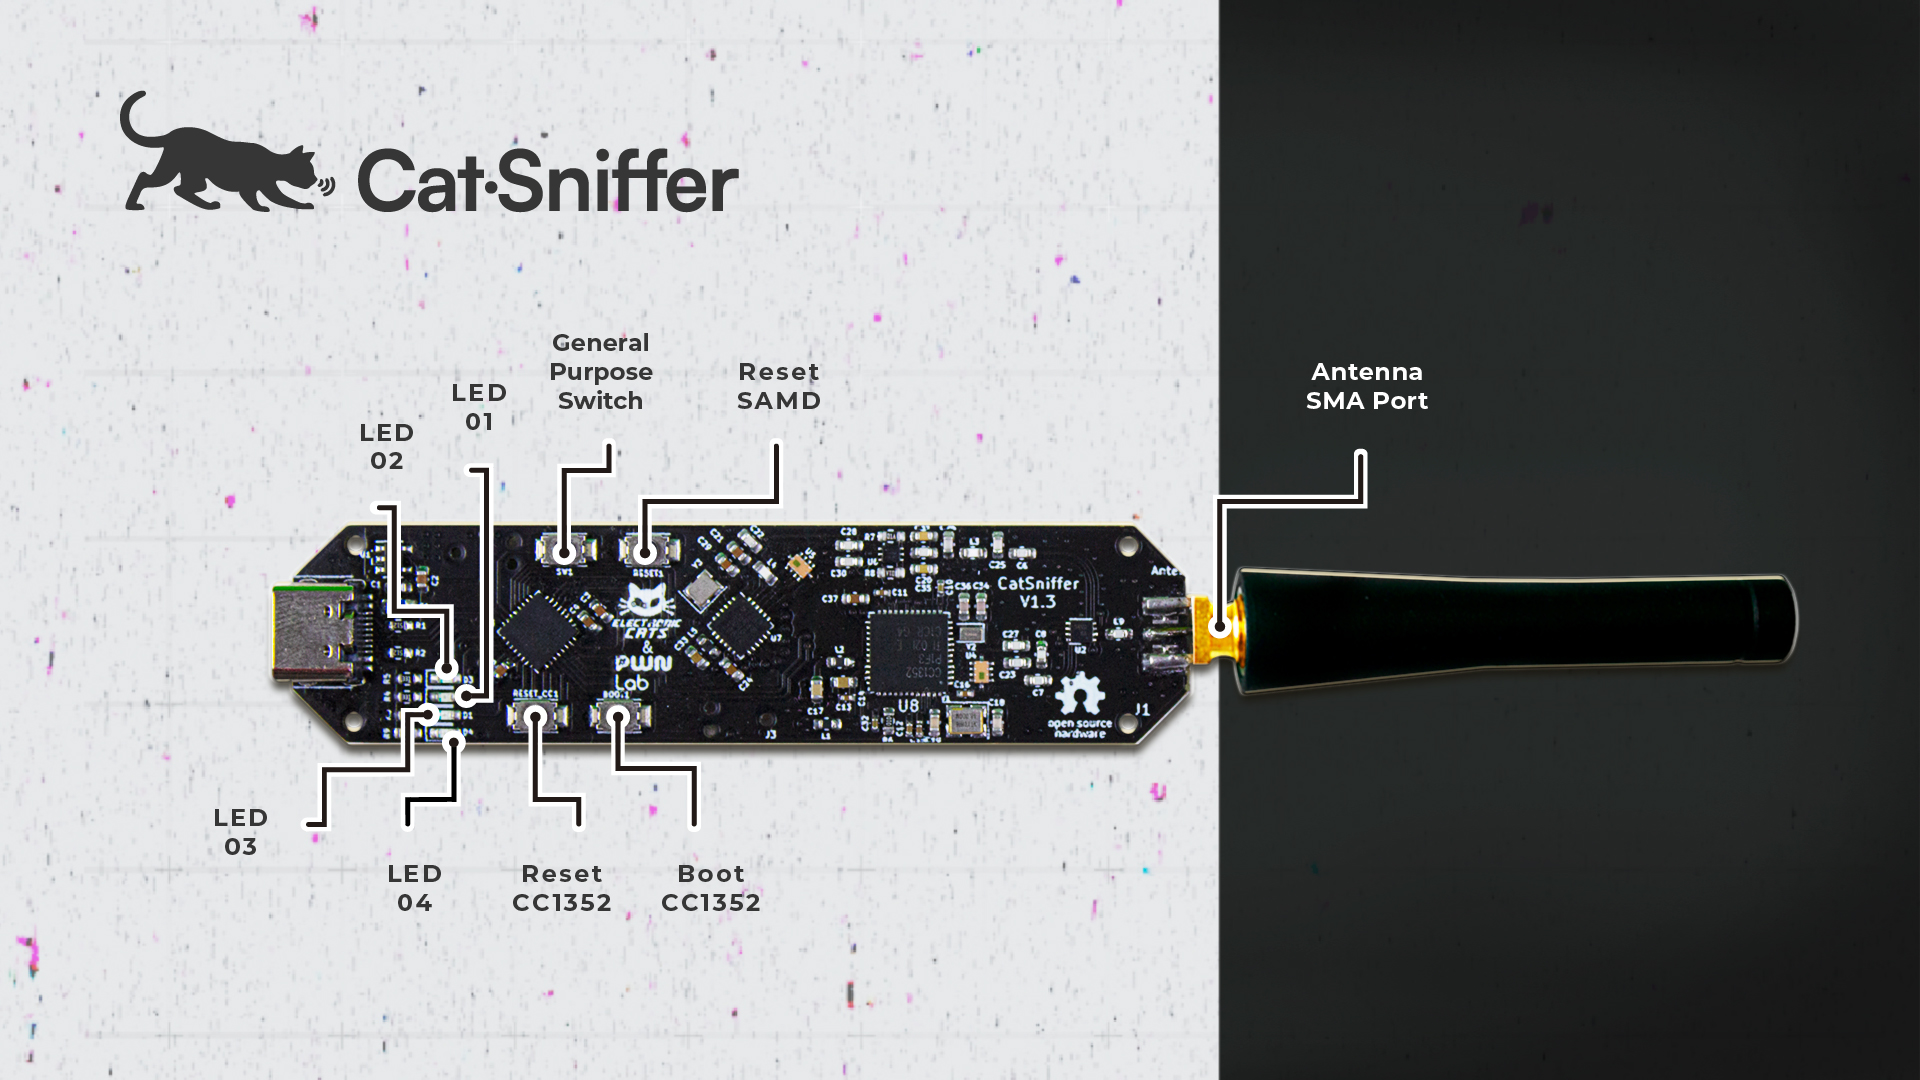 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
 alkersan/om-research
Documenting Osmo Mobile BLE protocol
 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
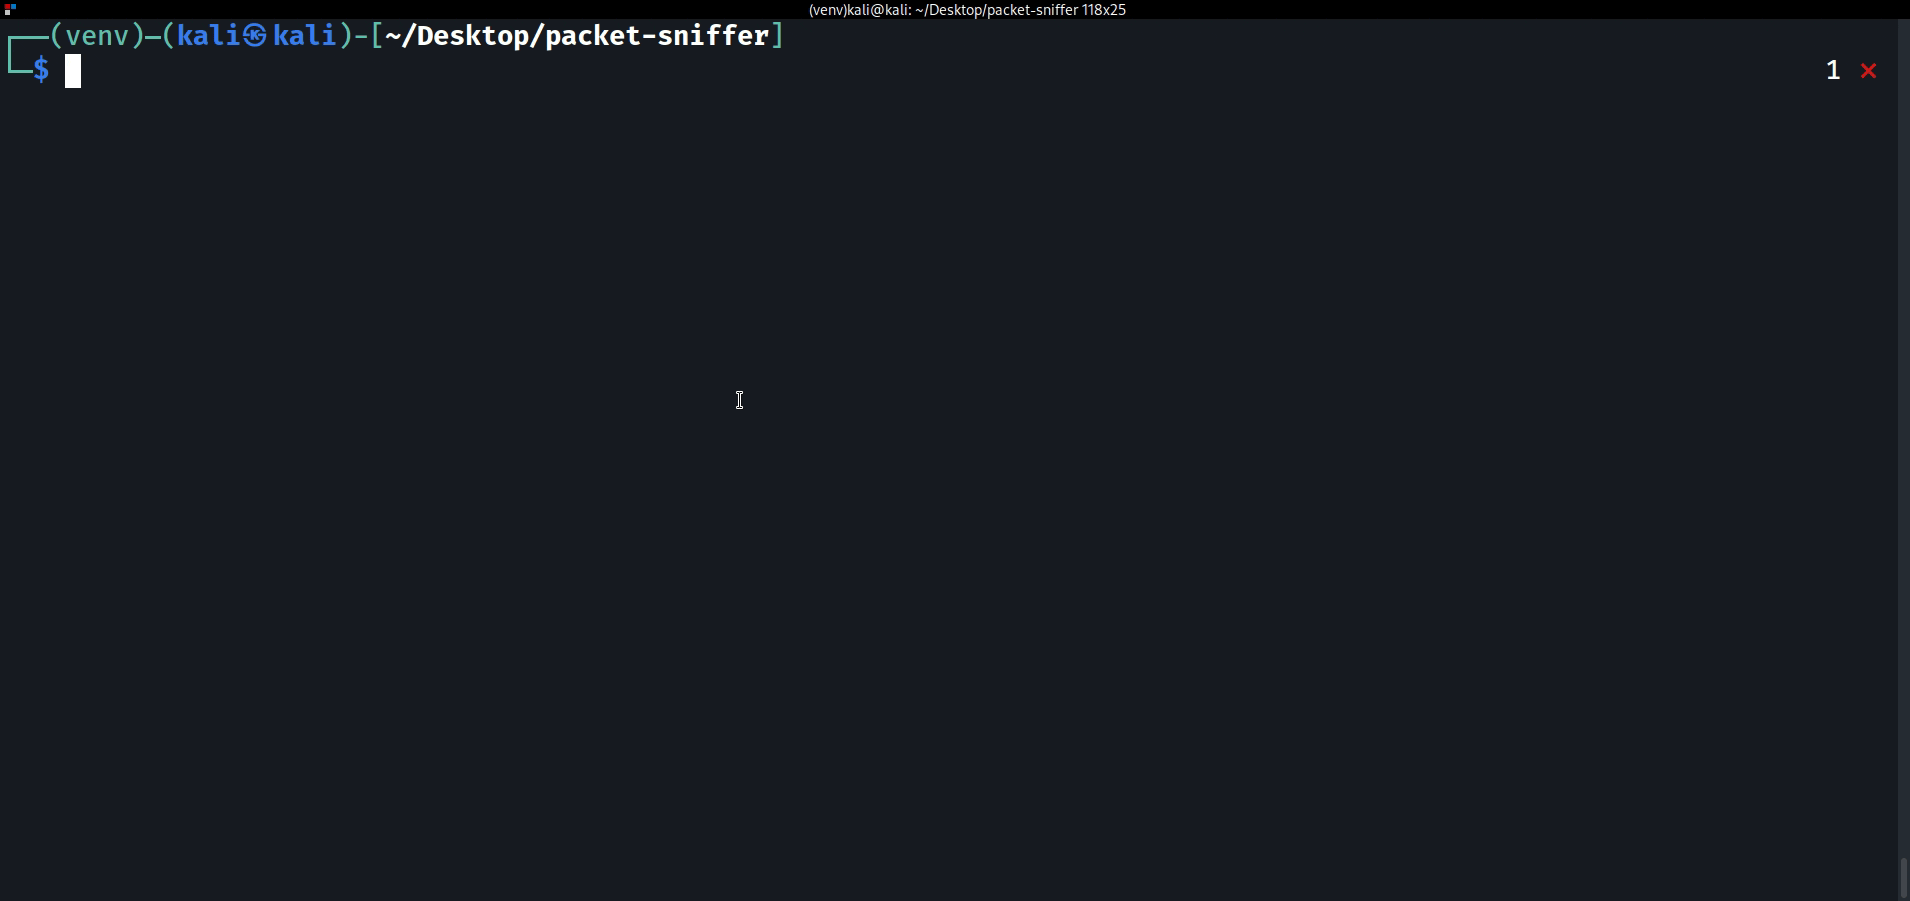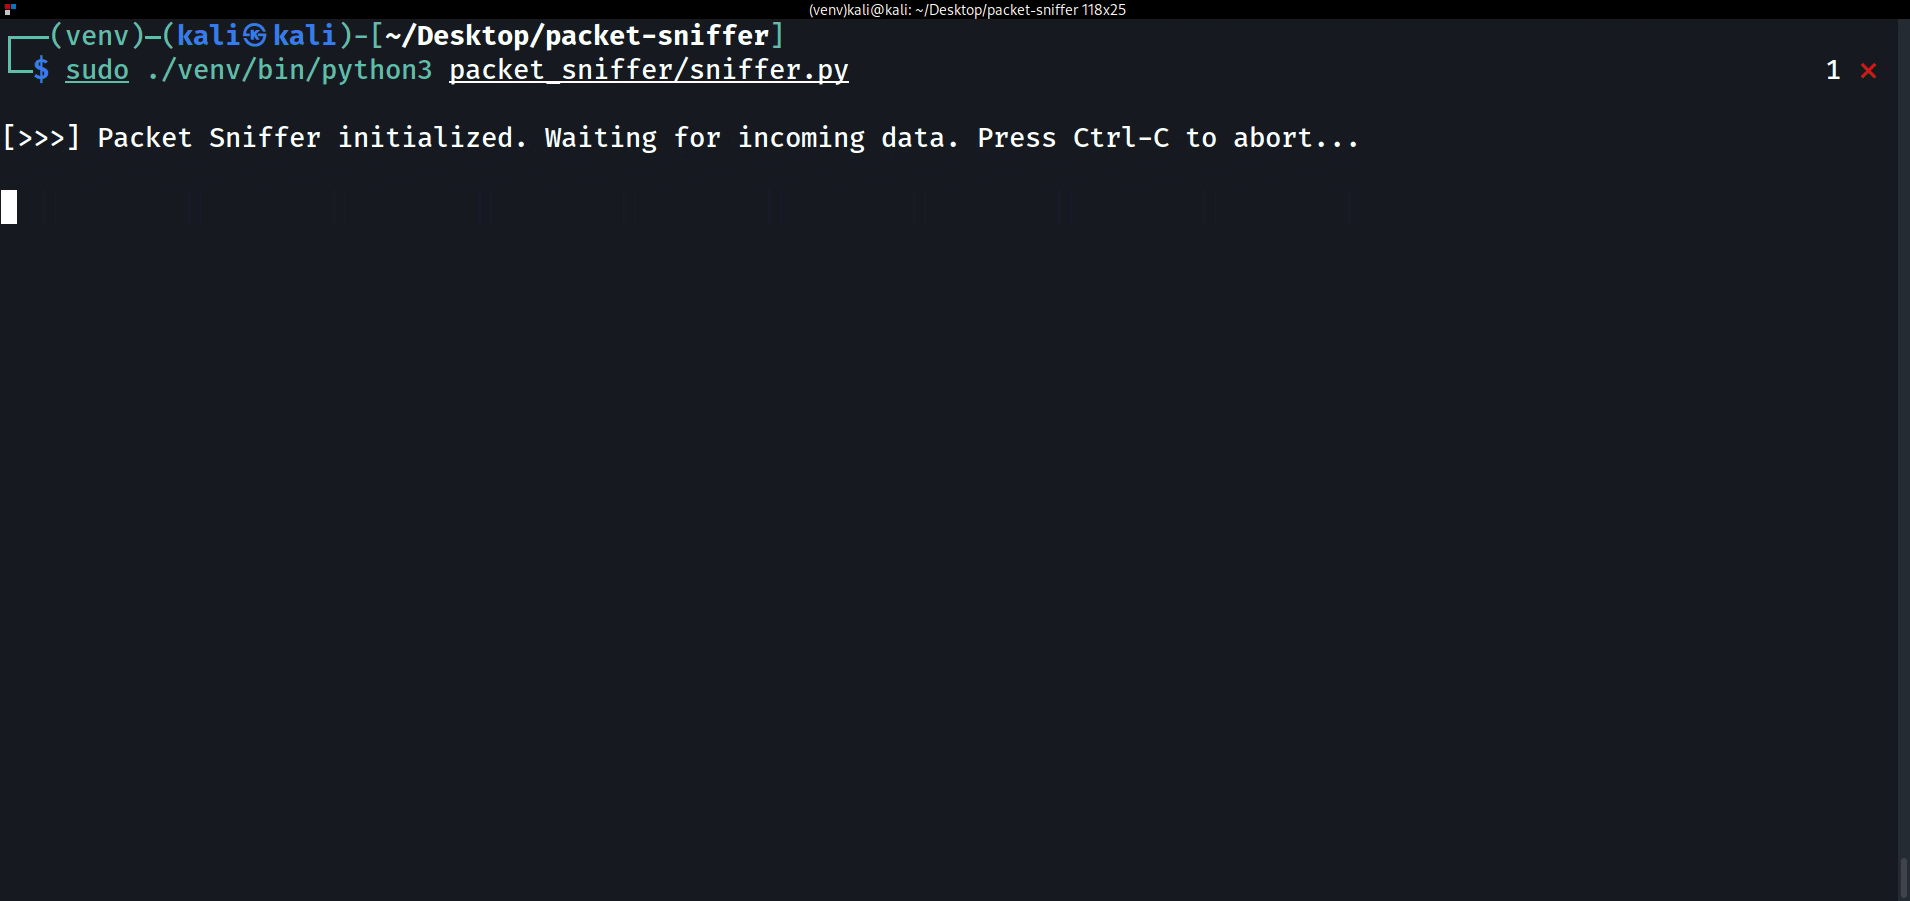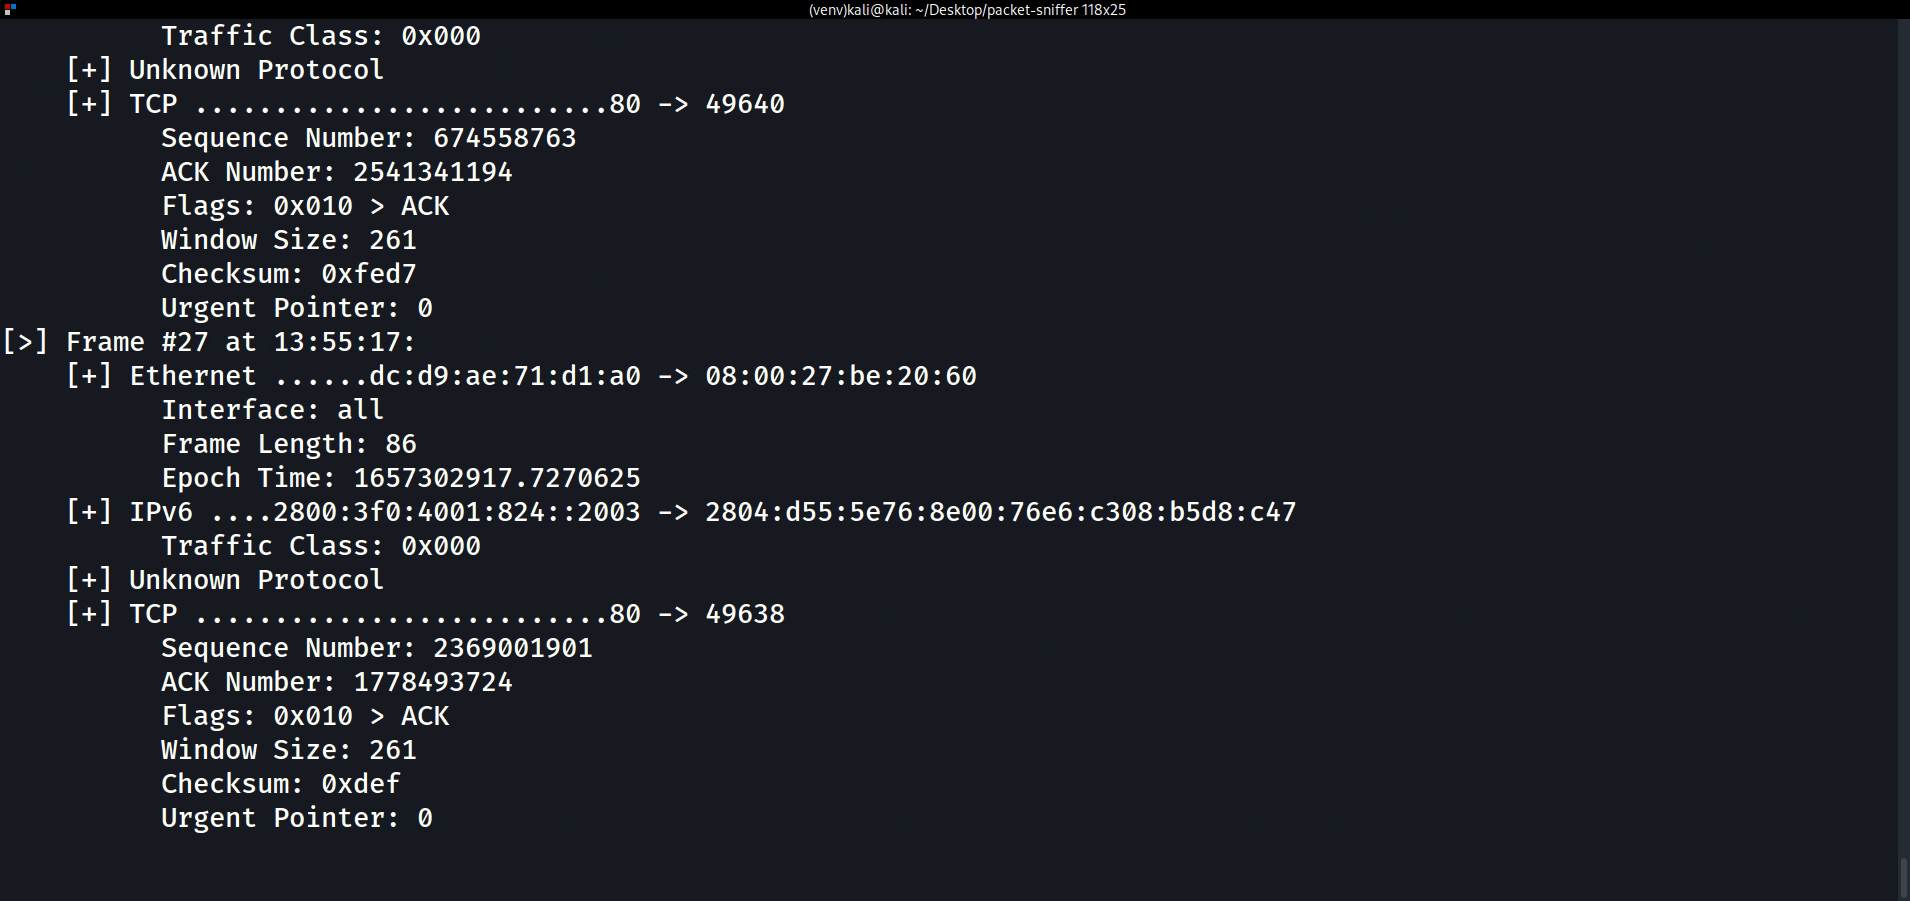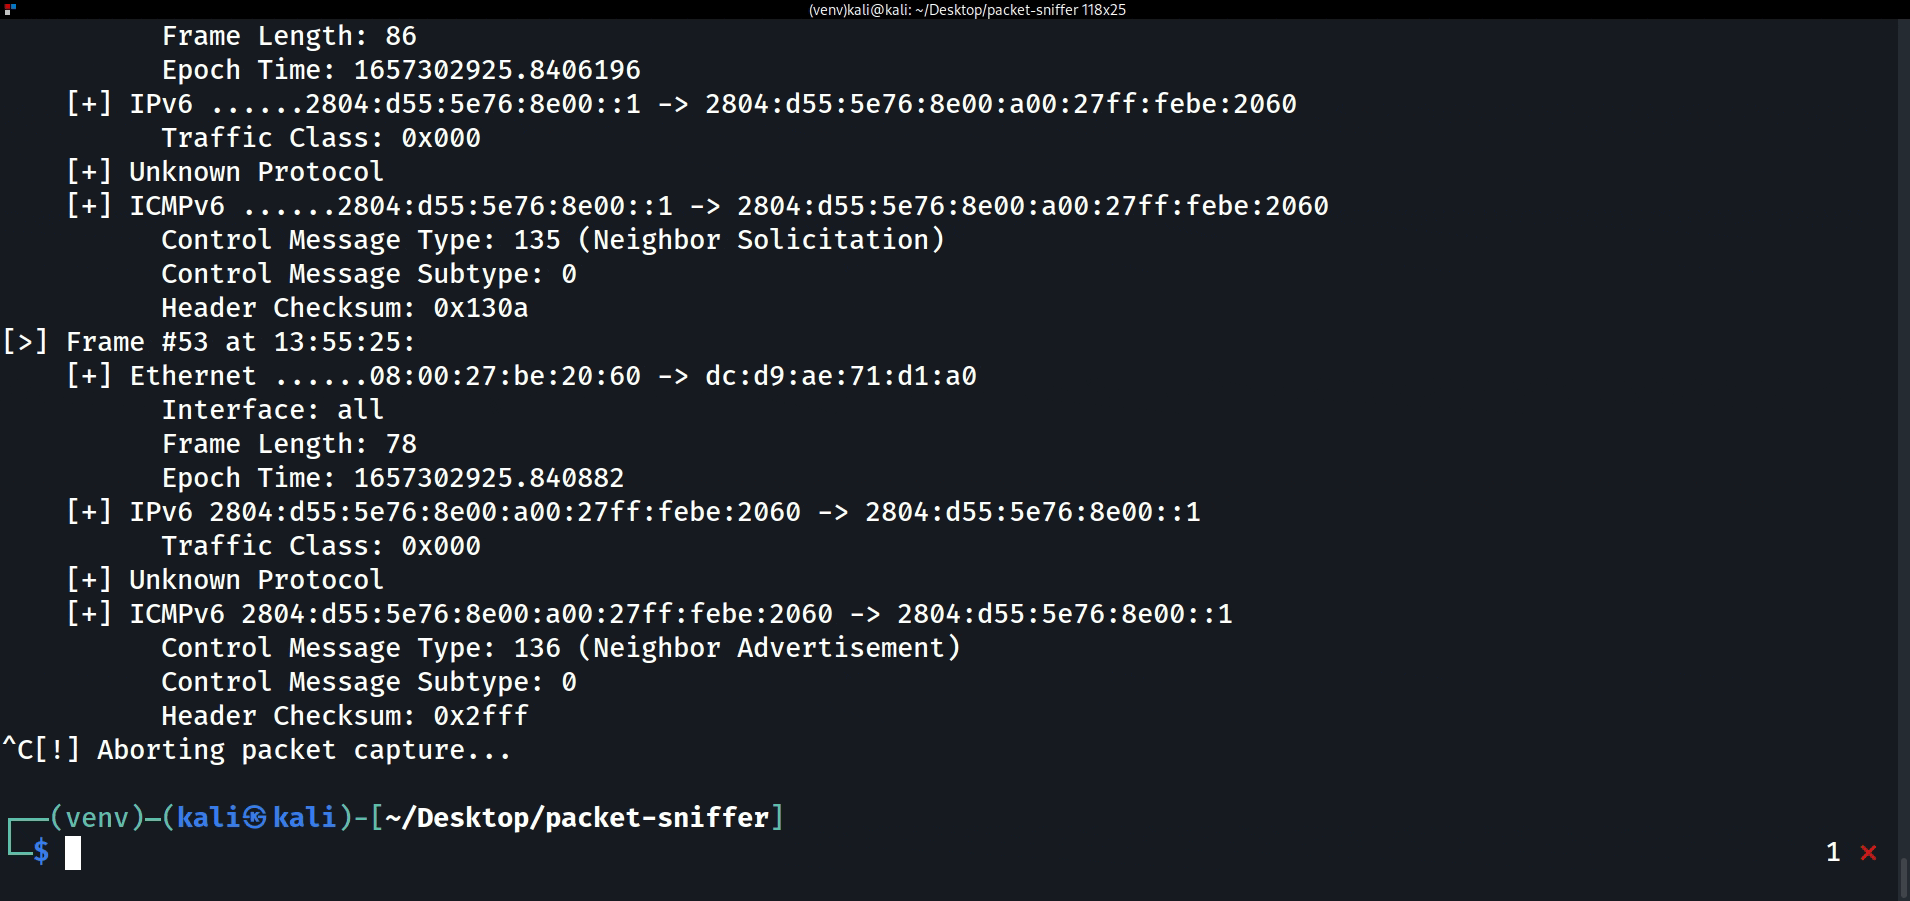 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 jlinebau/cve-2025-55315-scanner-monitor
Quick and Simple Scripts to Scan for Vulnerable Servers and Packet Level Monitors
 martinvks/cve-2022-45059-demo
Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols
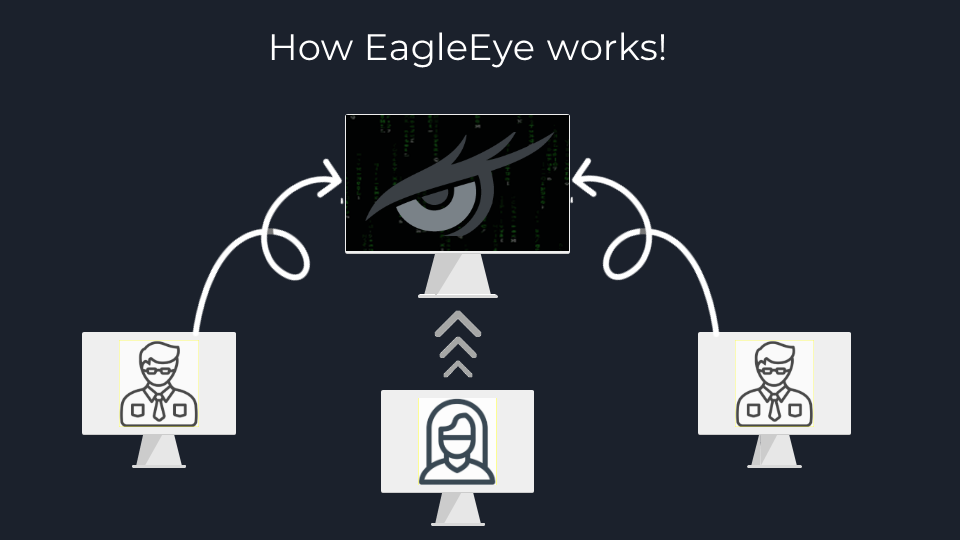 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
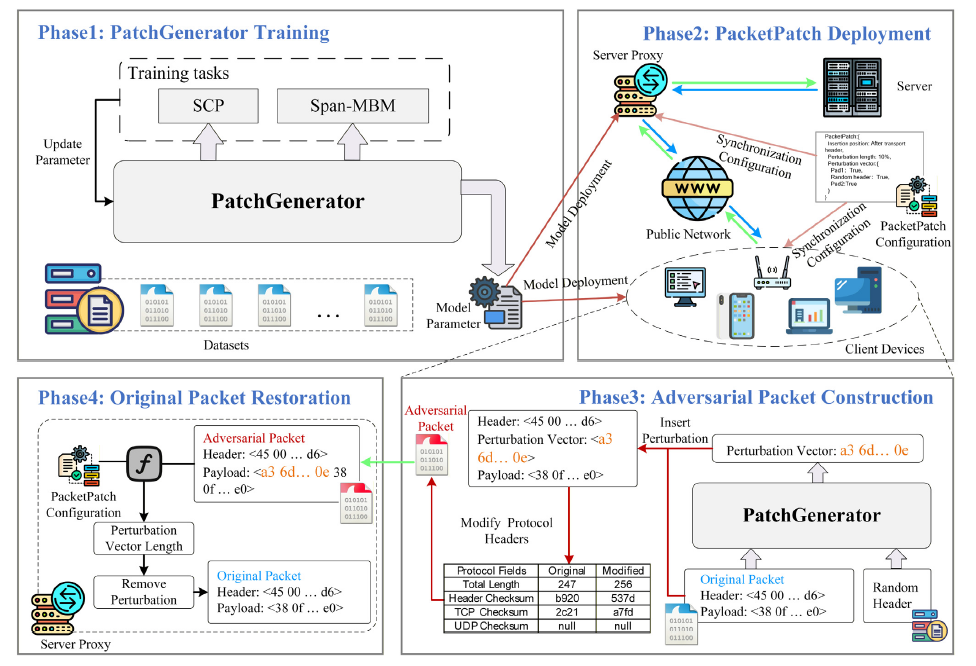 xuyw-seu/packetpatch
Practical black-box adversarial packet generation against encrypted traffic classification with minimal overhead and full packet recoverability.
 0xblackash/cve-2026-110912
Python/scapy proof-of-concept for CVE-2026-110912 (ARPBleed), an ARP ar_hln/ar_pln out-of-bounds read in DragonFly BSD that leaks kernel heap and…