
Preferred-Network-List-Sniffer
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
information-gatheringpacket-sniffing-analysisreconnaissance+3
178
aleksamcode/preferred-network-list-snifferA reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
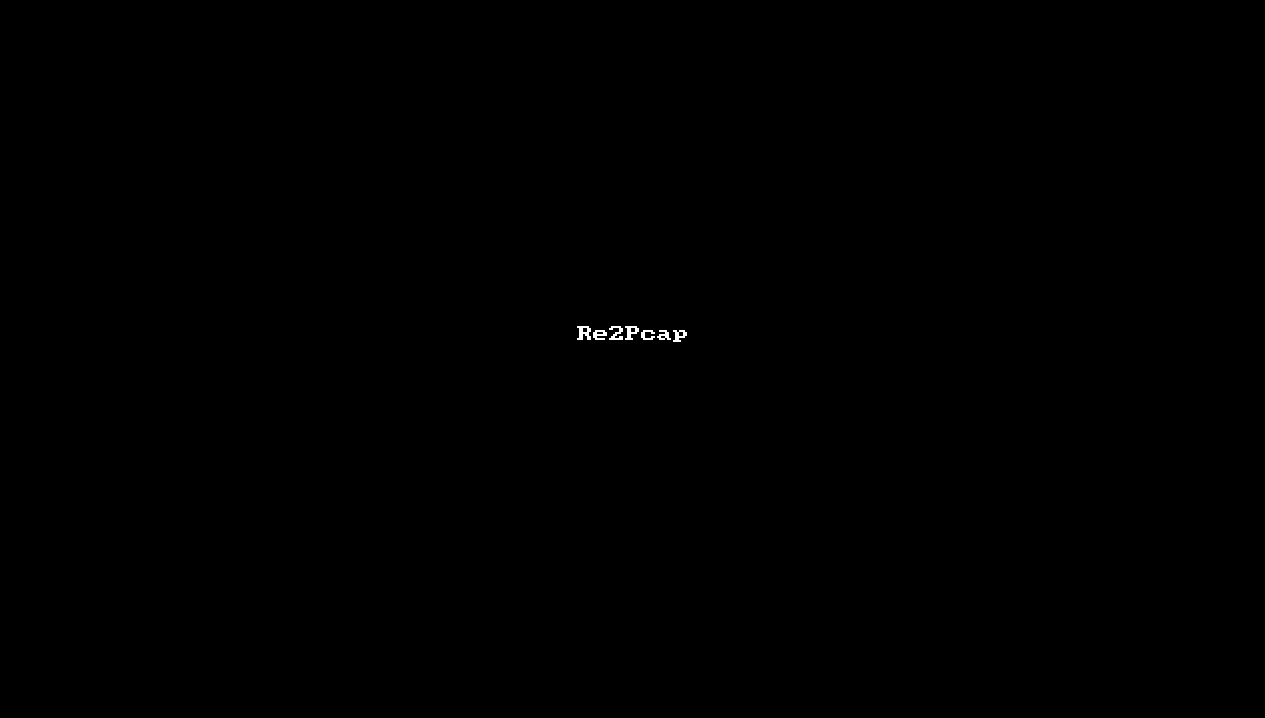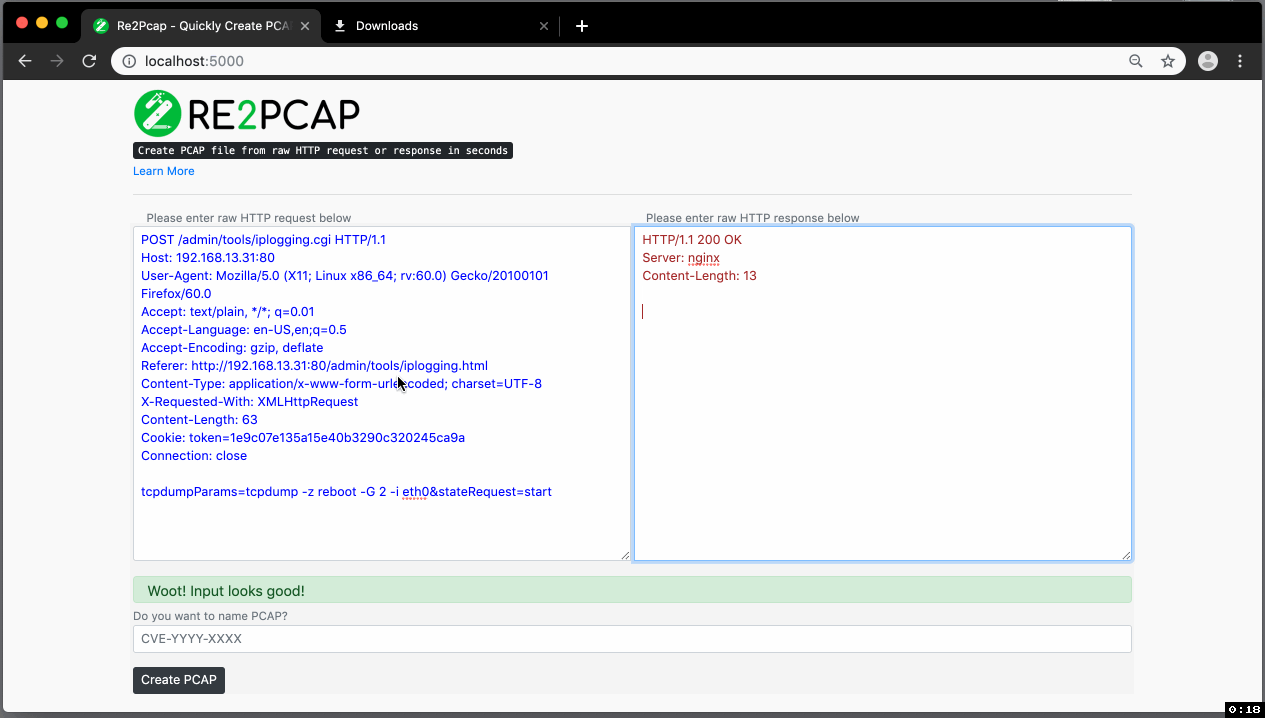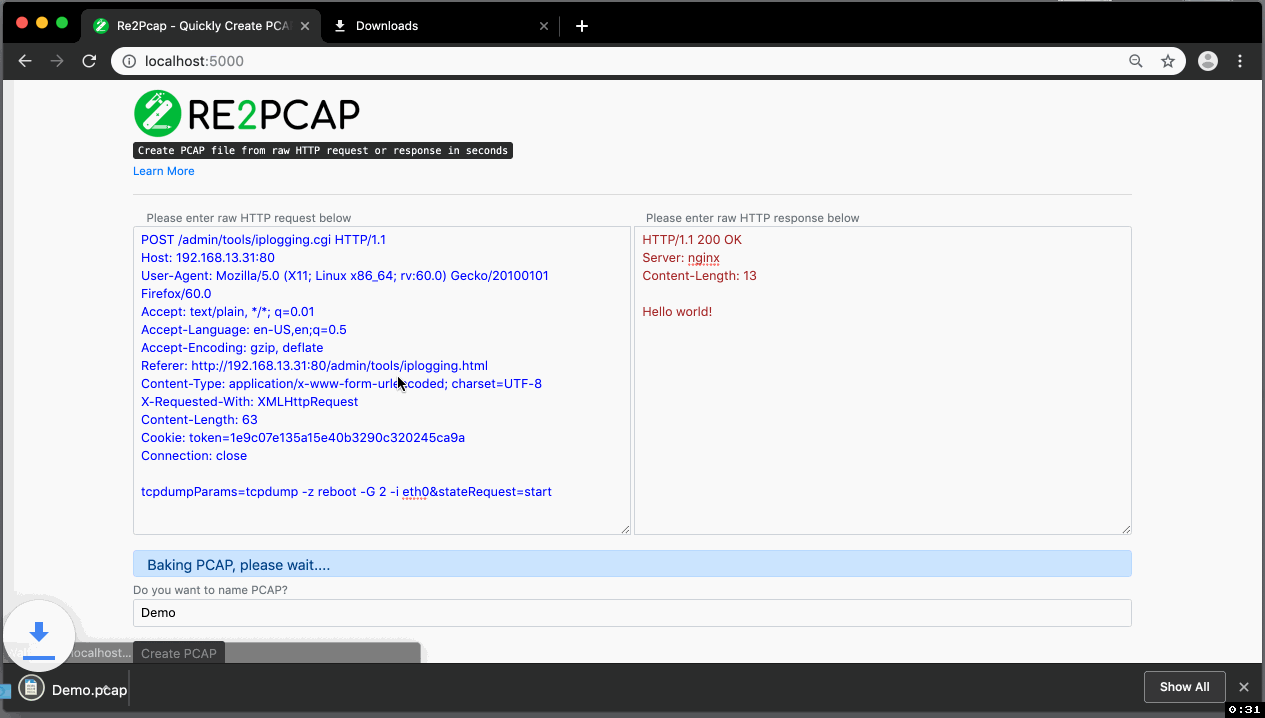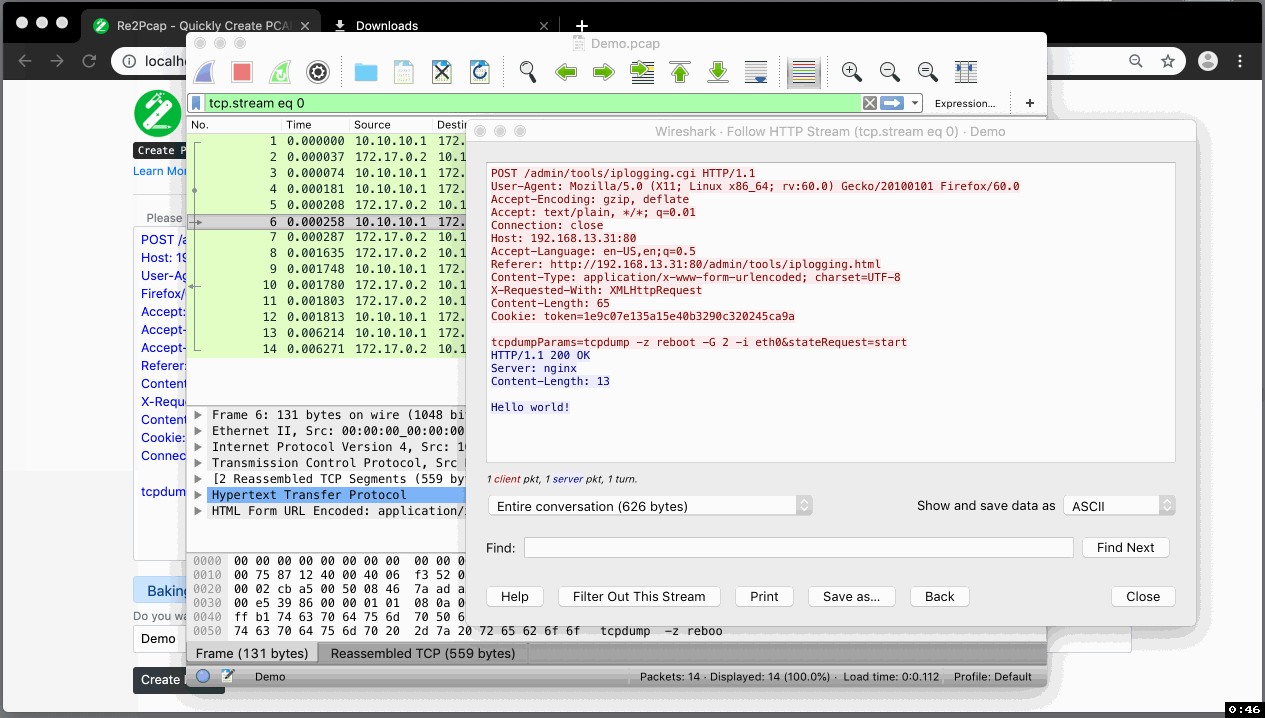 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 camp0/aiengine
Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
 mercuryworkshop/woeful
Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.
 corelight/zeek-mercury-npf
Zeek plugin generating Mercury NPF fingerprints for TCP, TLS/DTLS, QUIC, HTTP, SSH, OpenVPN, and STUN to support network security monitoring.
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 fevar54/cve-2025-4679-secureoauth-demo---enfoque-educativo
Isolated educational lab simulating CVE-2025-4679 OAuth credential exposure. Learn offensive and defensive security through hands-on exercises,…
 martinvks/cve-2022-45059-demo
Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…
 igrsoft/kismac2
KisMAC is a free, open source wireless stumbling and security tool for Mac OS X.
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…