
dnsmonster
 fenkohq/dnsmonster
Passive DNS Capture and Monitoring Toolkit
dns-analysisinformation-gatheringlog-analysis+3
fenkohq/dnsmonsterPassive DNS Capture and Monitoring Toolkit
 ga0/netgraph
A cross platform http sniffer with a web UI
 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 chrizator/netattack2
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
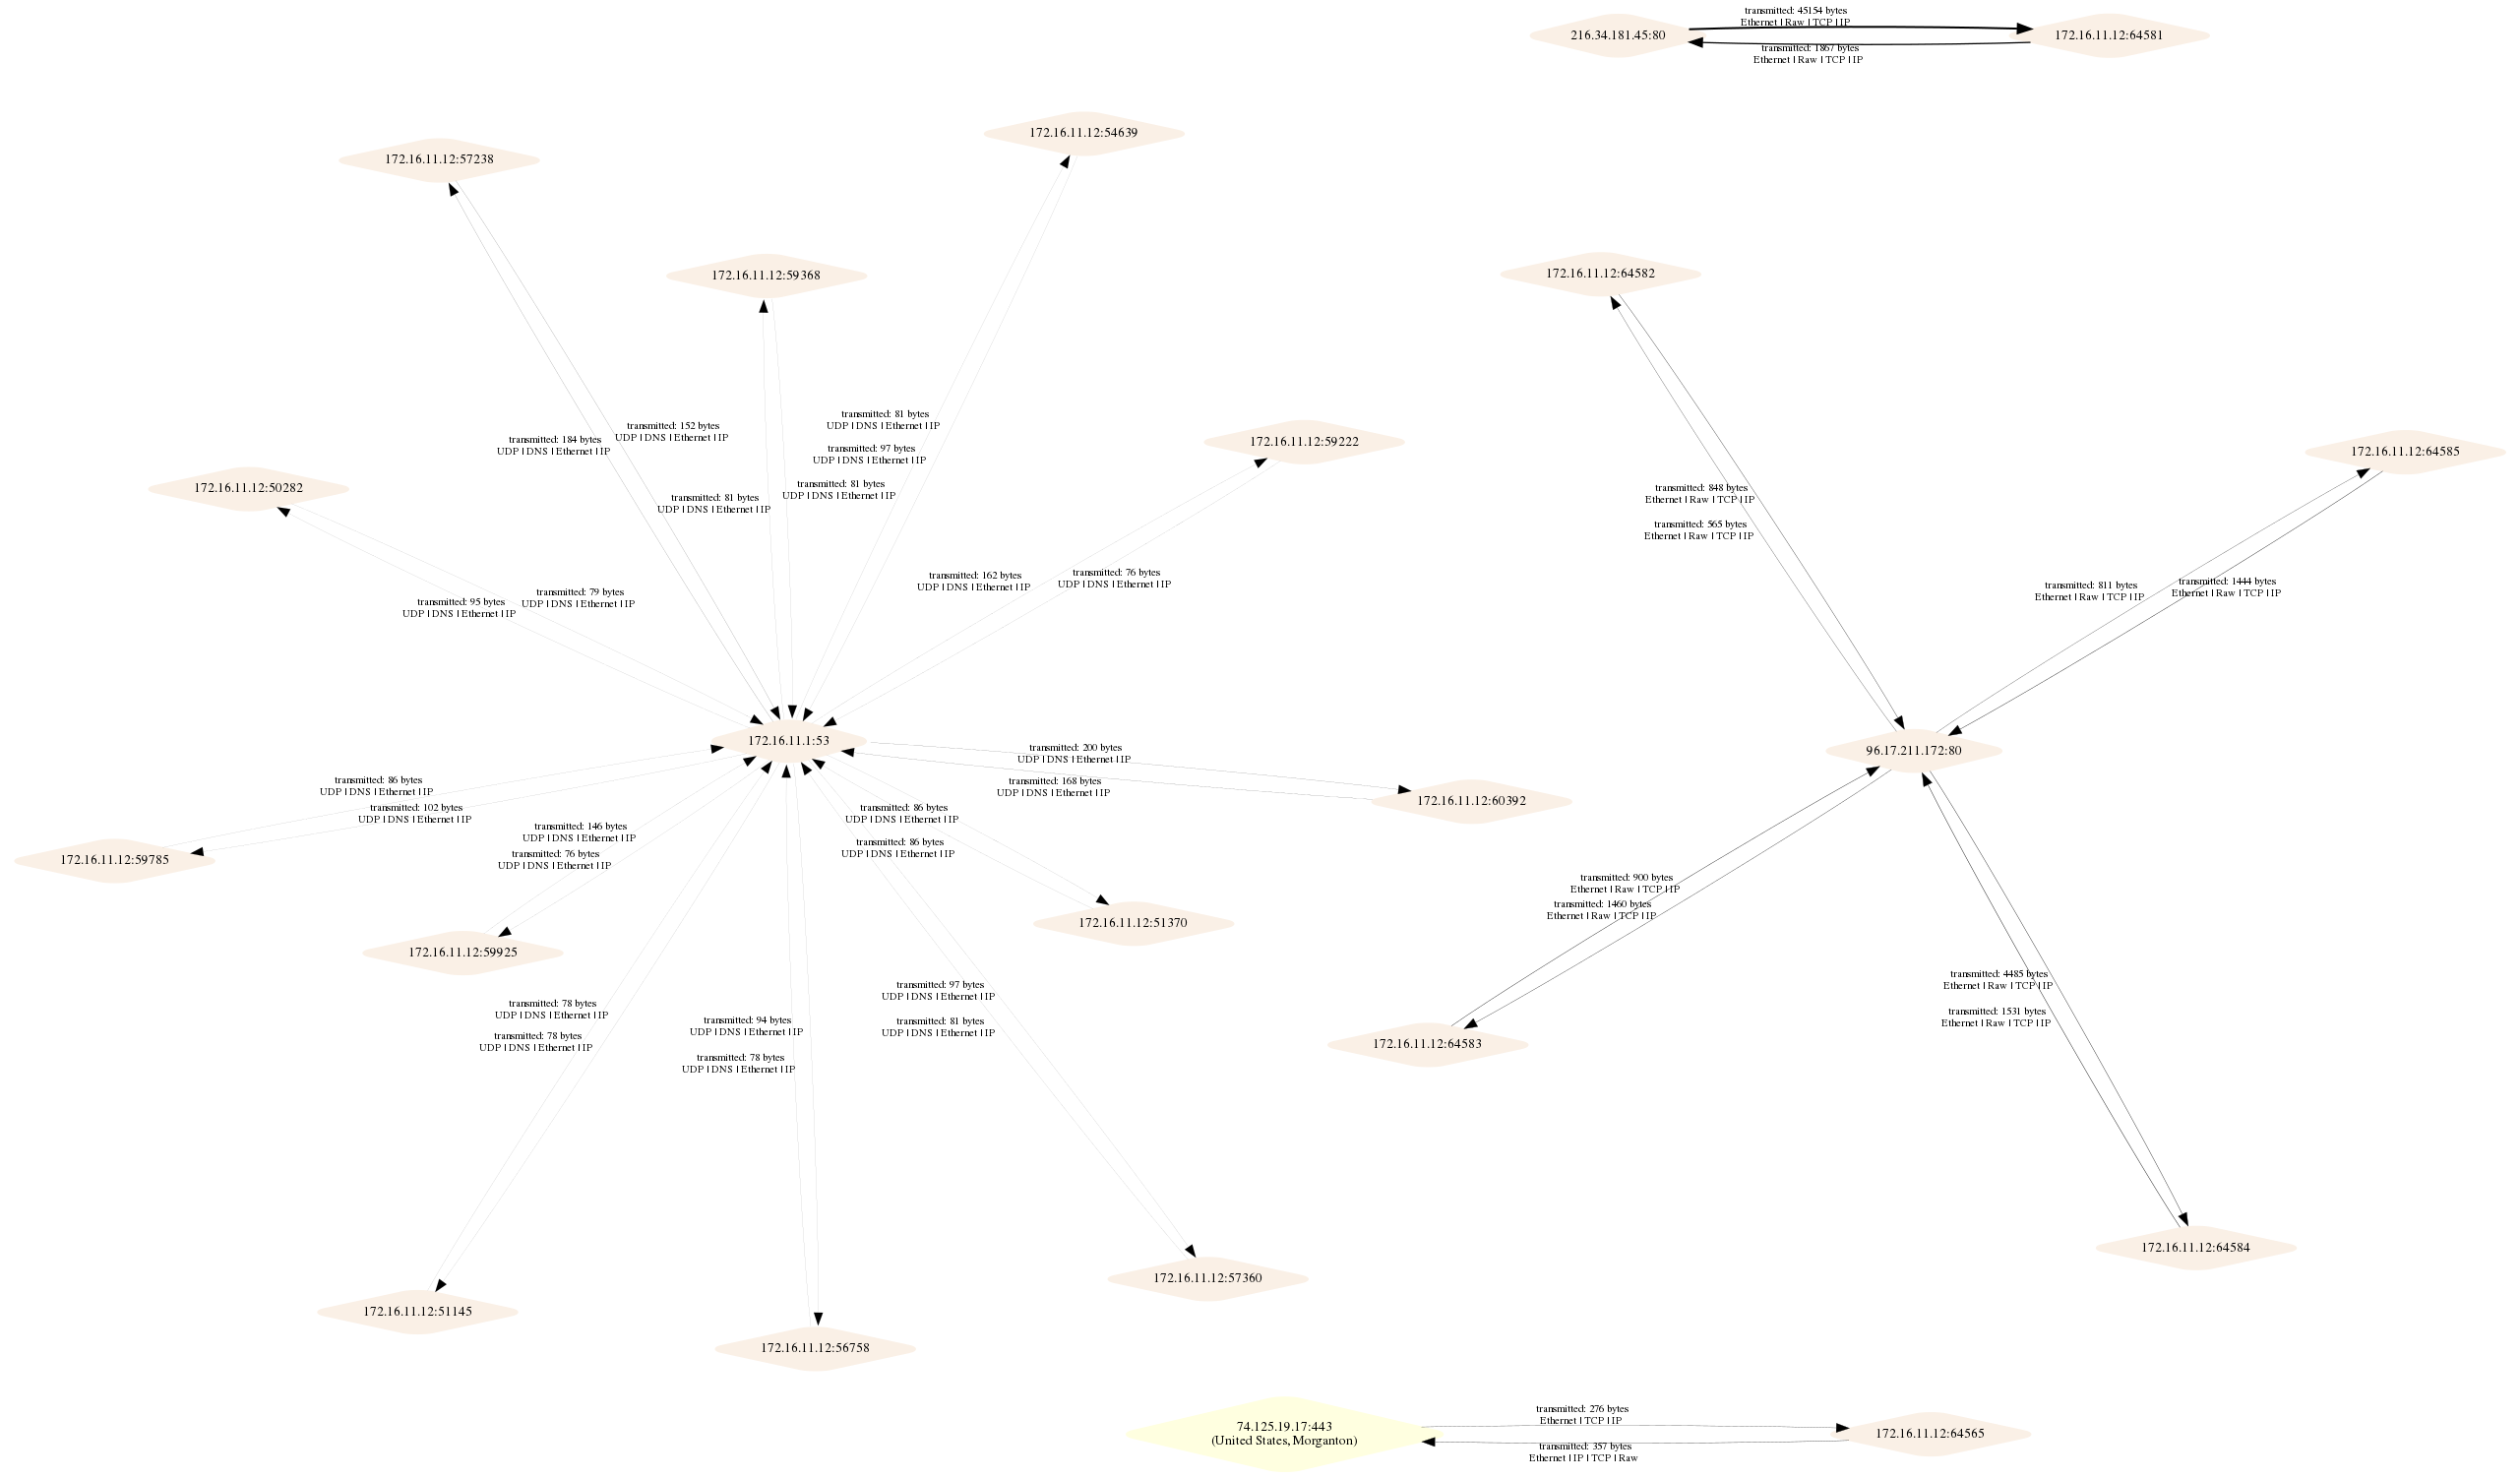 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
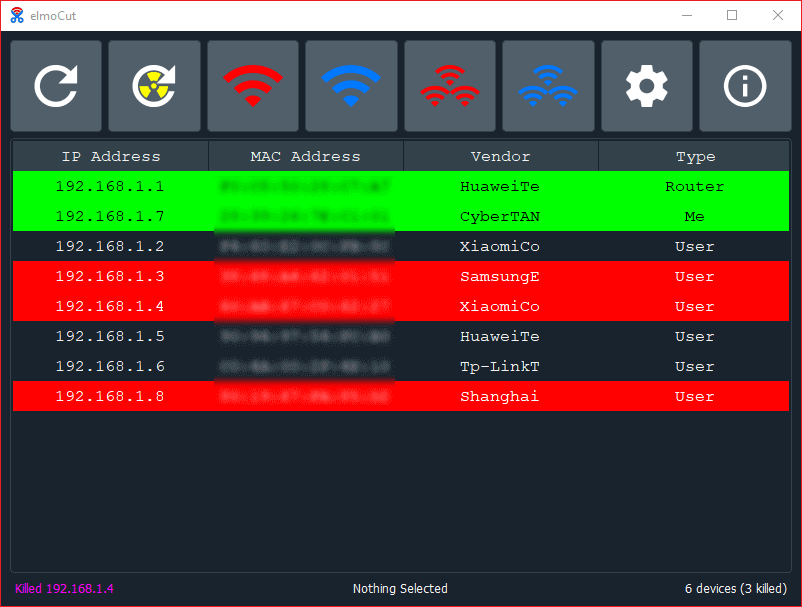 elmoiv/elmocut
Eye candy ARP spoofer for Windows
 danmcinerney/creds.py
Harvest FTP/POP/IMAP/HTTP/IRC creds
 offensive-hub/black-widow
GUI based offensive penetration testing tool (Open Source)
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 skyplabs/probequest
Toolkit for Playing with Wi-Fi Probe Requests
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 doronz88/harlogger
Simple utility for sniffing decrypted HTTP/HTTPS traffic on a macOS/iOS device (either jailbroken or not)
 galkan/flashlight
Pentesters spend too much time during information gathering phase. Flashlight (Fener) provides services to scan network/ports and gather information…
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
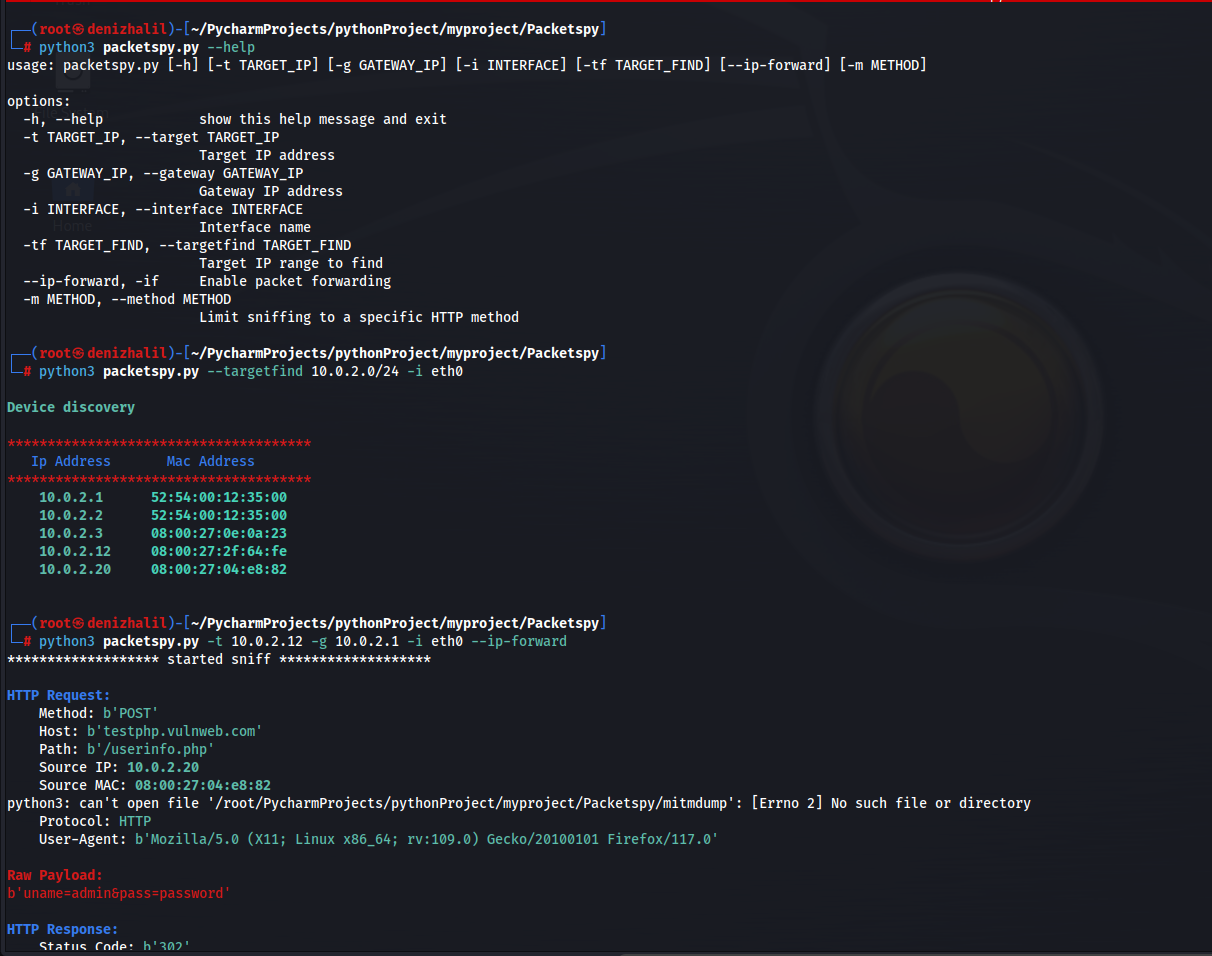 halildeniz/packetspy
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)