
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
pyshark-legacy preview

pyshark-legacy

GitHubkiminewt/pyshark-legacy

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors (Python2 legacy version)

network-securitypacket-sniffing-analysisutilities-frameworks
68 years ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

anomaly-detectiondefensive-toolsincident-response+6
29 days ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
digital-forensicsdynamic-analysis-sandboxingeducation+8
22 months ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

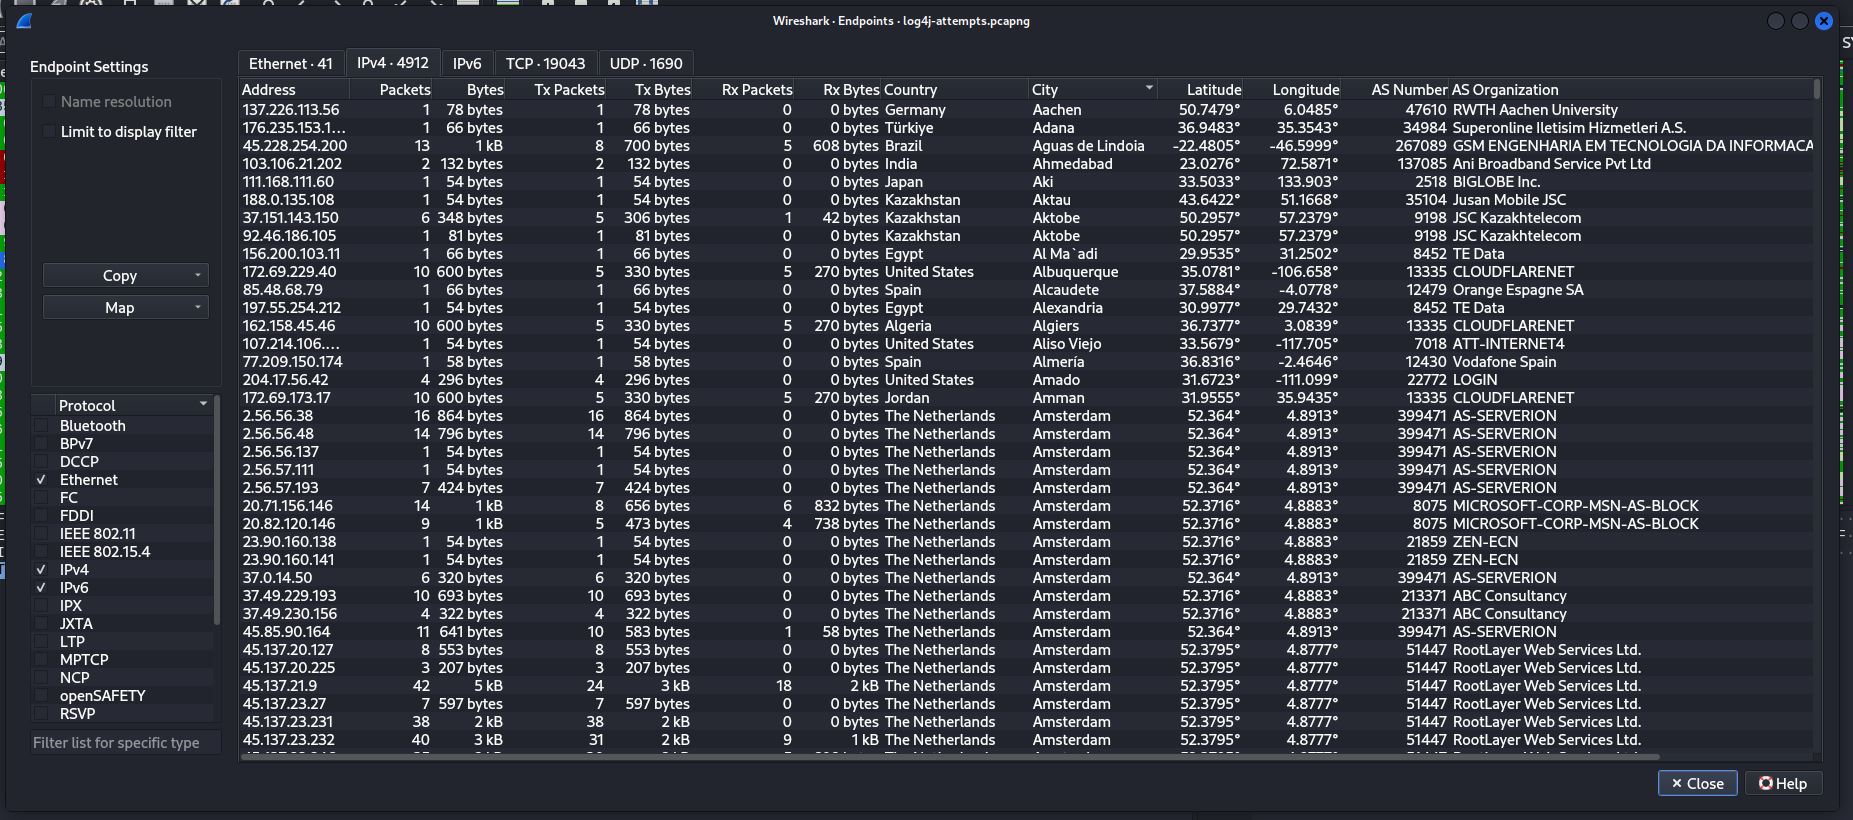
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
Intrusion-Alert-Educational-Network-IDS preview

Intrusion-Alert-Educational-Network-IDS

GitHubowasp/intrusion-alert-educational-network-ids

Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
anomaly-detectiondefensive-toolseducation+3
6 months ago
Multi-VLAN-Enterprise-Network-Vulnerability-Assessment preview

Multi-VLAN-Enterprise-Network-Vulnerability-Assessment

GitHubklairmanraj/multi-vlan-enterprise-network-vulnerability-assessment

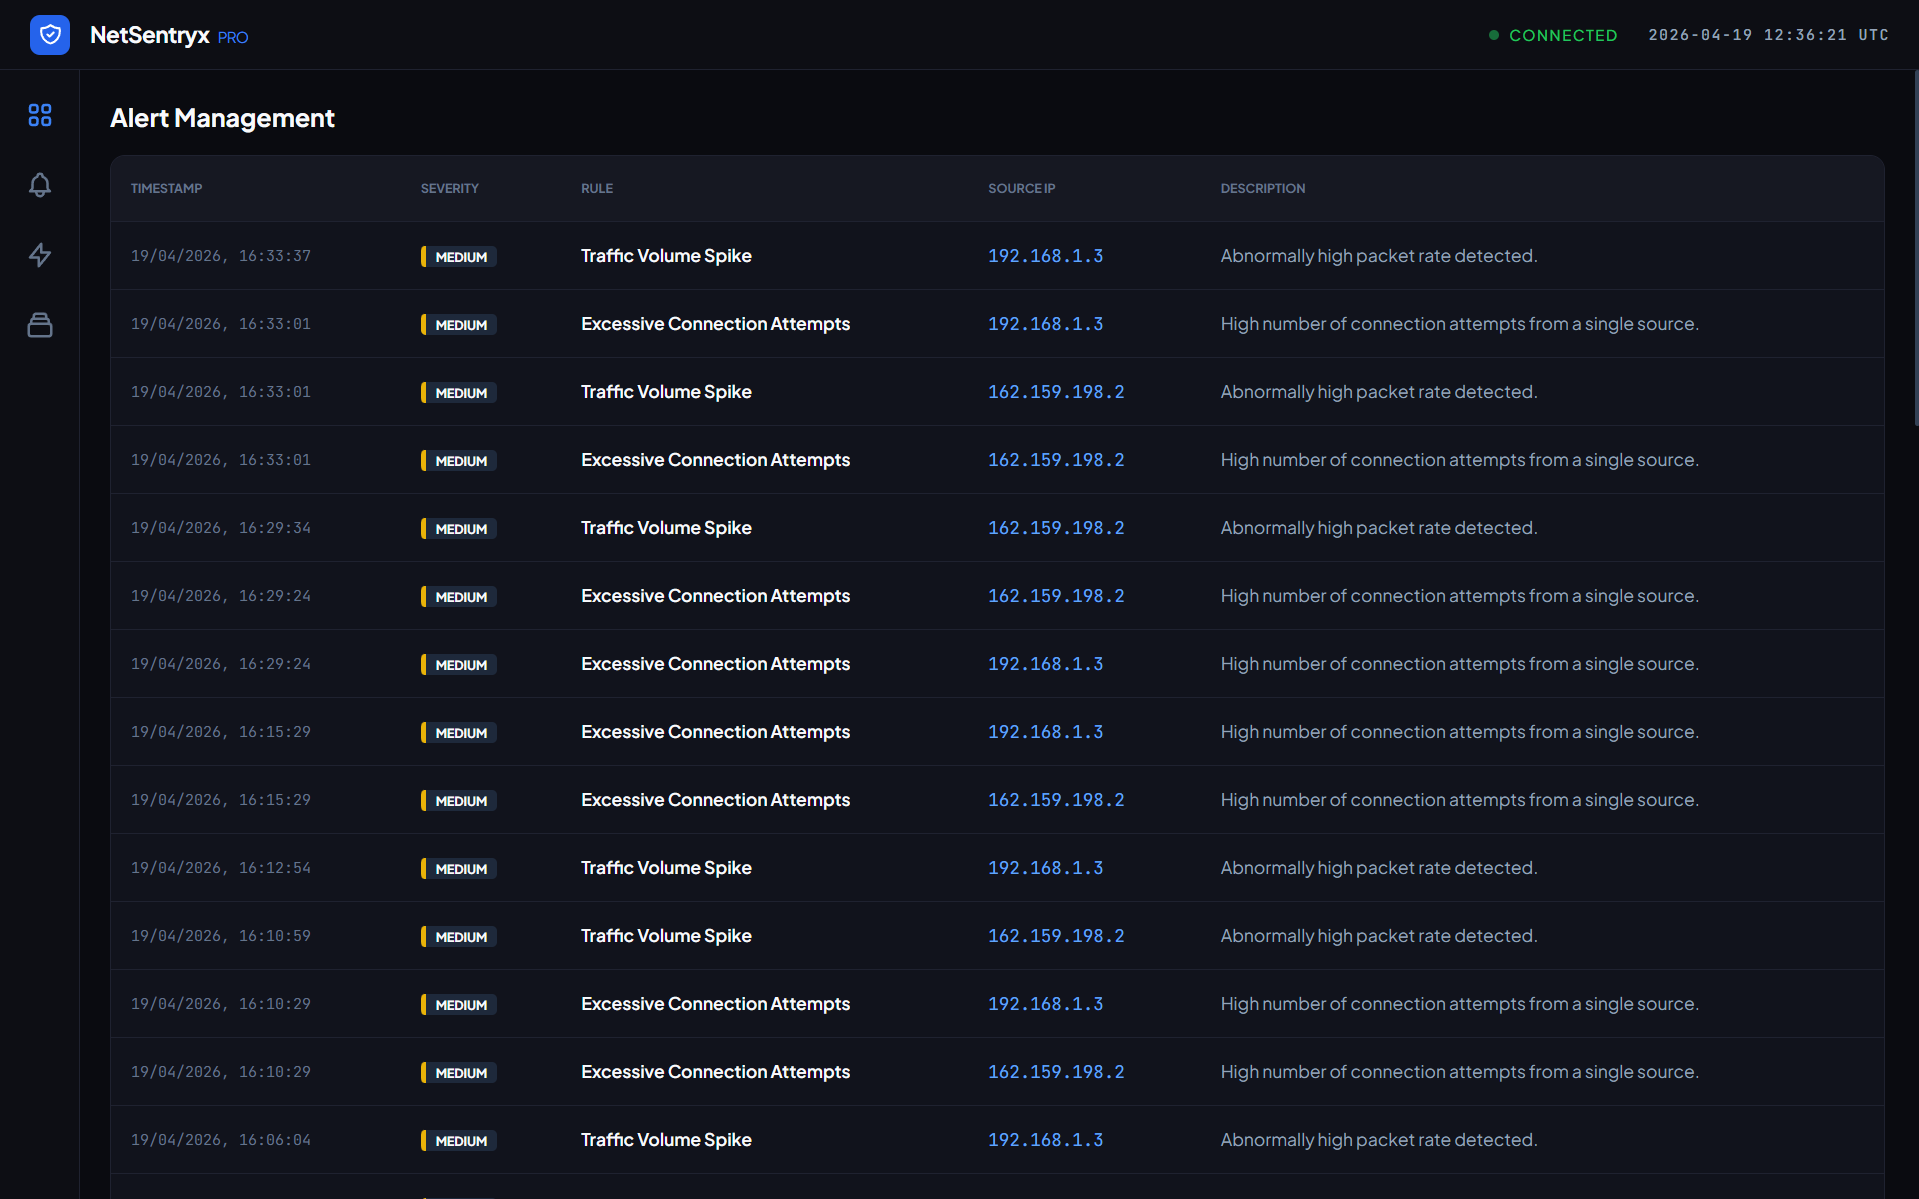
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
exploitationnetwork-mappingnetwork-security+6
6 months ago
netsentryx preview

netsentryx

GitHubaman-sharma-dev/netsentryx

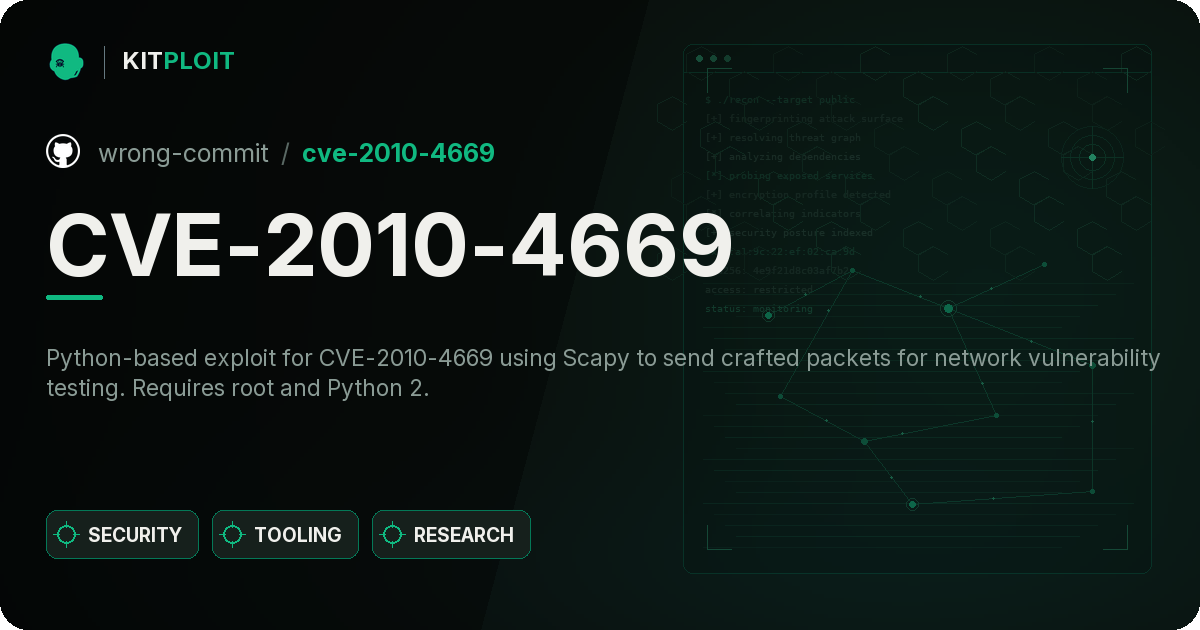
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
anomaly-detectioncloud-securitydefensive-tools+6
2 months ago
CVE-2010-4669 preview

CVE-2010-4669

GitHubwrong-commit/cve-2010-4669

Python-based exploit for CVE-2010-4669 using Scapy to send crafted packets for network vulnerability testing. Requires root and Python 2.

exploitationnetwork-securitypacket-sniffing-analysis+1
2 years ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

ai-securitycloud-infrastructure-securitycloud-security+9
12.1k18h 26m ago
tpotce preview

tpotce

GitHubtelekom-security/tpotce

🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
9.6k4 days ago
betwixt preview

betwixt

GitHubkdzwinel/betwixt

:zap: Web Debugging Proxy based on Chrome DevTools Network panel.

debuggerspacket-sniffing-analysisweb-proxies-interception+1
4.6k7 years ago
joy preview

joy

GitHubcisco/joy

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.

anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago
Sniffle preview

Sniffle

GitHubnccgroup/sniffle

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…

bluetooth-securityembedded-systems-securityhardware-hacking+5
1.2k1 year ago
PcapViz preview

PcapViz

GitHub1ultimat3/pcapviz

Visualize network topologies and collect graph statistics based on pcap files
information-gatheringnetwork-forensicsnetwork-mapping+1
3603 years ago
arp-validator preview

arp-validator

GitHubrnehra01/arp-validator

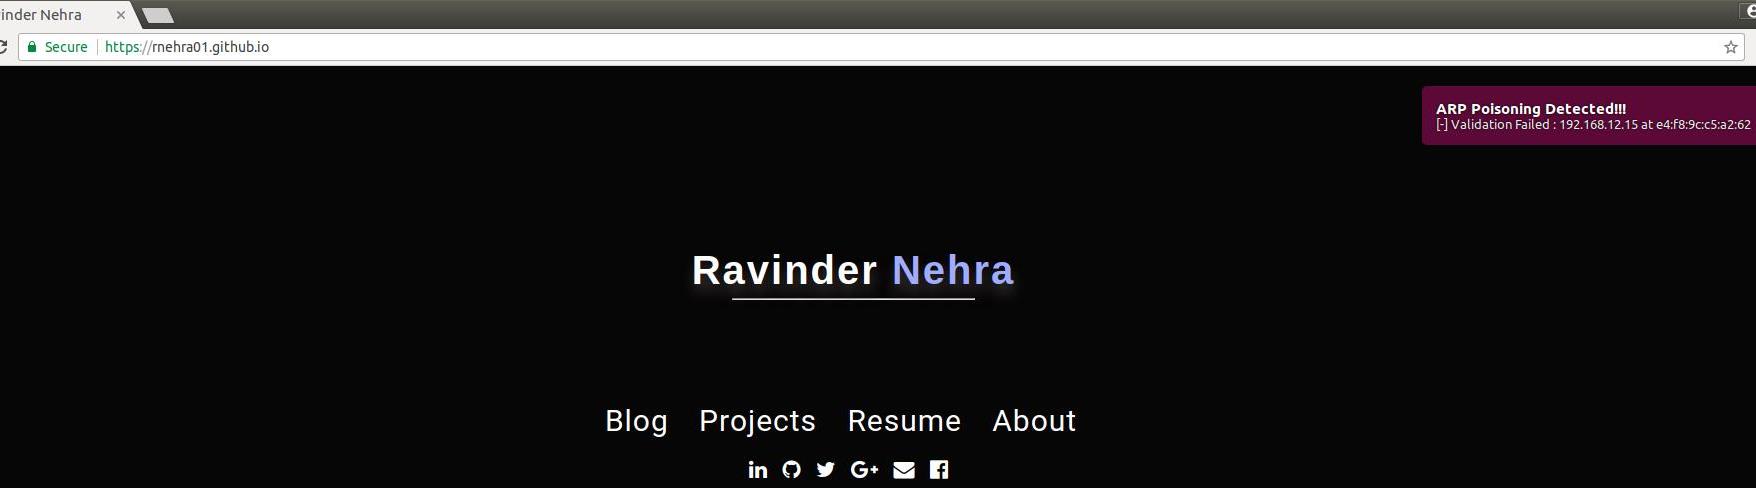
Security Tool to detect arp poisoning attacks
defensive-toolsintrusion-detectionnetwork-security+1
548 years ago
PiX-C2 preview

PiX-C2

GitHubrobertdavis1/pix-c2

Ping Exfiltration Command and Control (PiX-C2)

command-and-controlnetwork-securitypacket-sniffing-analysis+3
3111 years ago
zeek-quic preview

zeek-quic

GitHubcorelight/zeek-quic

Bro analyzer that detects Google's QUIC protocol

intrusion-detectionlog-analysisnetwork-forensics+2
125 years ago
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

anomaly-detectiondefensive-toolsdns-analysis+5
1 month ago
Previous123Next