
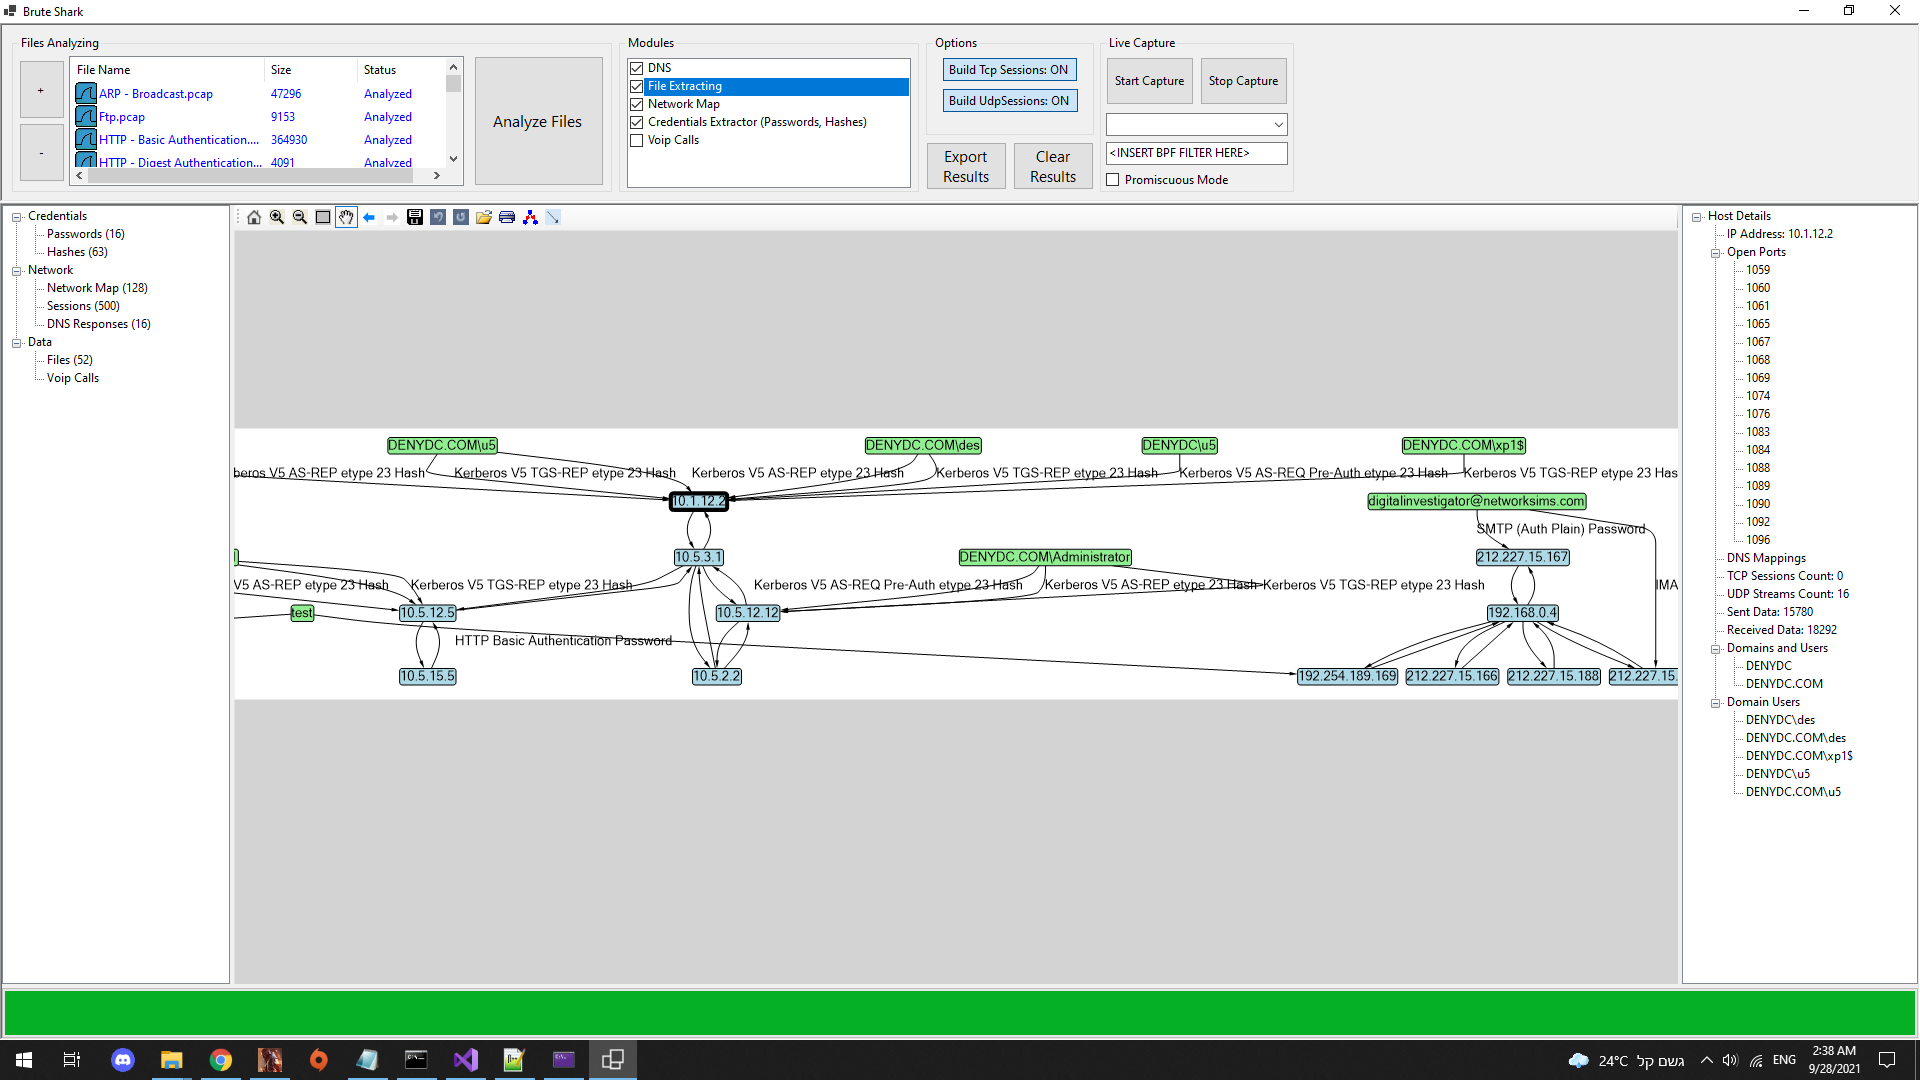
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
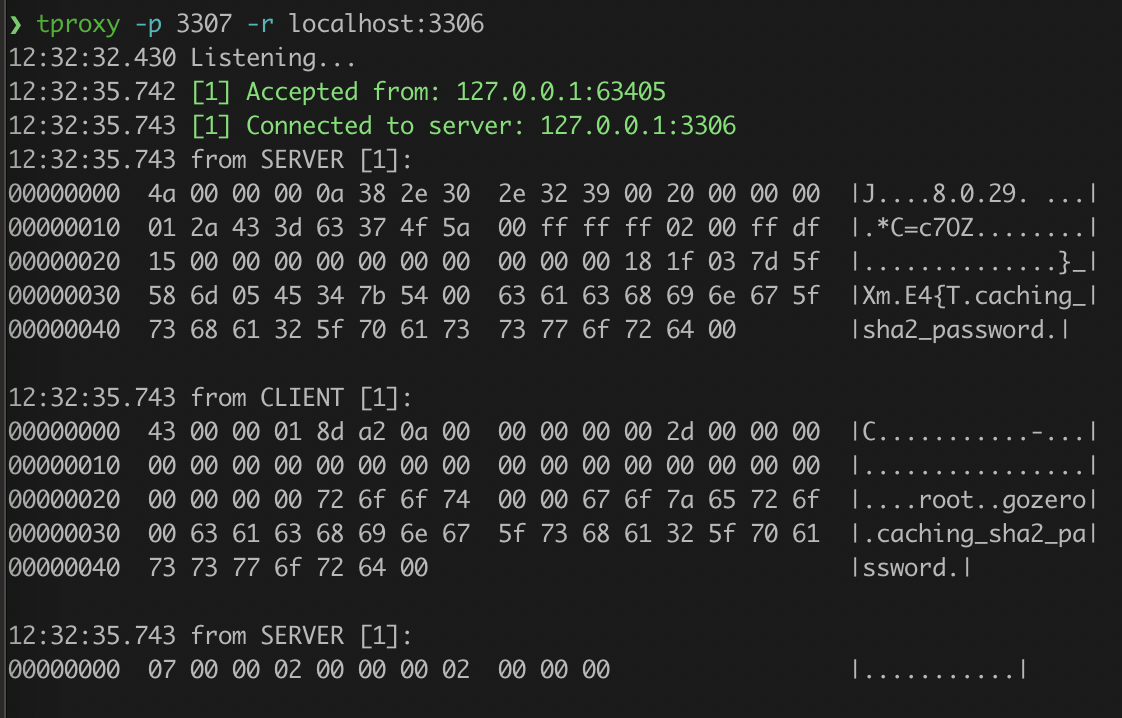 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.

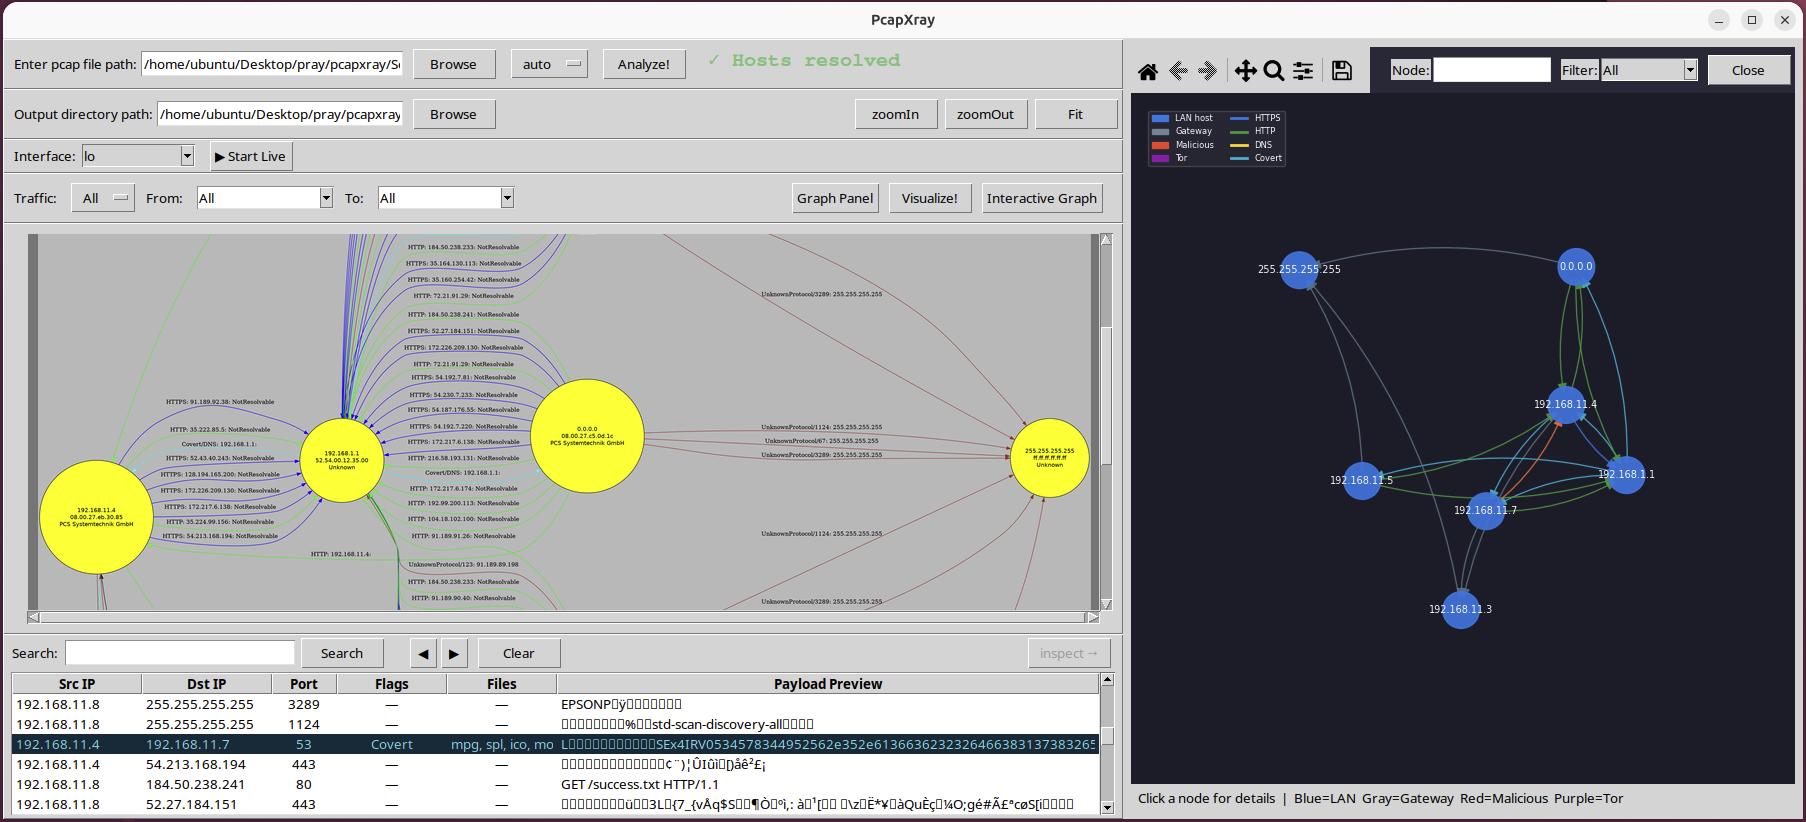 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

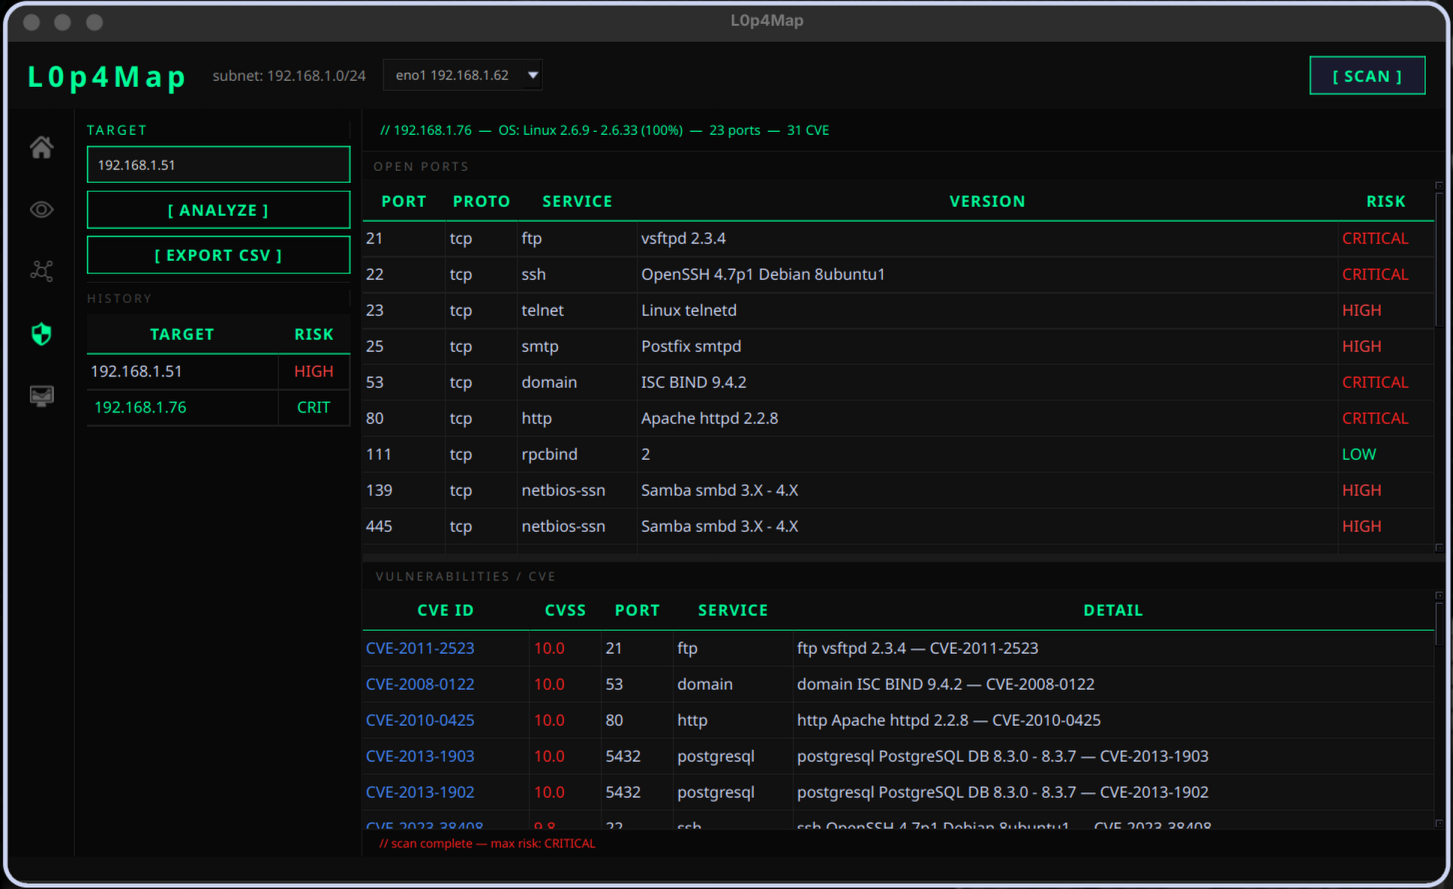 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
 medpaf/hawk
Network, recon and offensive-security tool for Linux.
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
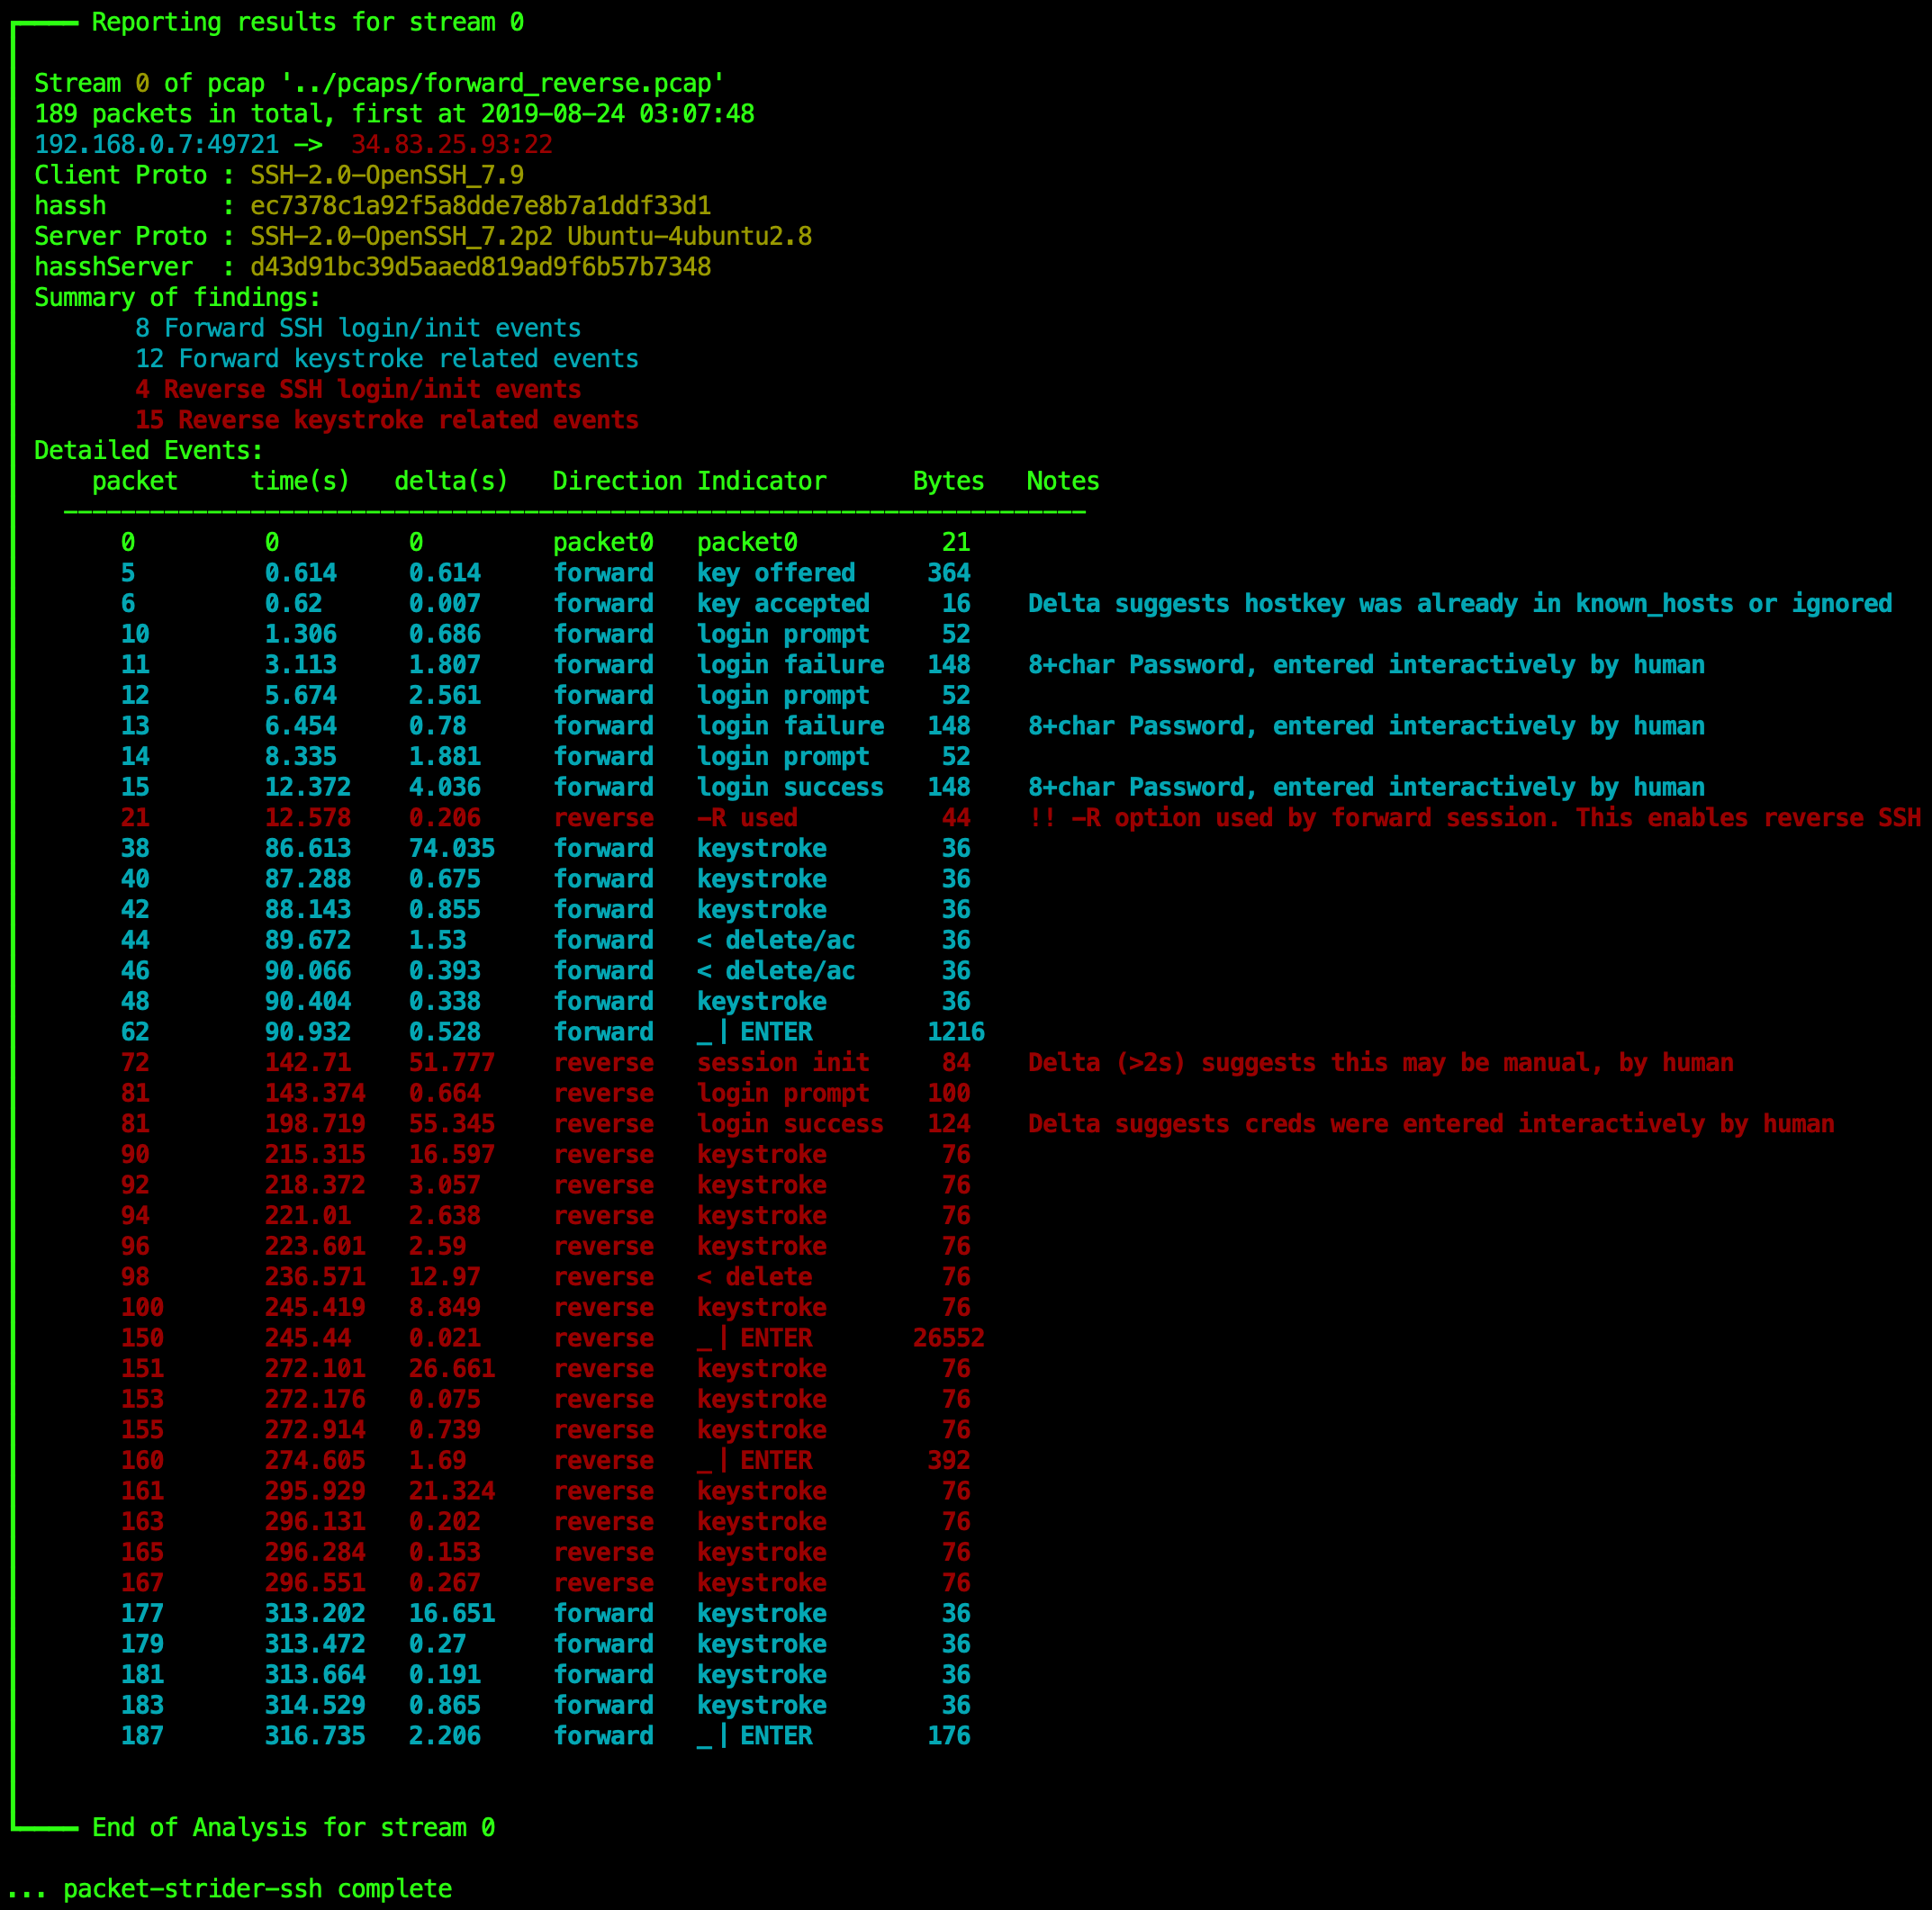 benjeems/packetstrider
A network packet forensics tool for SSH
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files