
polymorph
 shramos/polymorph
Polymorph is a real-time network packet manipulation framework with support for almost all existing protocols
educationnetwork-securitypacket-sniffing-analysis+2
497
shramos/polymorphPolymorph is a real-time network packet manipulation framework with support for almost all existing protocols
 gdssecurity/wifitap
wifitap updated for BT5r3

 josh0xa/espionage
A Linux Packet Sniffing Suite for Automated MiTM Attacks
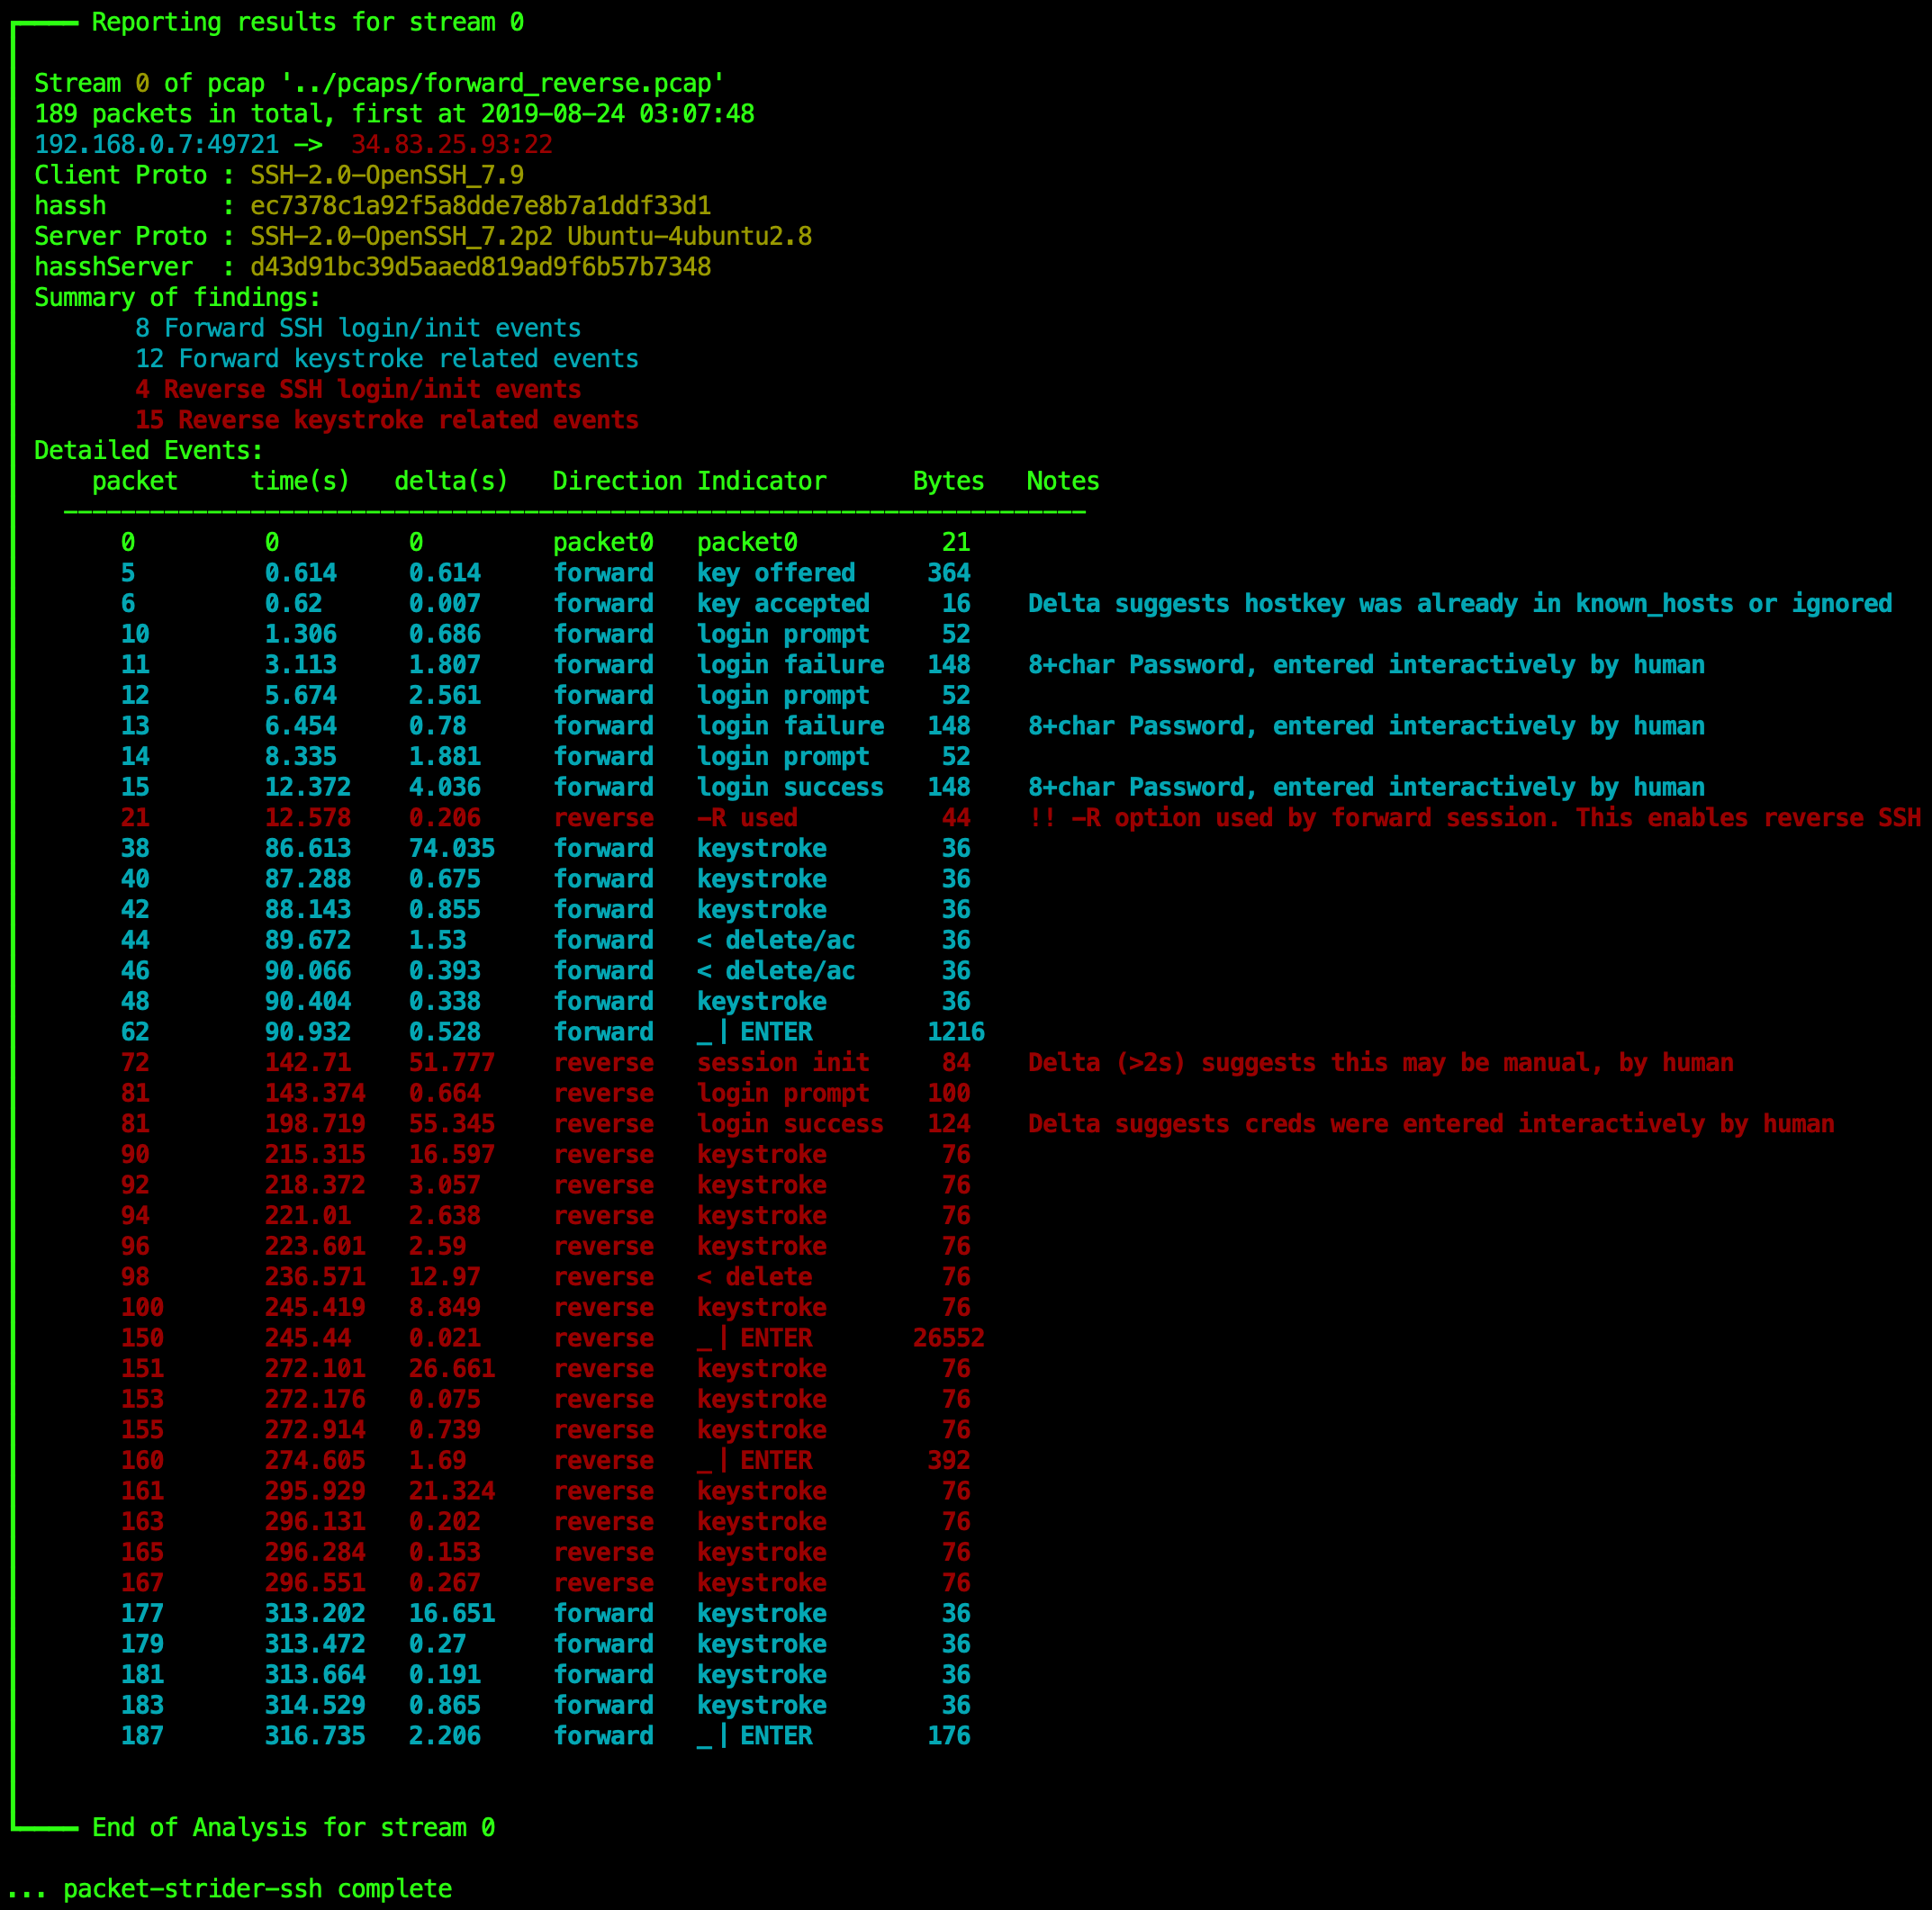 benjeems/packetstrider
A network packet forensics tool for SSH
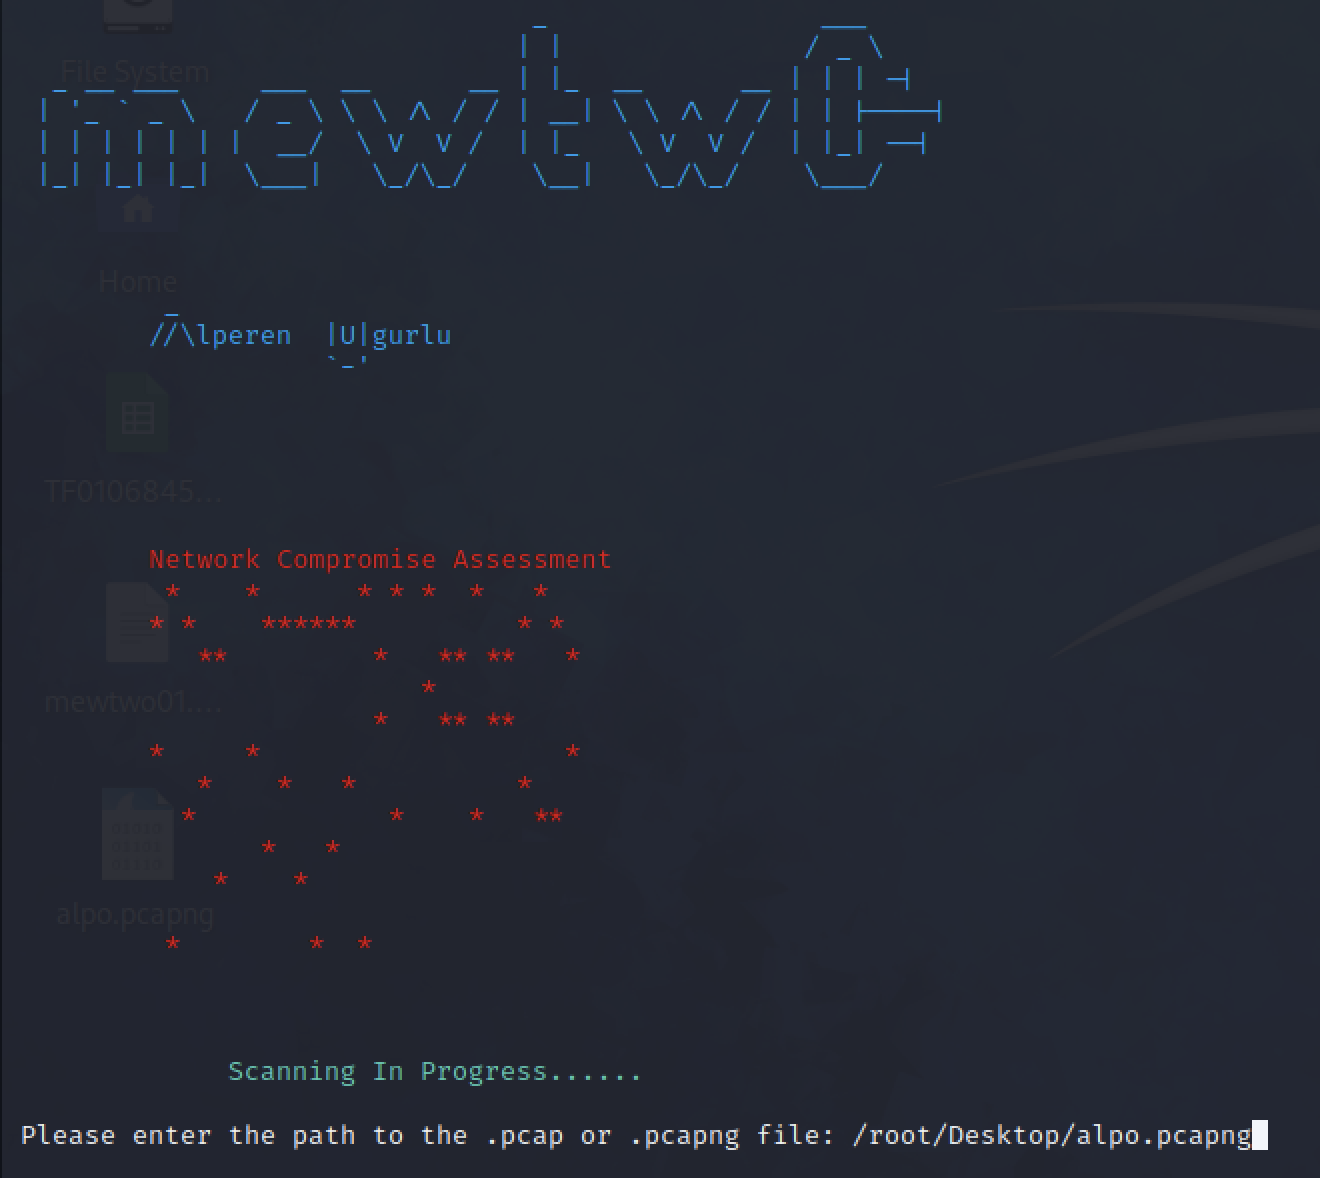 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 mhils/honeyproxy
This project is now part of @mitmproxy.
 codepr/creak
Poison, reset, spoof, redirect MITM script
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 awakecoding/wireshark-rdp
Wireshark RDP resources
 iamckn/mousejack_transmit
Wireless mouse/keyboard attack with replay/transmit poc
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 kevin-robertson/conveigh
Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool
 mspicer/pcapinator
A tool for processing a lot of pcaps using tshark
 jduck/challack
Proof-of-concept exploit code for CVE-2016-5696
 nccgroup/ebpf
eBPF - extended Berkeley Packet Filter tooling