

UPnP-Pentest-Toolkit
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
exploitationhardware-iot-securitynetwork-security+5
262
nccgroup/upnp-pentest-toolkitUPnP Pentest Toolkit for Windows
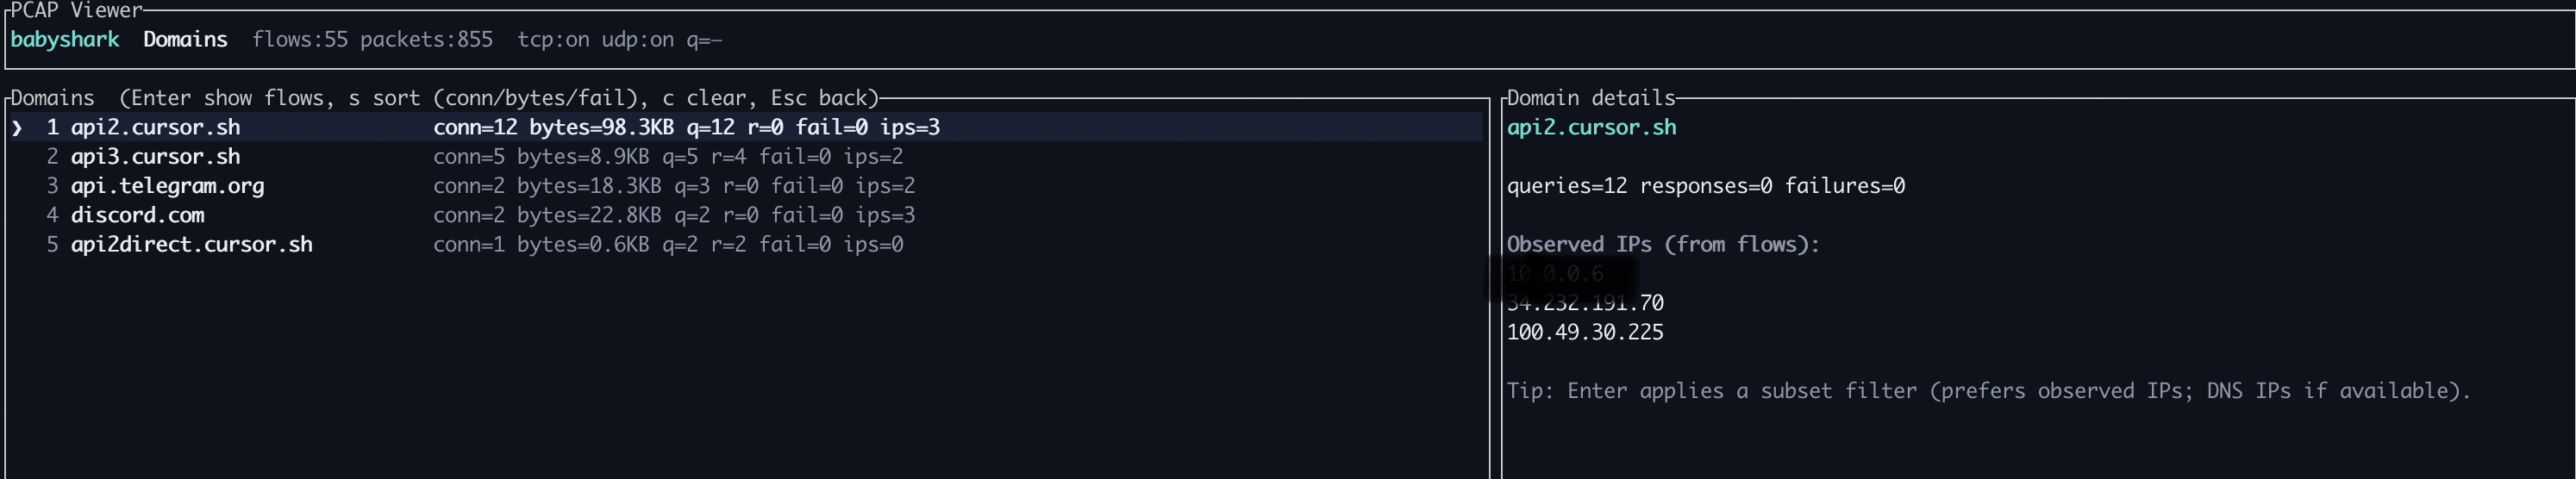 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 nccgroup/pcap-burp
Pcap importer for Burp
 leonward/openfpc
OpenFPC, Open Source Full Packet Capture
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 ipopov/starttls-mitm
A starttls-capable transparent man-in-the-middle proxy
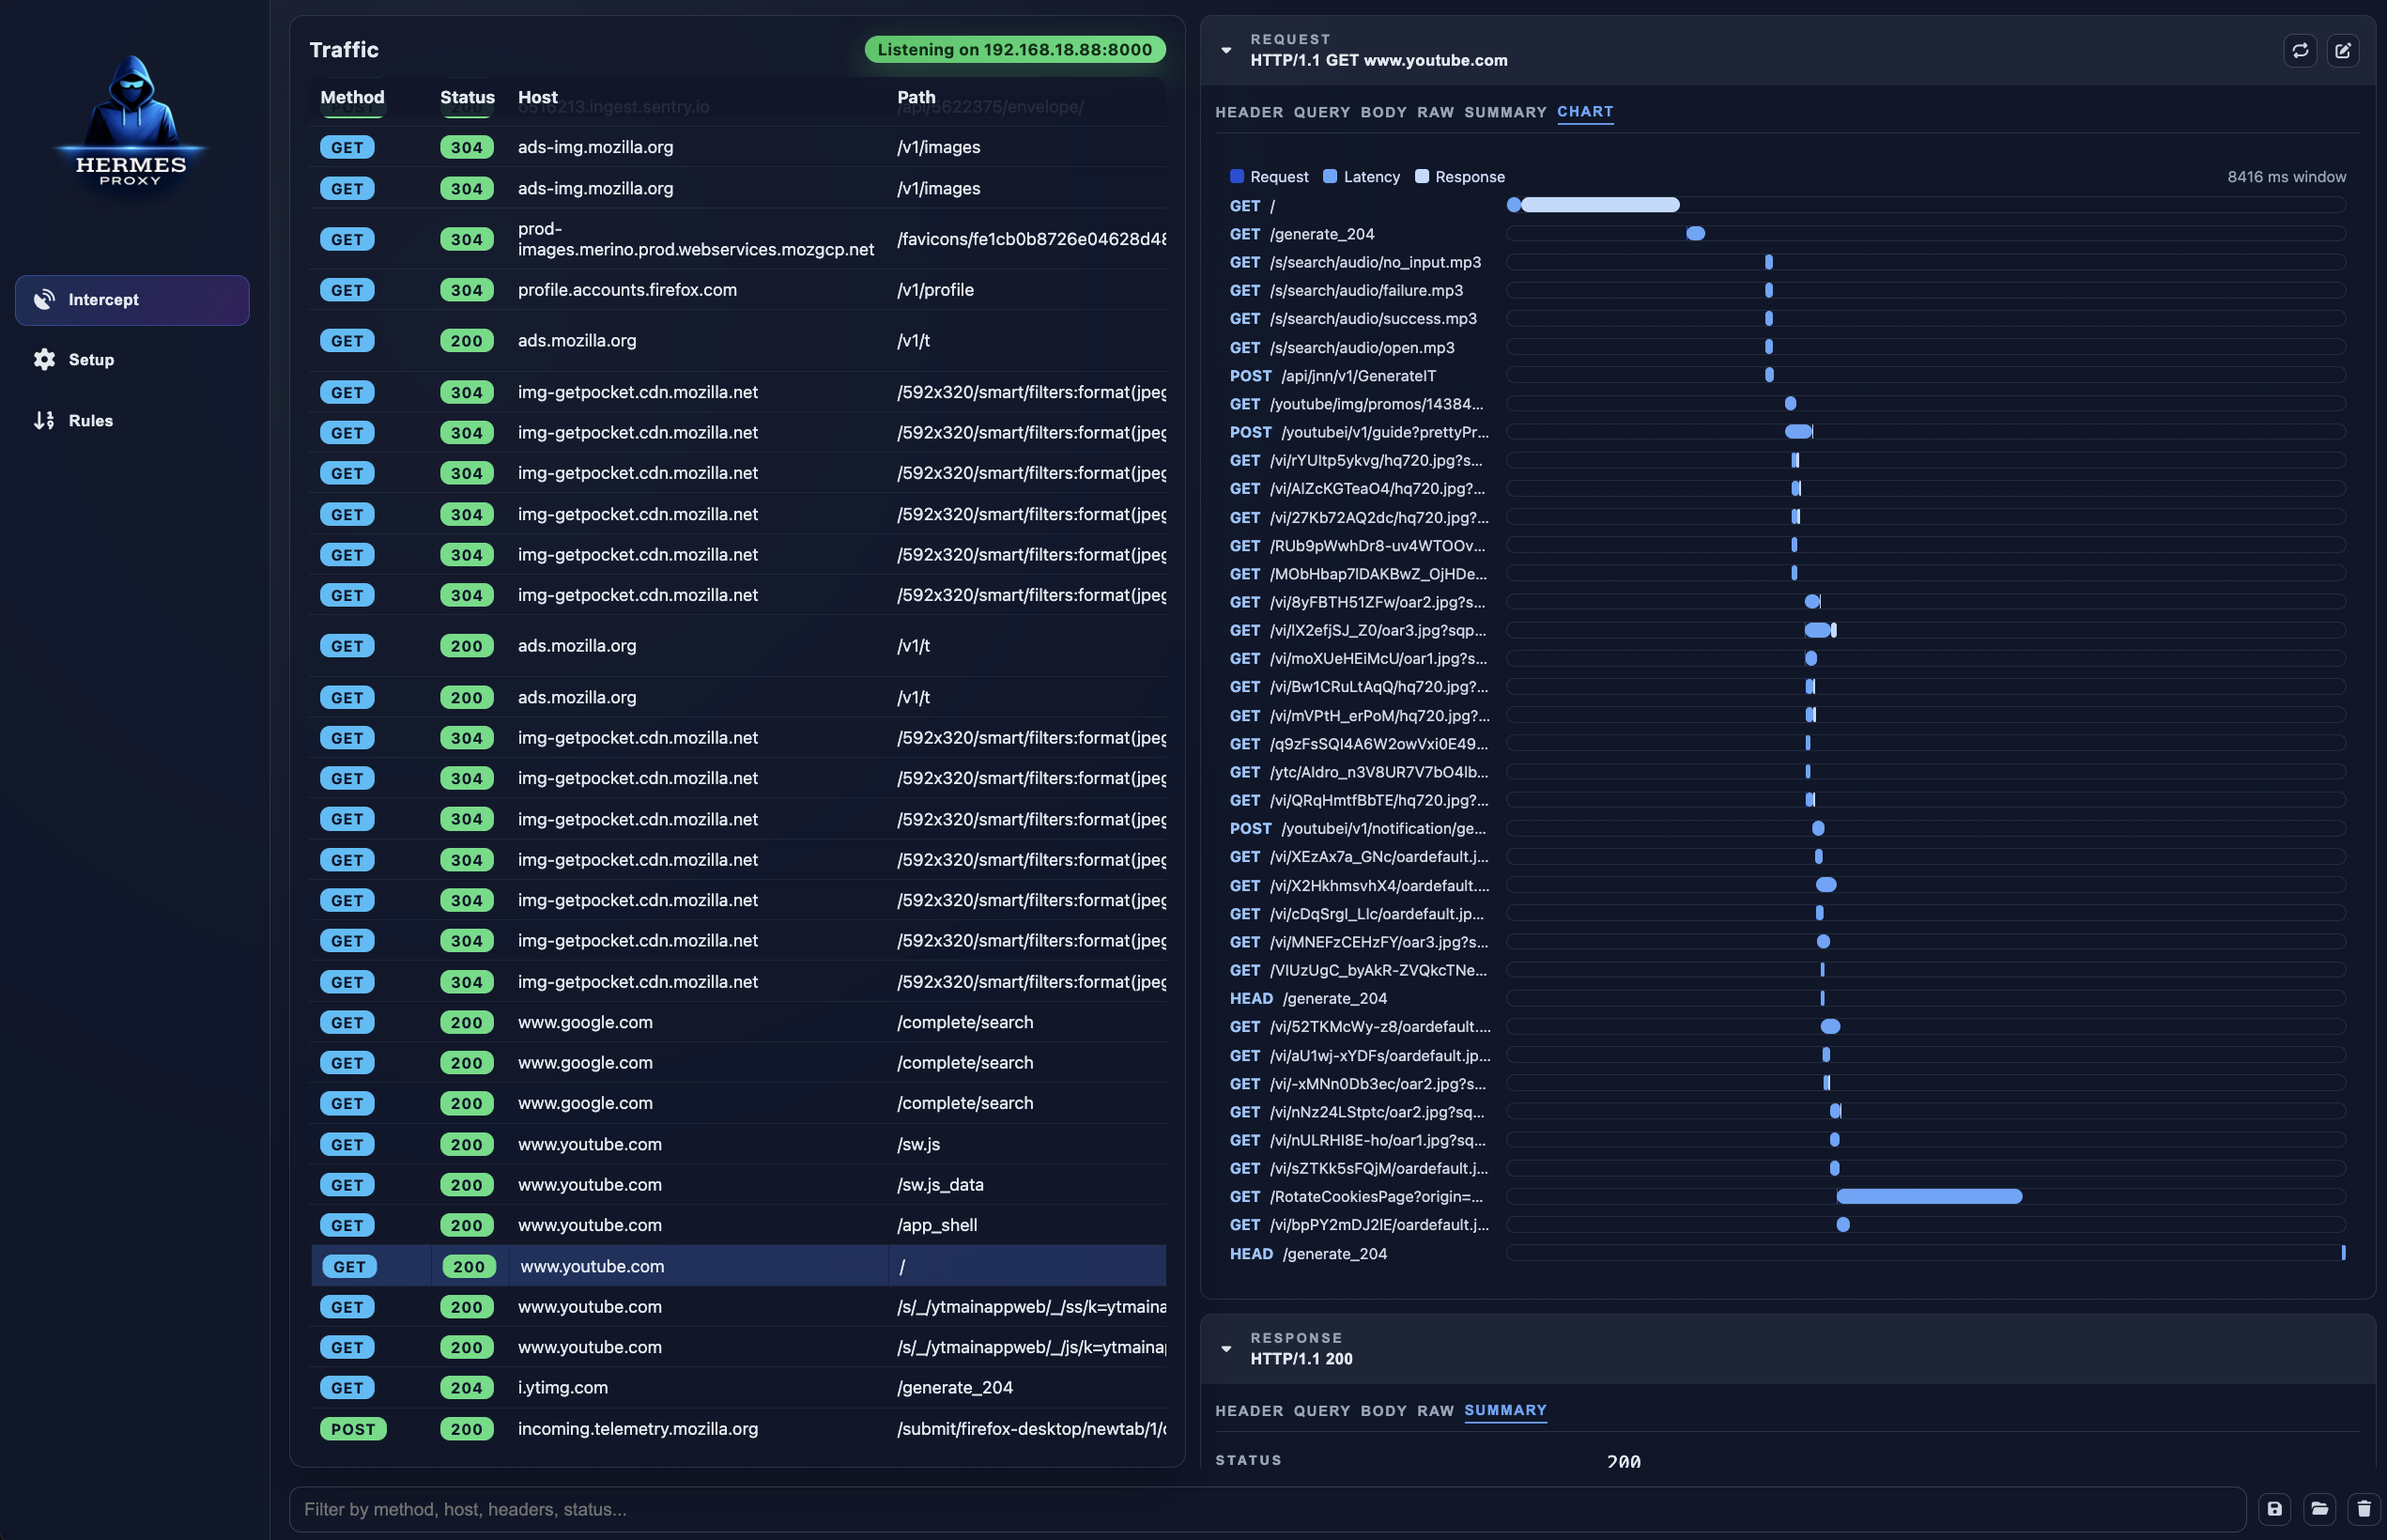 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 amlight/ofp_sniffer
An OpenFlow sniffer to help network troubleshooting in production networks.
 corelight/raspi-corelight
Corelight@Home script
 lpefferkorn/ipdecap
Decapsulate traffic encapsulated within GRE, IPIP, 6in4, ESP (ipsec) protocols, can also remove IEEE 802.1Q (virtual lan) header. Works with pcap…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol