

kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 electroniccats/catsniffer
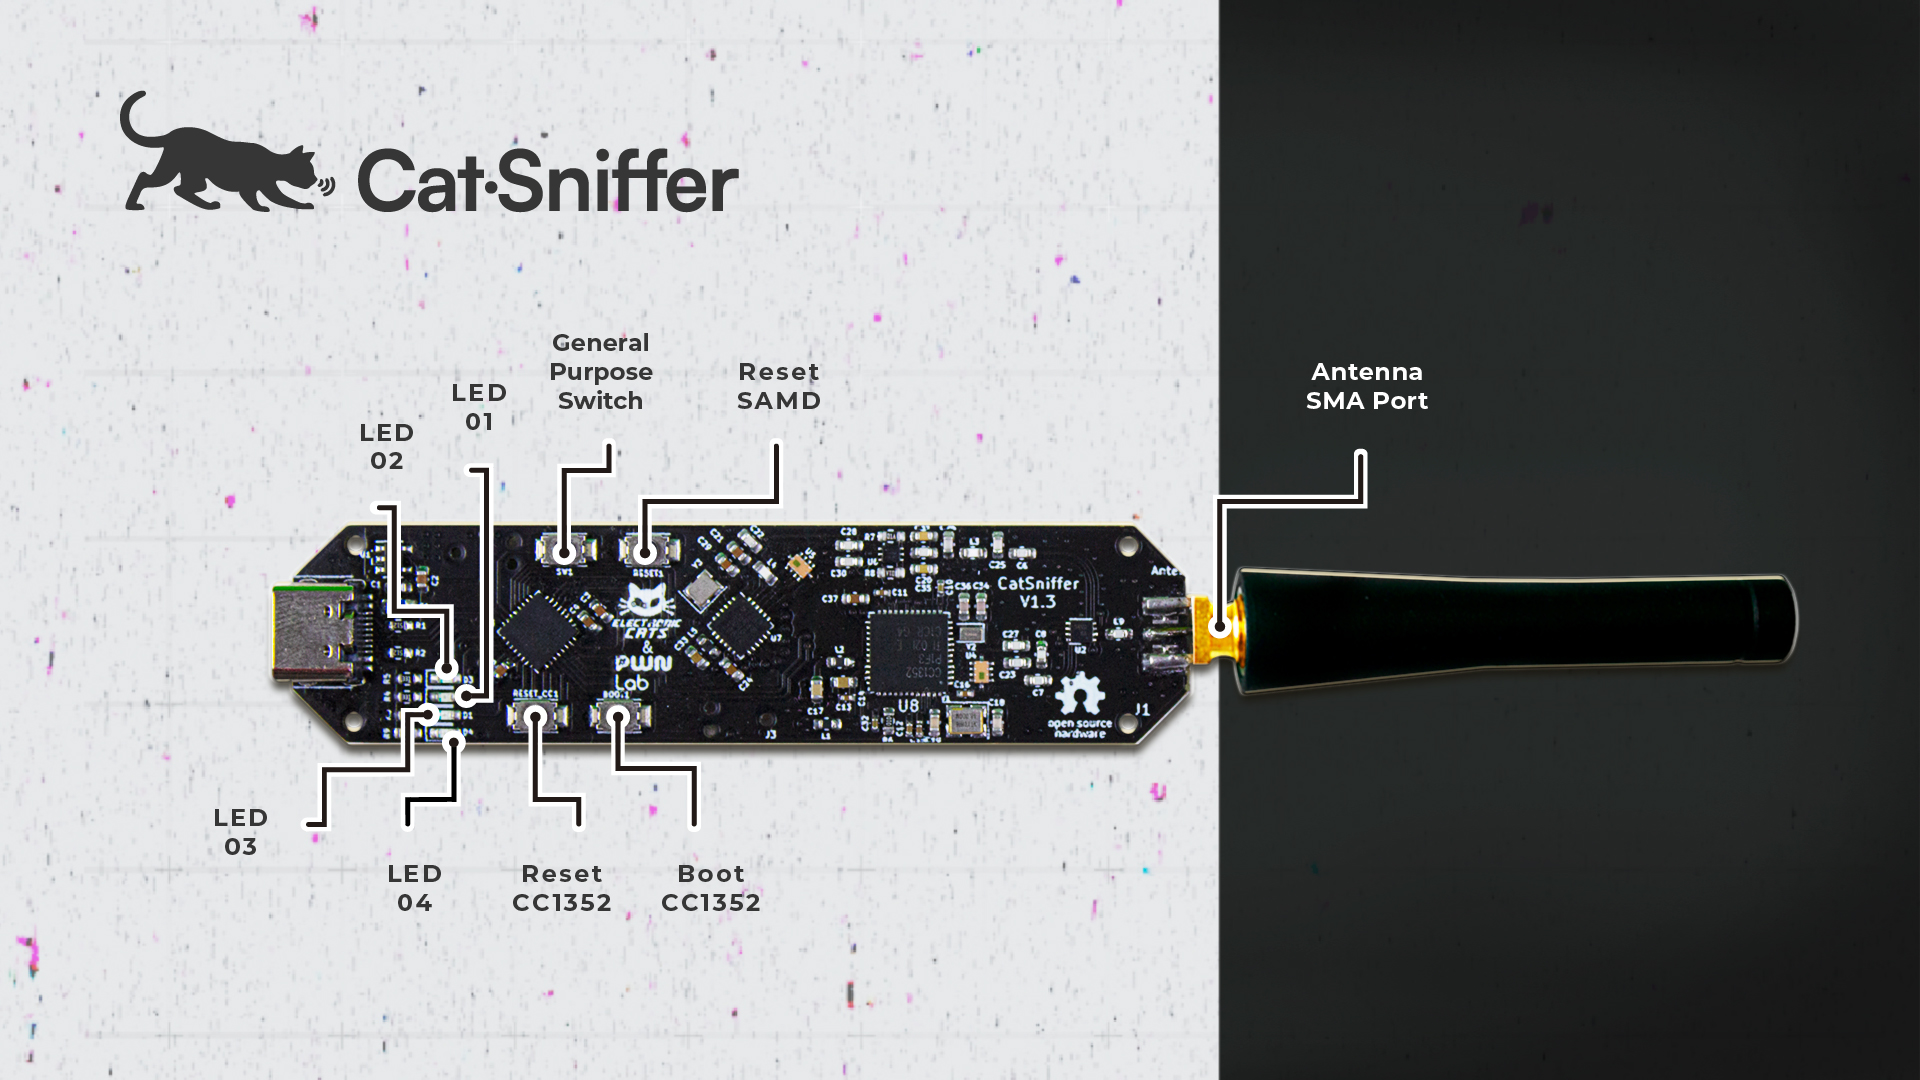
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 owasp/pysap
pysap is an open source Python library that provides modules for crafting and sending packets using SAP's NI, Diag, Enqueue, Router, MS, SNC, IGS,…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 aman-sharma-dev/netsentryx
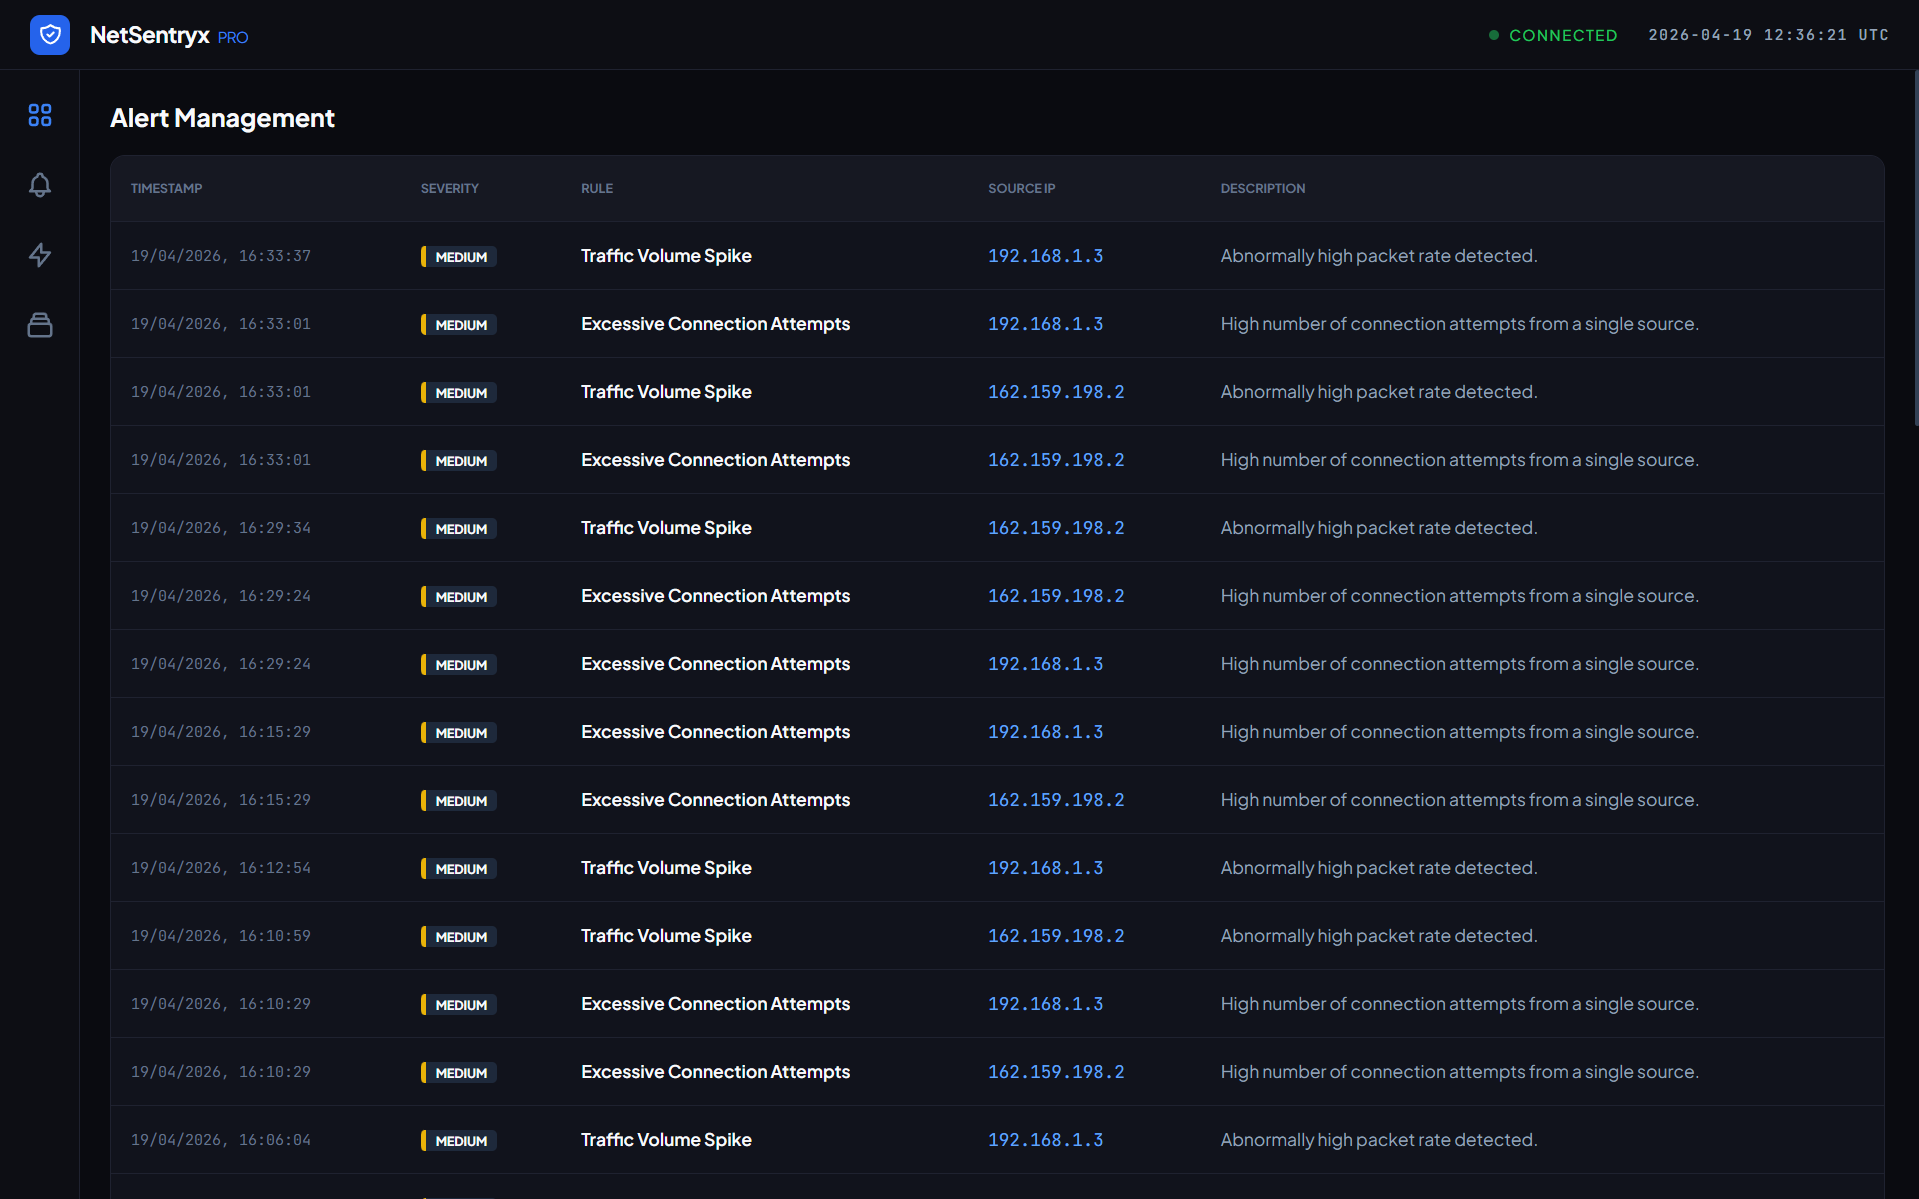
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
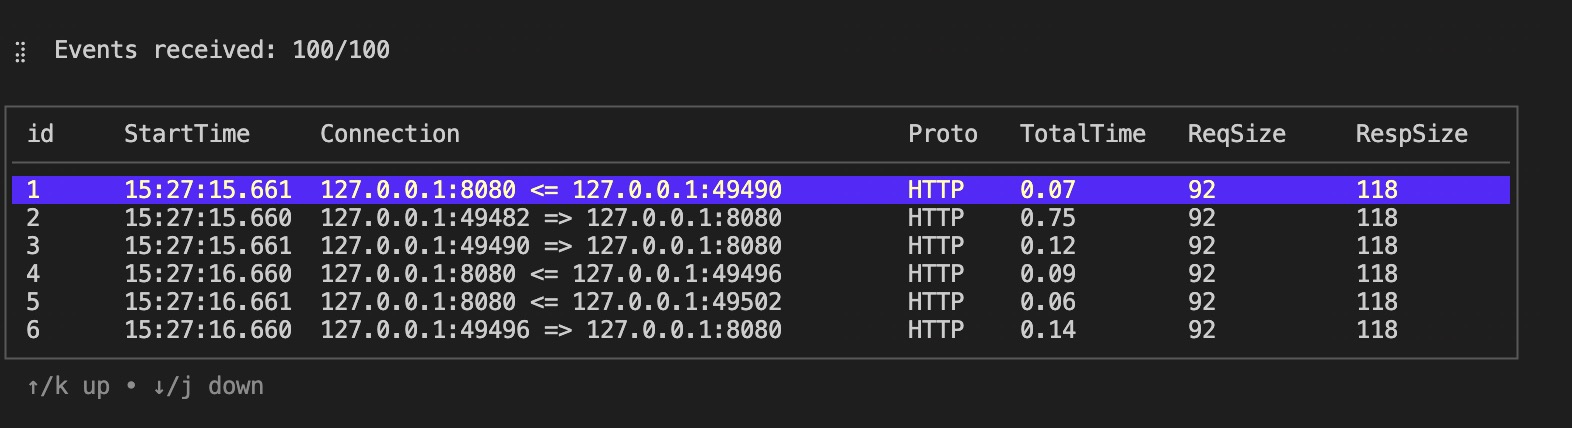 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
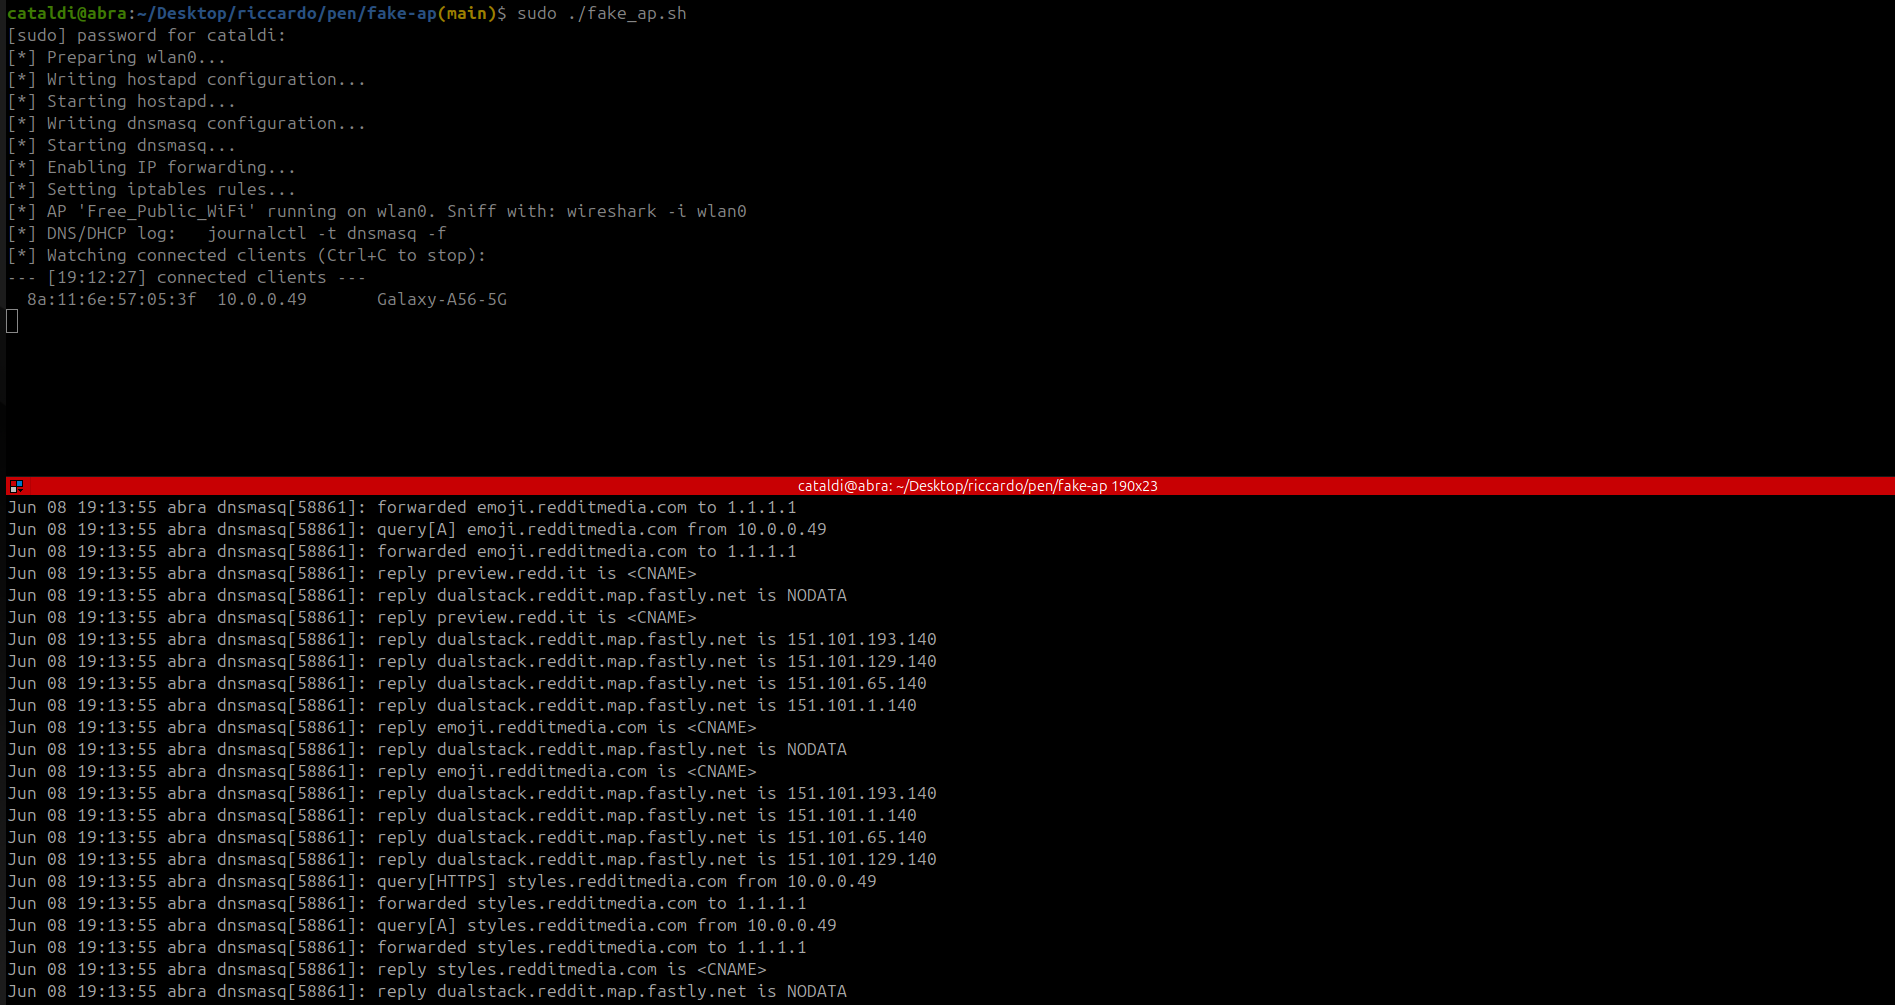 riccardocataldi/access-point
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
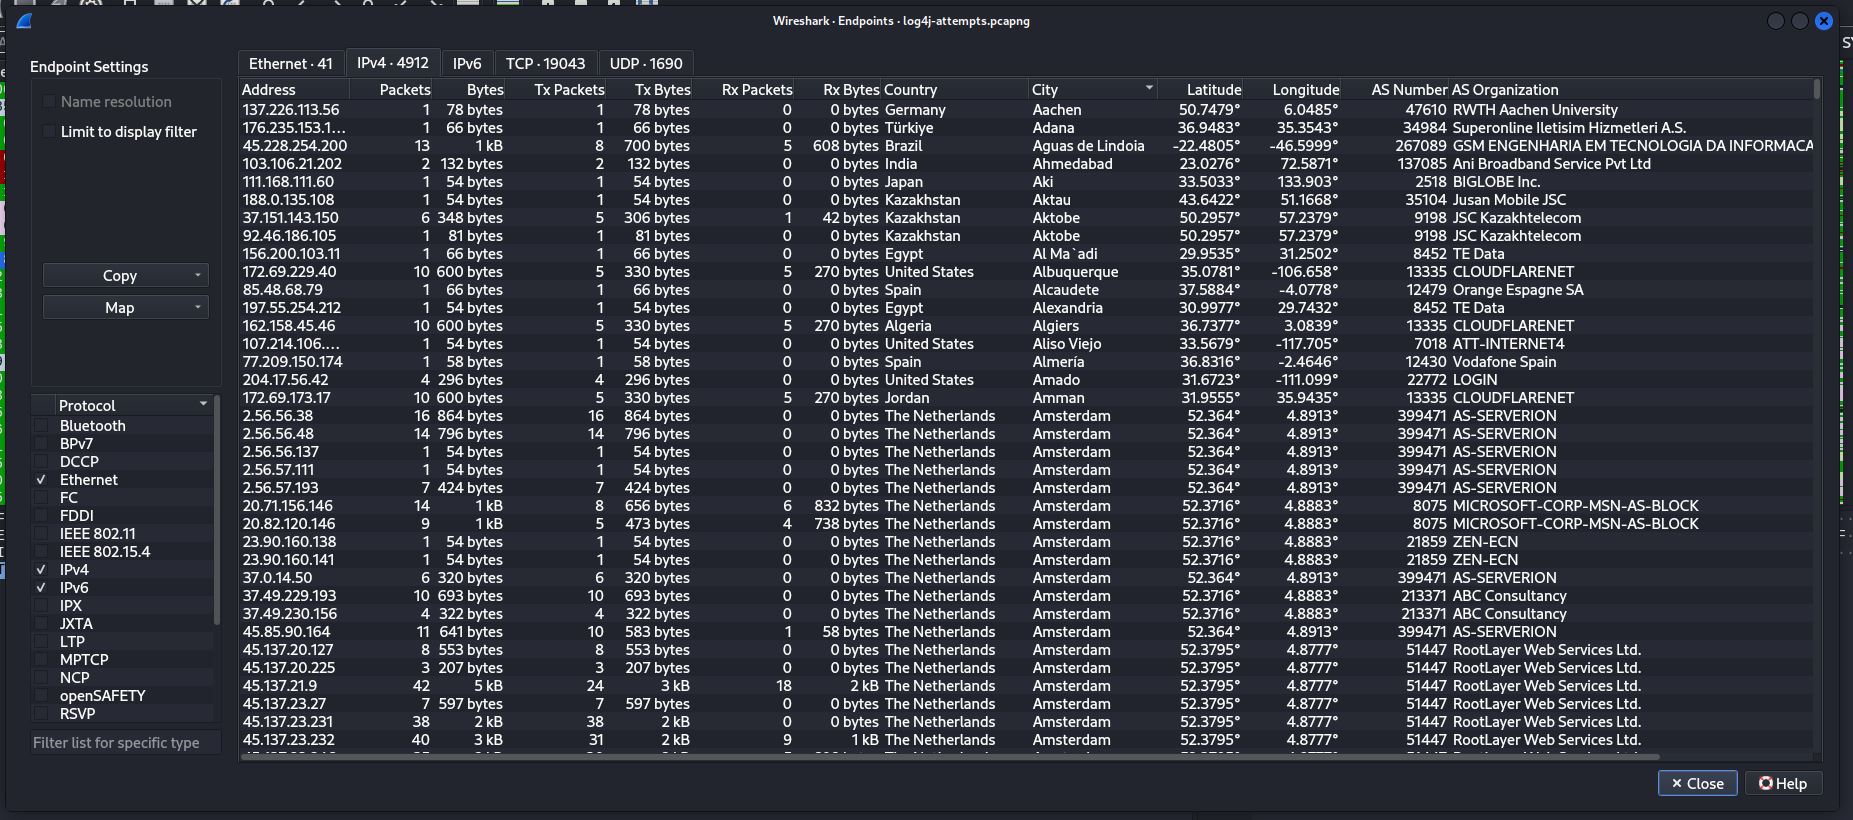 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…