
ecapture
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
android-securitydatabase-securitydynamic-analysis-sandboxing+3
15.5k
gojue/ecaptureCapturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
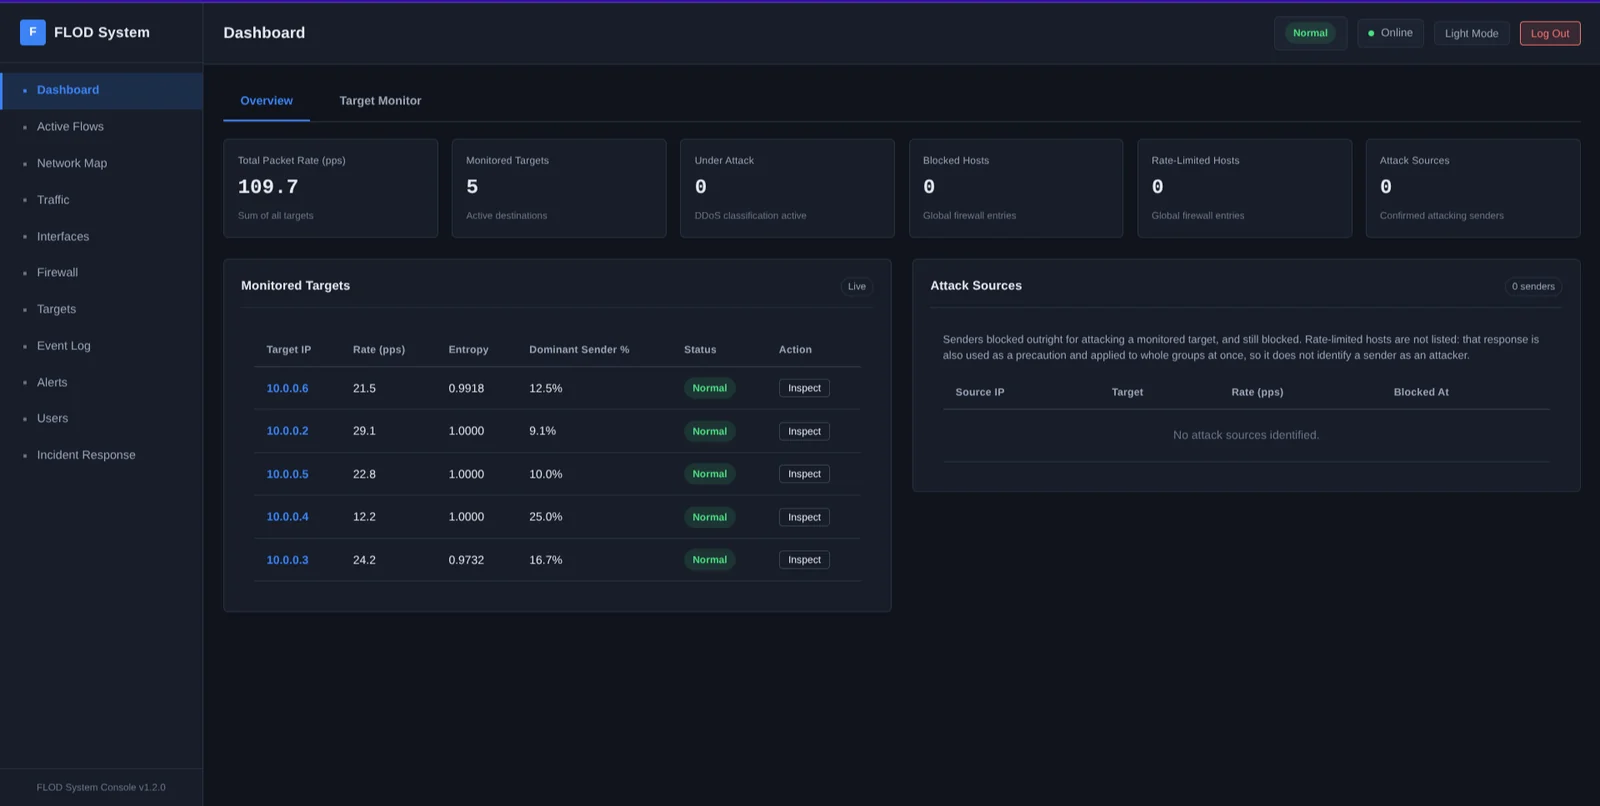 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
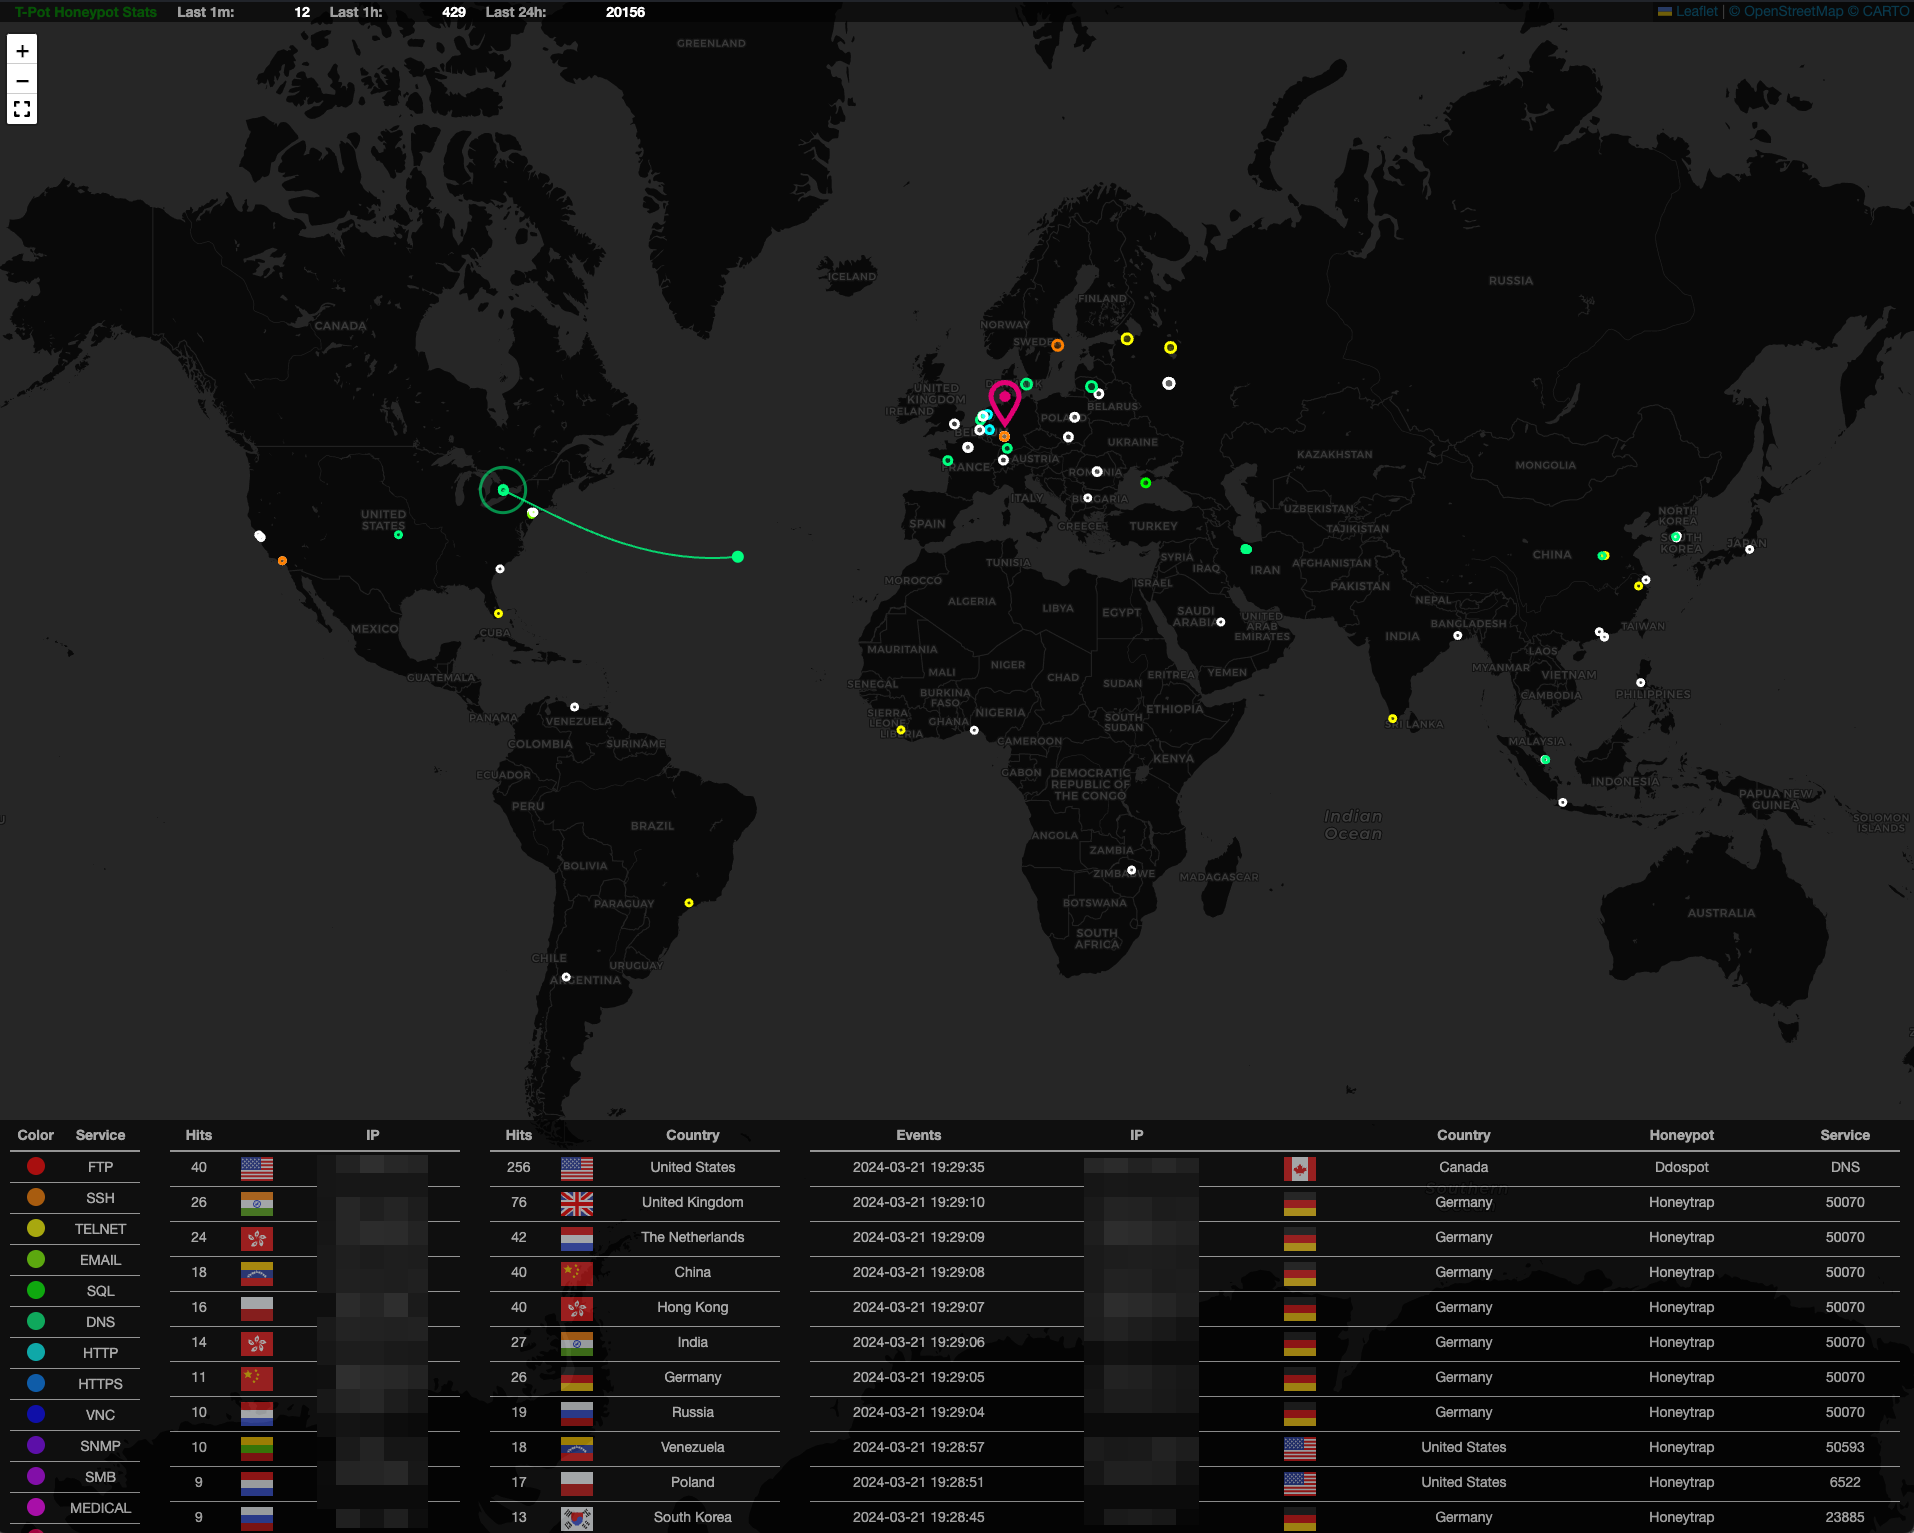 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
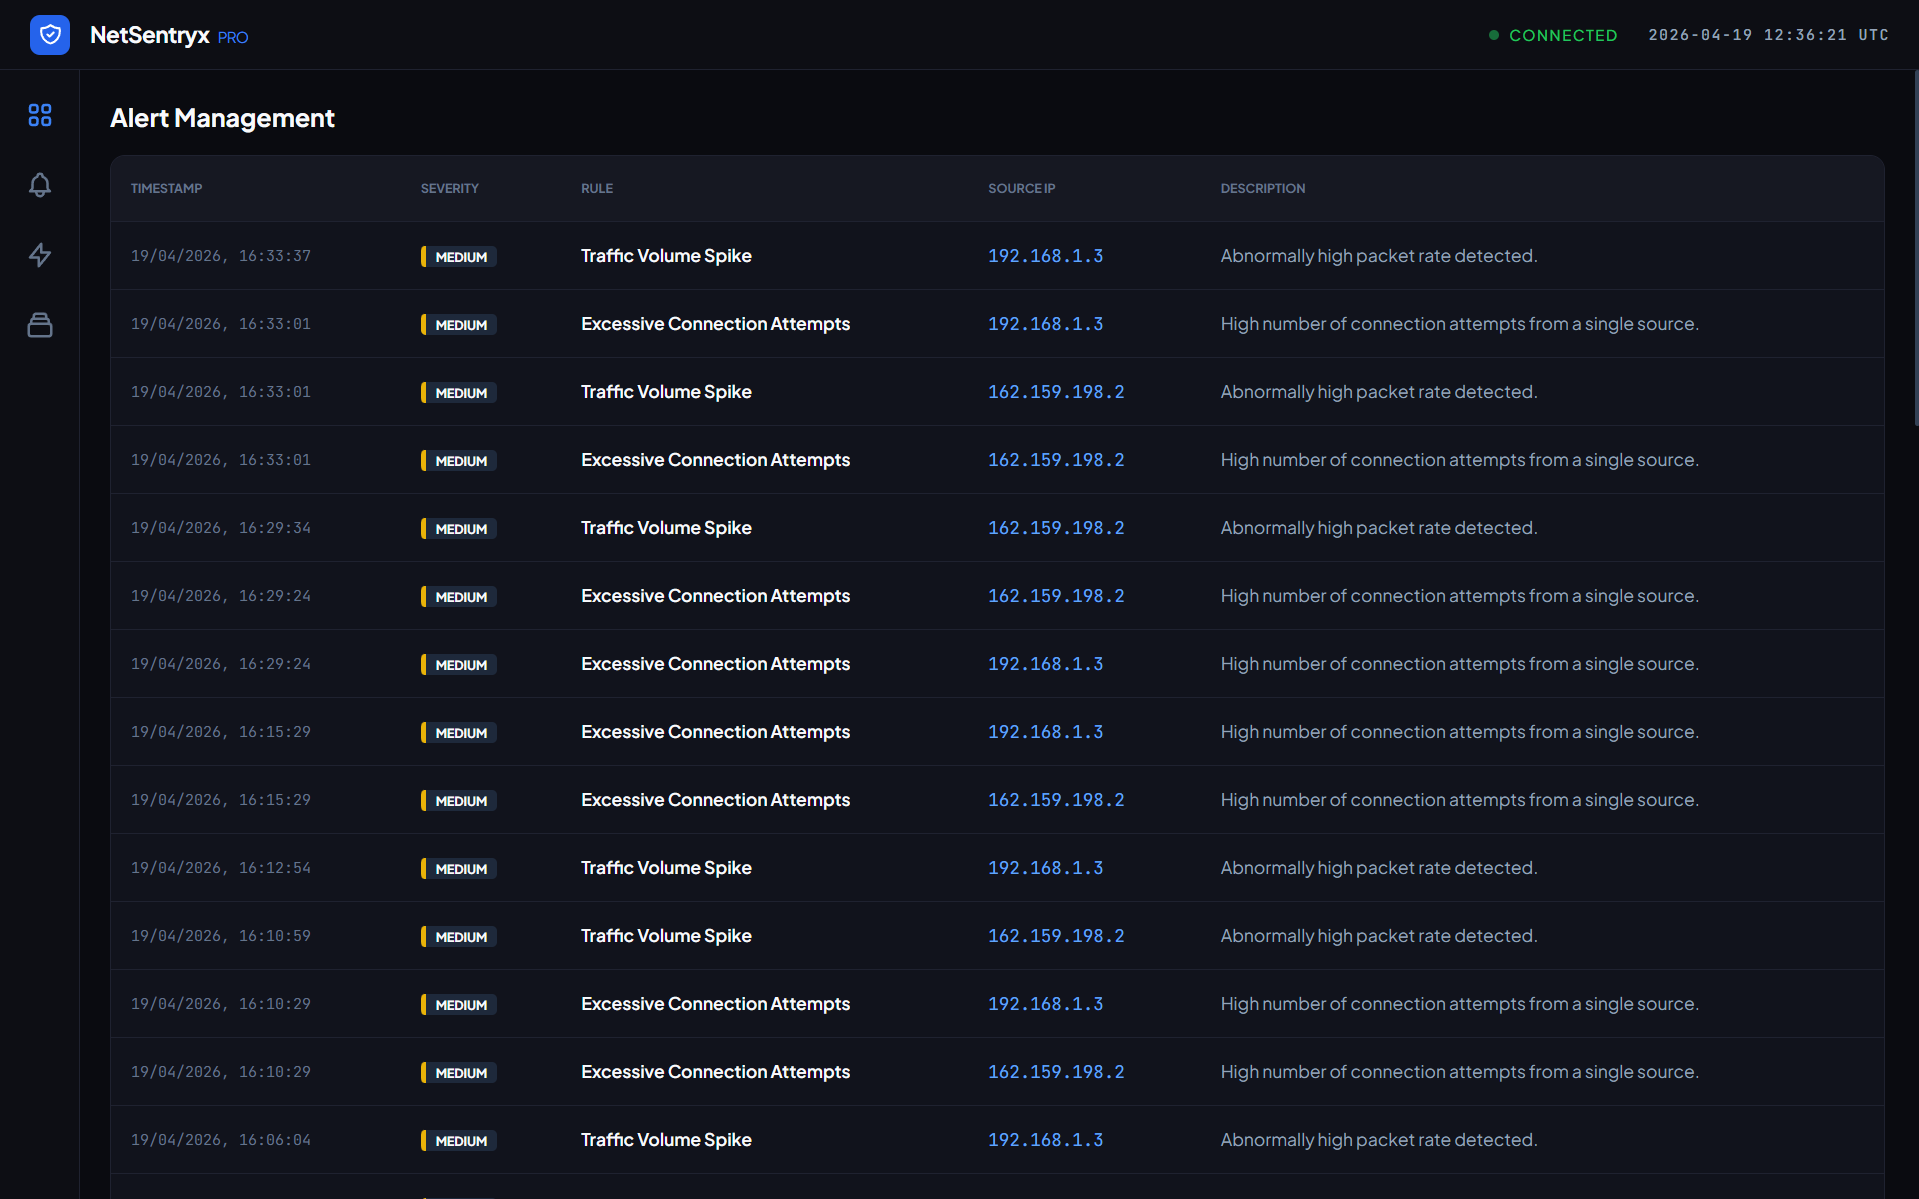 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
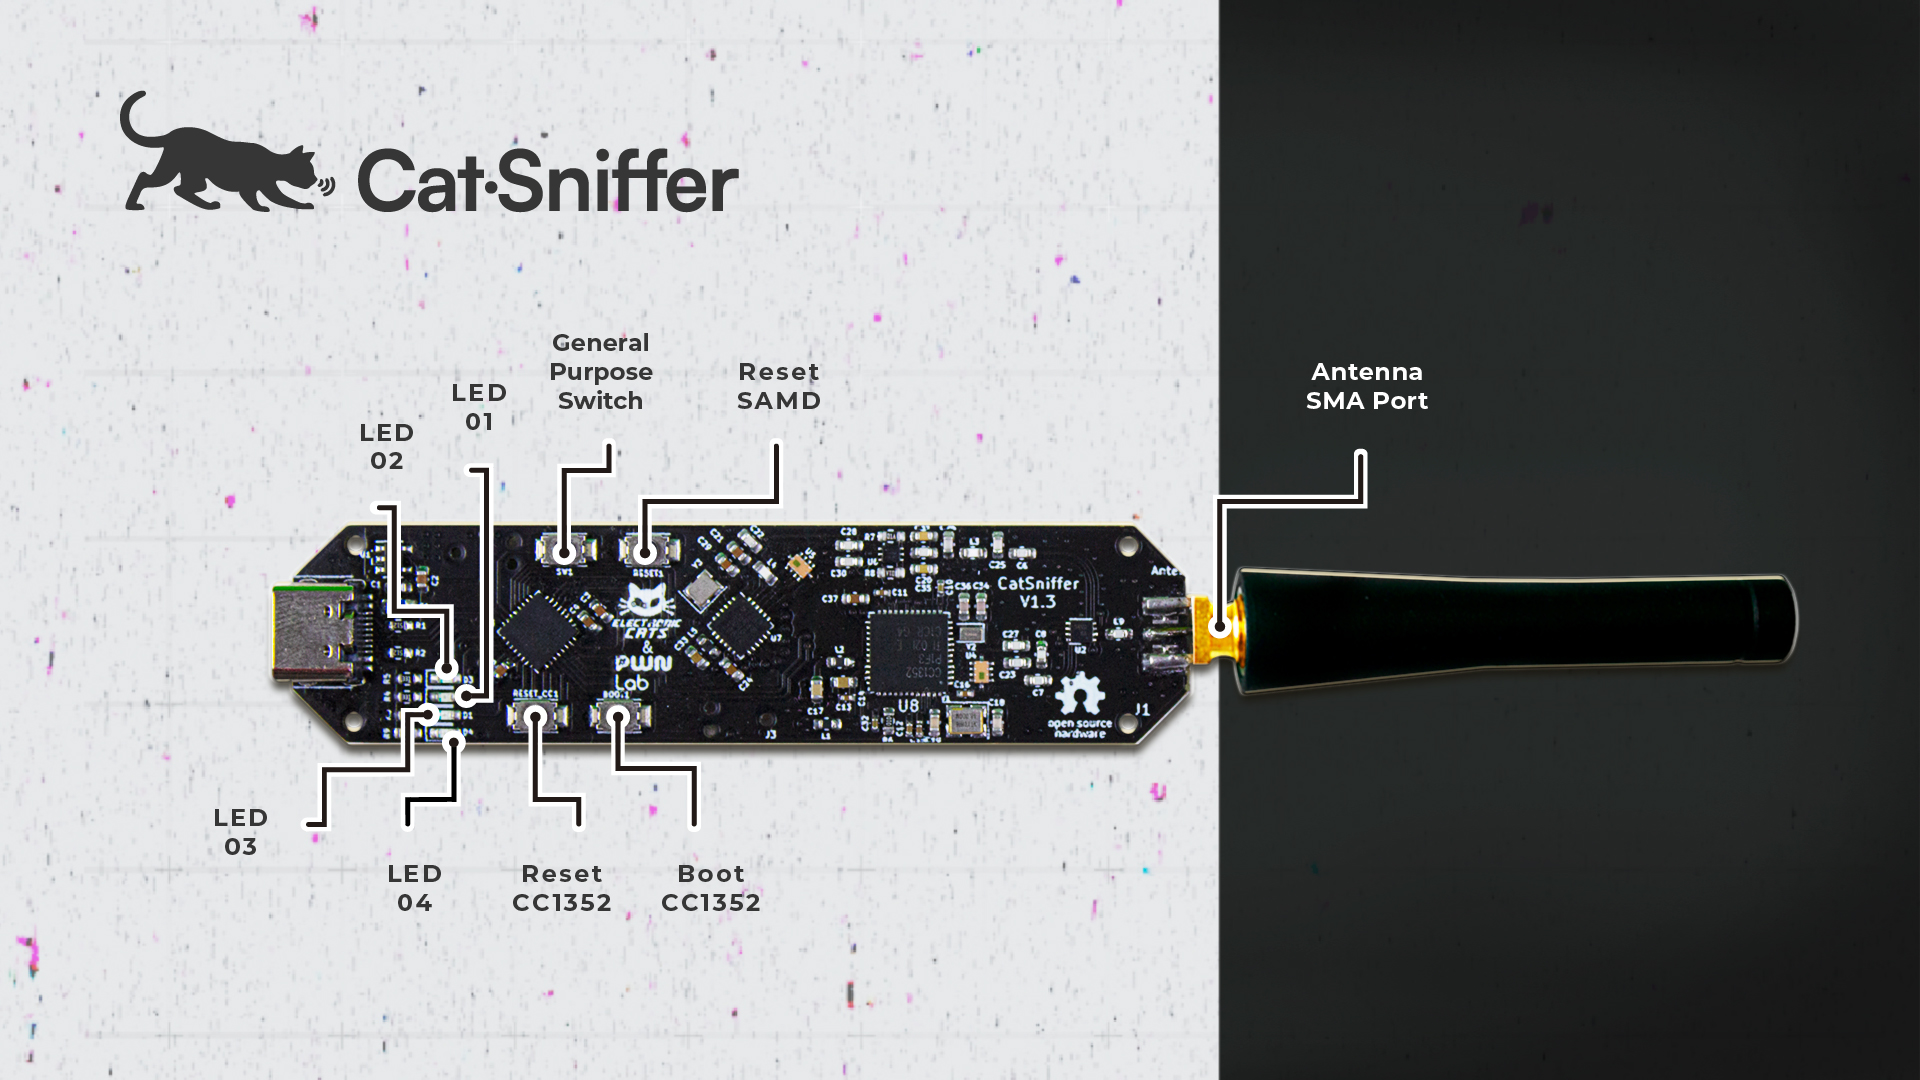 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 kdzwinel/betwixt
:zap: Web Debugging Proxy based on Chrome DevTools Network panel.
 mrschyte/socksmon
Monitor arbitrary TCP traffic using your HTTP interception proxy of choice
 ashishraste/arp-dns-attacks
ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library