
kamene
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
information-gatheringnetwork-mappingnetwork-security+3
872
phaethon/kameneNetwork packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 elderlypirate/bus_pirate
Multi-protocol firmware for a hardware hacking tool supporting SPI, I2C, JTAG, UART, 1-Wire, bus sniffing, logic analysis, and microcontroller…
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
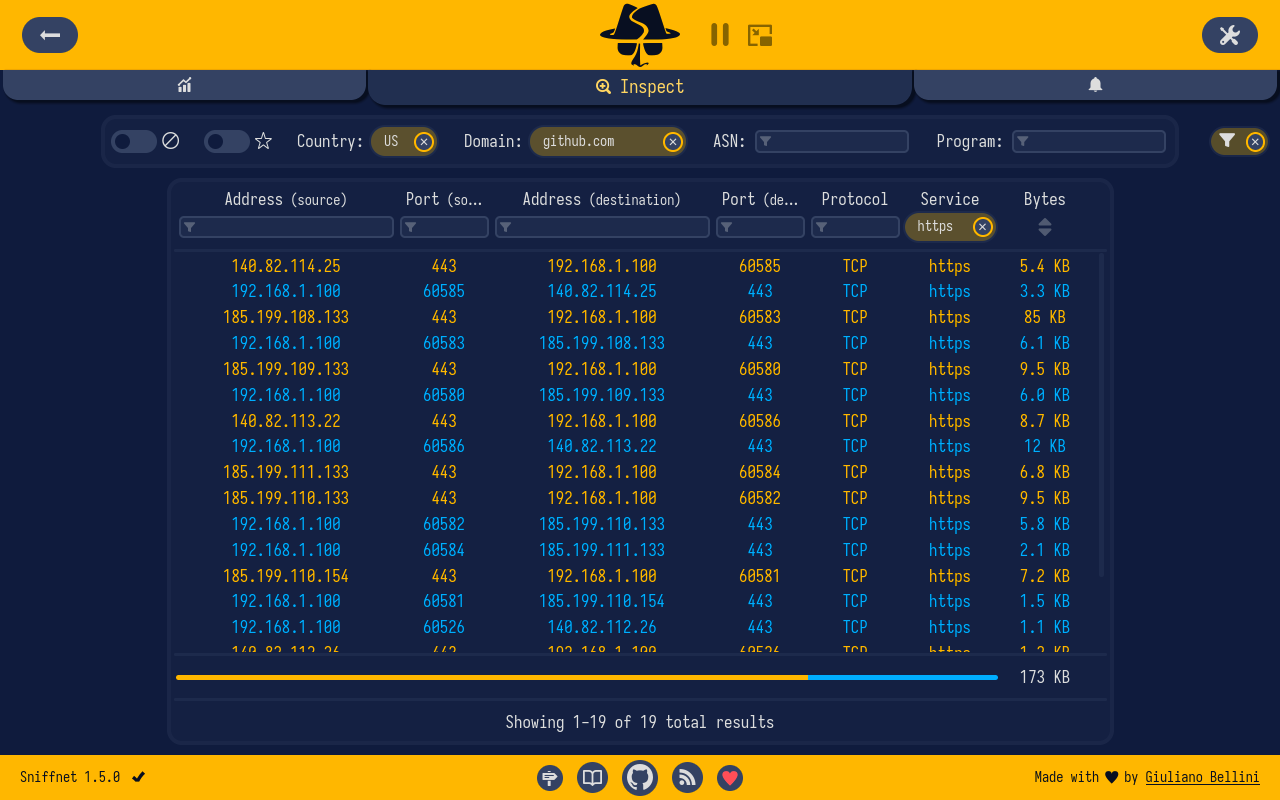 gyulyvgc/sniffnet
Comfortably monitor your network traffic 🕵️♂️
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 lele394/dnsnitch
DNSnitch is a local, privacy-first DNS server that puts you in complete control of your network traffic. Unlike passive blocklists, DNSnitch operates…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
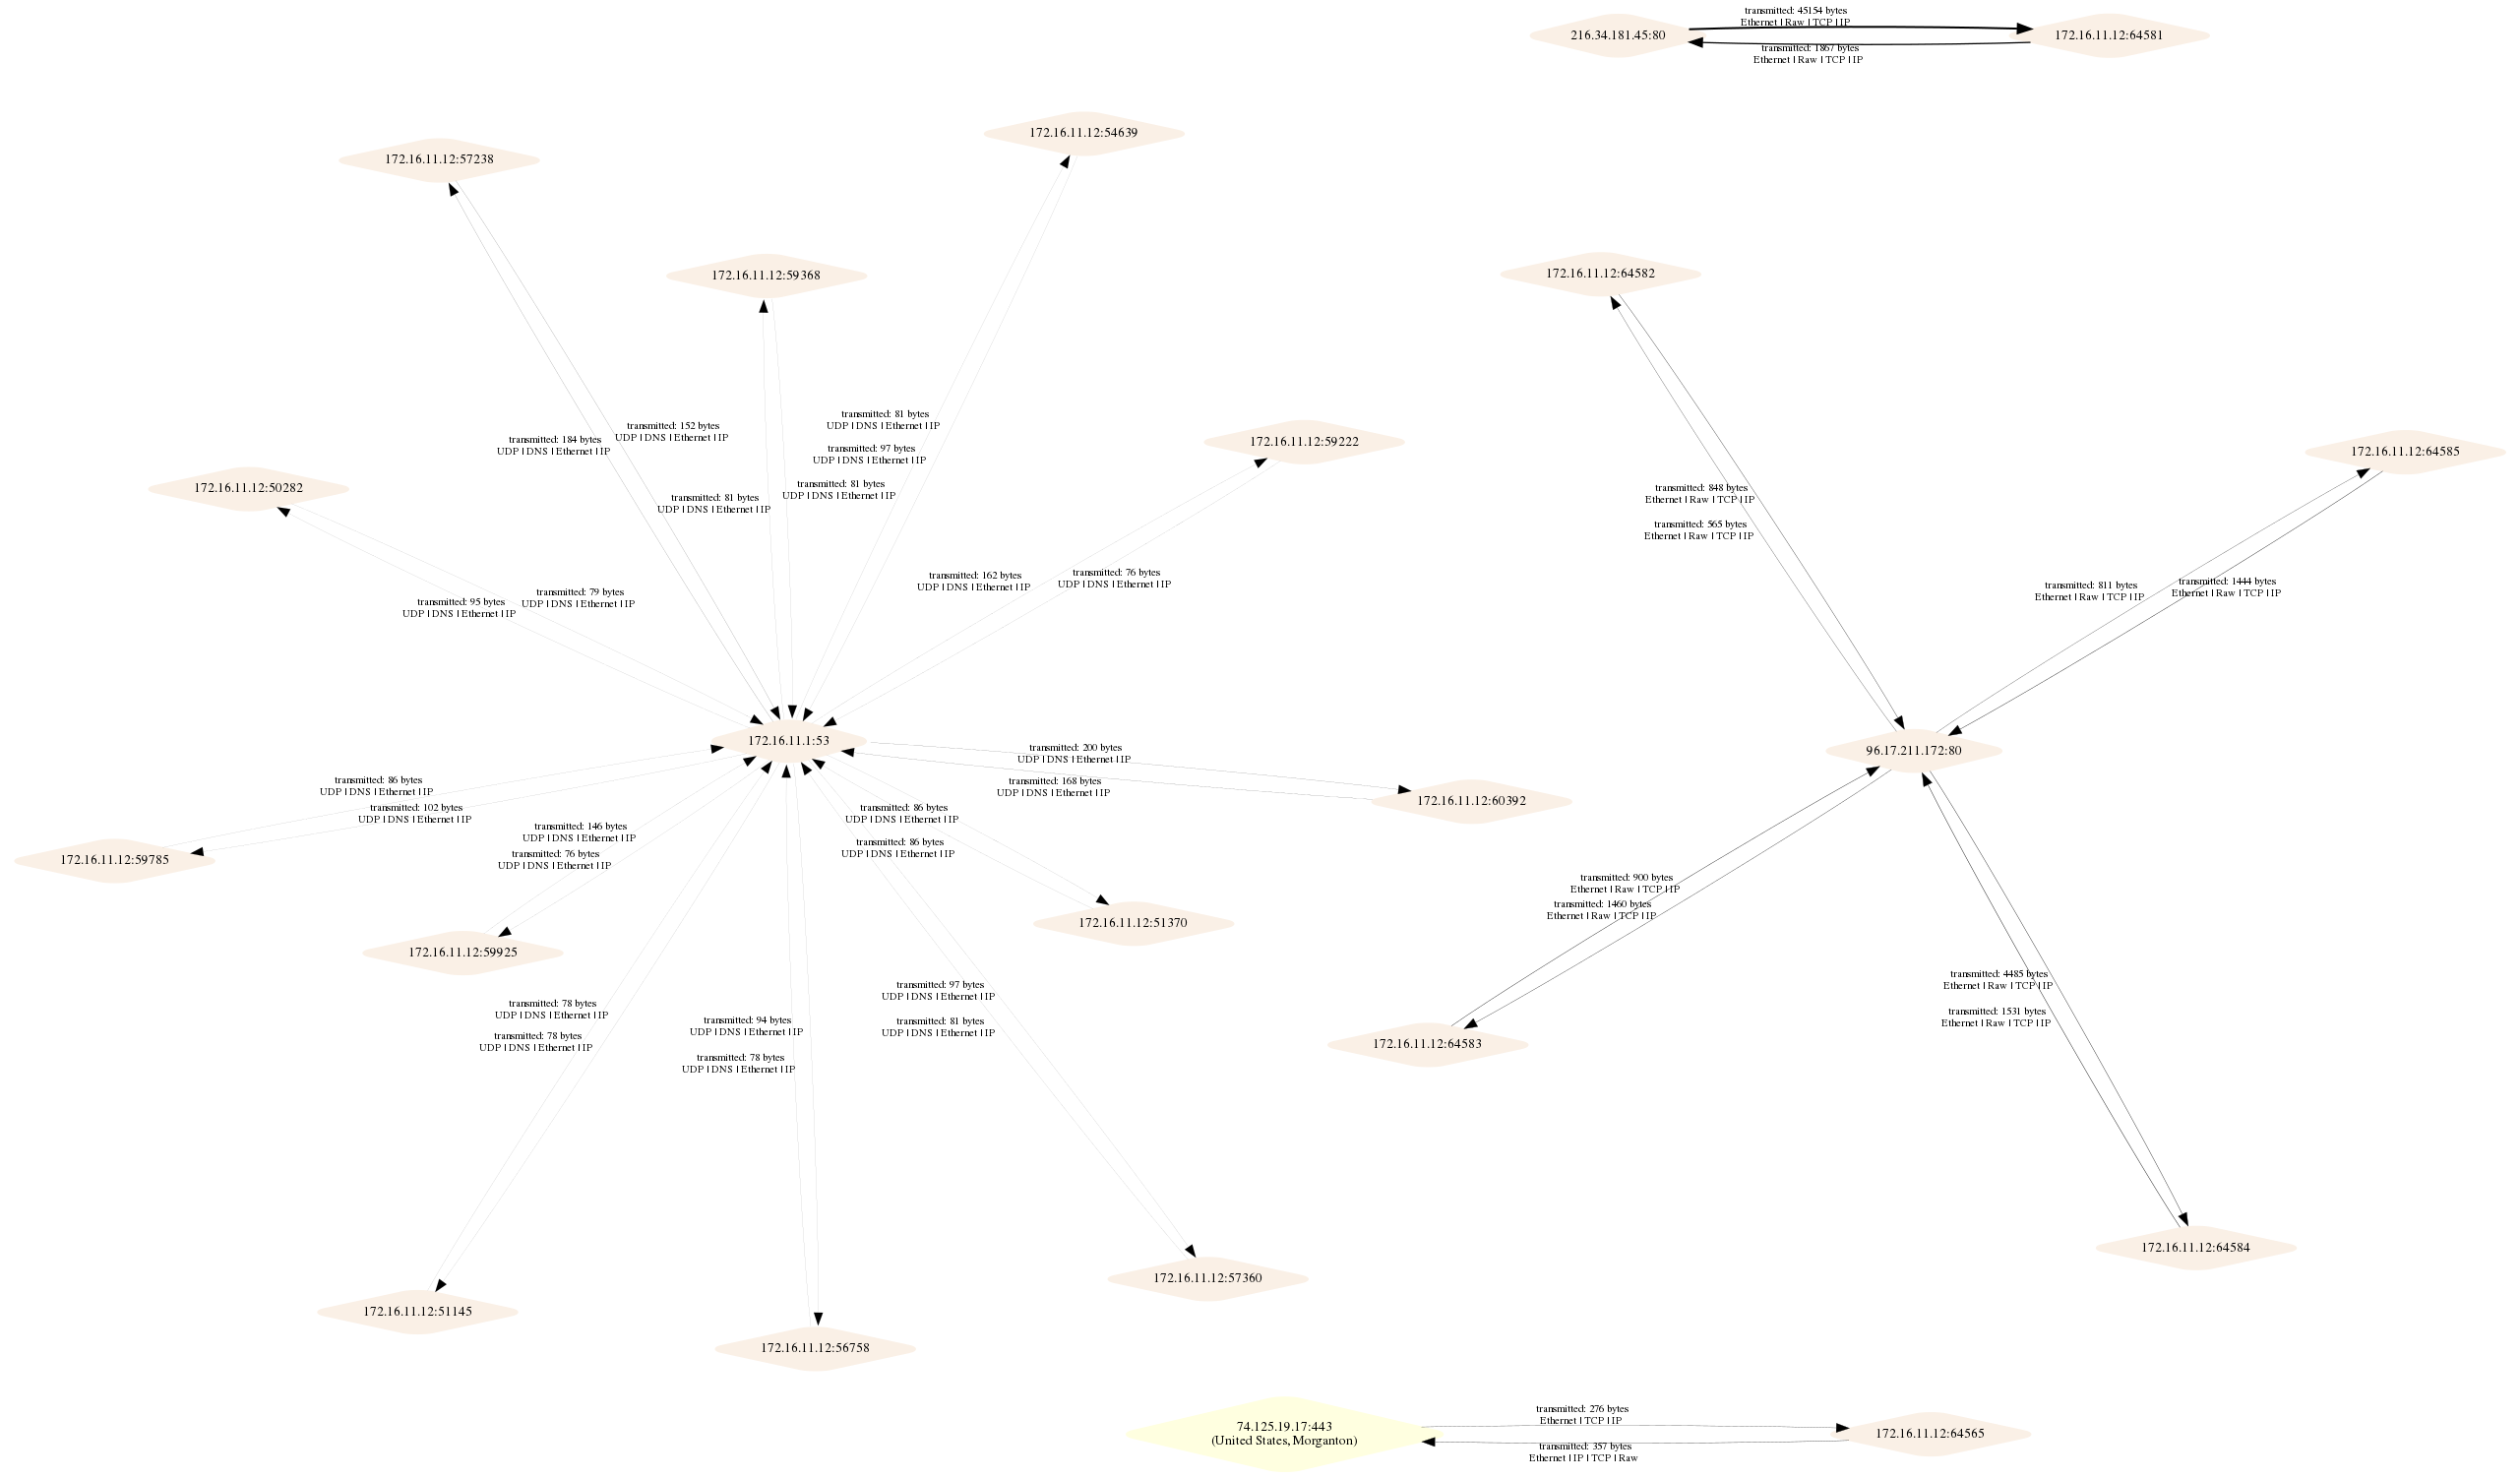 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 darkoperator/dnsrecon
DNS Enumeration Script
 fenkohq/dnsmonster
Passive DNS Capture and Monitoring Toolkit
 camp0/aiengine
Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
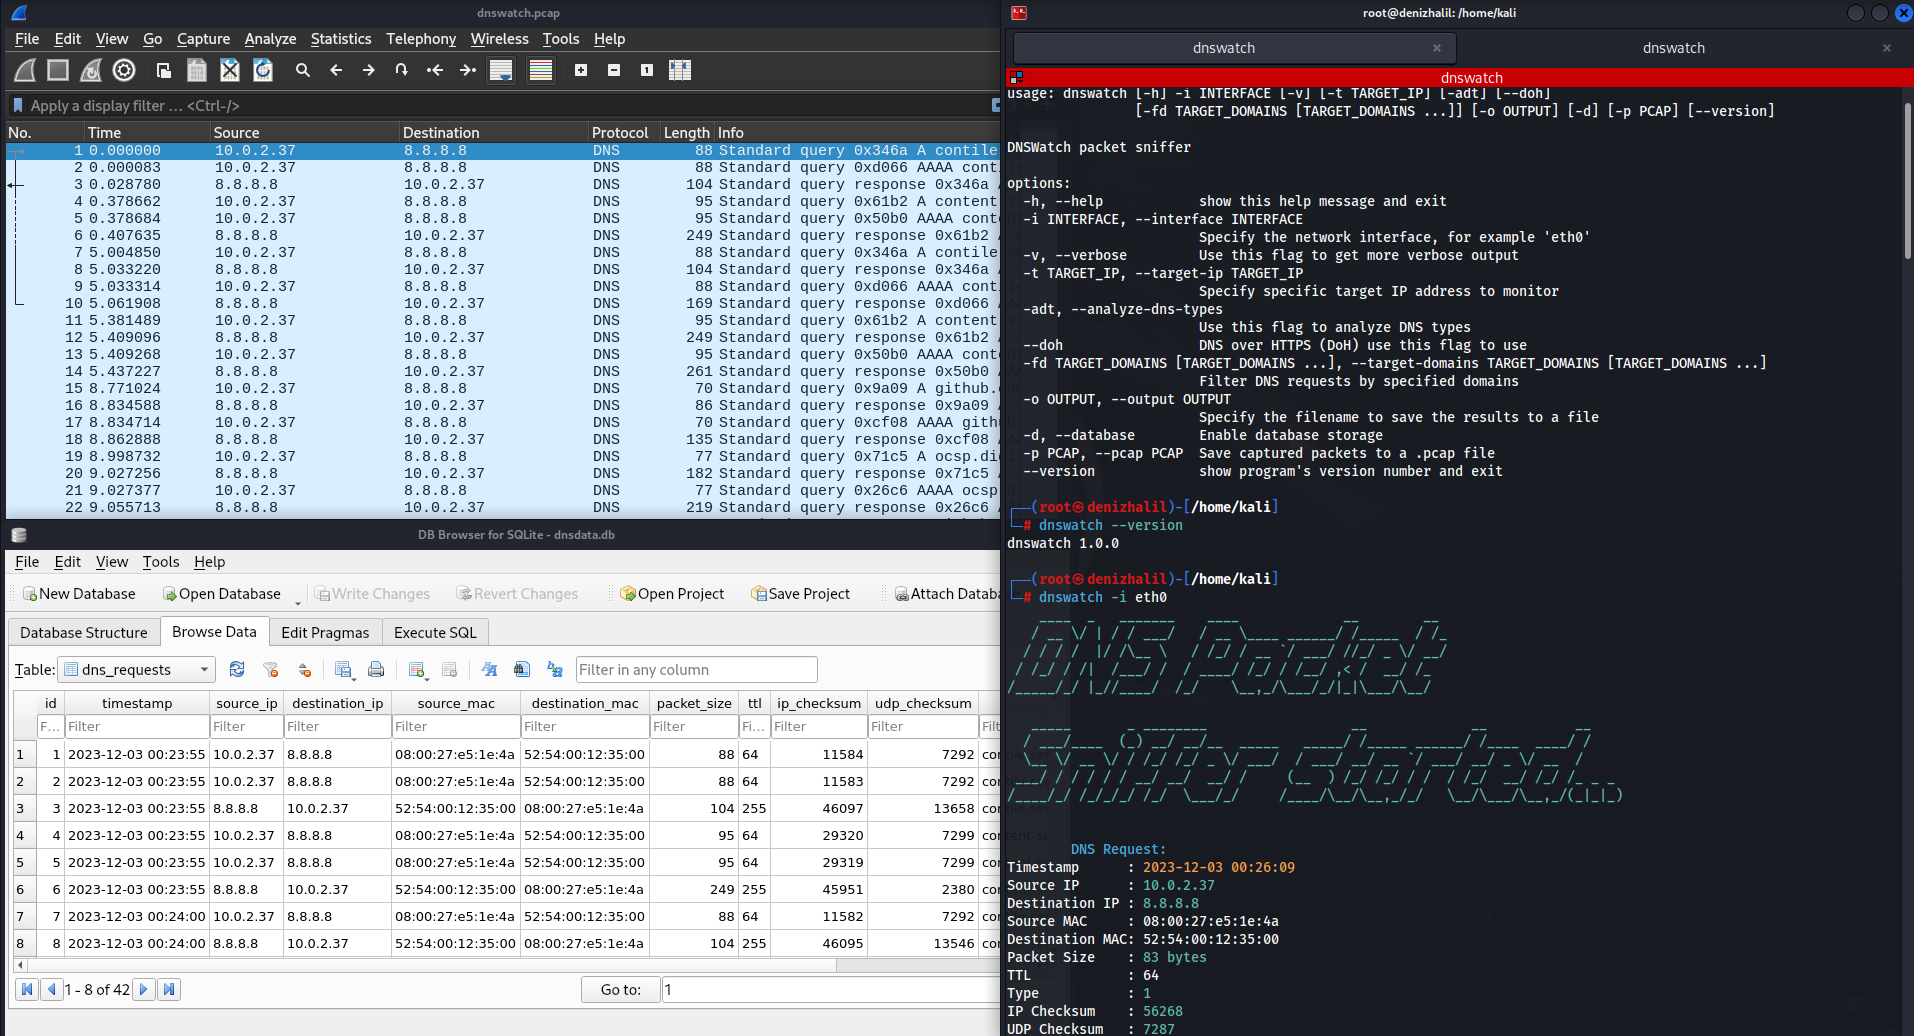 halildeniz/dnswatch
DNS traffic sniffer and analyzer for monitoring, filtering, and detecting anomalies in DNS queries. Features include PCAP export, DoH support, and a…
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…