
spookyssl-pcaps
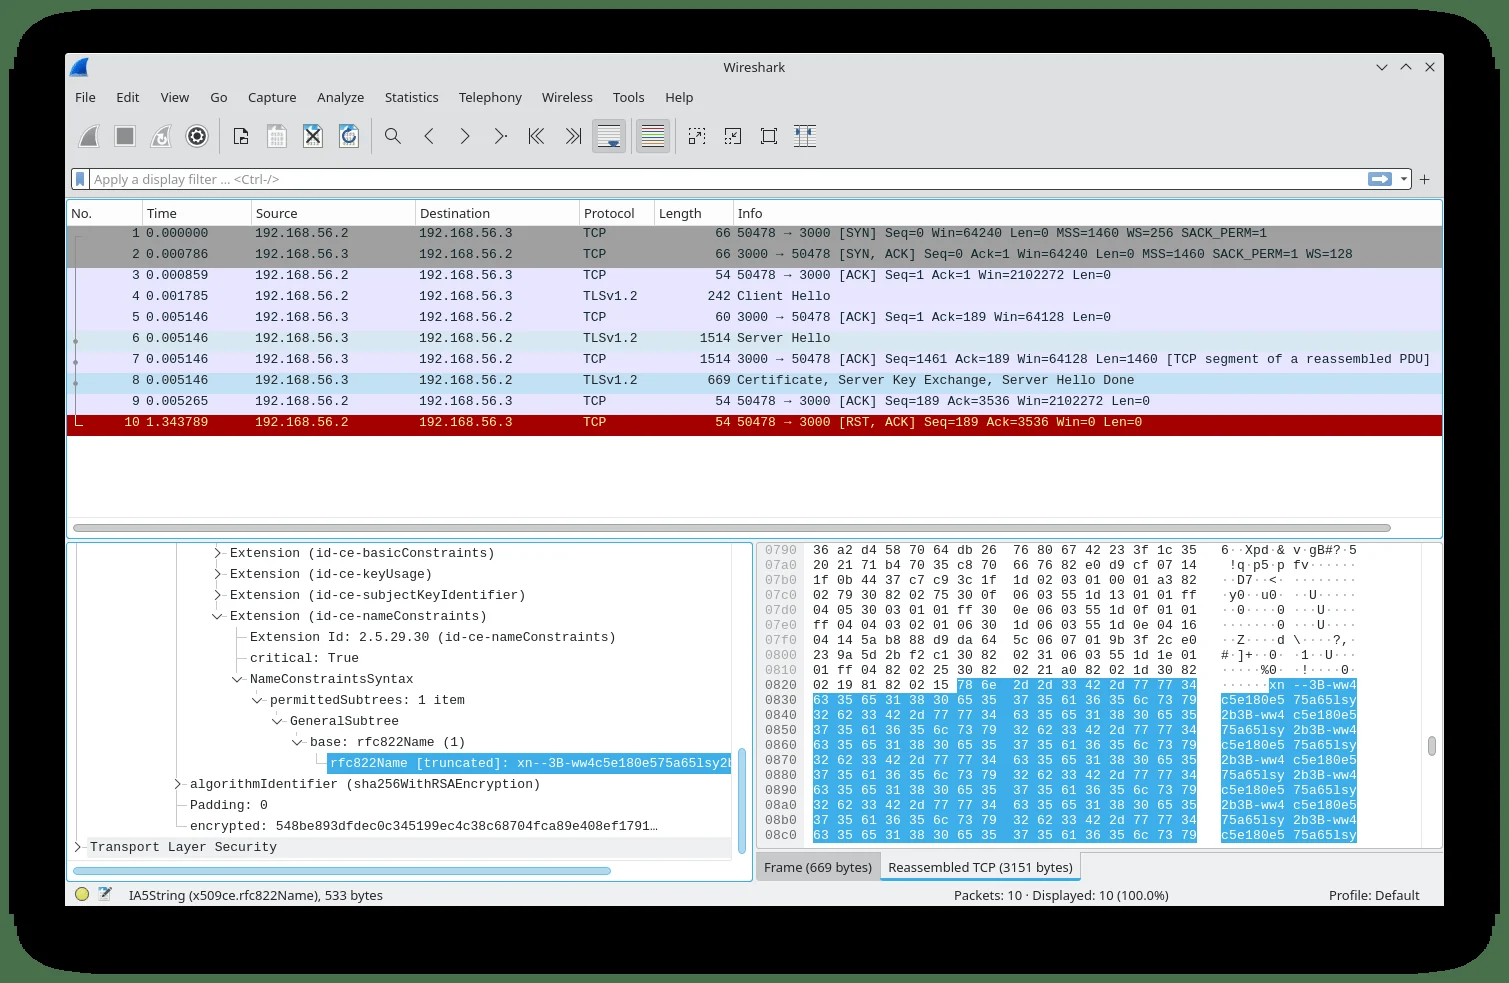
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…

PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…

Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…

Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…

Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…

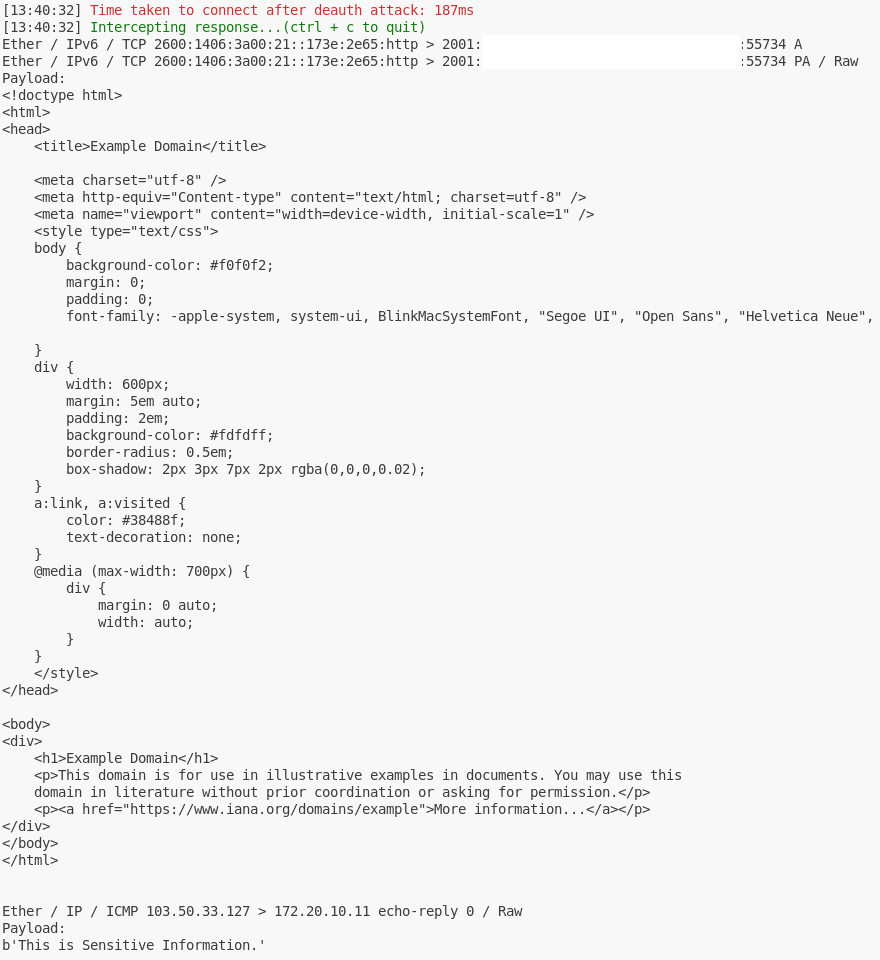
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…

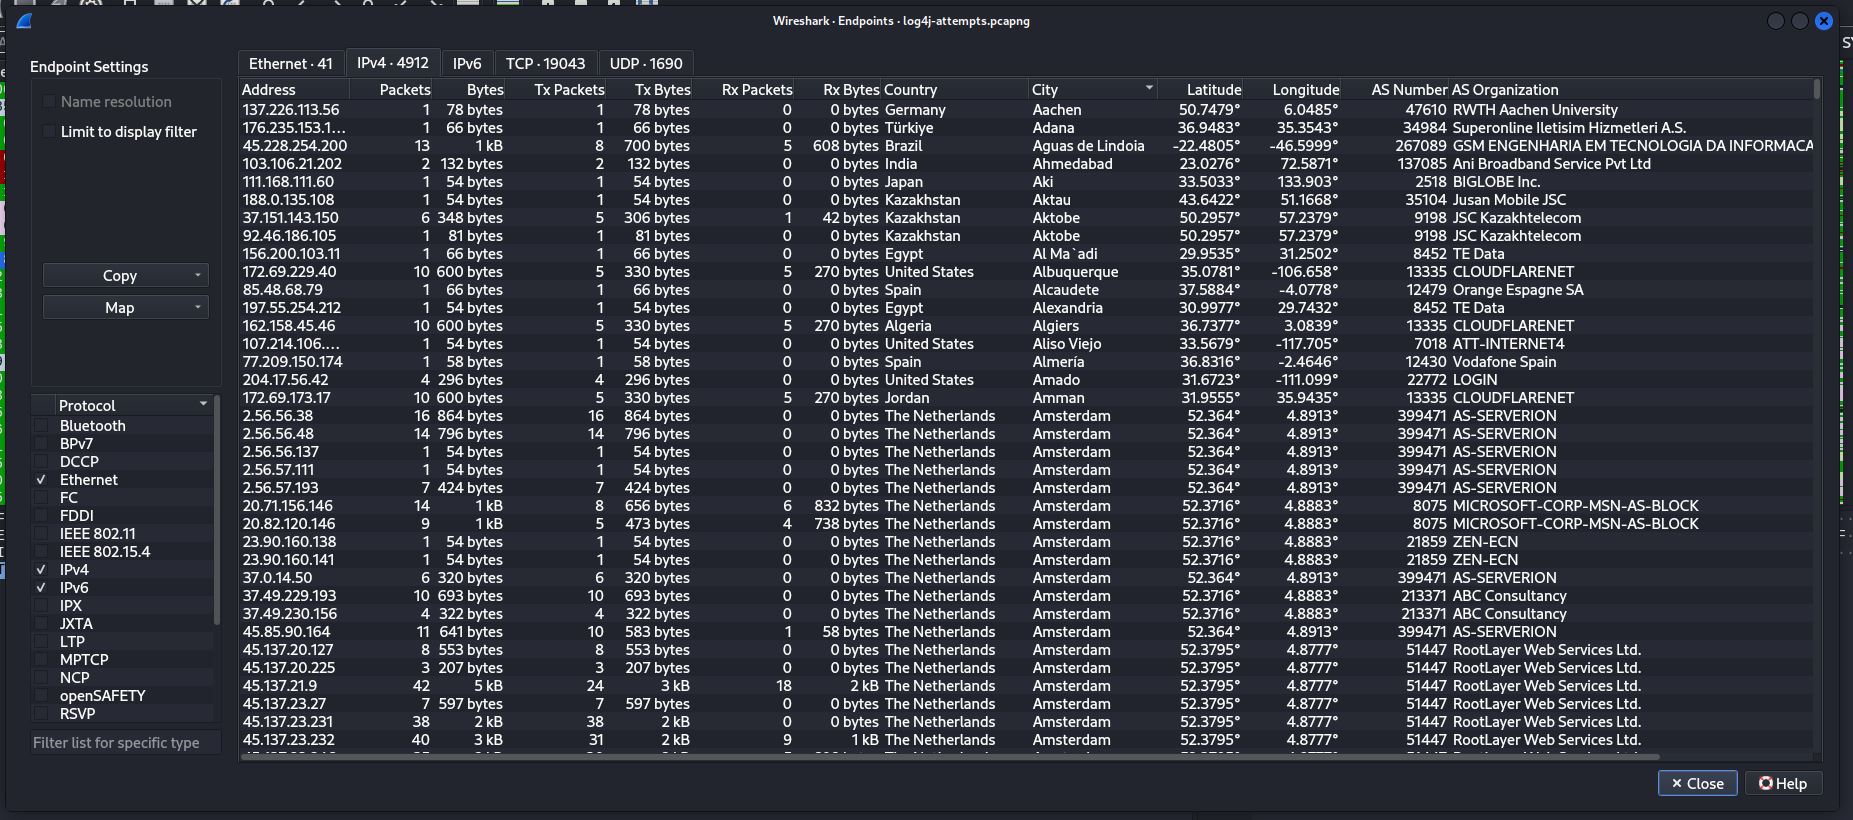
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

scripts associate with bourne shell EVN function parsing vulnerability CVE-2014-6271

Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…

This Python script helps to detect the Etherleak (CVE-2003-0001) vulnerability on a target host by analyzing the padding data in network packets. The…

AnySniff is a tool for monitoring TCP connections of processes like AnyDesk on Windows. It uses the CVE-2024-52940 vulnerability to track open…

Interactive demo of CVE-2022-45059 Varnish Cache request smuggling vulnerability. Includes Spring Boot web app, vulnerable proxy, automated victim…

Files and tools for CVE-2021-26258

Python-based exploit for CVE-2010-4669 using Scapy to send crafted packets for network vulnerability testing. Requires root and Python 2.

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…

A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)

Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11