

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
44.7k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64\arm64 and loong64.
 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 gvcoder09/nodpi4android
Android proxy app that circumvents Deep Packet Inspection censorship by fragmenting TLS ClientHello packets and rewriting the TLS version to restore…
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
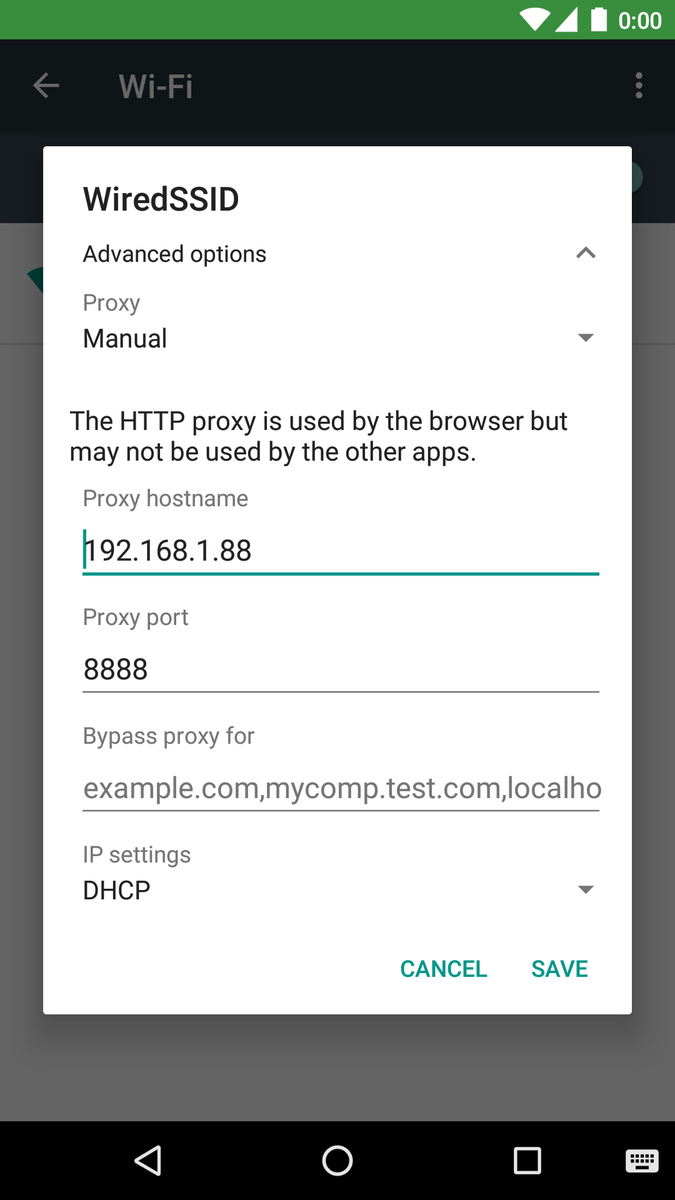 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
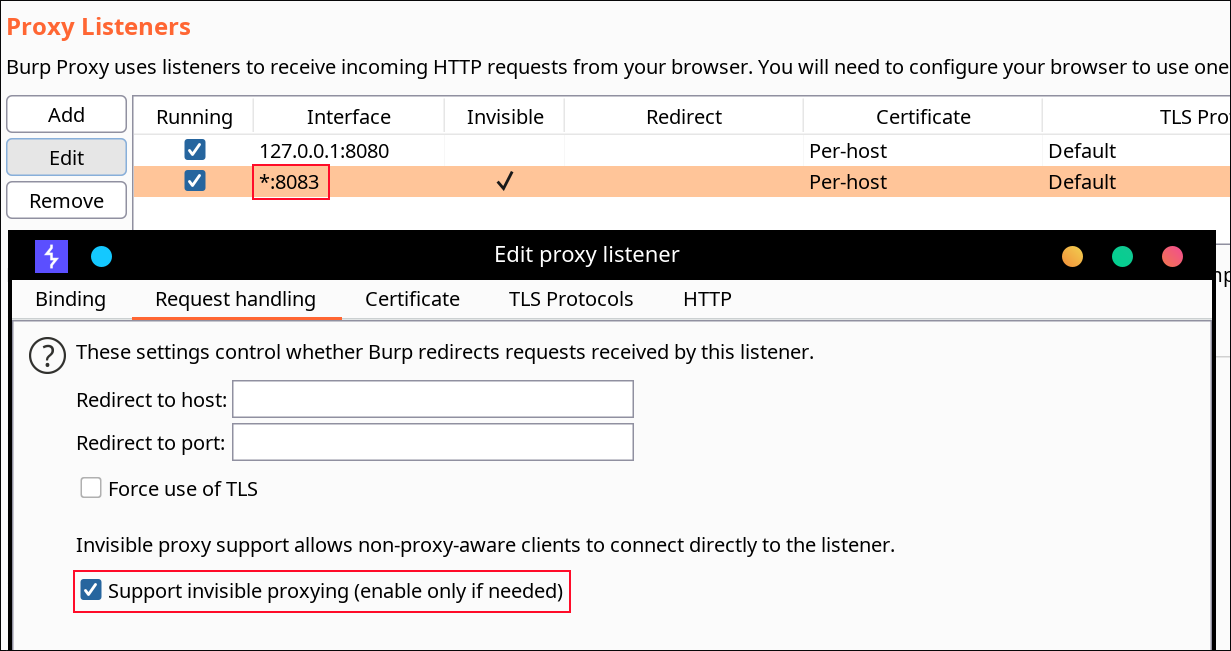 ptswarm/reflutter
Flutter Reverse Engineering Framework
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 s_r_e_e_r_a_j/netraptor
NetRaptor is a GUI-based ARP poisoning tool built with Python that allows you to scan a network, select a target and gateway, and perform a…
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 androguide/dsploit
dSploit - The most complete and advanced IT security professional toolkit on Android.