

mitmproxy
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
android-securityapi-securityapi-security-testing+12
45.1k
mitmproxy/mitmproxyAn interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 jean-nestor/evil-twin-ap
Automated evil twin access point toolkit with traffic capture and real-time monitoring for wireless penetration testing and security research.
 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
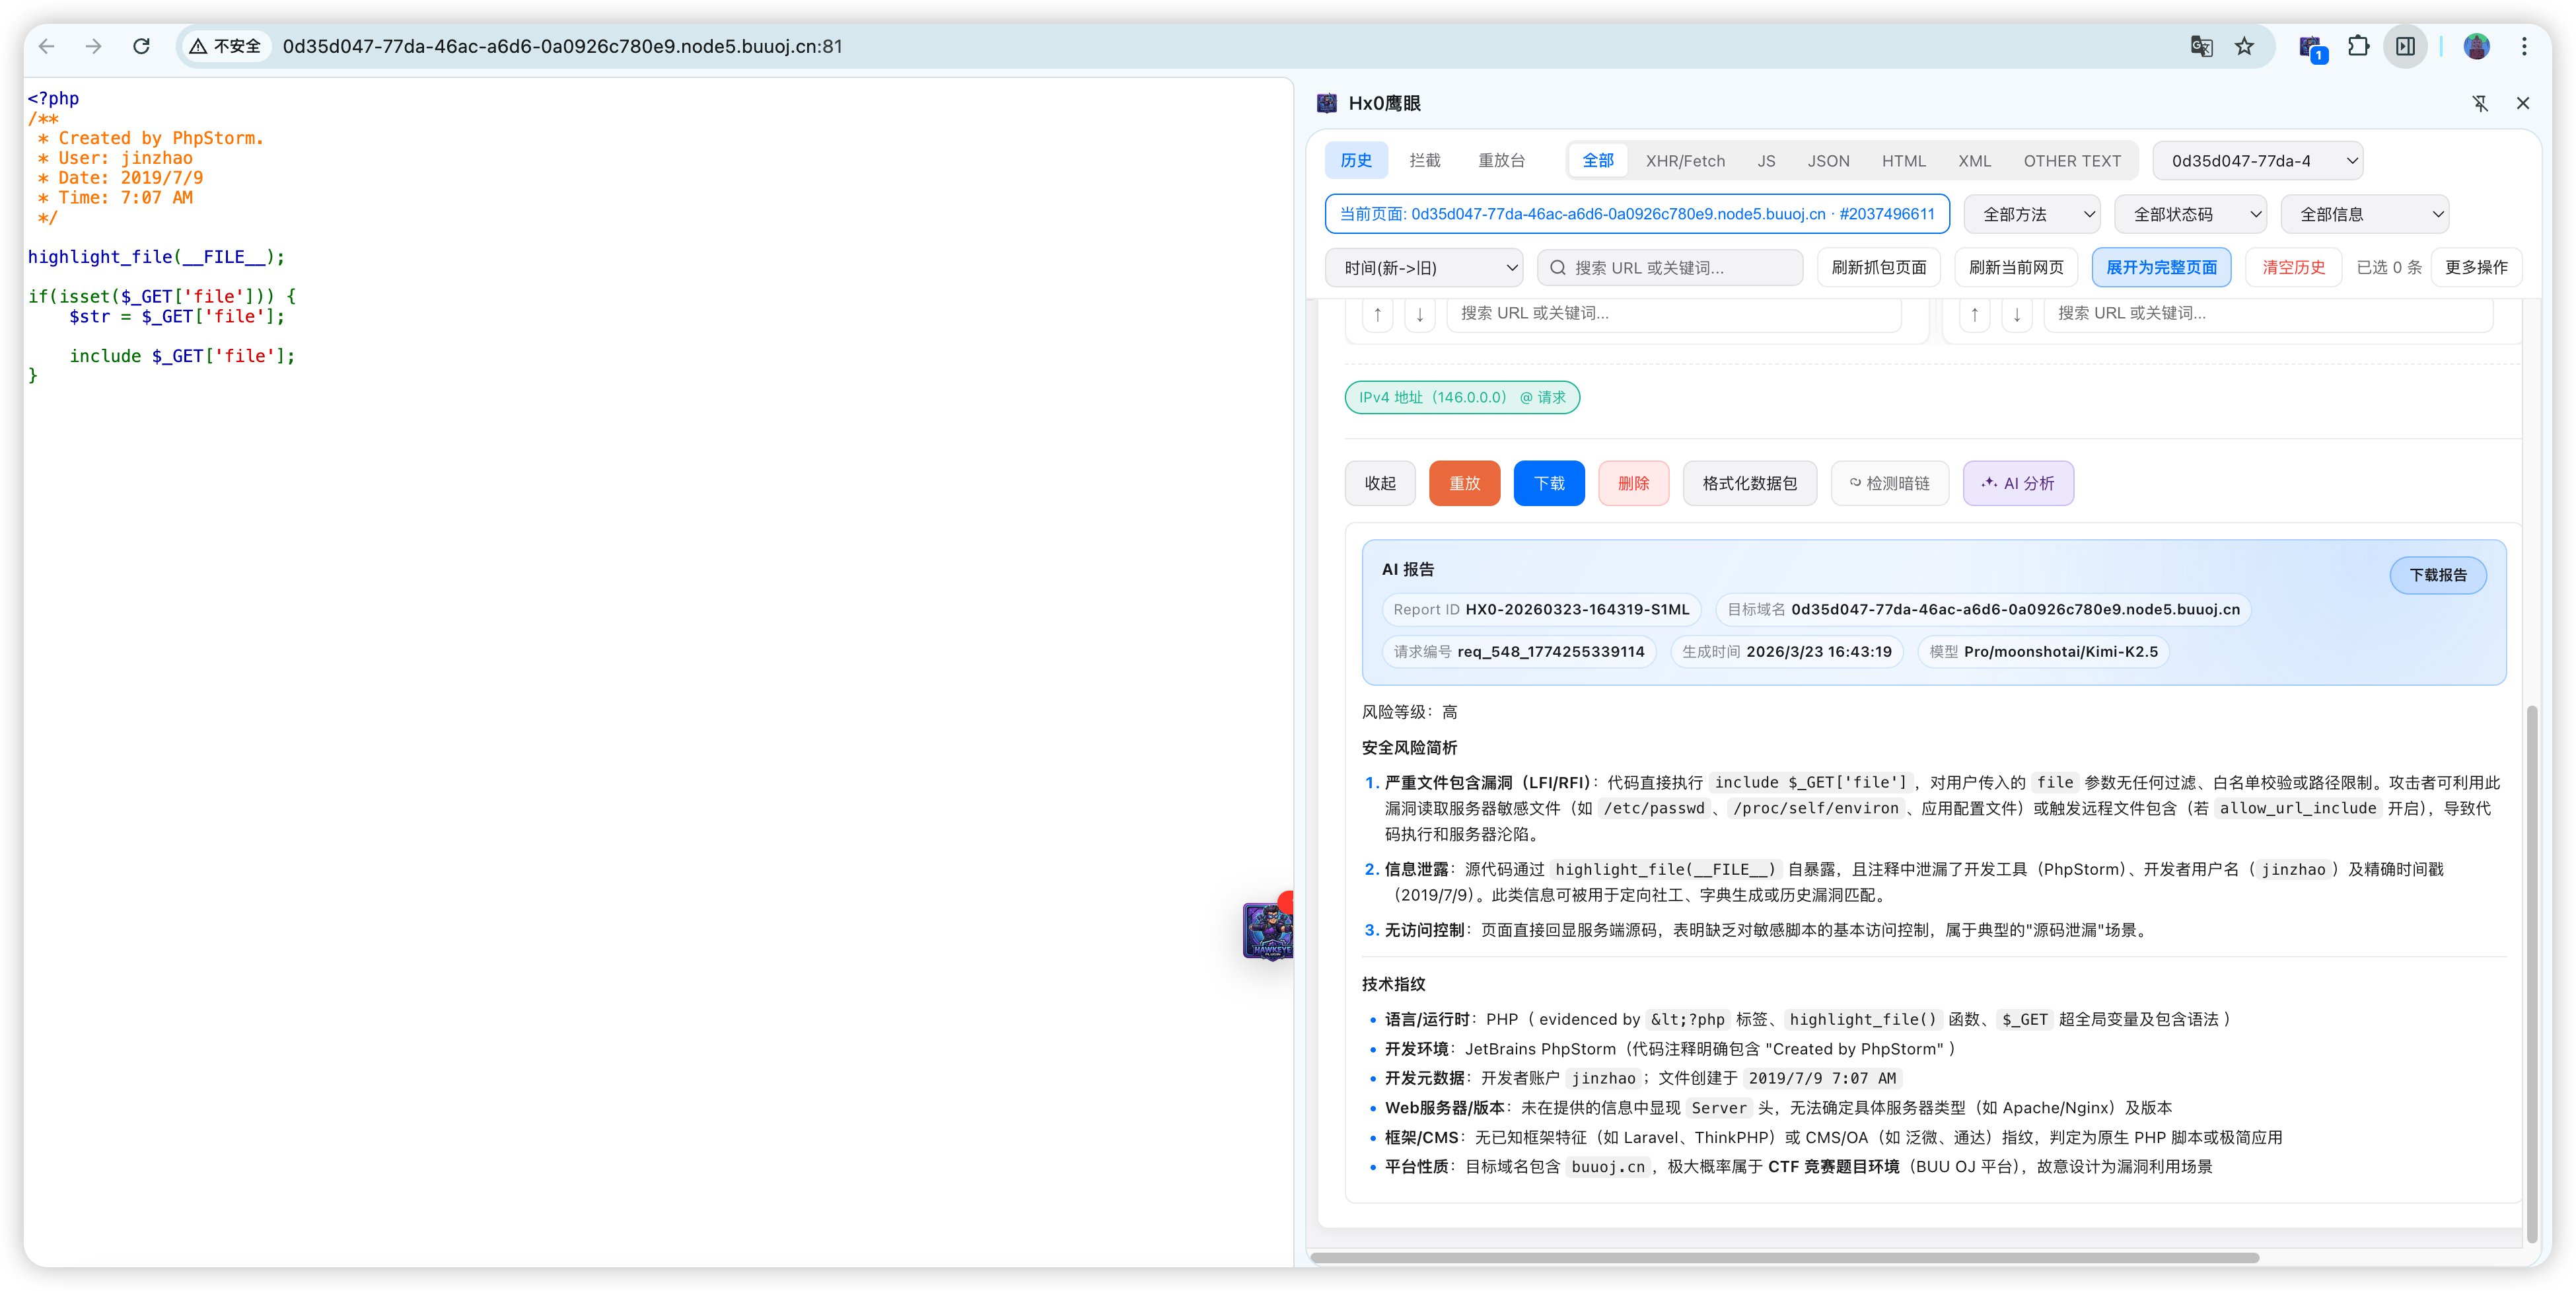 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 kdbugk/game-of-kingshot-re
Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 nytrorst/netripper
NetRipper - Smart traffic sniffing for penetration testers
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
 loukious/android_kernel_xiaomi_sm8150
Nethunter kernel for the POCO X3 Pro (vayu) based on crDroid's kernel.
 mandiant/flare-fakenet-ng
FakeNet-NG - Next Generation Dynamic Network Analysis Tool
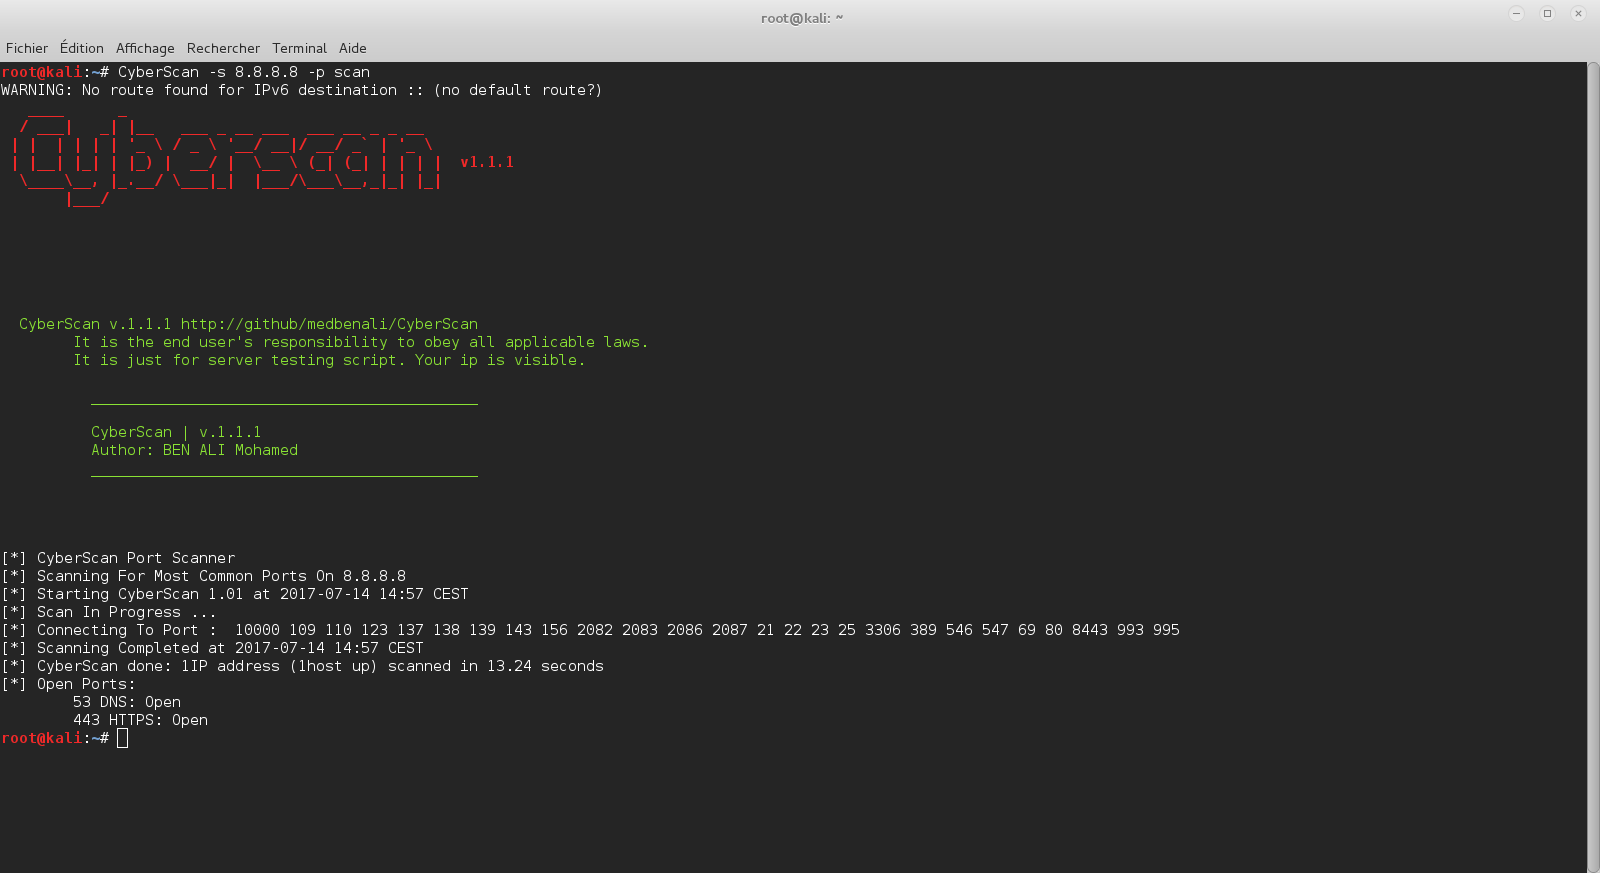 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
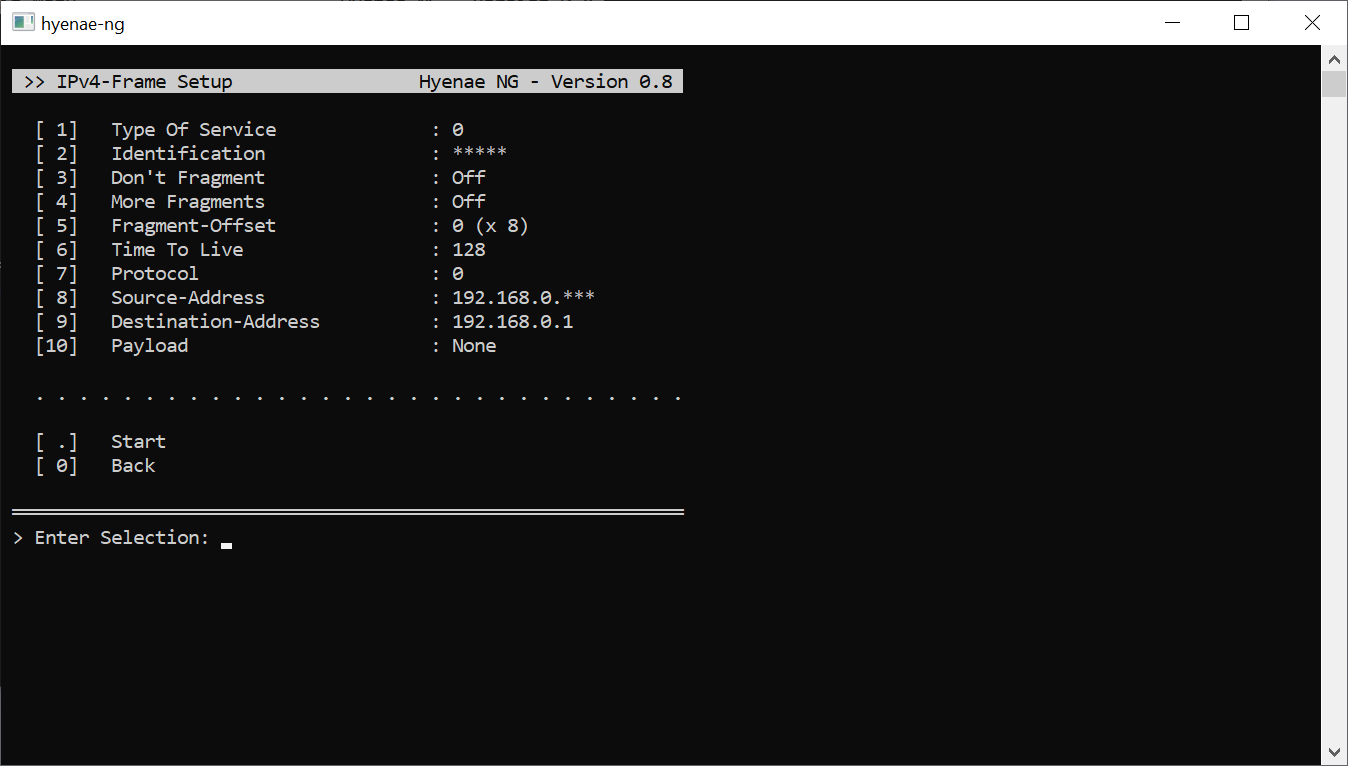 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
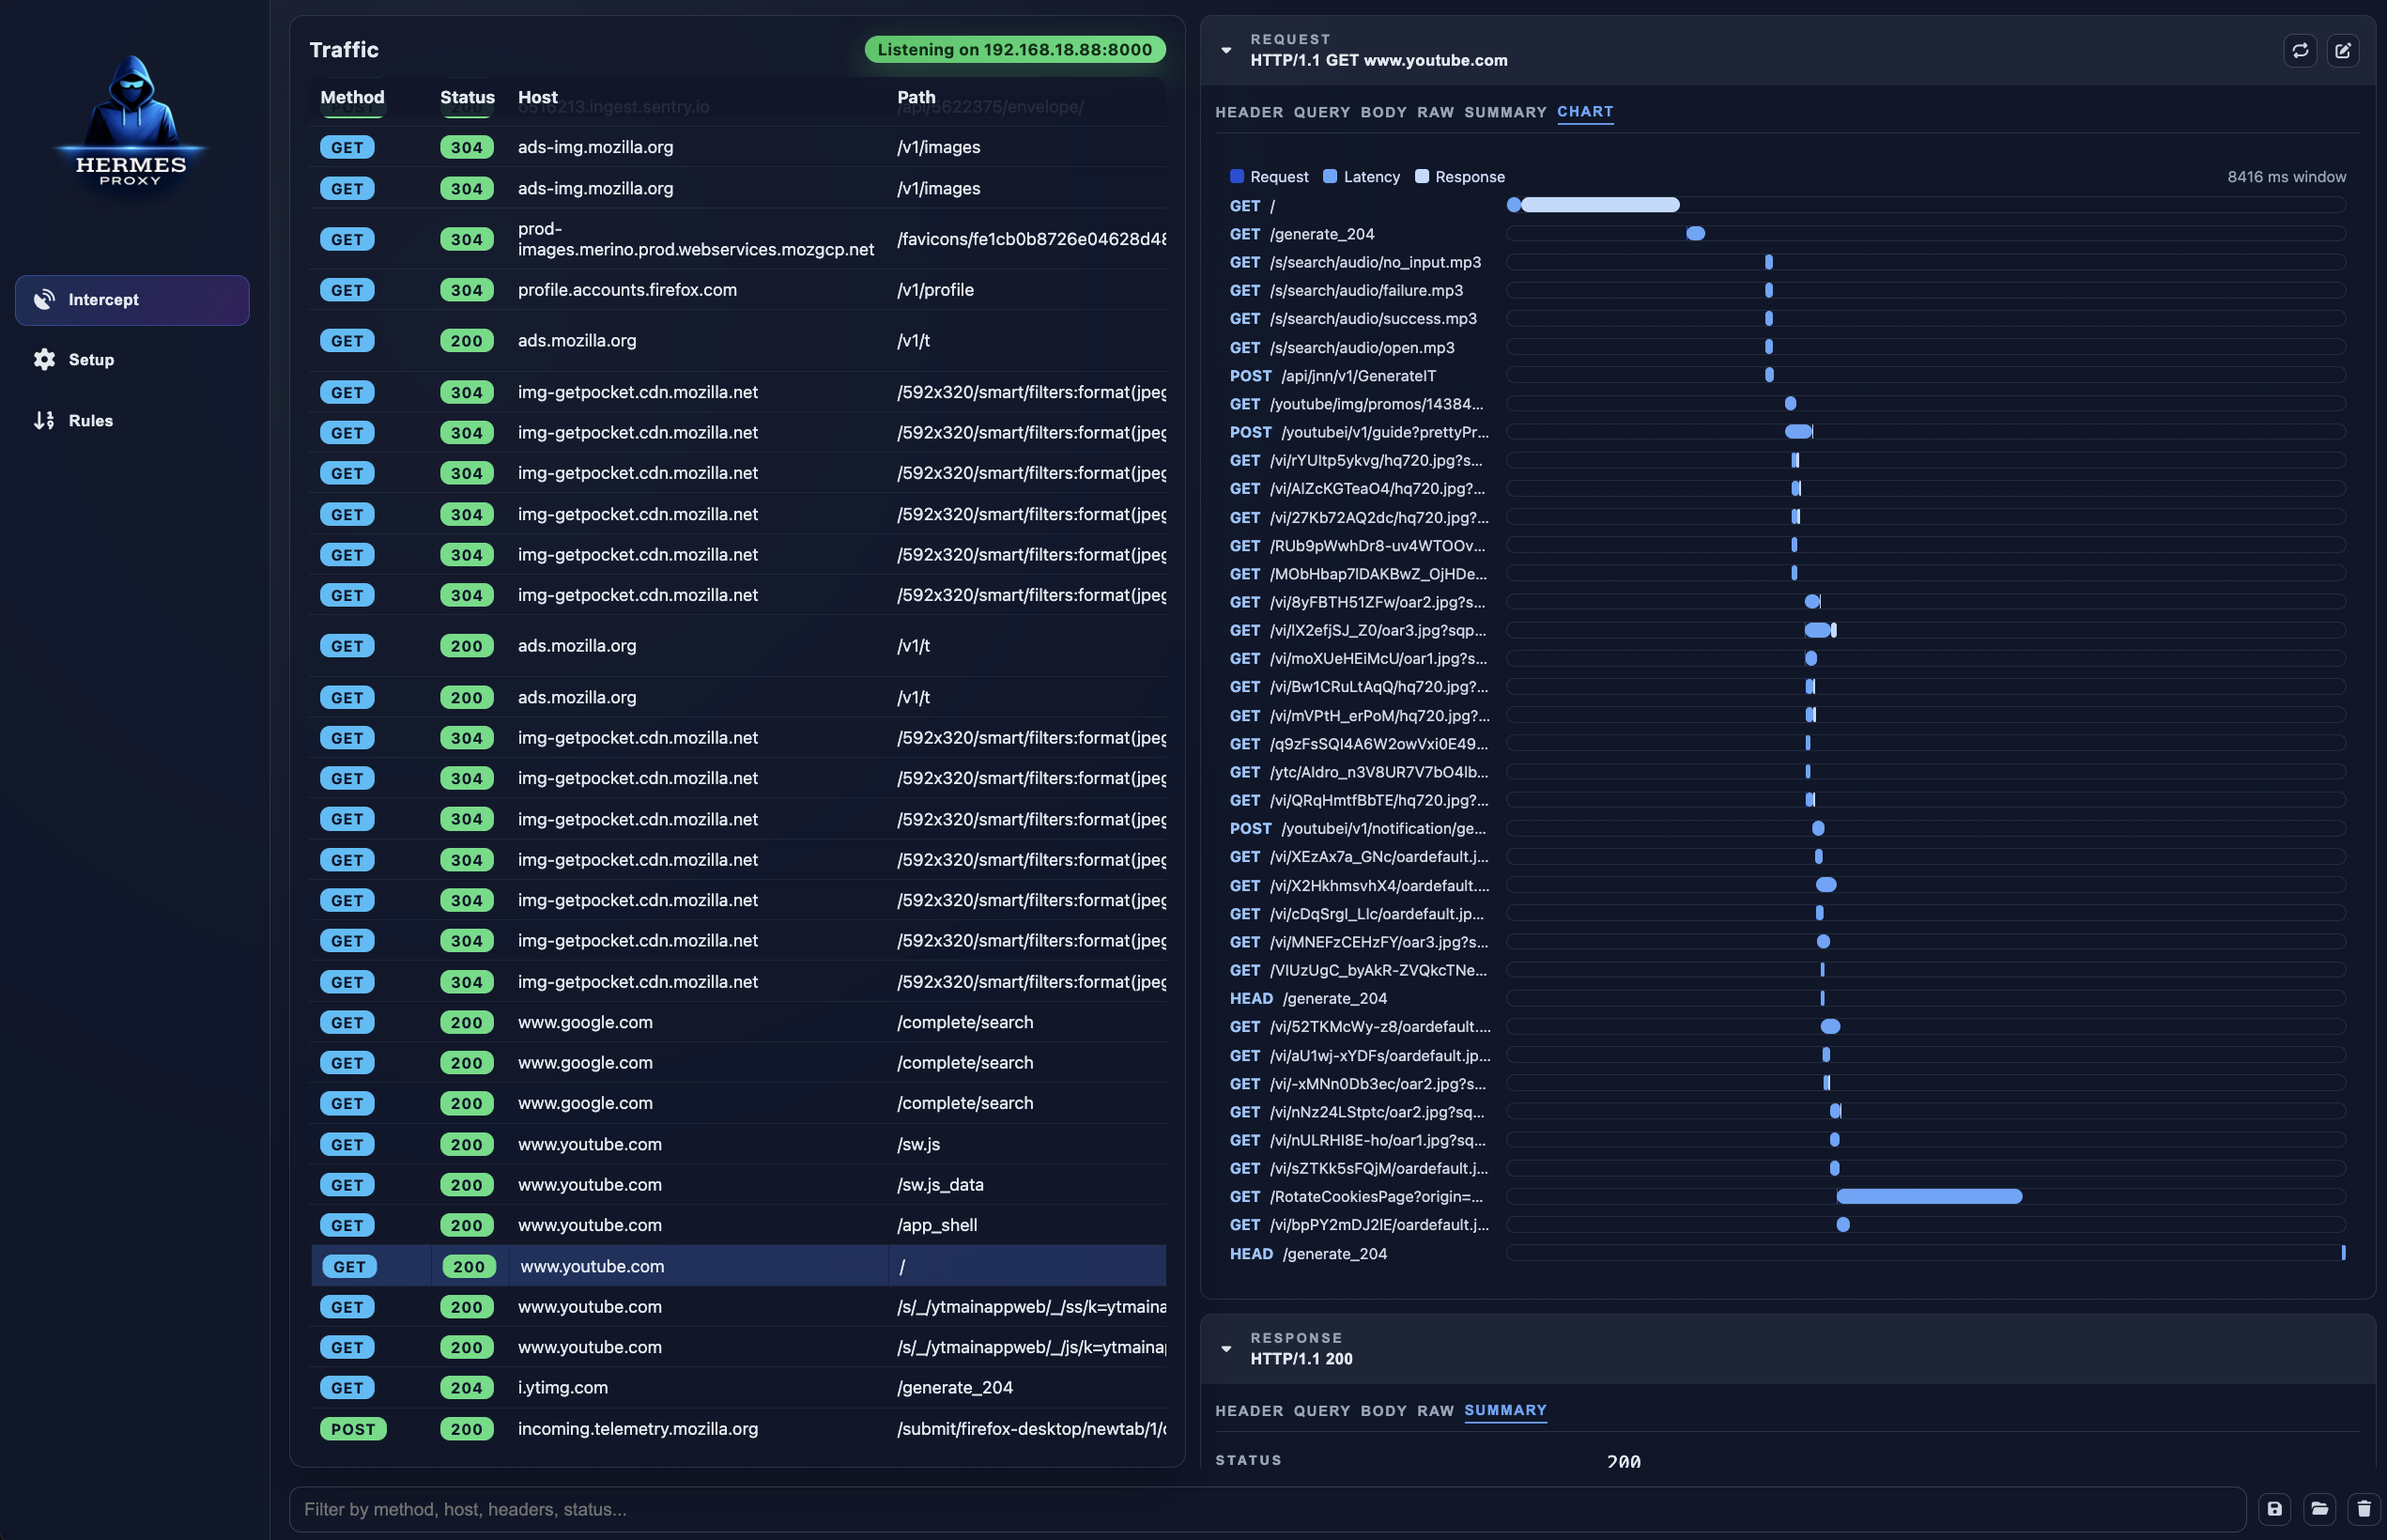 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer