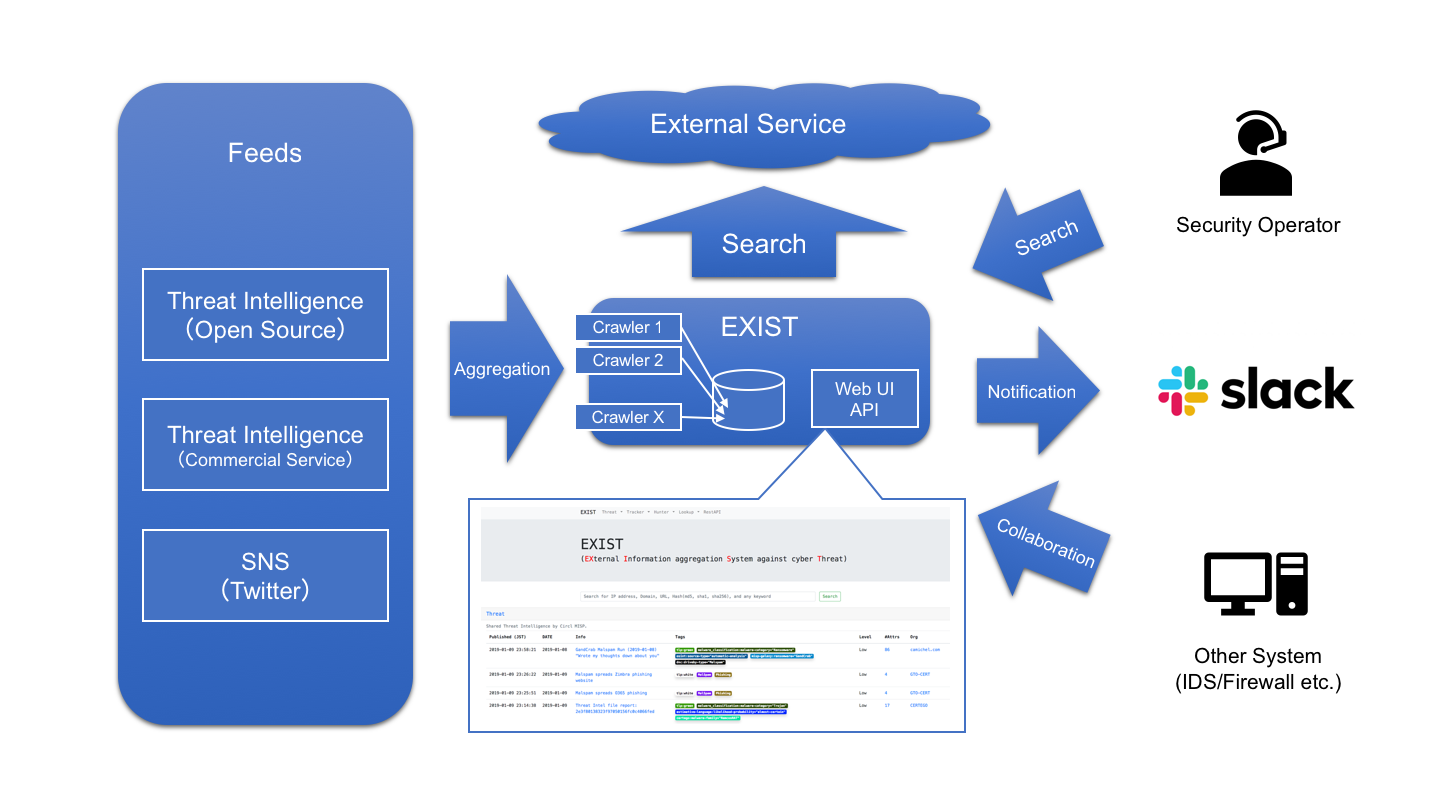
BlueBox
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
50
svdwi/blueboxOpen-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
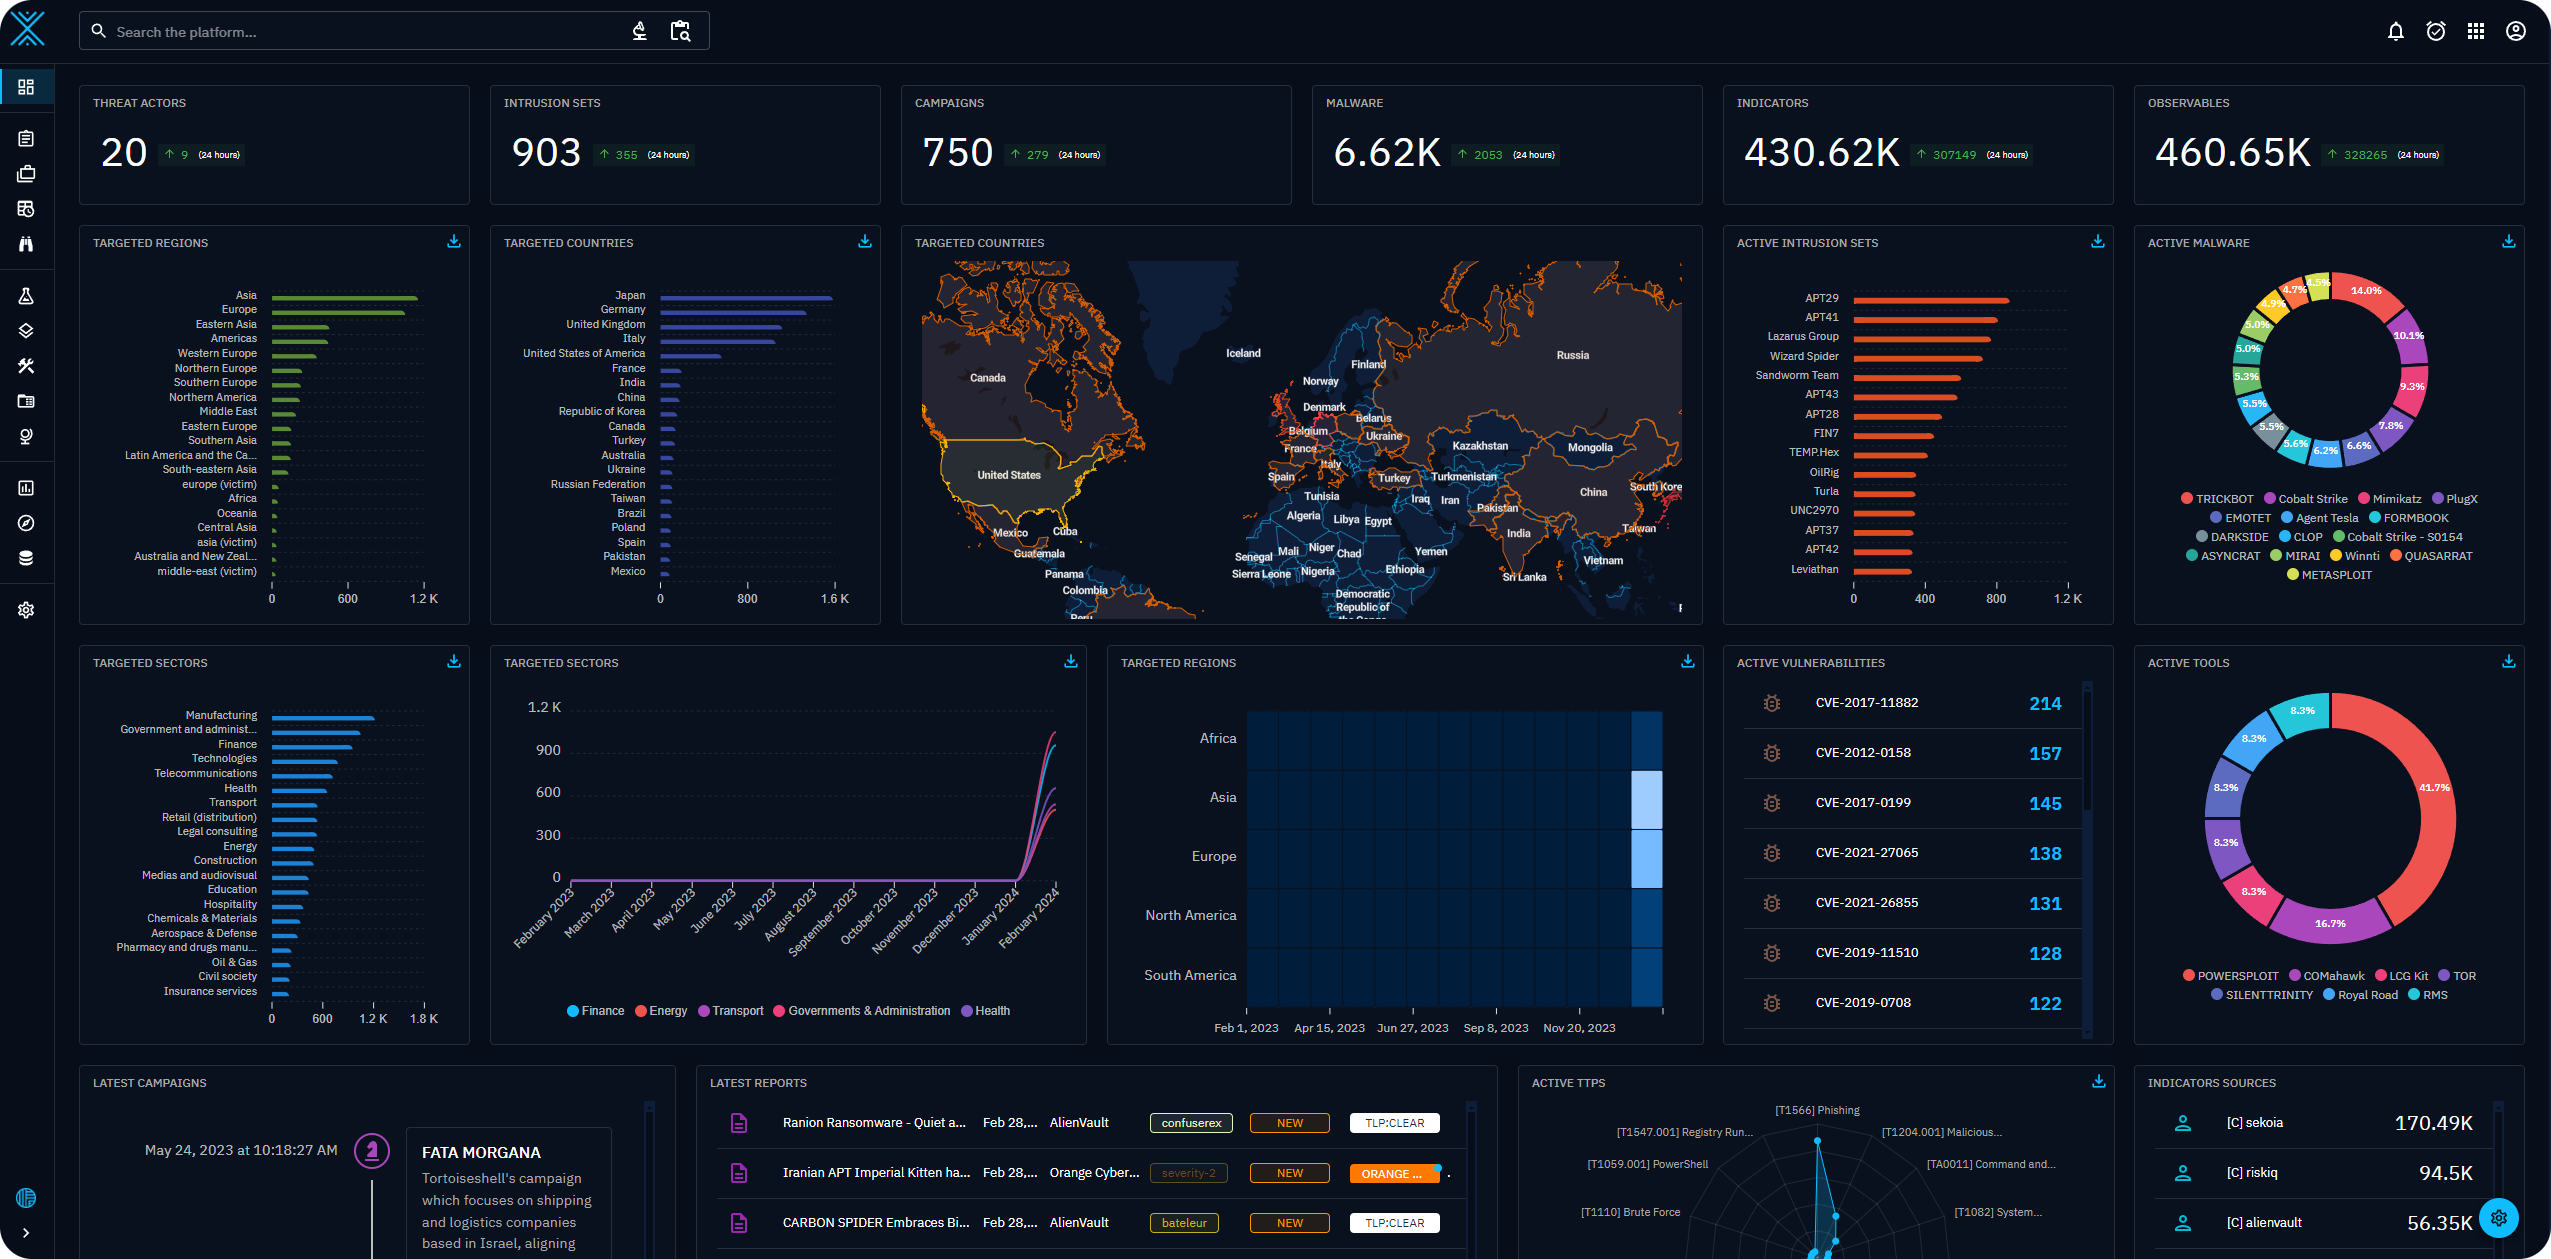 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 dev-lu/osint_toolkit
Open source platform for cyber security analysts with many features for threat intelligence and detection engineering.
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
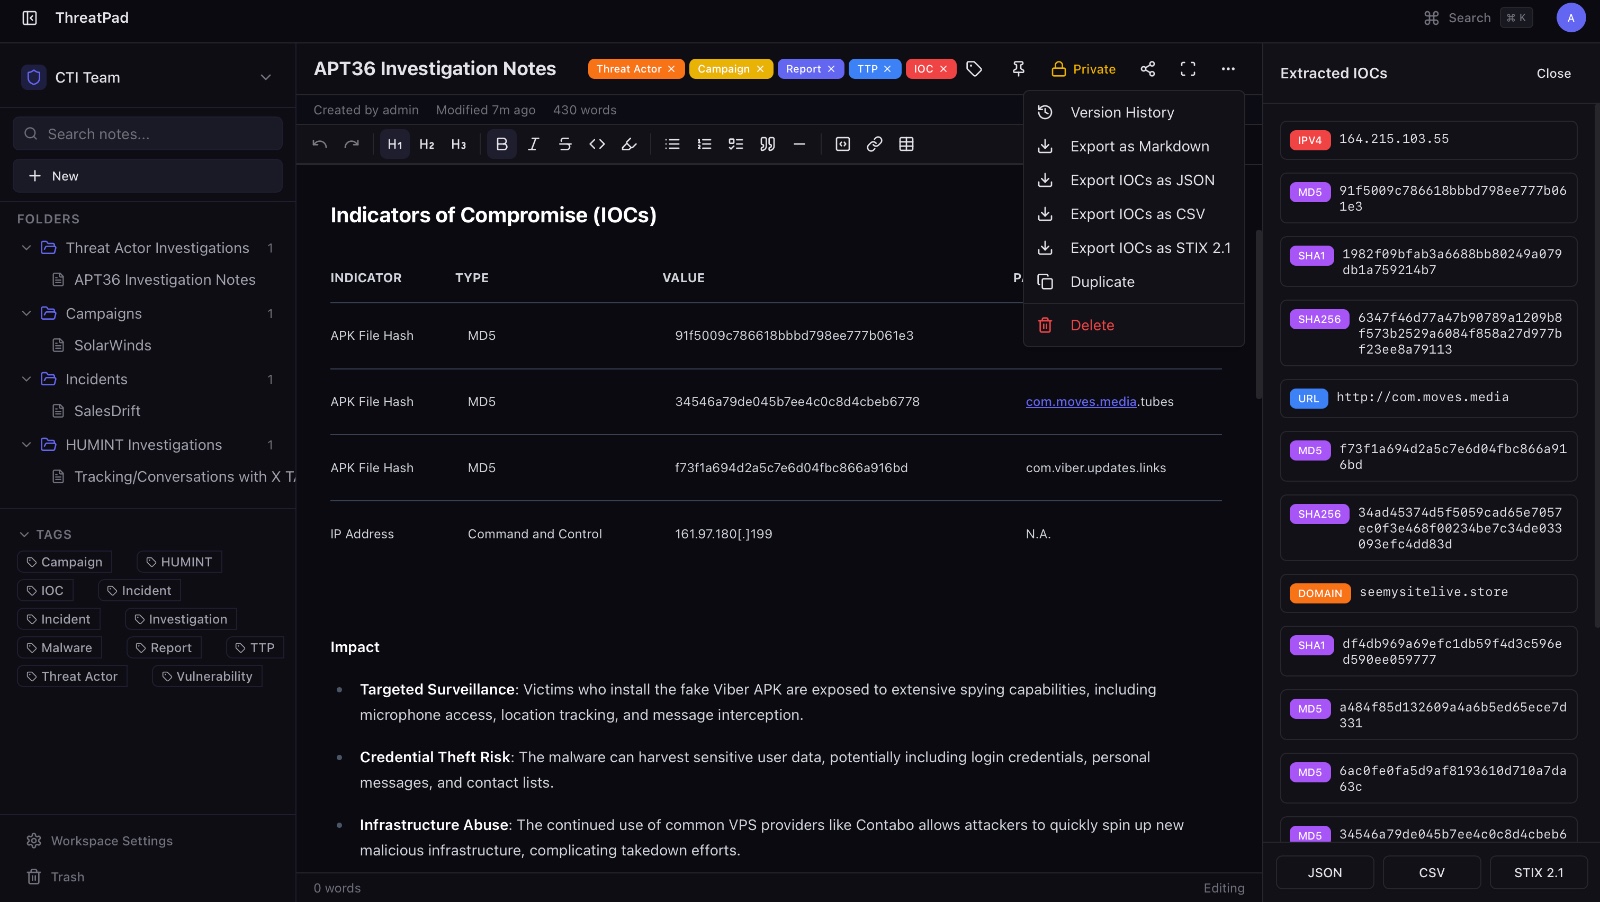 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
 00gxd14g/misp-extractor
Extracts selected MISP attributes, including IP addresses, URLs, and hashes, into reusable output files.

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
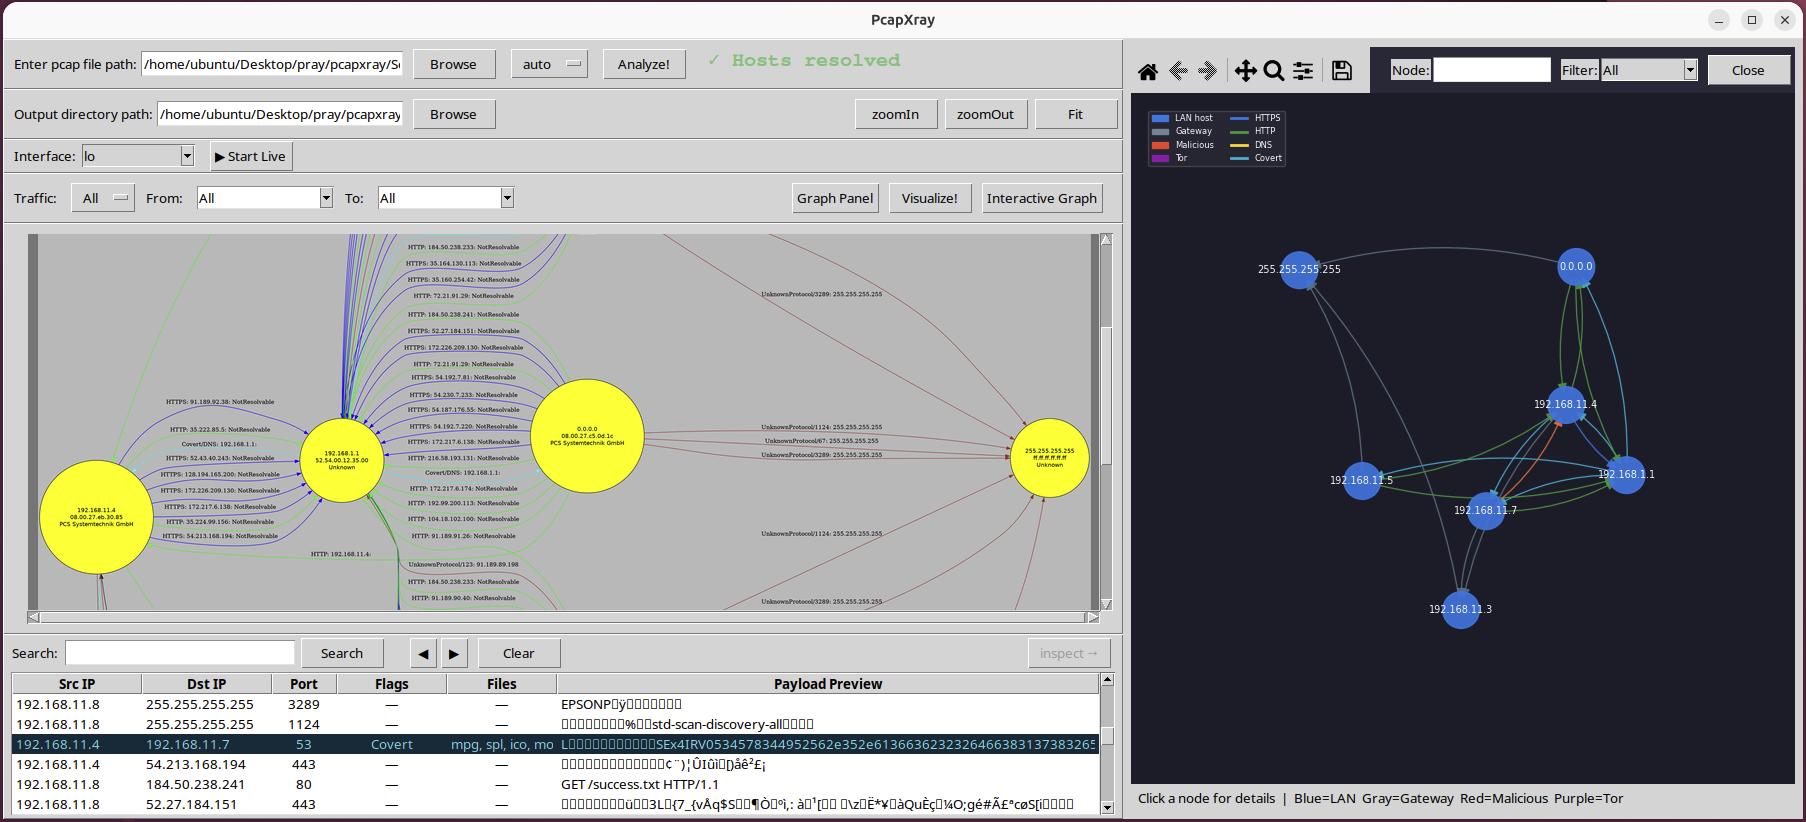 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
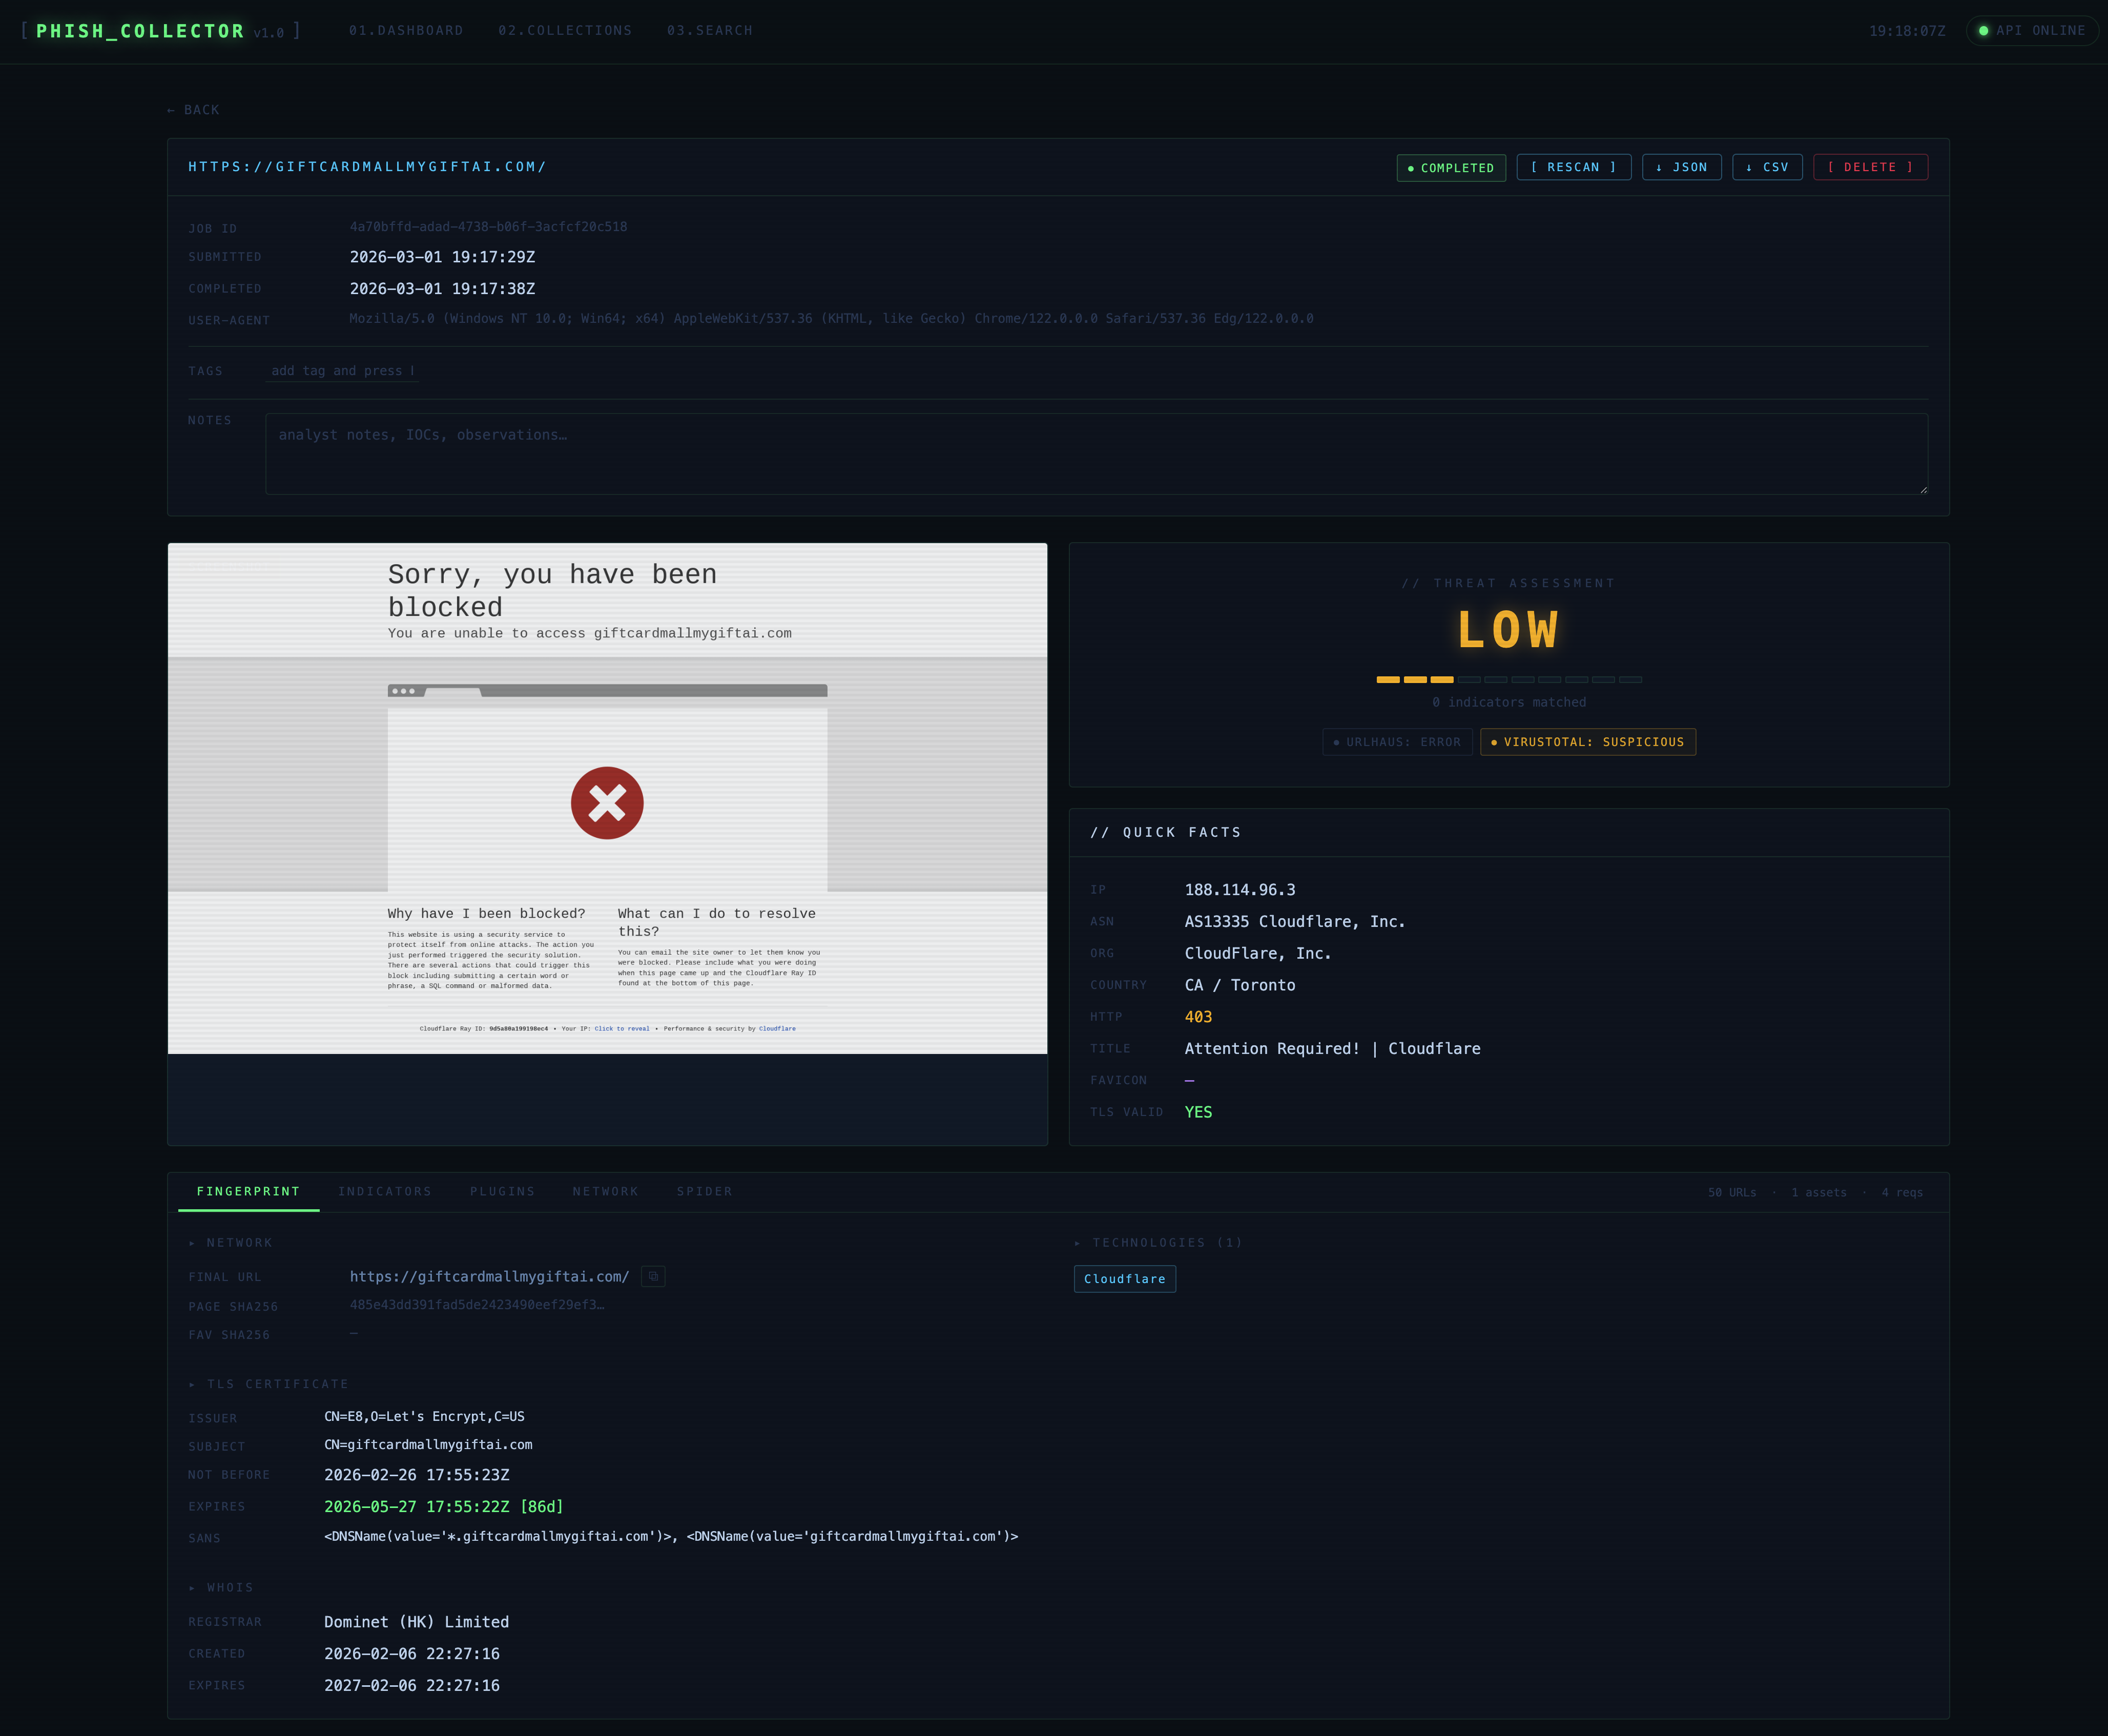 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 enriquenegri-cyberlaw/boa-cve-2009-4496-analysis
Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…