
CVE-2021-45901
 9lyph/cve-2021-45901
Proof-of-concept Python script that enumerates valid ServiceNow user accounts by exploiting the password-reset response discrepancy in CVE-2021-45901.
exploitationinformation-gatheringosint+3
2
9lyph/cve-2021-45901Proof-of-concept Python script that enumerates valid ServiceNow user accounts by exploiting the password-reset response discrepancy in CVE-2021-45901.
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.
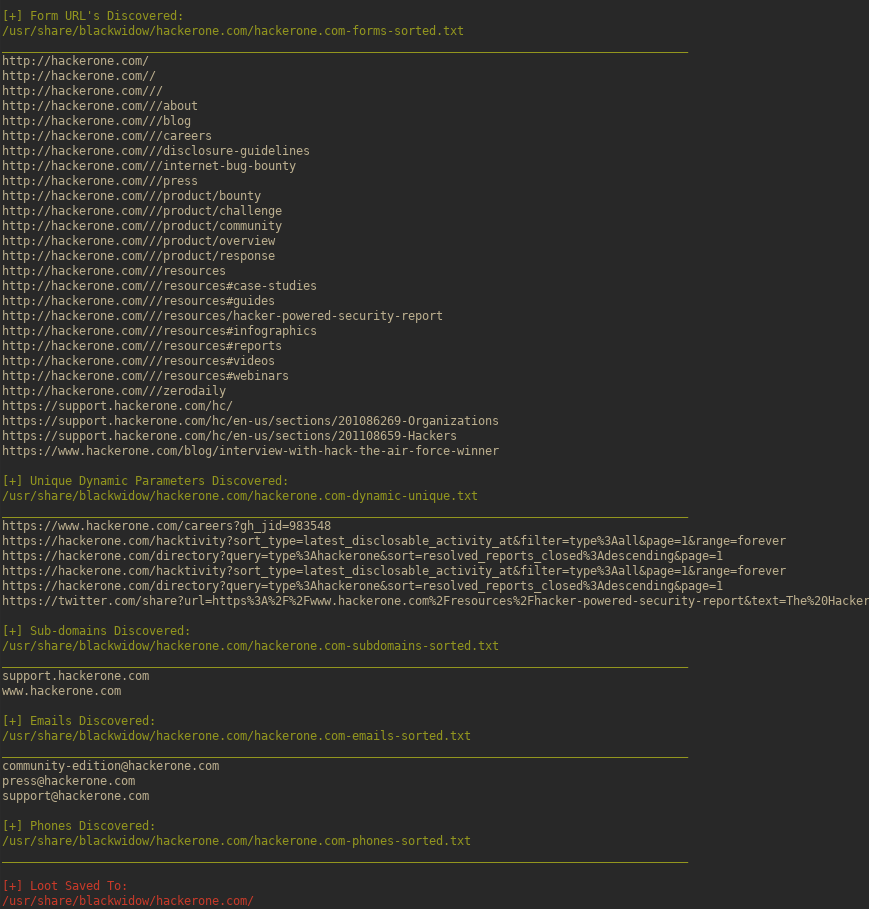 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
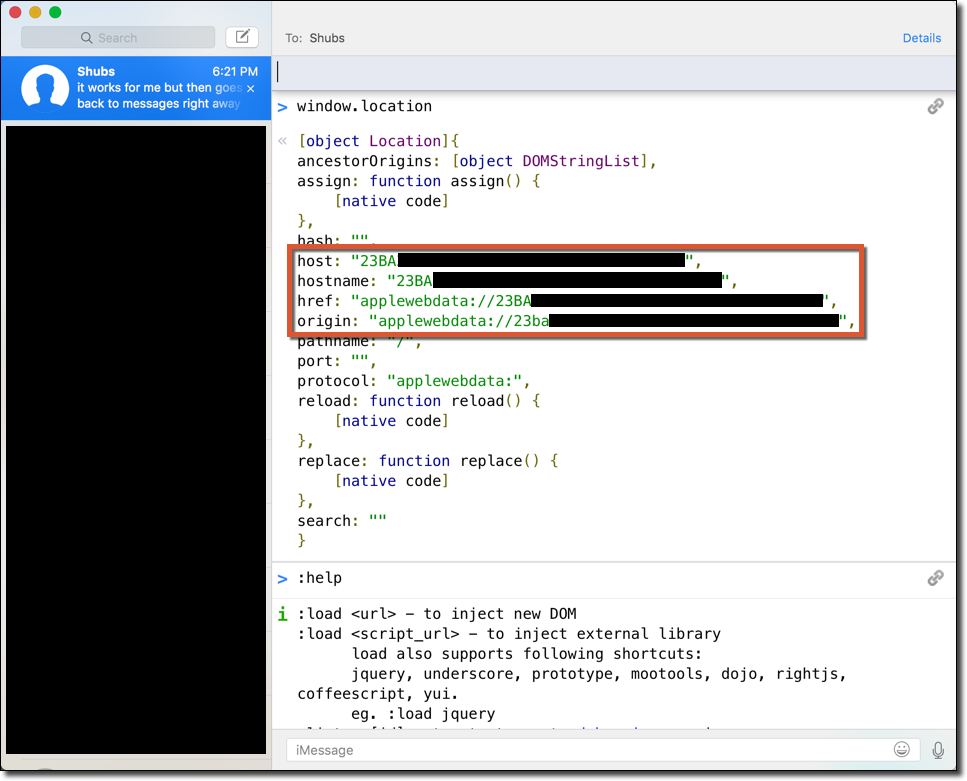 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS