
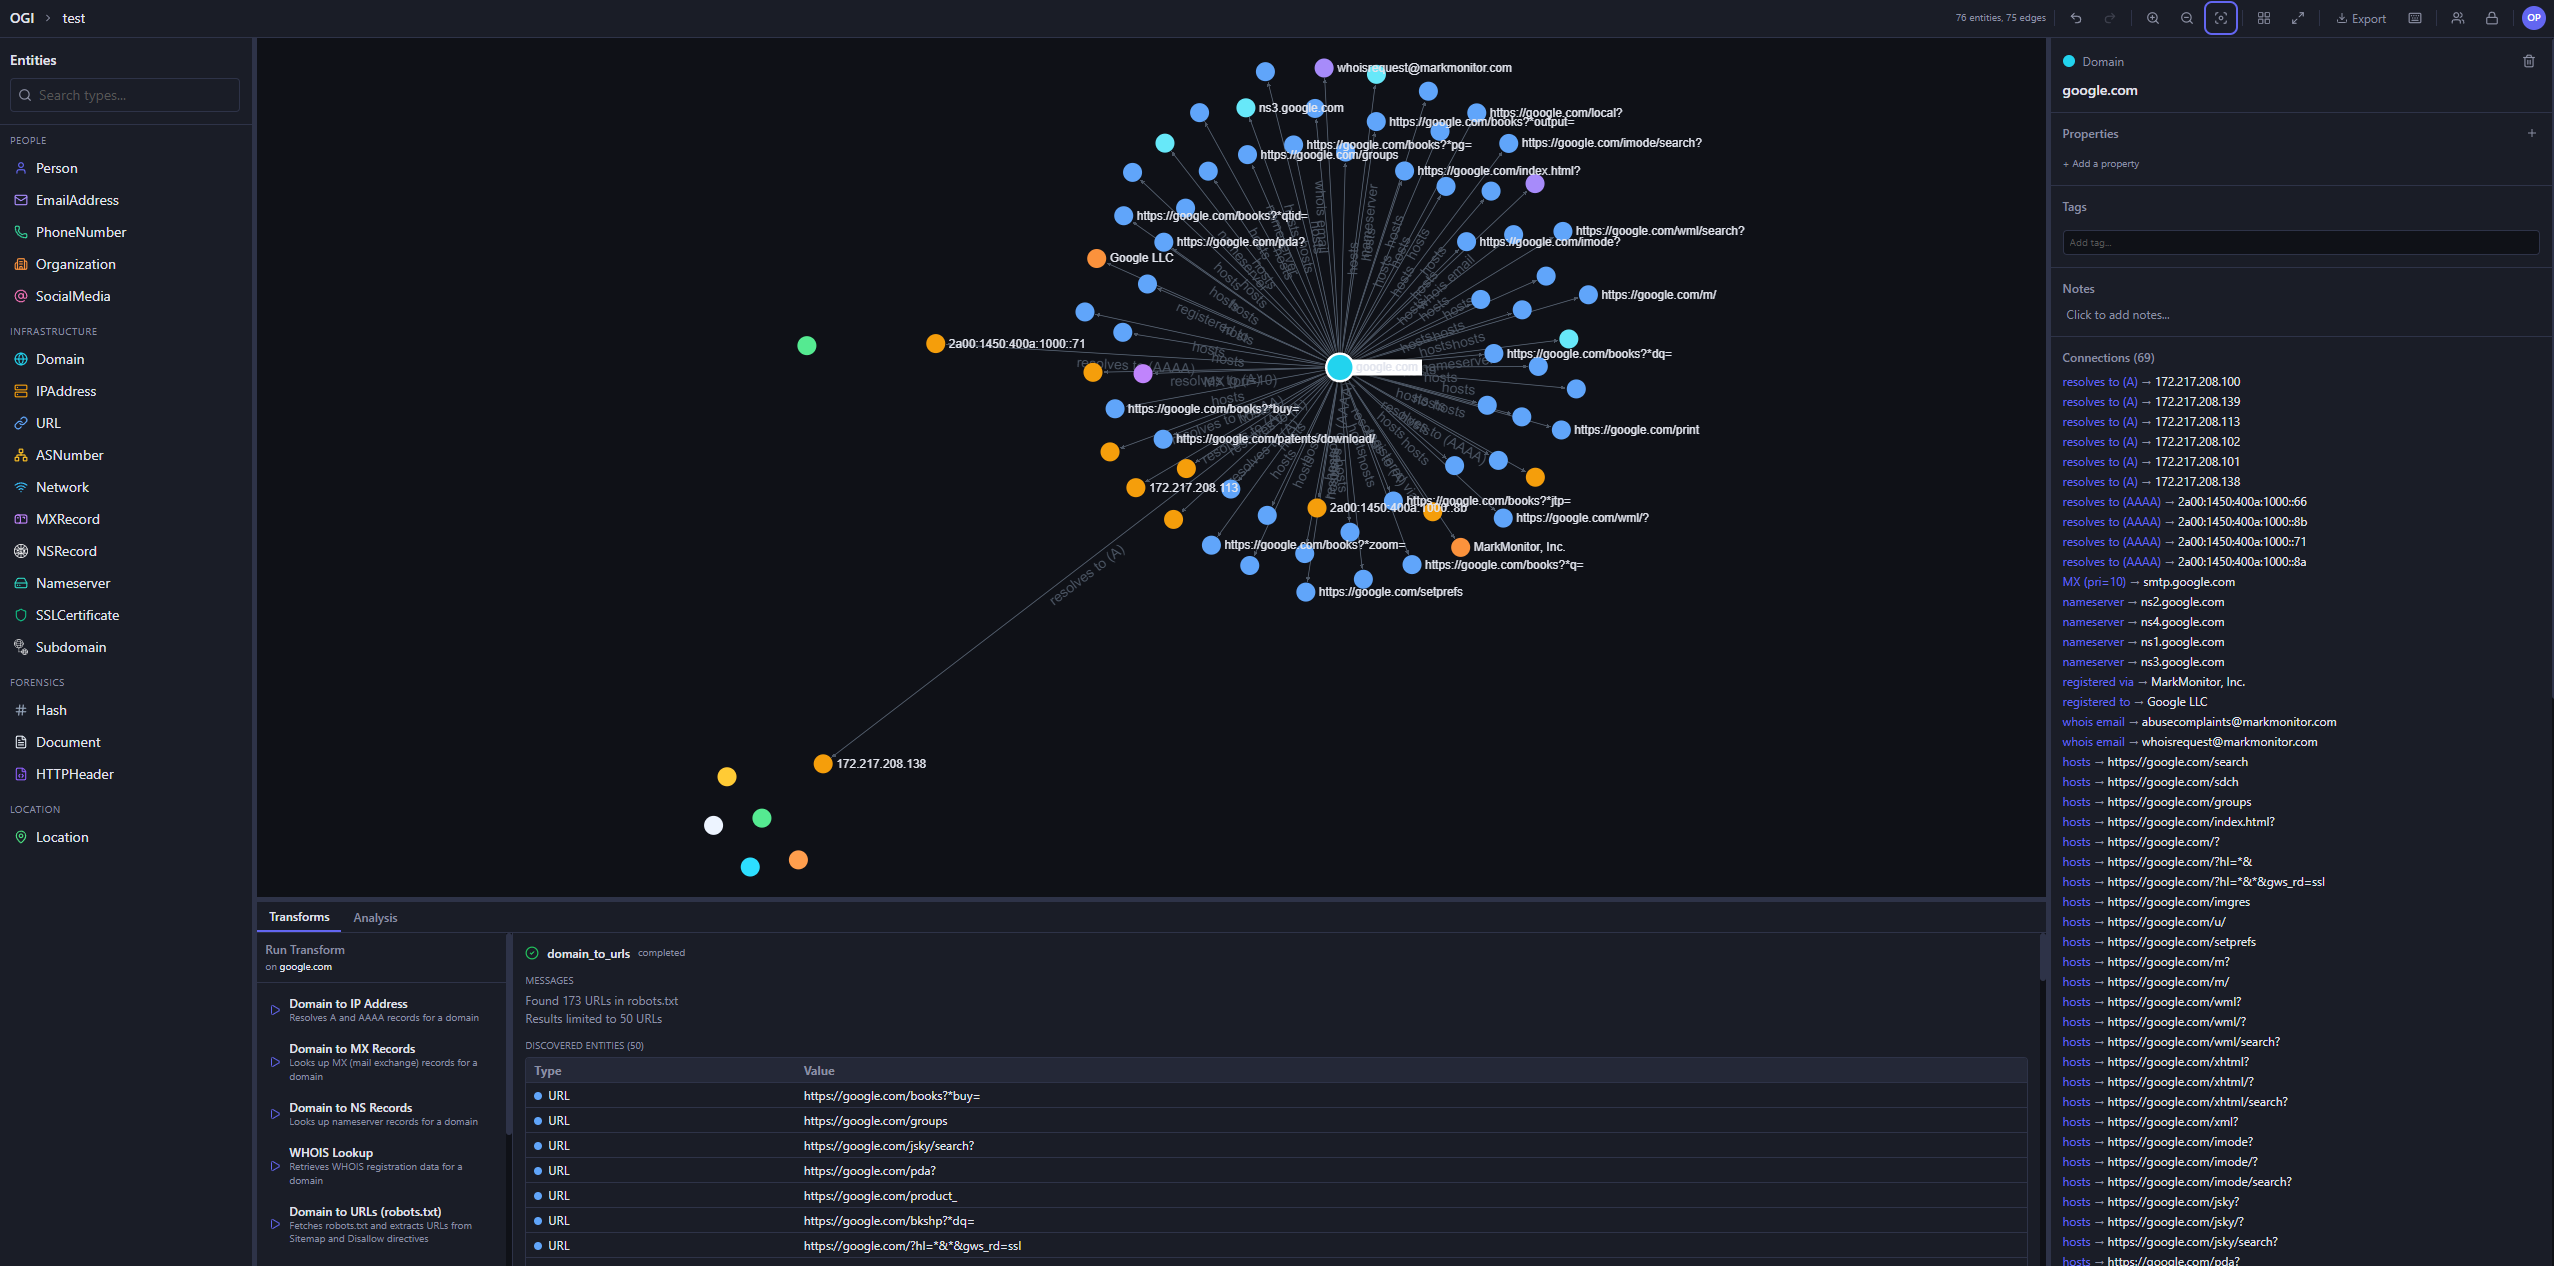
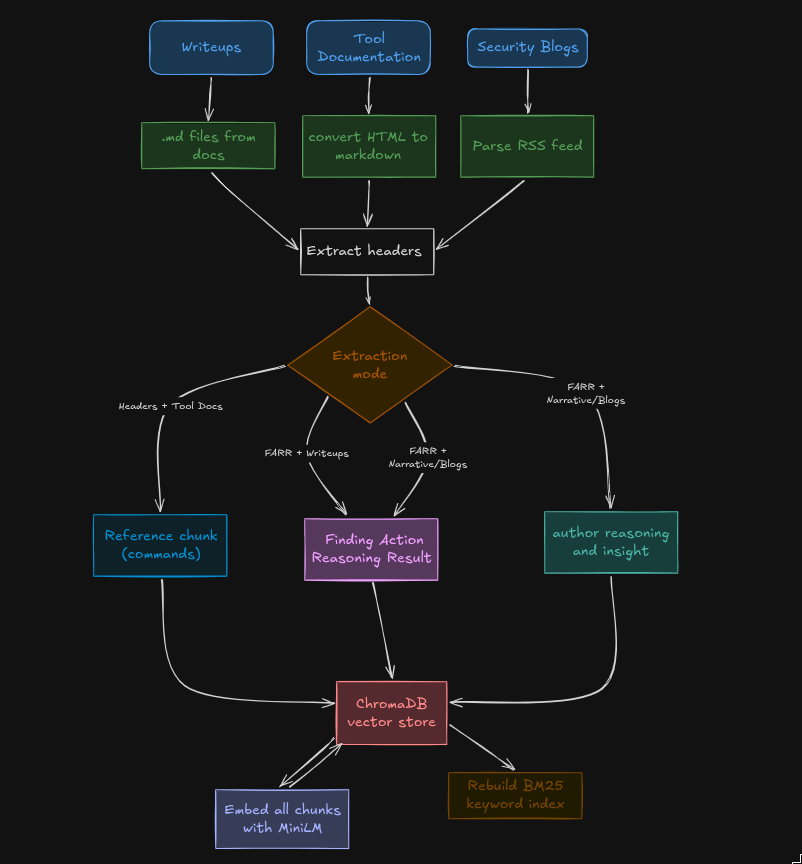
 chaelsoo/zetsu
A personal RAG system for offensive security knowledge
 ibrahimbalic/androidrat
Android RAT
 downunderctf/challenges_2022_public
Files + Writeups for DownUnderCTF 2022 Challenges
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 quantika14/osint-suite-tools
Repositorio del conjunto de herramientas para hacer OSINT y SOCMINT con Dante's Gates Minimal Version.
 micro-joan/d4ta-hunter
Automated OSINT framework for ethical hacking audits. Collects employee emails, password hashes, subdomains, and IPs via BreachDirectory and…
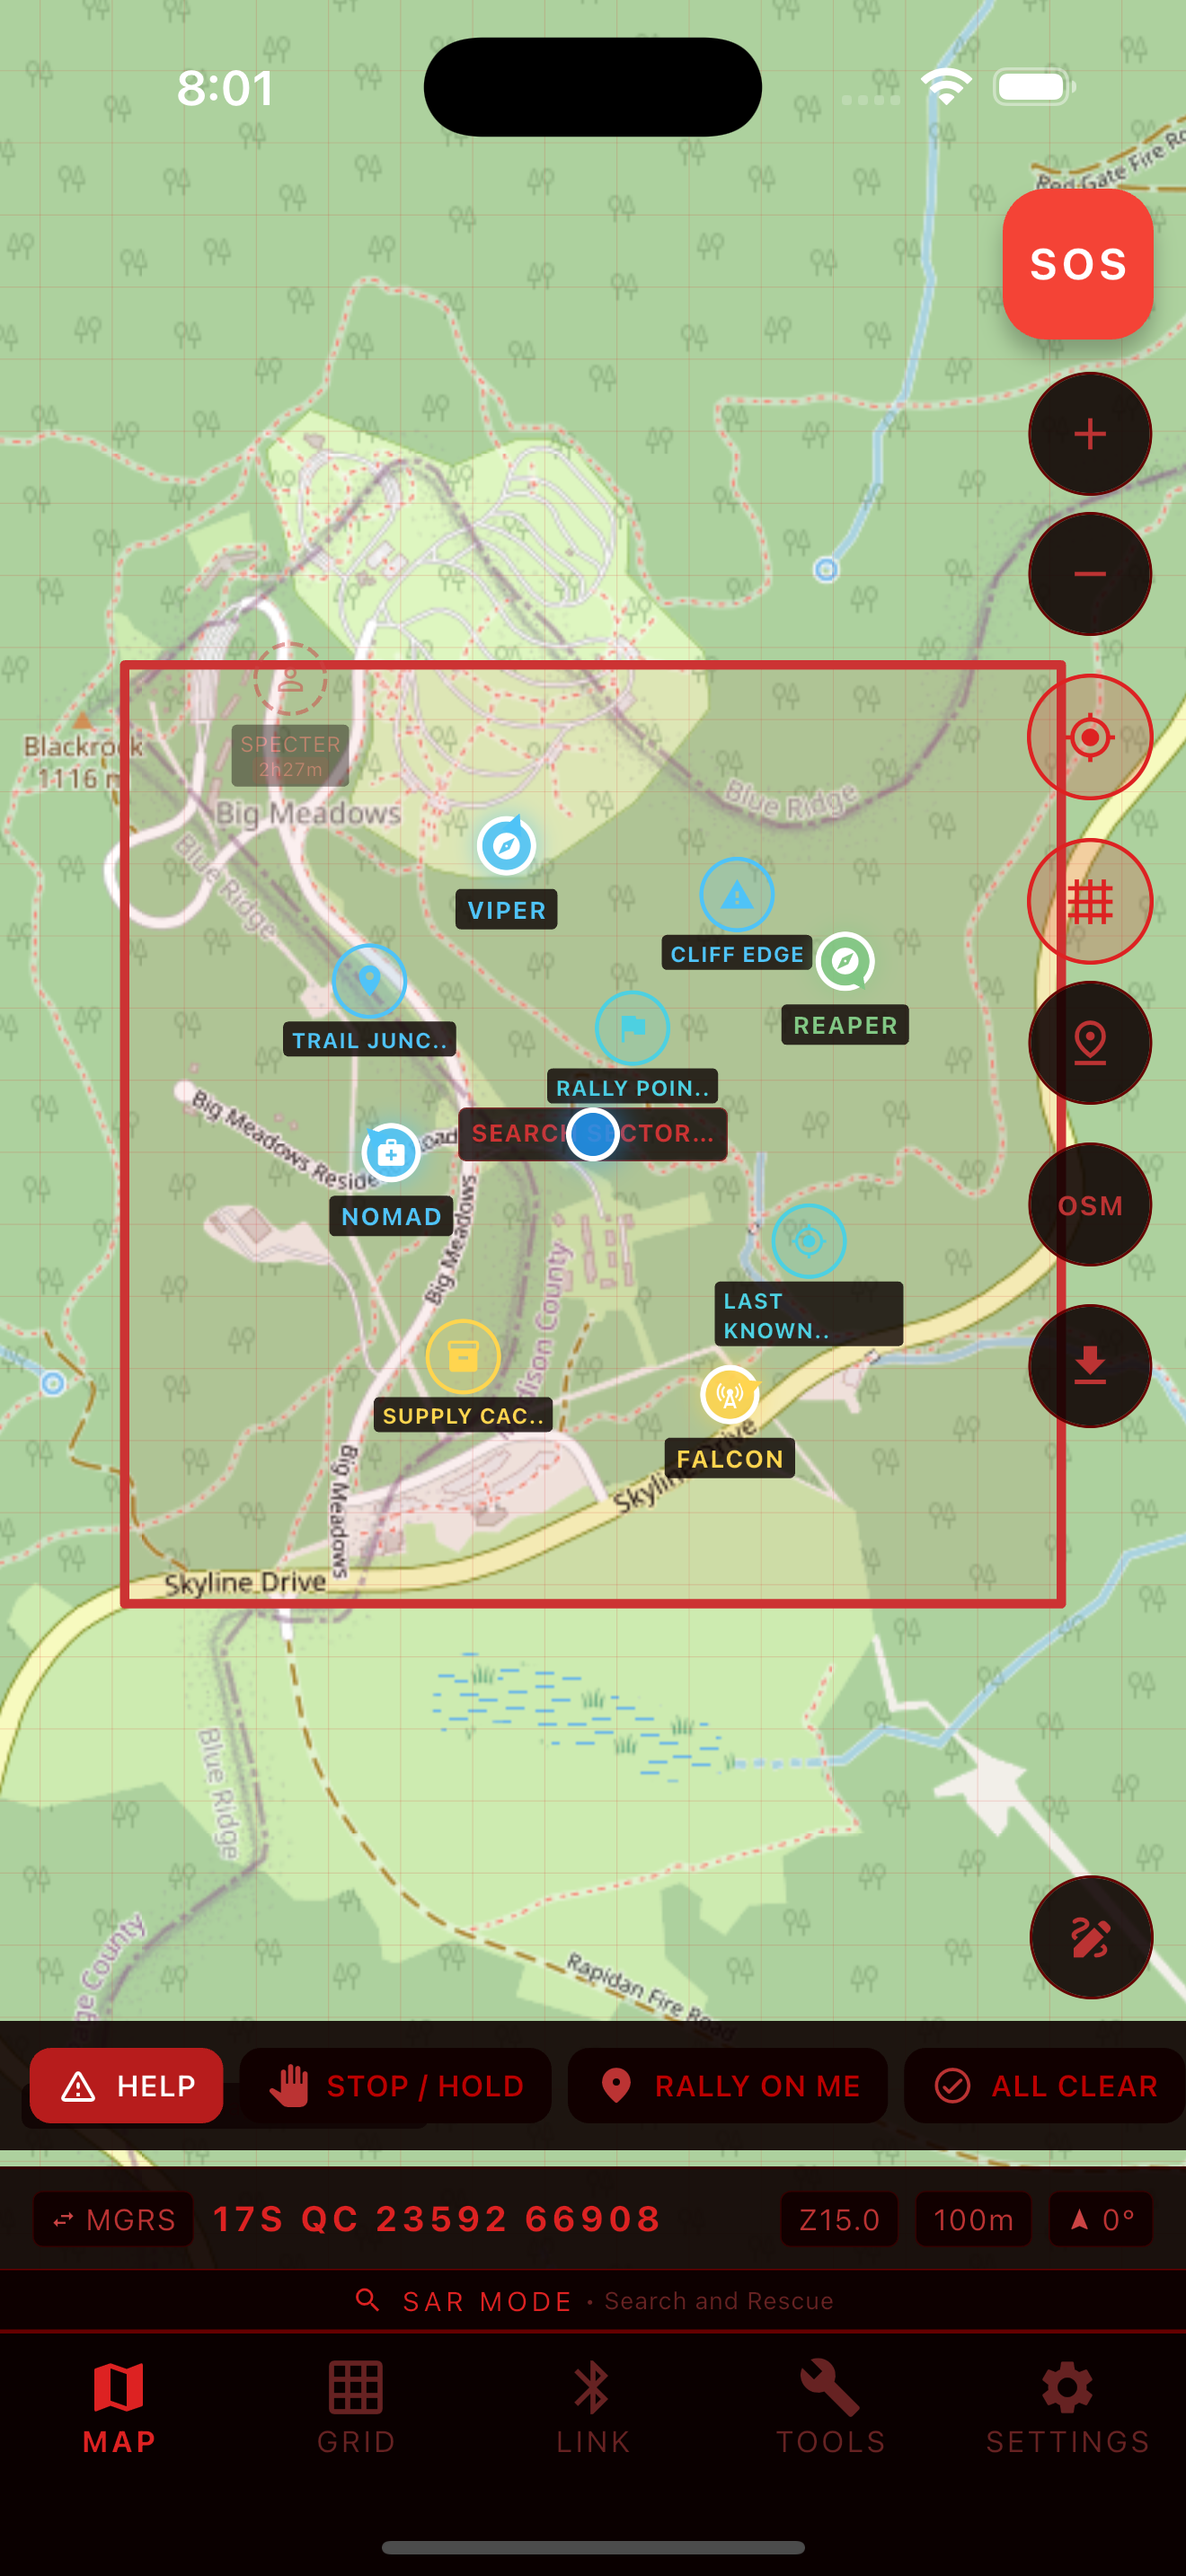 redgridtactical/redgridlink
Offline MGRS navigation + BLE proximity team sync for 2-8 people. No cell service needed. V1.0 through V4.0 roadmap in README.
 spyboy-productions/spyboy-productions
Discord bot providing cybersecurity tools, information gathering, and community-driven resources for security enthusiasts and CTF participants.
 synthient/public-research
Open source research and talks on threat intelligence, fingerprinting, and fraud detection.
 s4vitar/airdroidpwner
Programa ideal para robar toda la información de un dispositivo remotamente a través de la aplicación AirDroid. [CVE-2019-9599]…
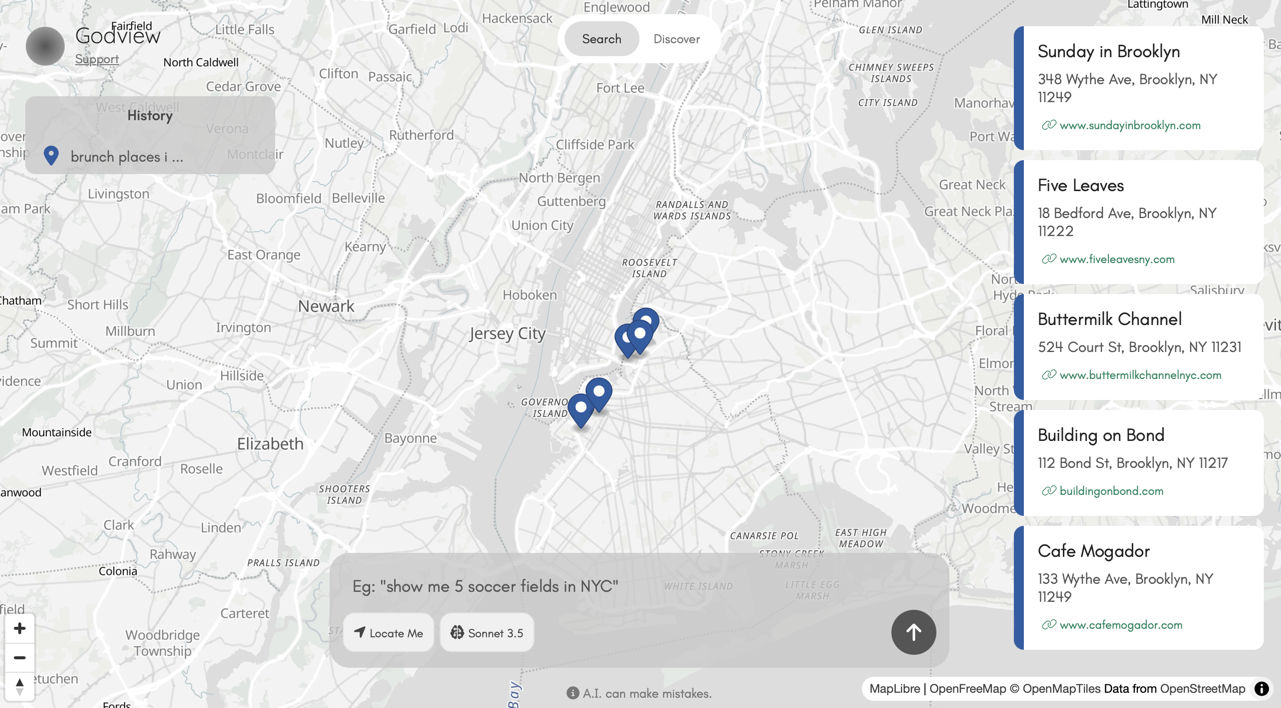 space0blaster/smartmap
LLM based map for research, exploration and discovery.
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
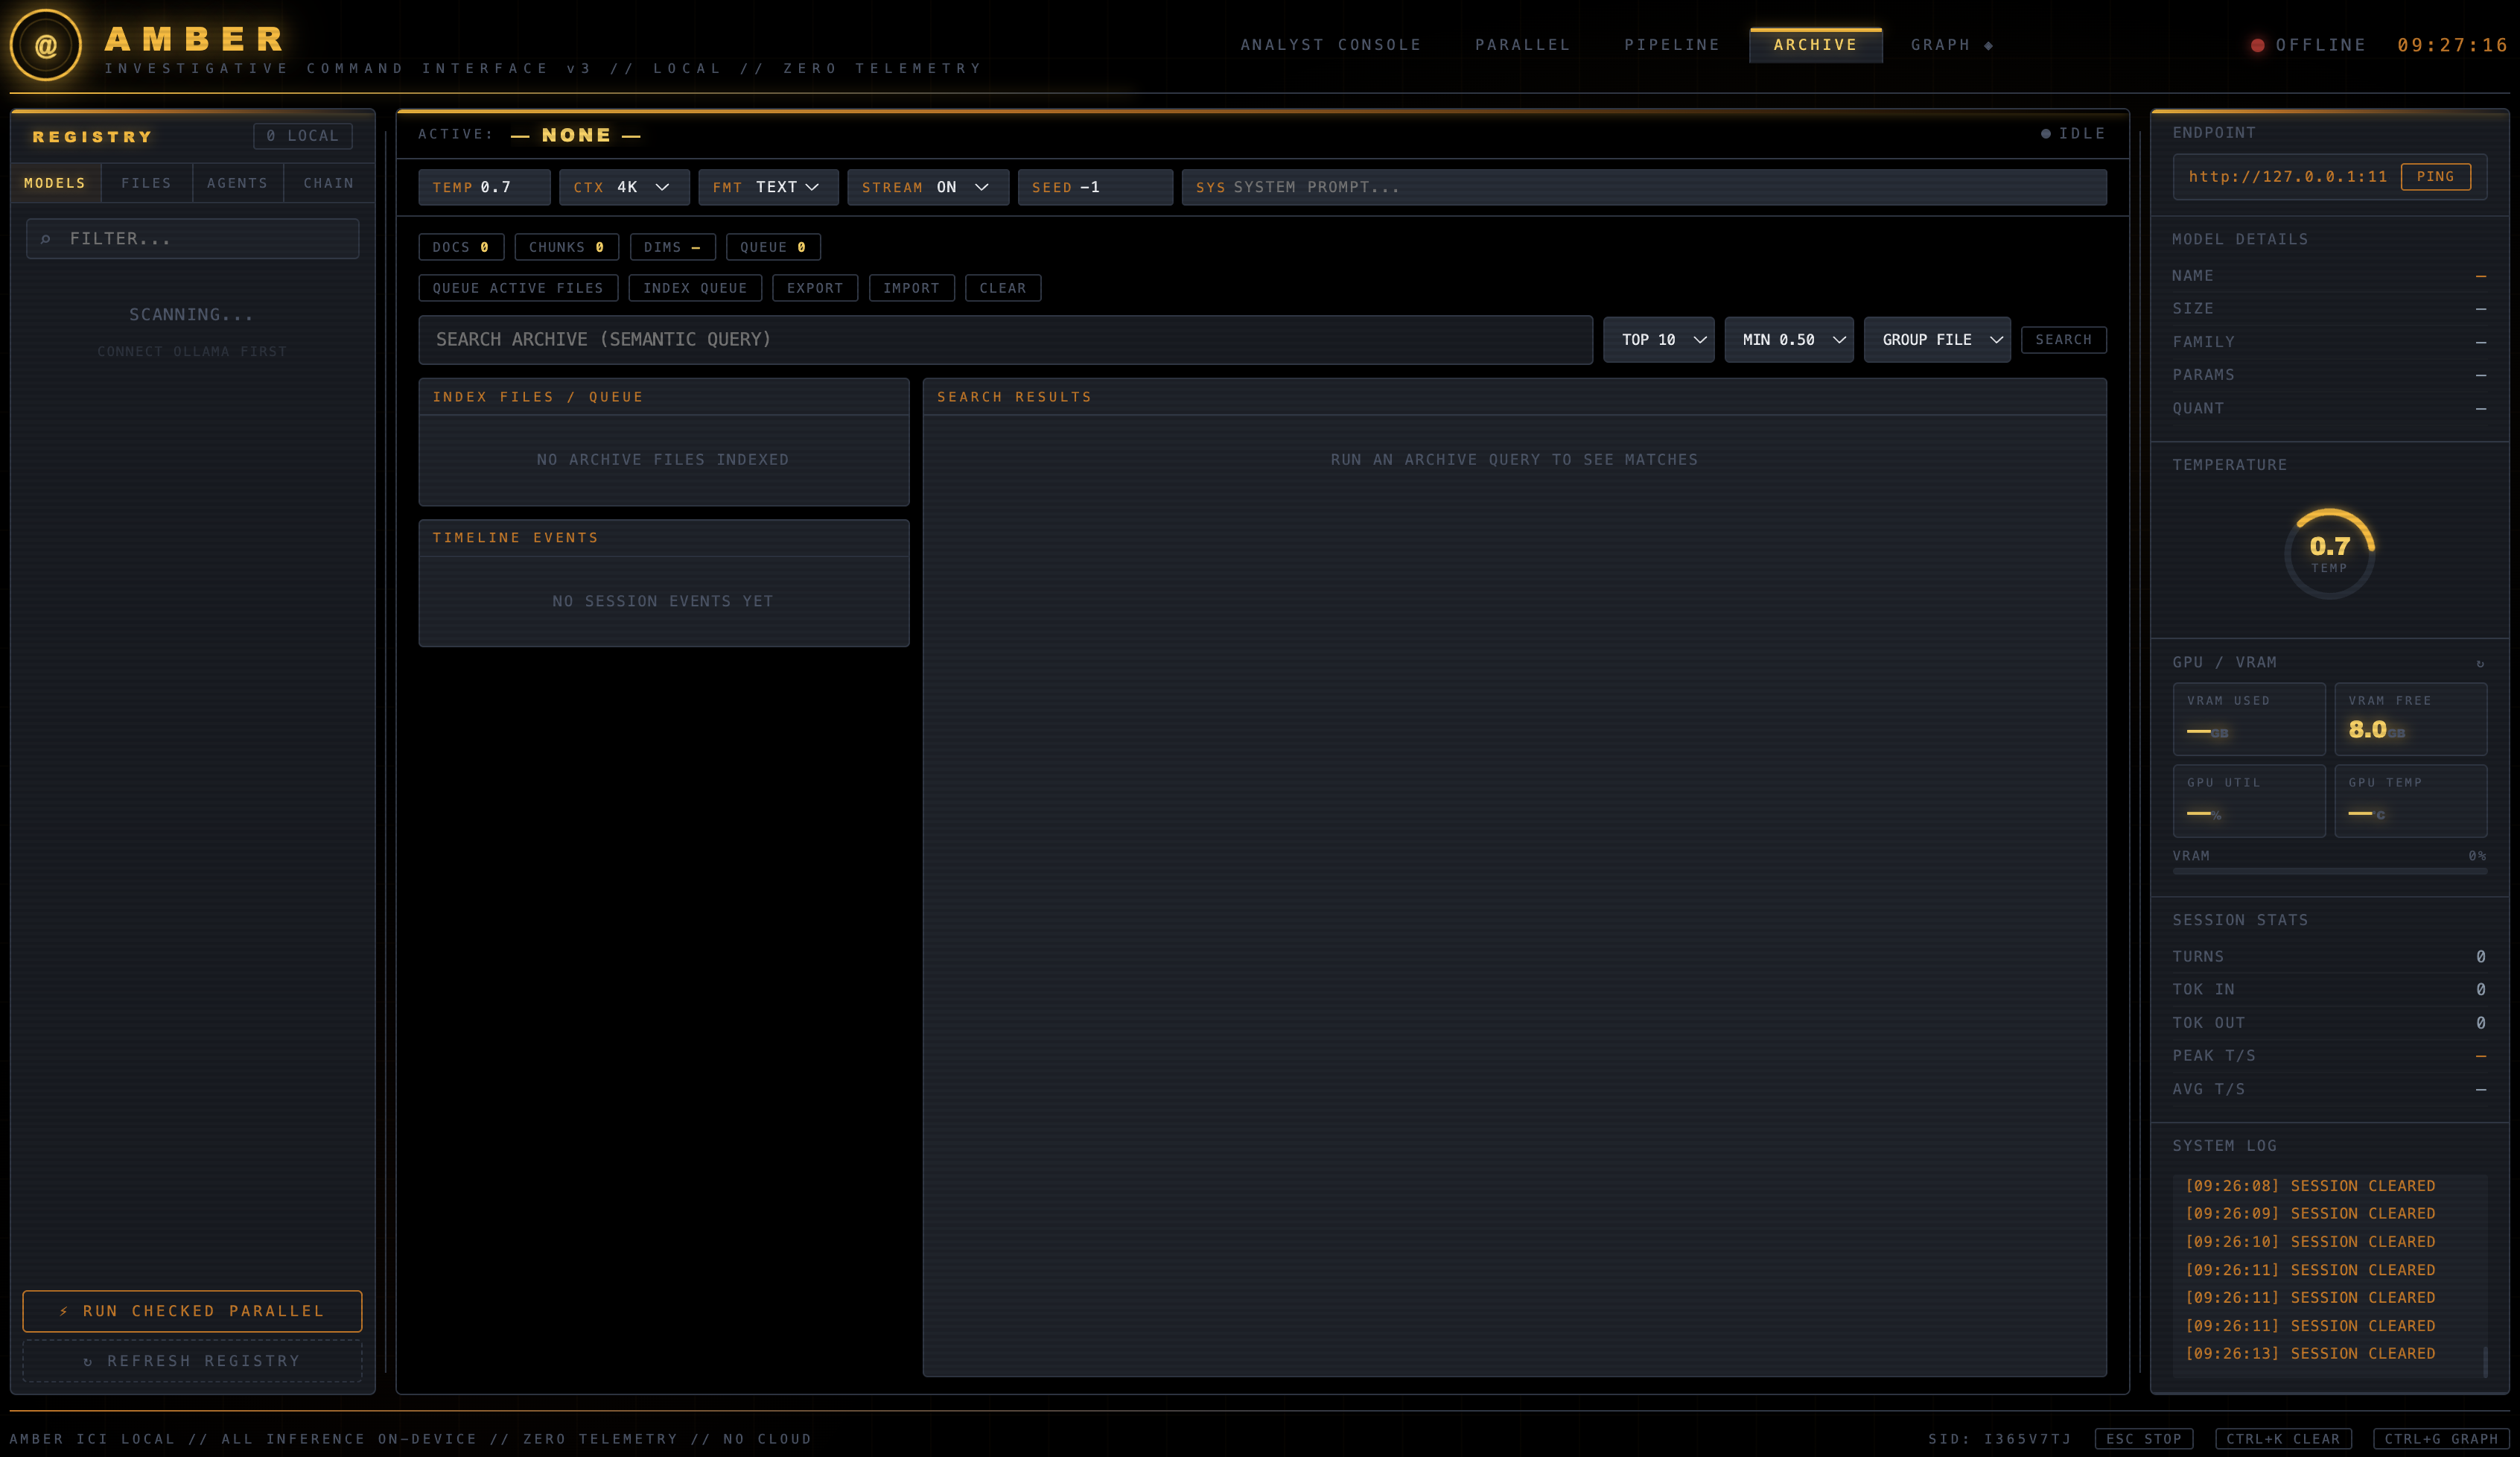 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…
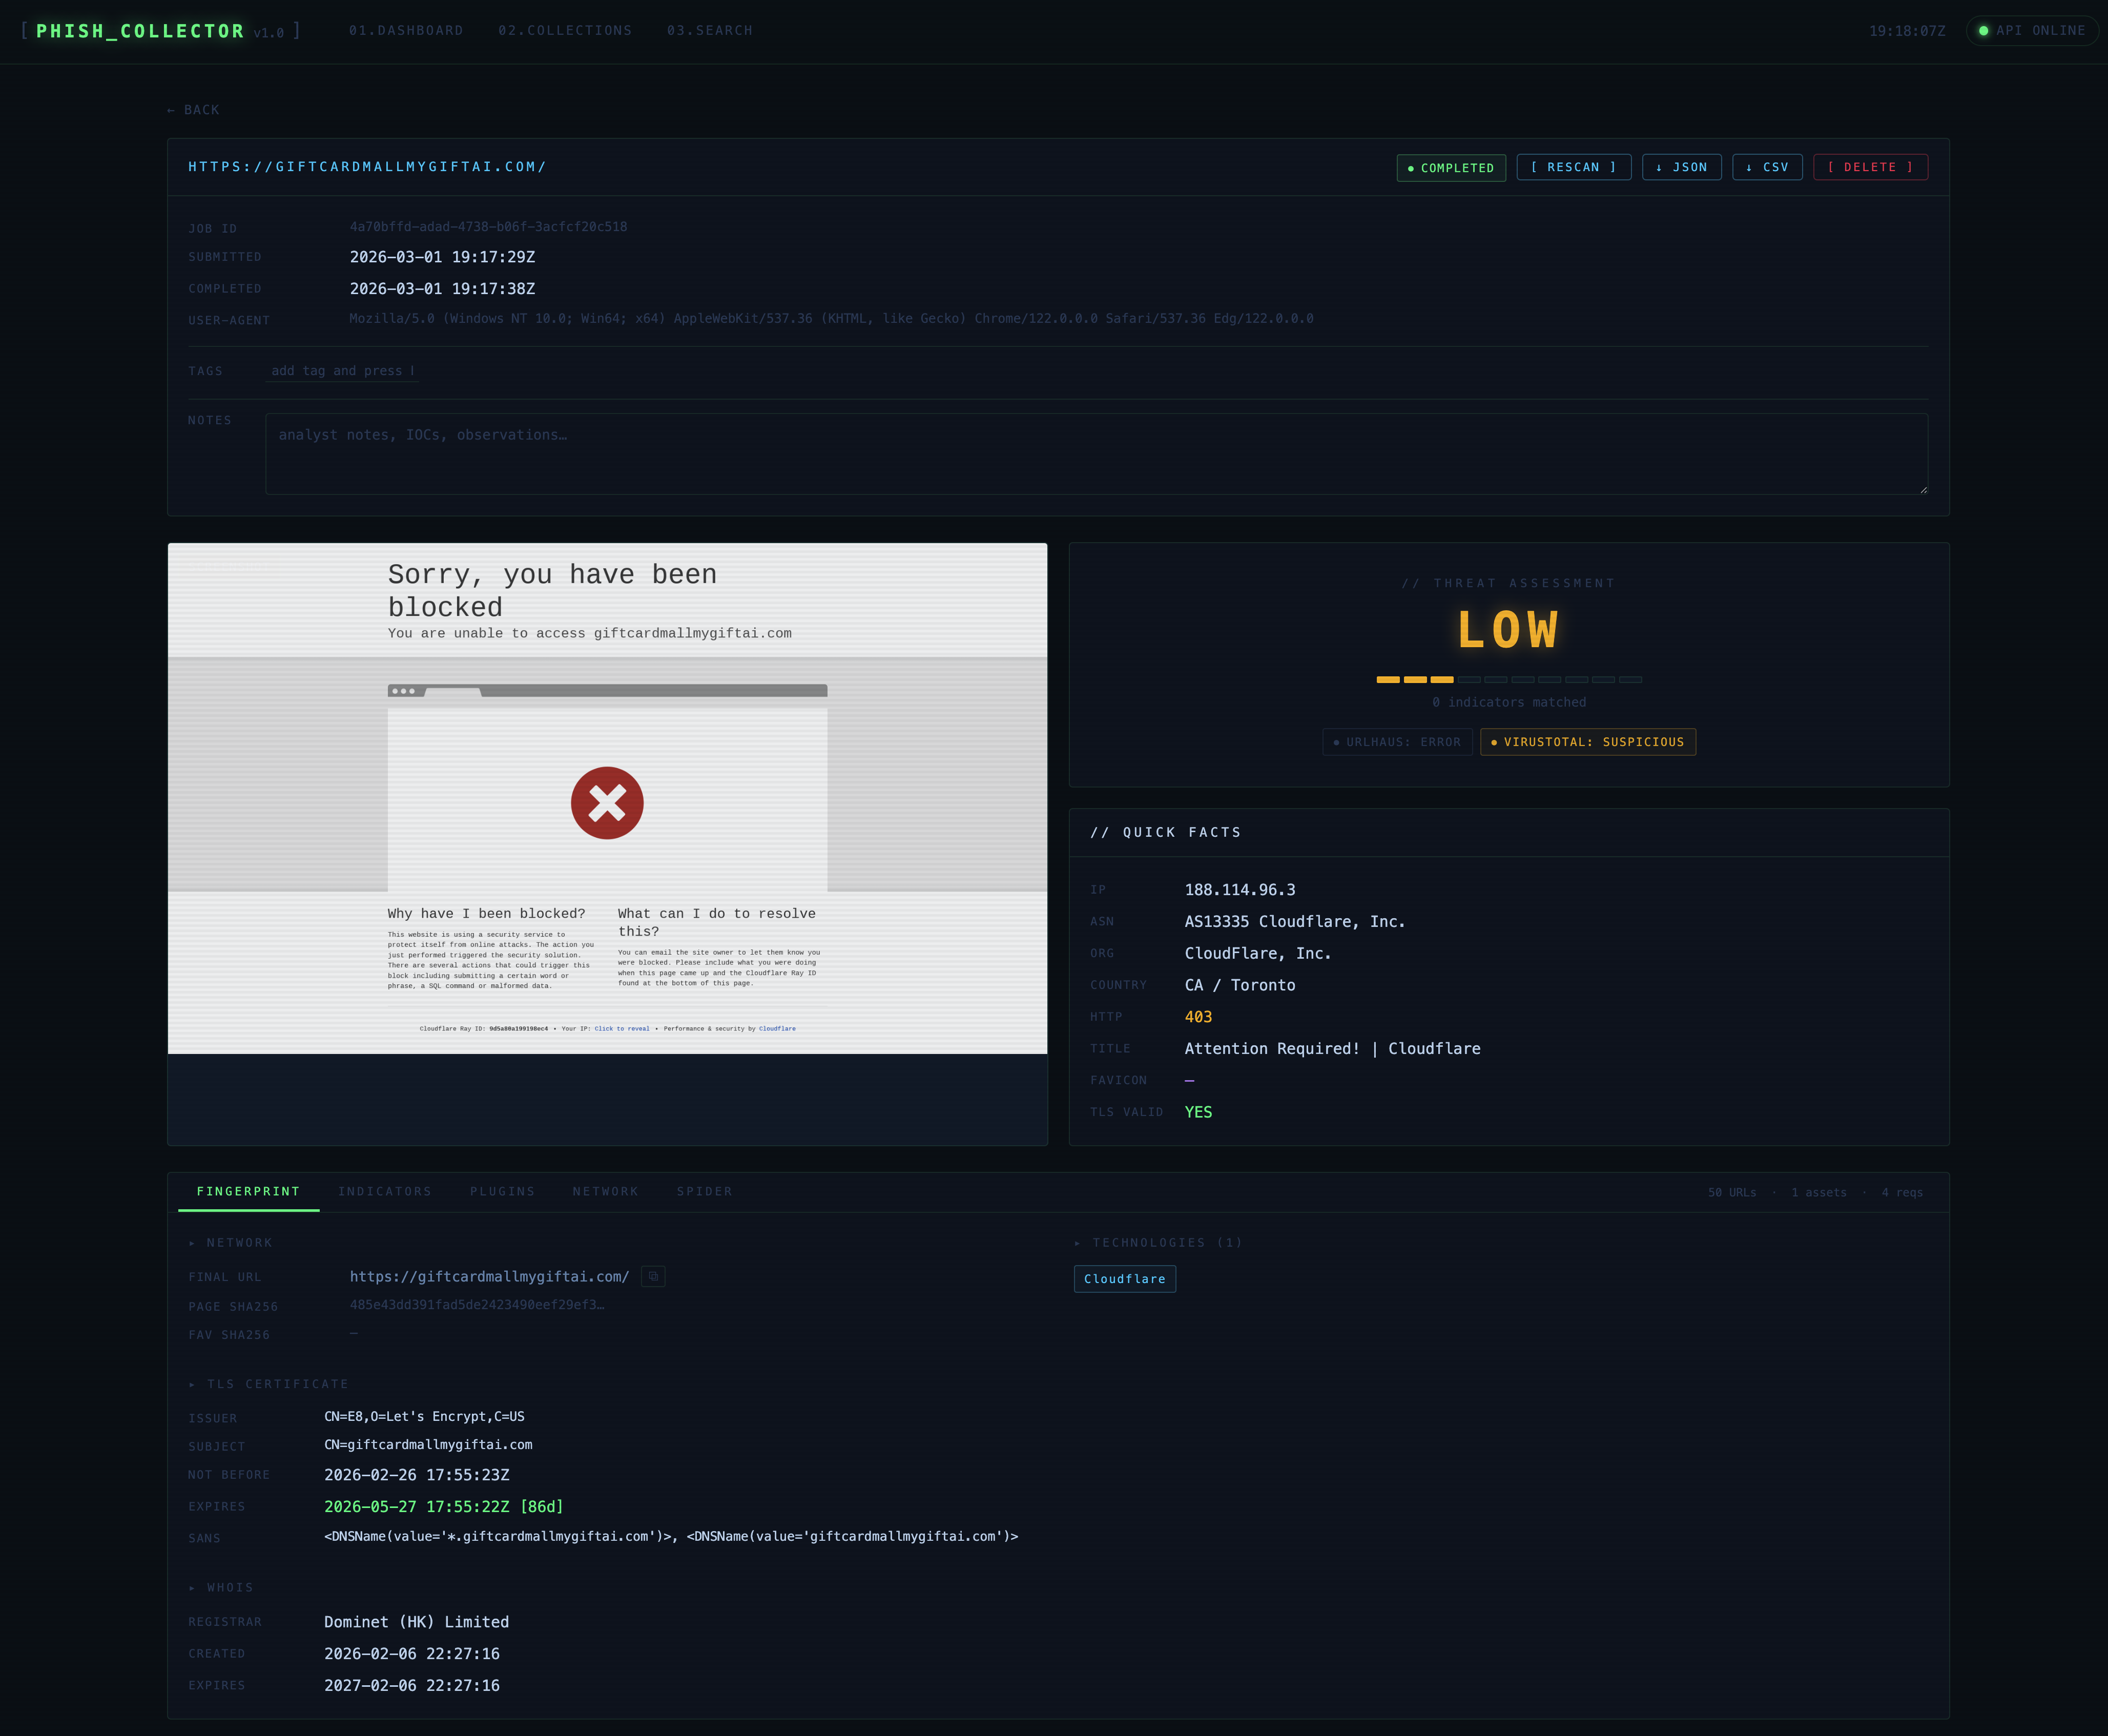 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 sanix-darker/falla
A search-engine-cli-scraper for more than 15 search engines, including Google. duckduckgo, Bing, Ask, etc...
 thewhiteh4t/llmreaper
Passive LLM Conversation Capture & Sensitive Data Exposure Research
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People