
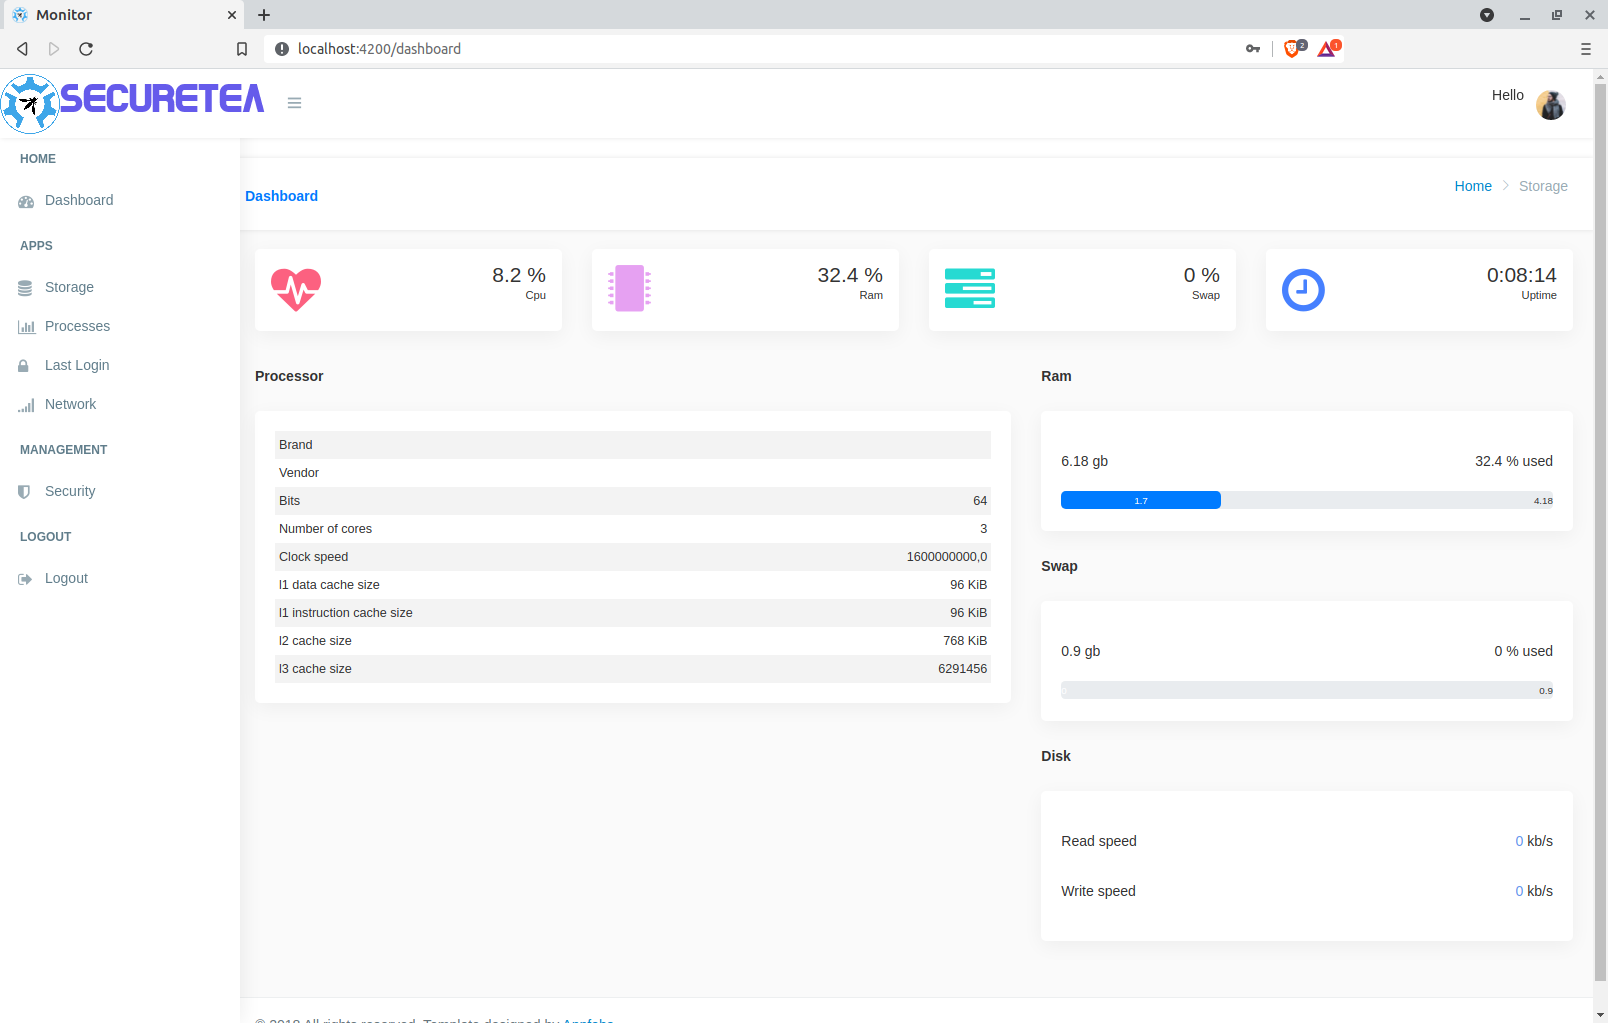
SecureTea-Project
 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
defensive-toolsintrusion-detectioniot-security+4
302
owasp/securetea-projectThe OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
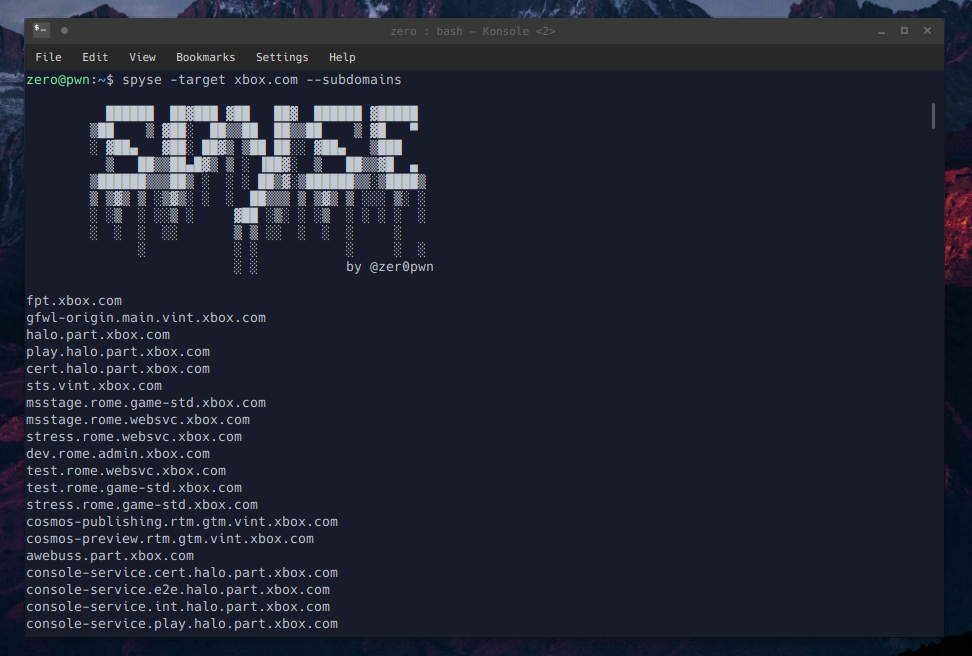 zeropwn/spyse.py
Python API wrapper and command-line client for the tools hosted on spyse.com.
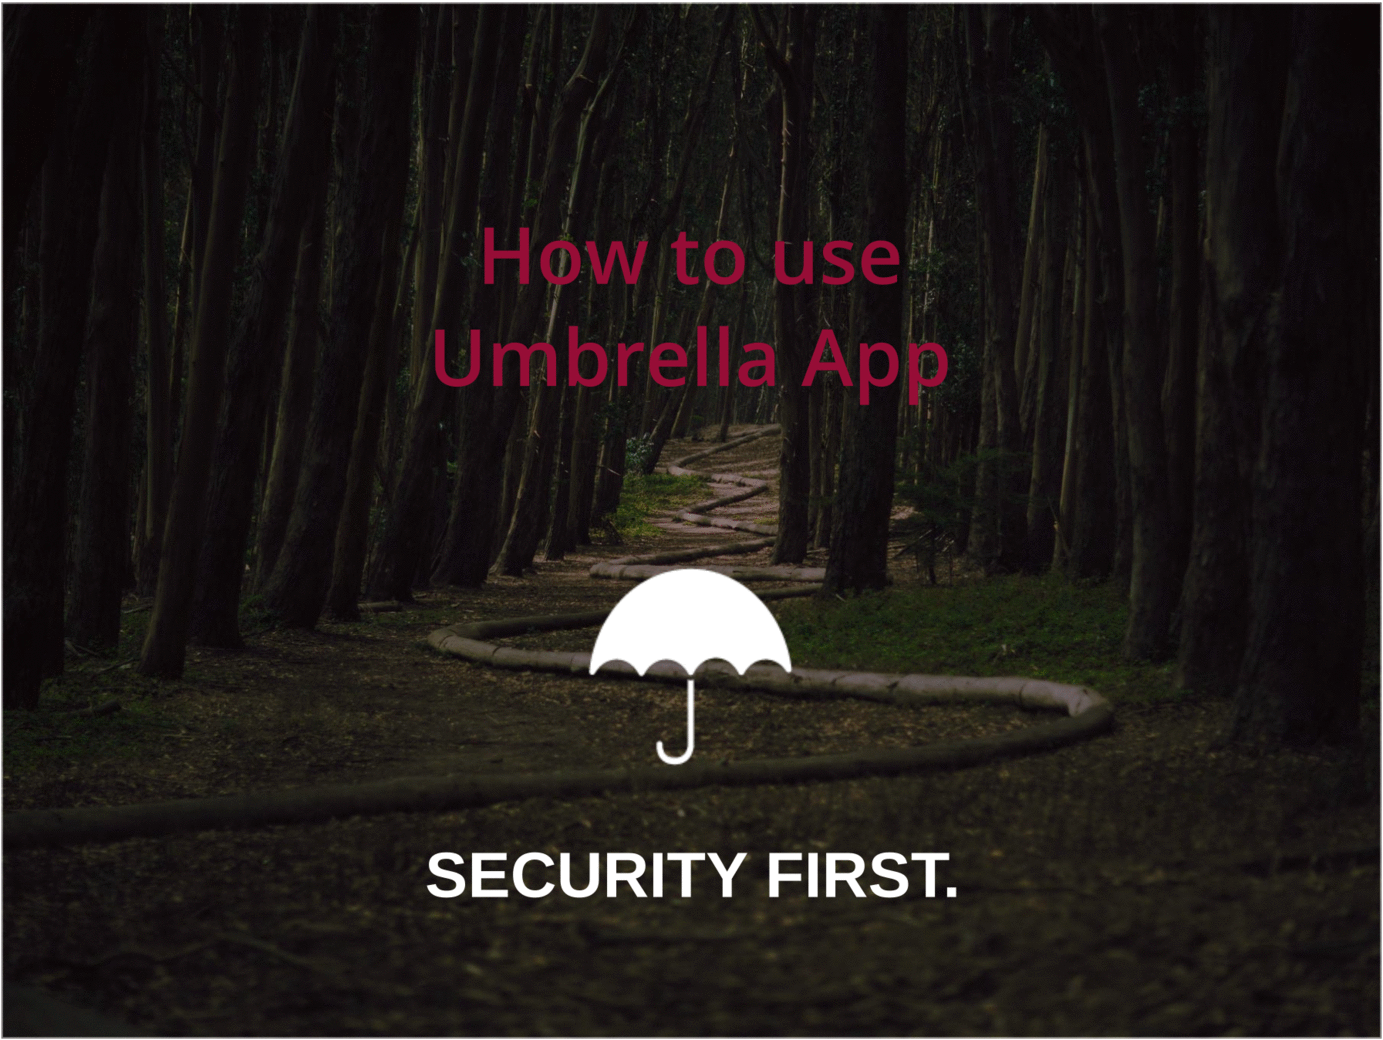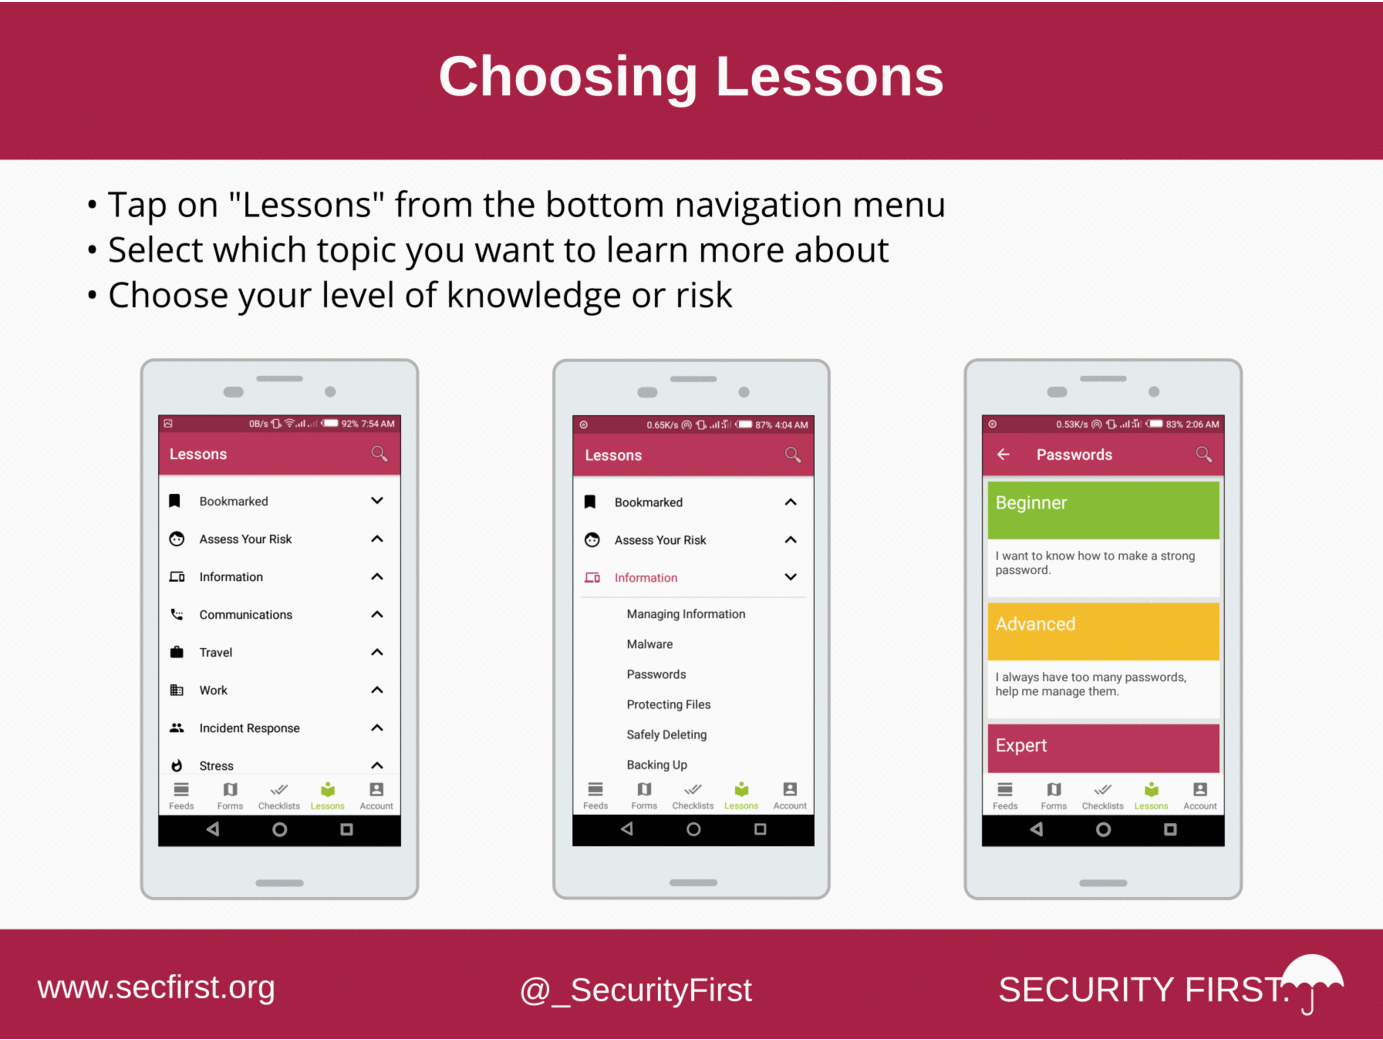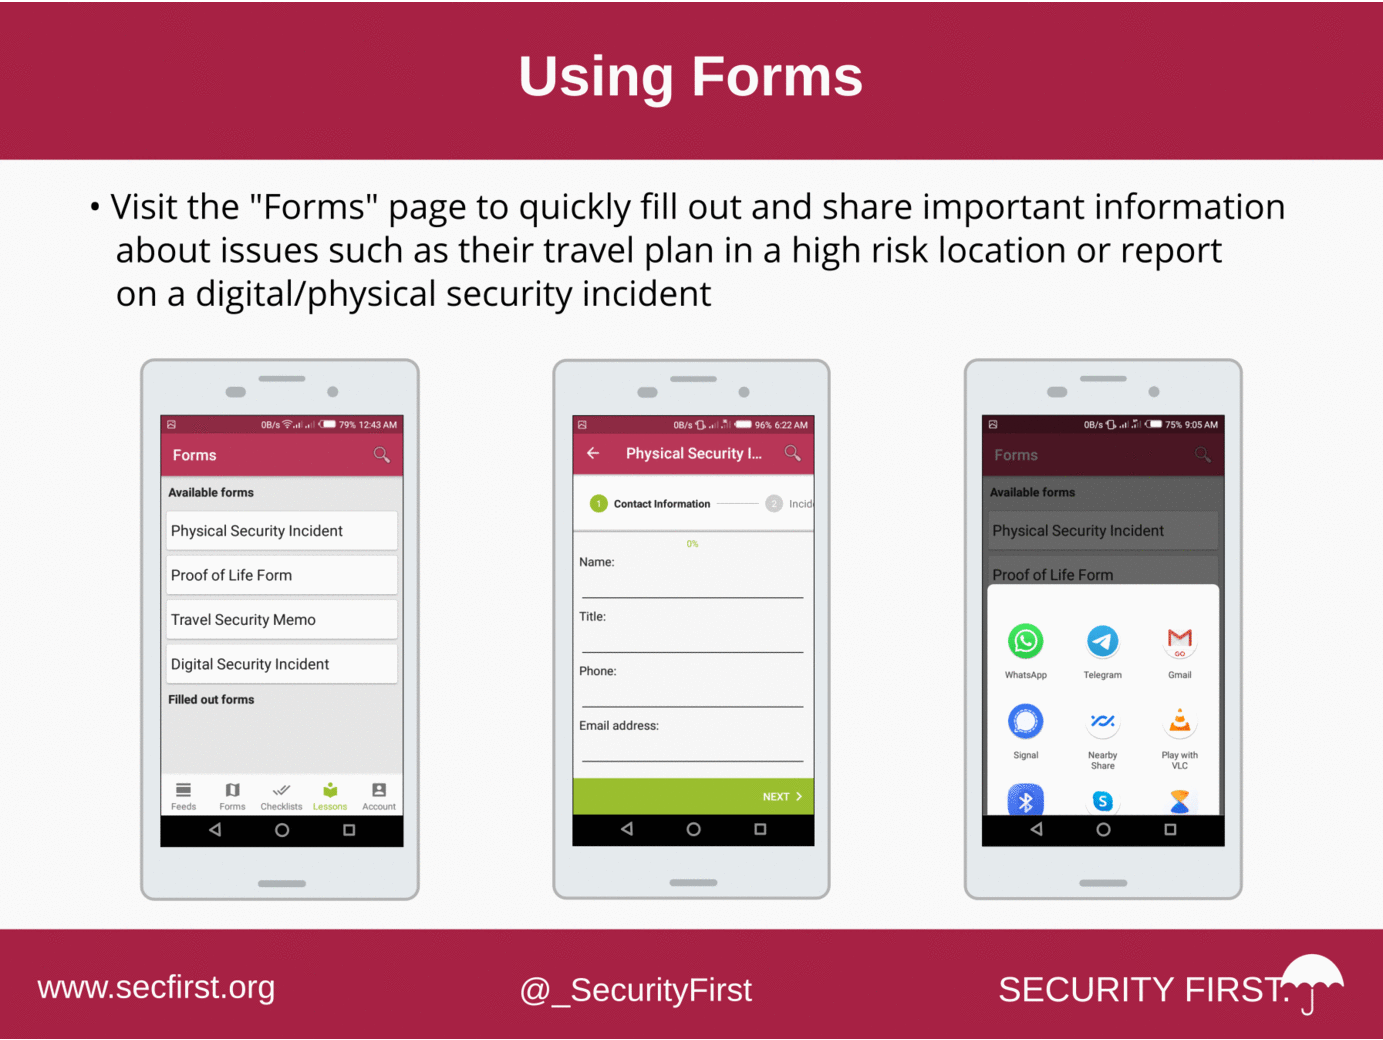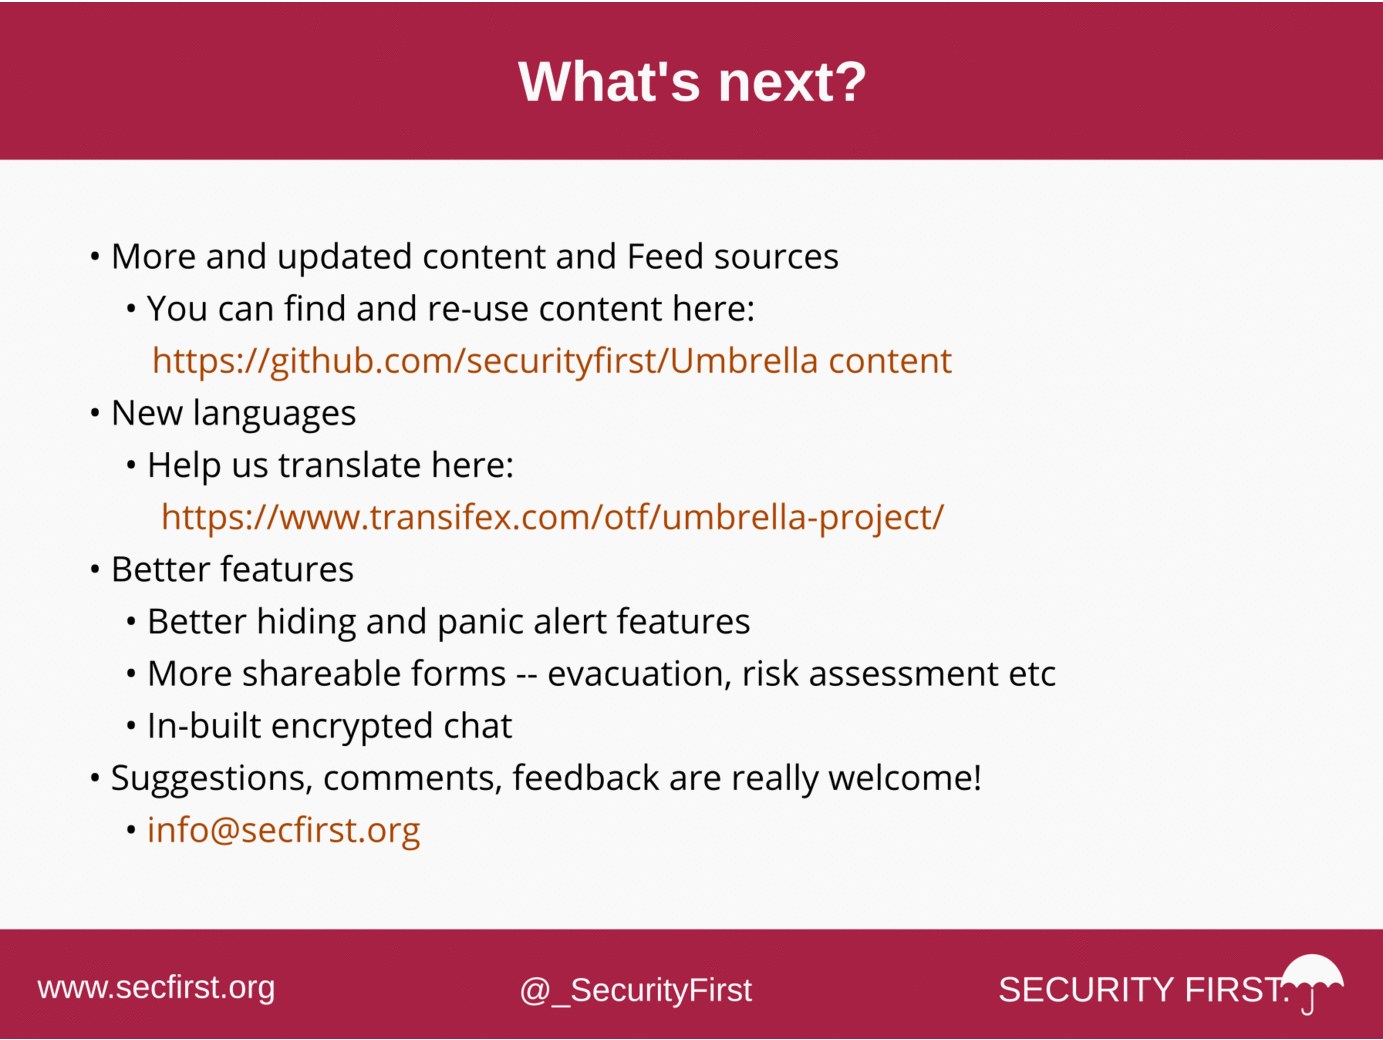 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…
 refloow/refloow-geo-forensics
❤️ Free batch image & video geolocation digital forensics tool. Automatically extract EXIF data, visualize GPS coordinates on maps, and reconstruct…
 serain/bbrecon
Python library and CLI for the Bug Bounty Recon API
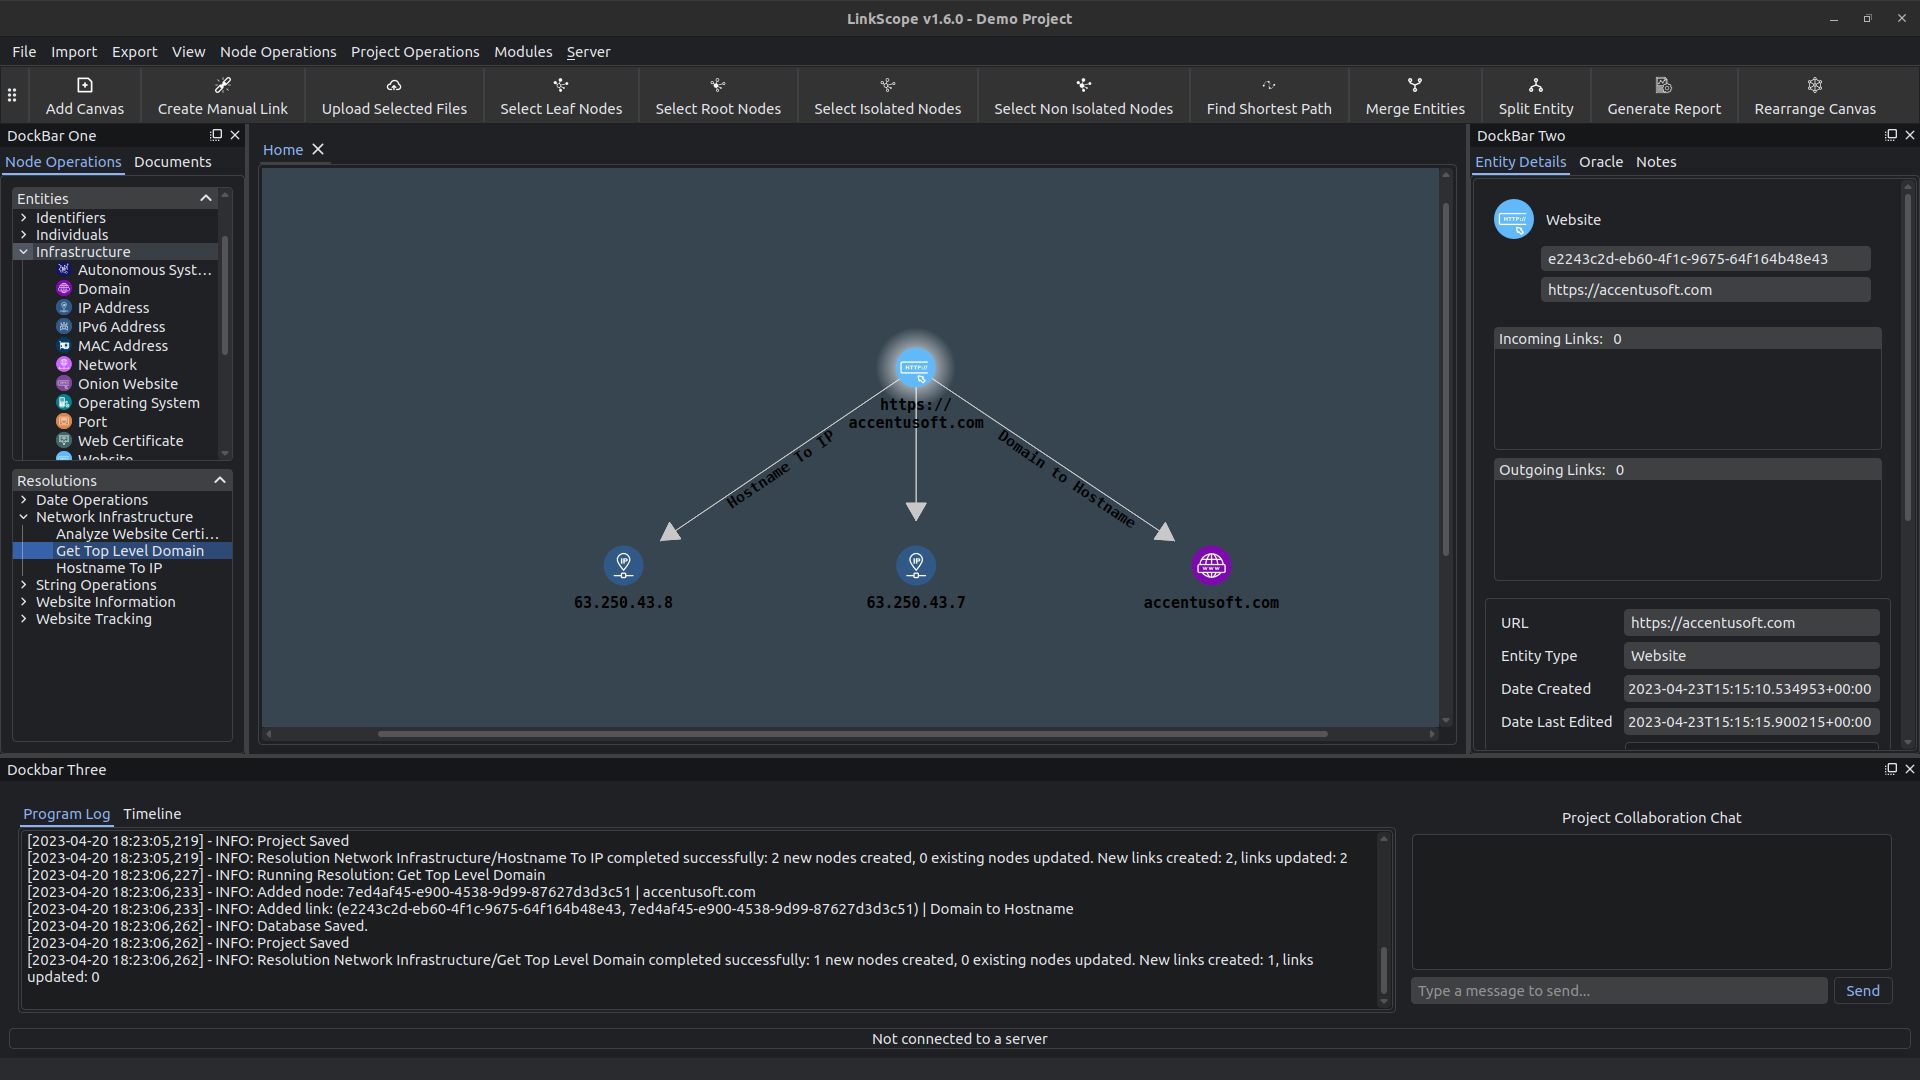 accentusoft/linkscope_client
Repository for the LinkScope Client software.
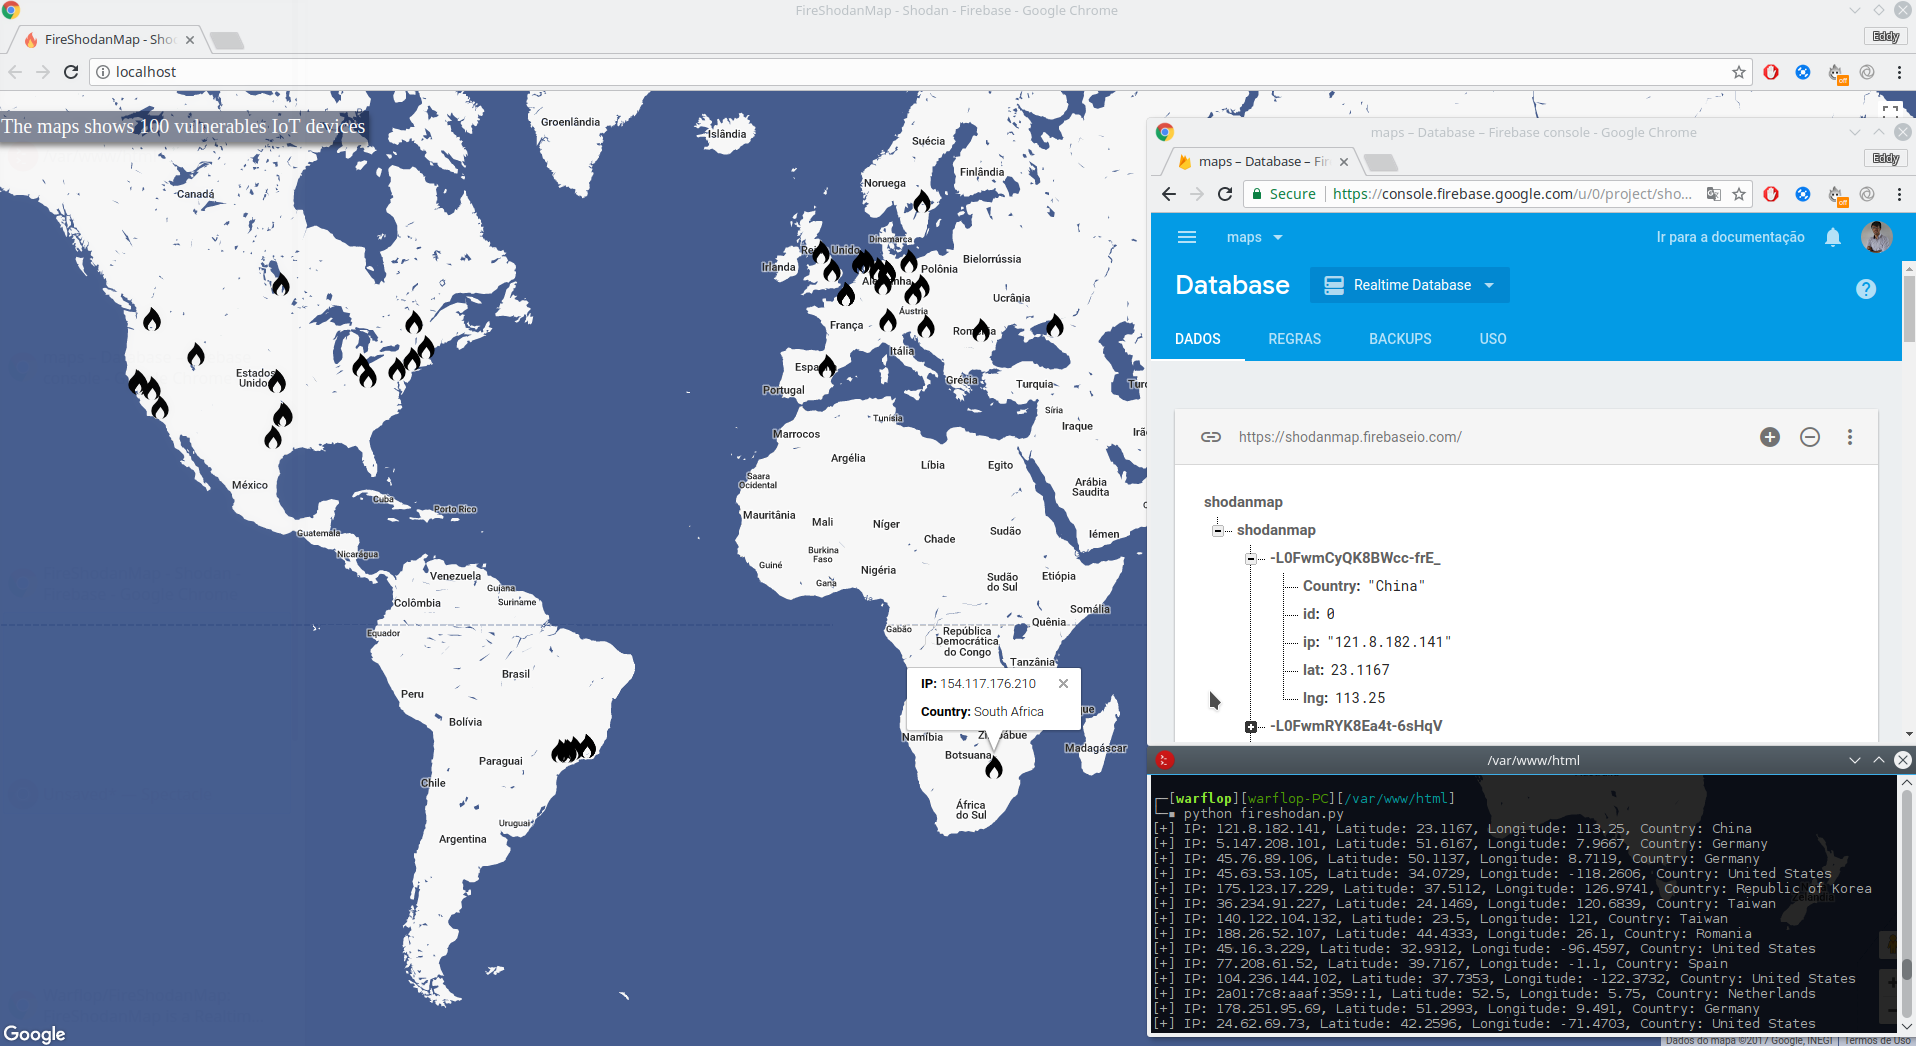 warflop/fireshodanmap
FireShodanMap is a Realtime map that integrates Firebase, Google Maps and Shodan. A search is carried out using Shodan searching vulnerable devices…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 mirsamantajbakhsh/onionharvester
A small TOR Onion Address harvester for checking if the address is available or not.
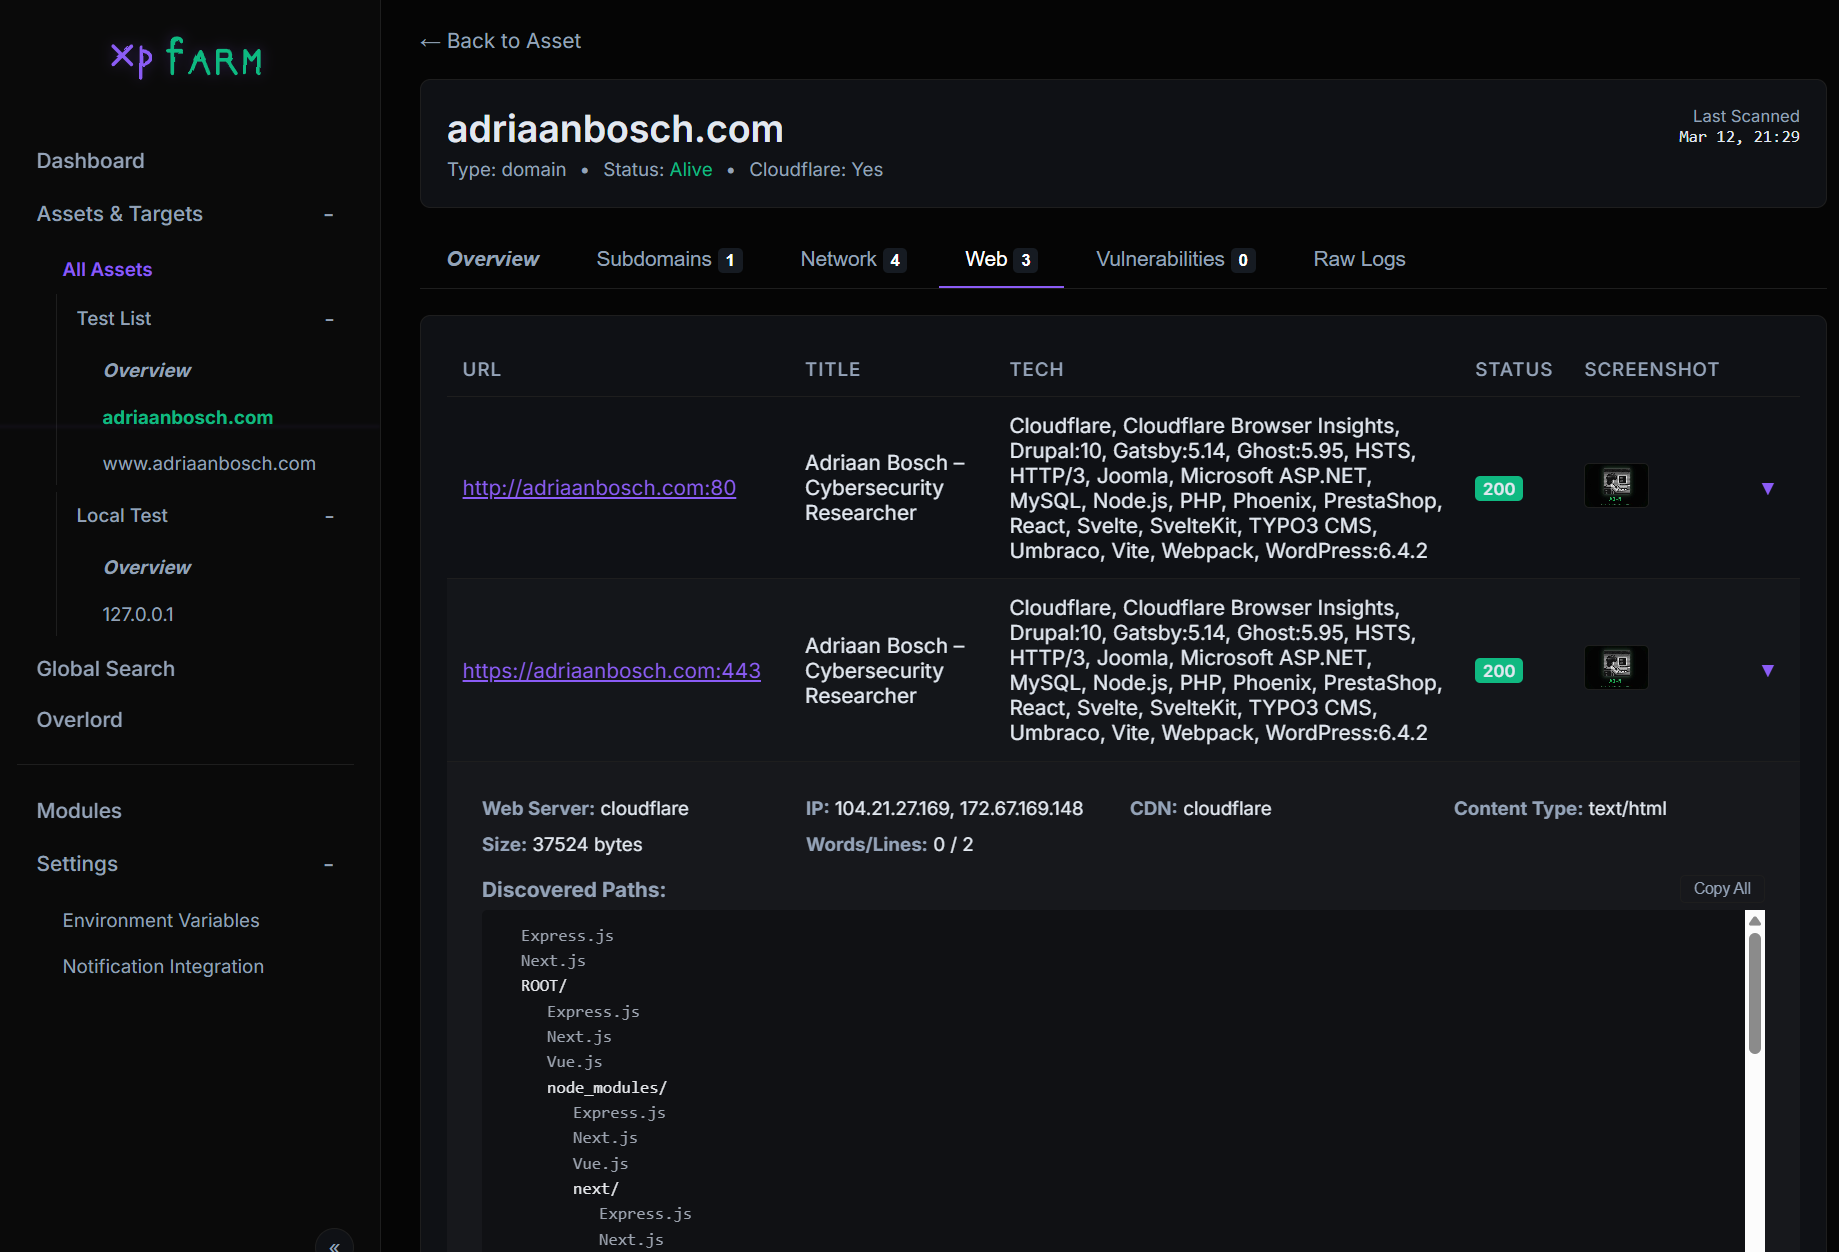 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 raddad87/rayhunter-web-flasher
Interactive wizard to flash EFF's Rayhunter on Orbic RC400L — auto-detects OS
 thewhitecircle/thewhitecircle.github.io
Official website of TWC
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 chirantar7004/android-passive-location-tracker
Location tracking app without location permissions! Makes use of CVE-2018-15835 which makes use of Android OS information leakage.
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).