Open-Source-Threat-Intel-Feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

🕵️♂️ All-in-one OSINT tool for analysing any website

Community curated list of search queries for various products across multiple search engines.

Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…

CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

Automated OSINT tool for phone number discovery, pattern detection, and cross-platform correlation.

Automated web screenshot tool for reconnaissance, capturing site visuals, server headers, and identifying default credentials. Supports multiple…

A lightweight aviation intelligence tool that queries ADSB-Exchange flight data using tail numbers or ICAO identifiers to quickly profile aircraft…

A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…

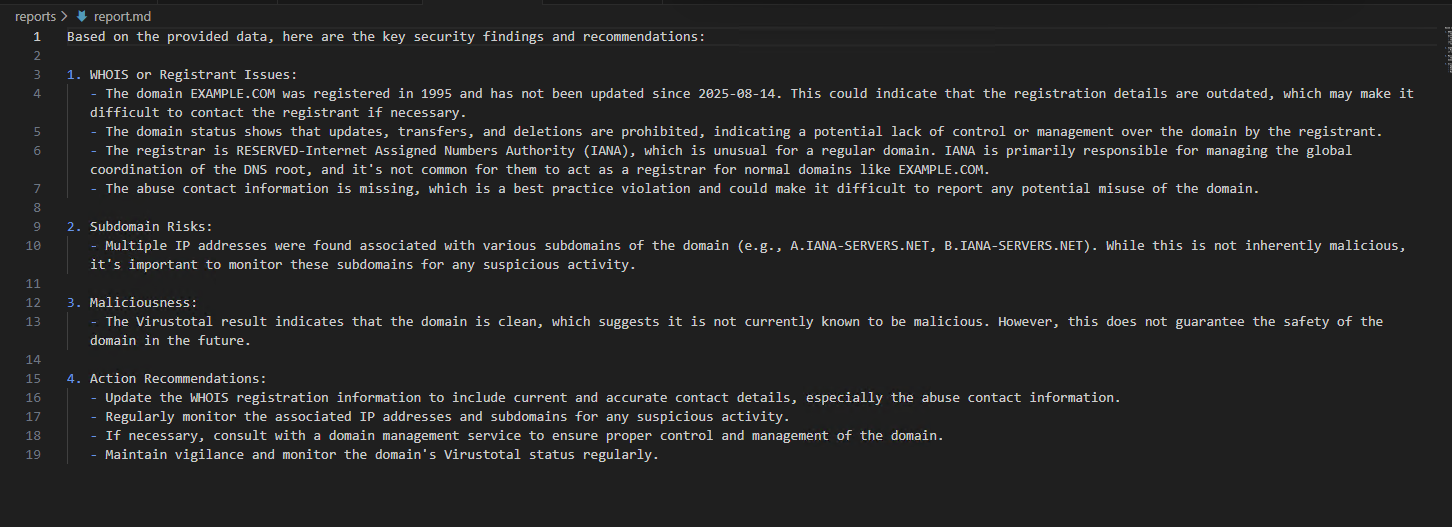
It’s an OSINT reconnaissance poc powered by Local LLMs (Ollama). You can feed it an email, domain, or IP, and it automatically performs multiple…

Passive URL discovery tool that collects domain-associated URLs from multiple public sources via command-line, supporting stdin/stdout and JSONL…

Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…


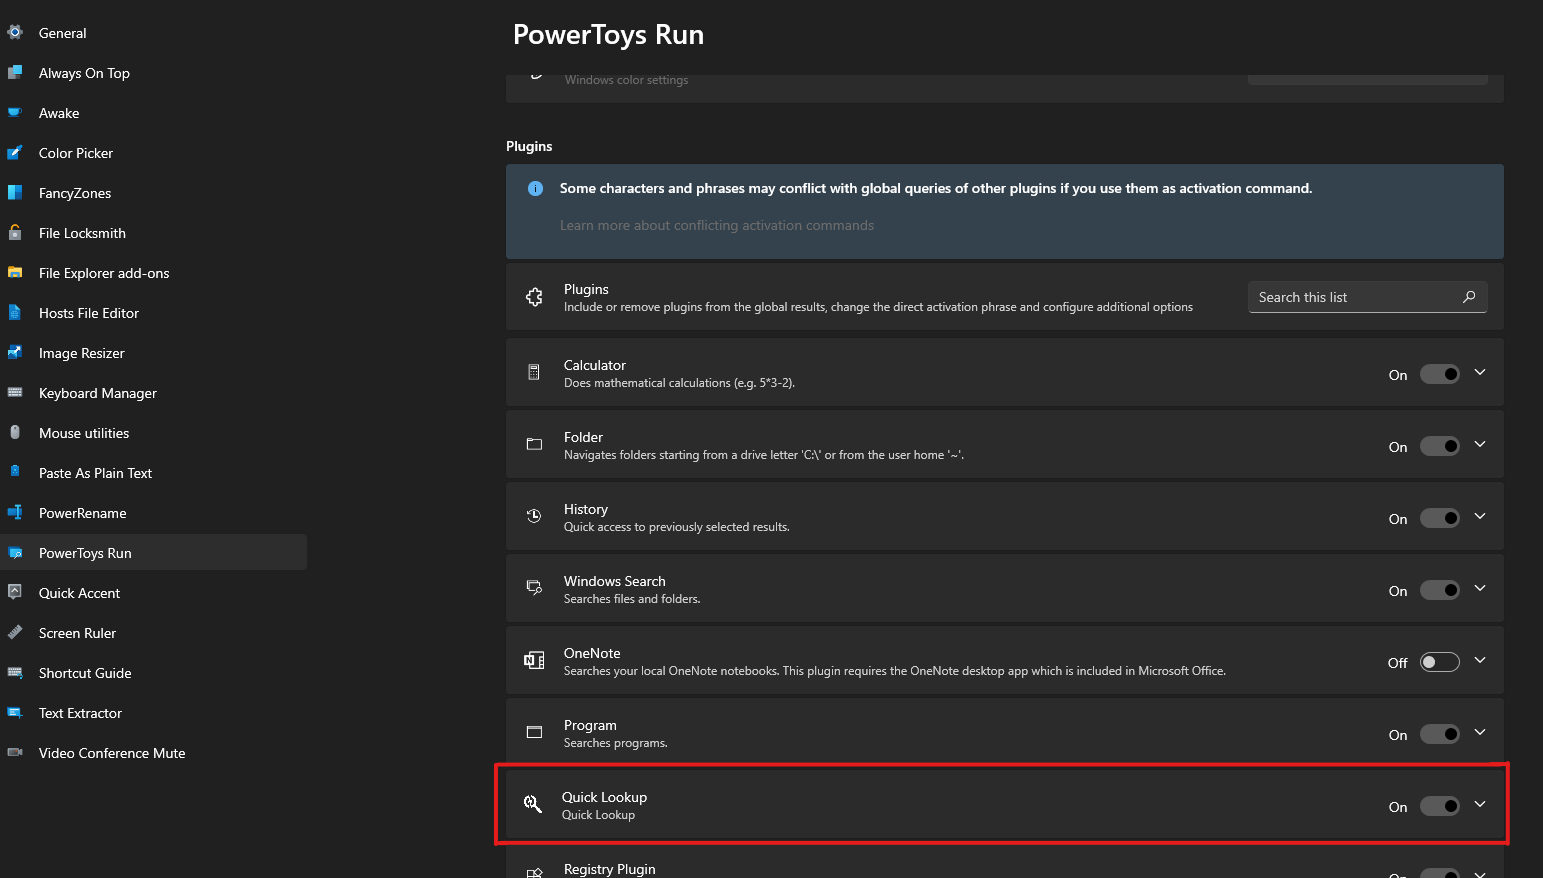
PowerToys Run plugin for instant IP, domain, and hash lookups across multiple threat intelligence platforms like Shodan, VirusTotal, and GreyNoise.

operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…

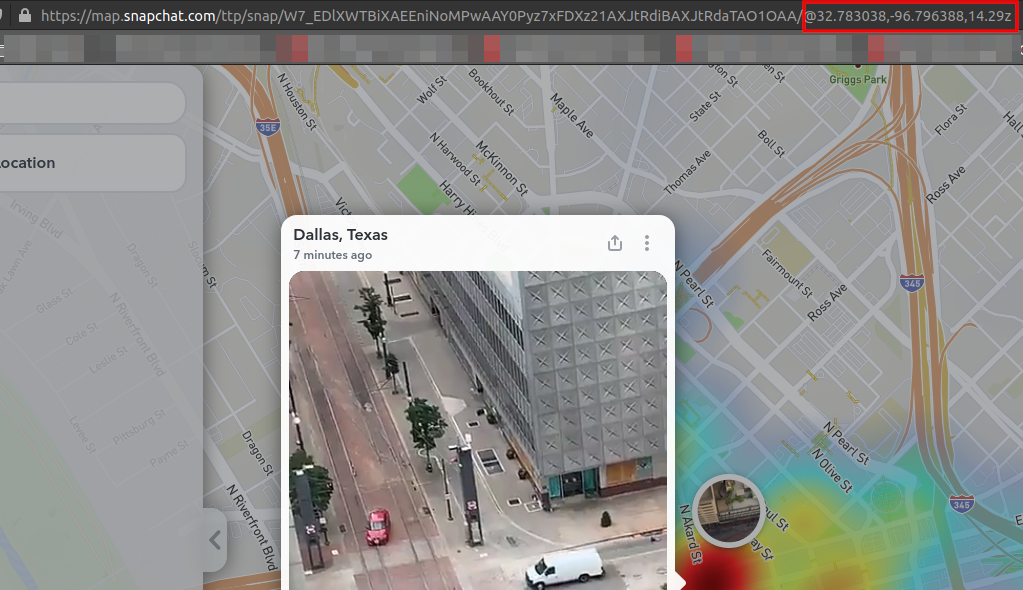
Scrapes public Snap Map locations to download and classify stories for investigative analysis, with randomized geolocation and automated review…