BlueBox
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
50
svdwi/blueboxOpen-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 nate0634034090/bug-free-memory
Curated threat intelligence repository providing vetted OSINT sources, threat reports, and indicators of compromise to support organizations during…
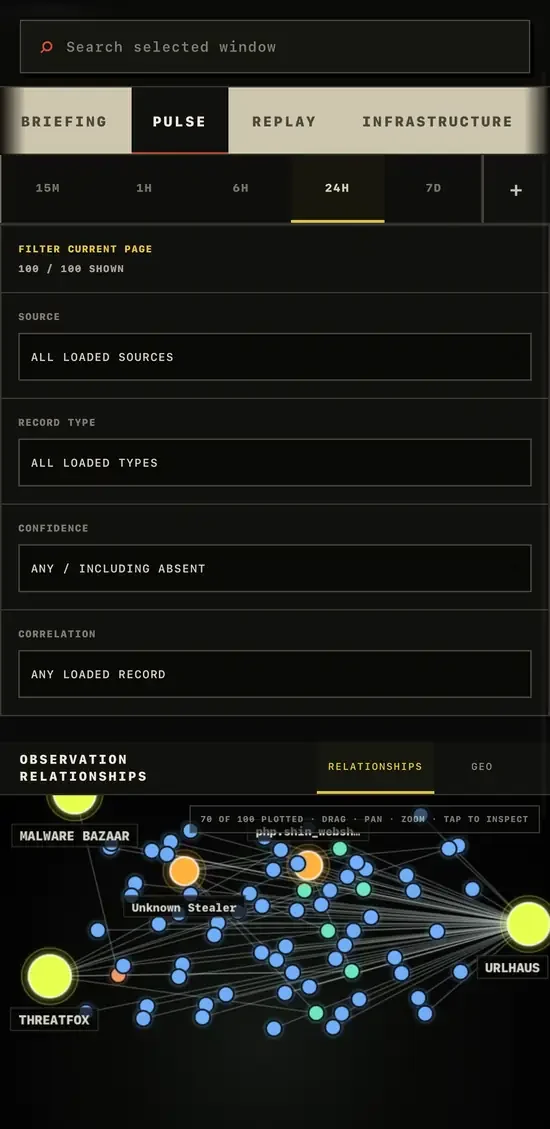
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
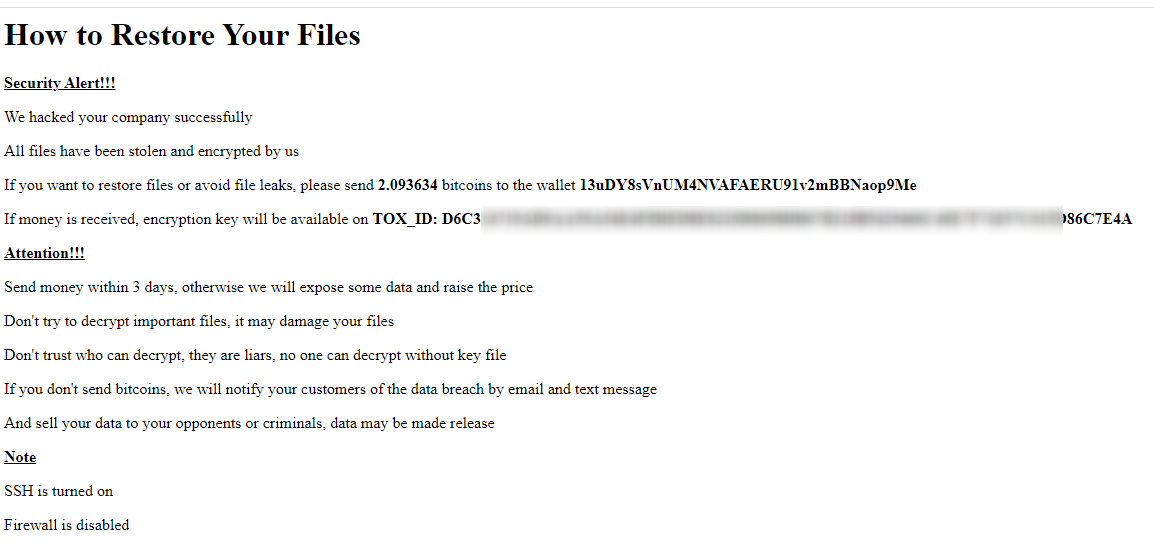 soufianetahiri/esxi_ransomware_bitcoinwallets
ESXi semi-automated ransomware attacks bitcoin wallets
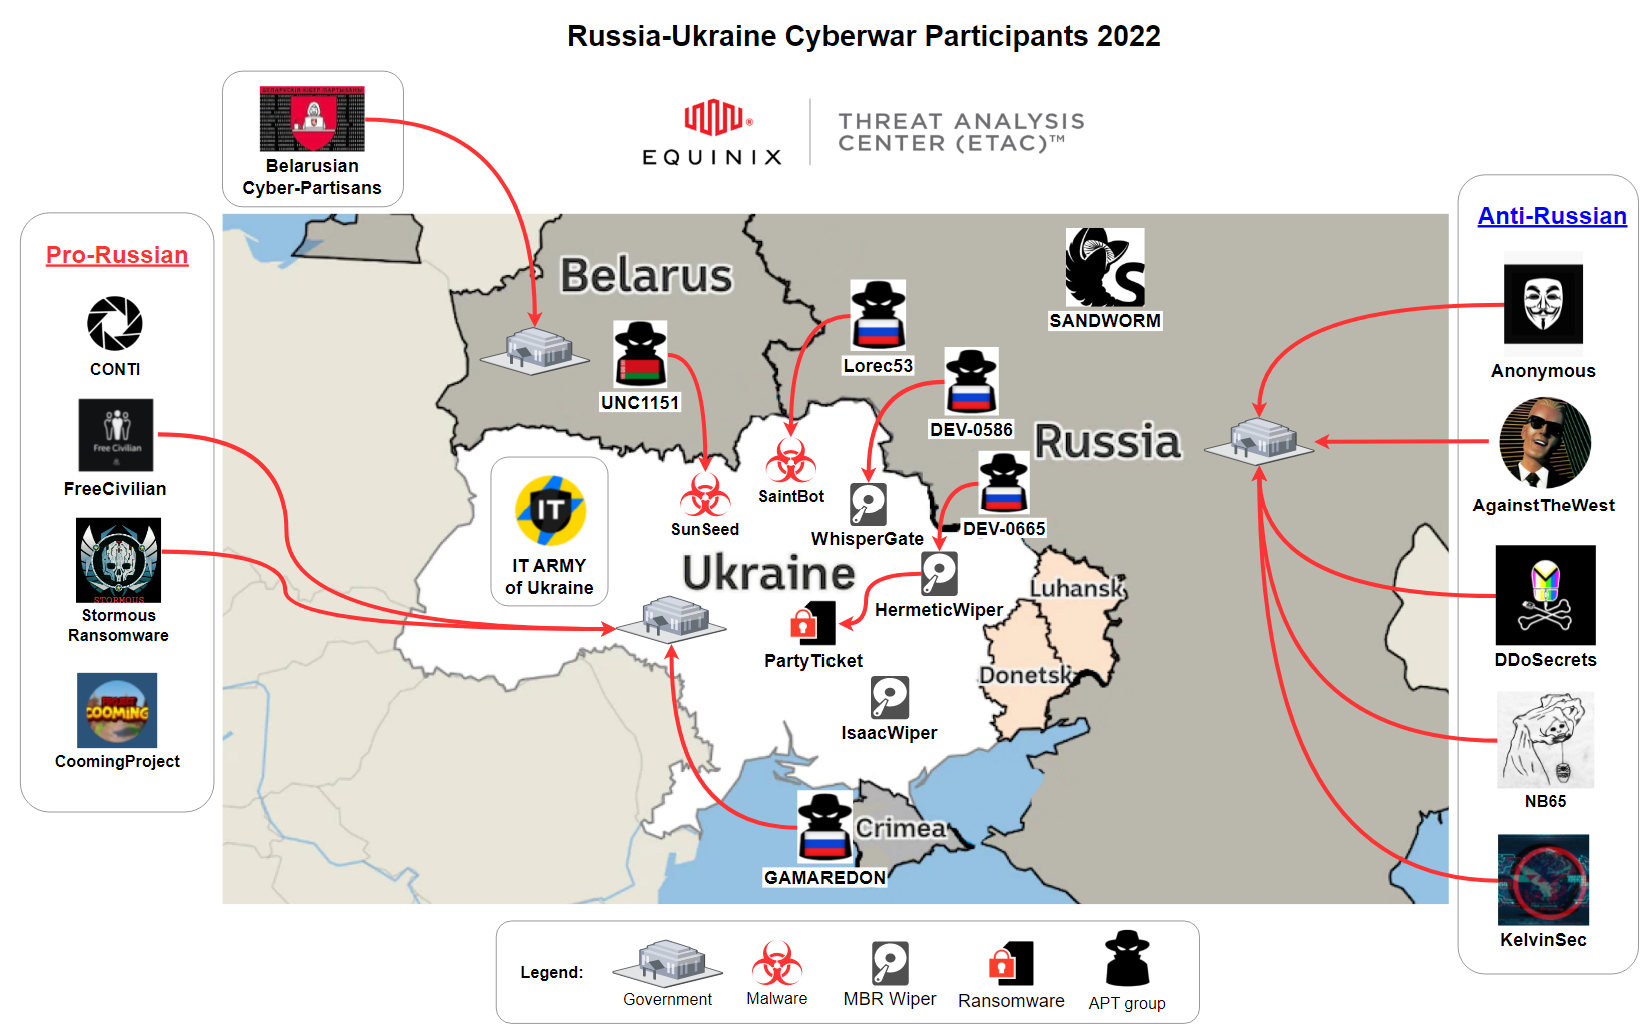 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 amnestytech/investigations
Indicators of Compromise from Amnesty International's cyber investigations
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
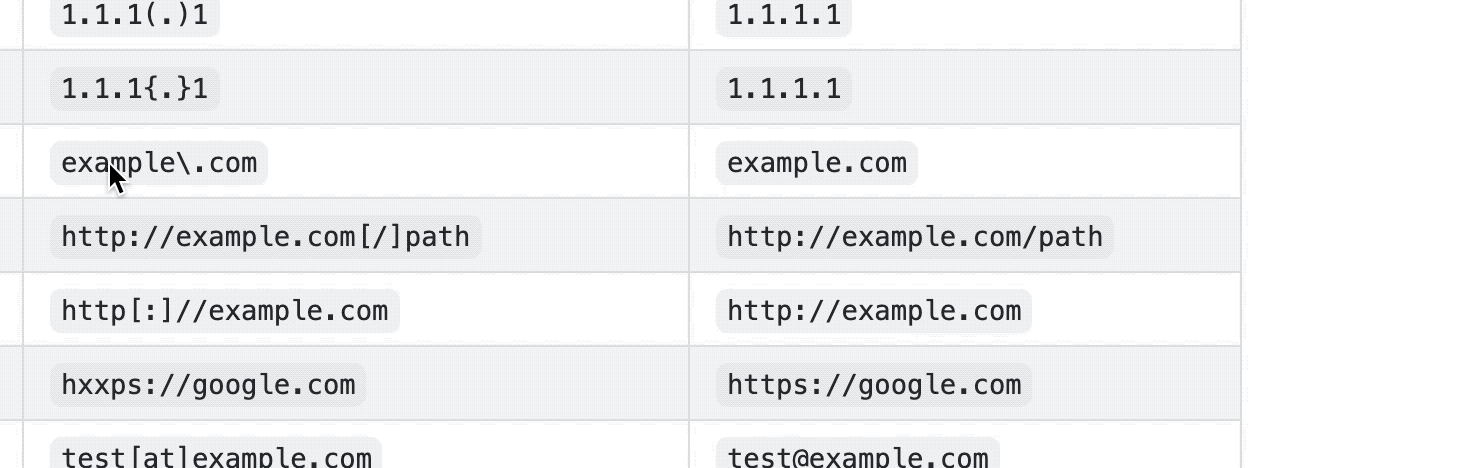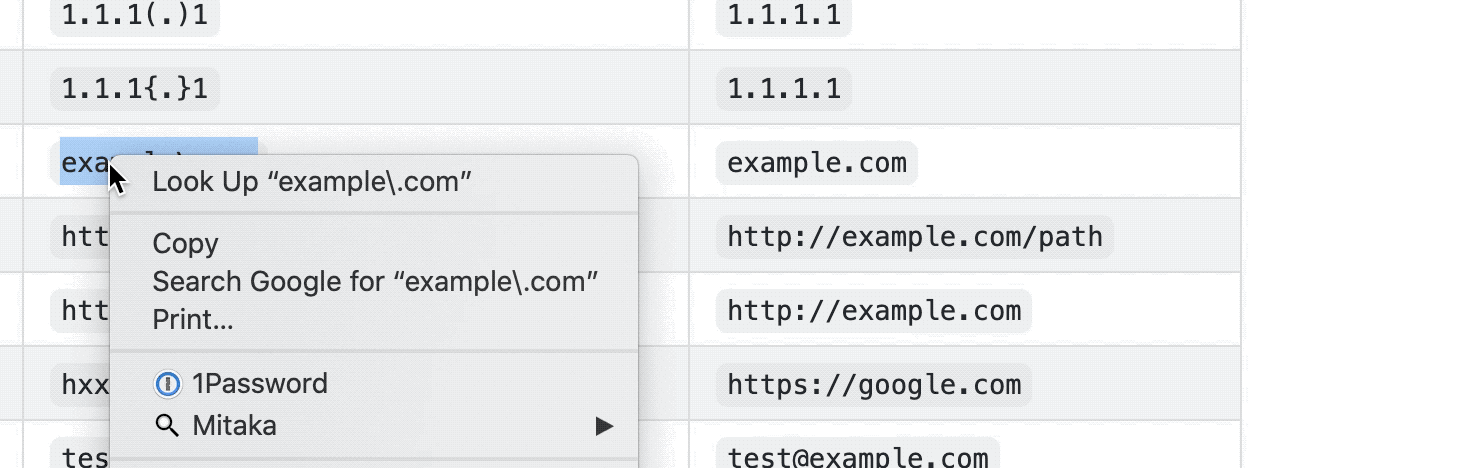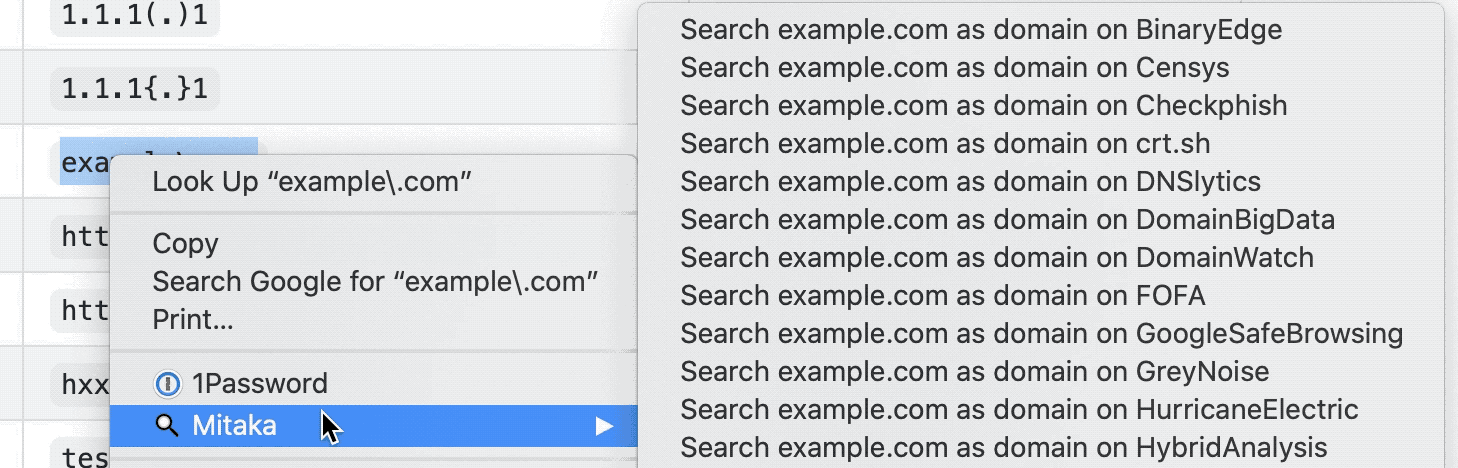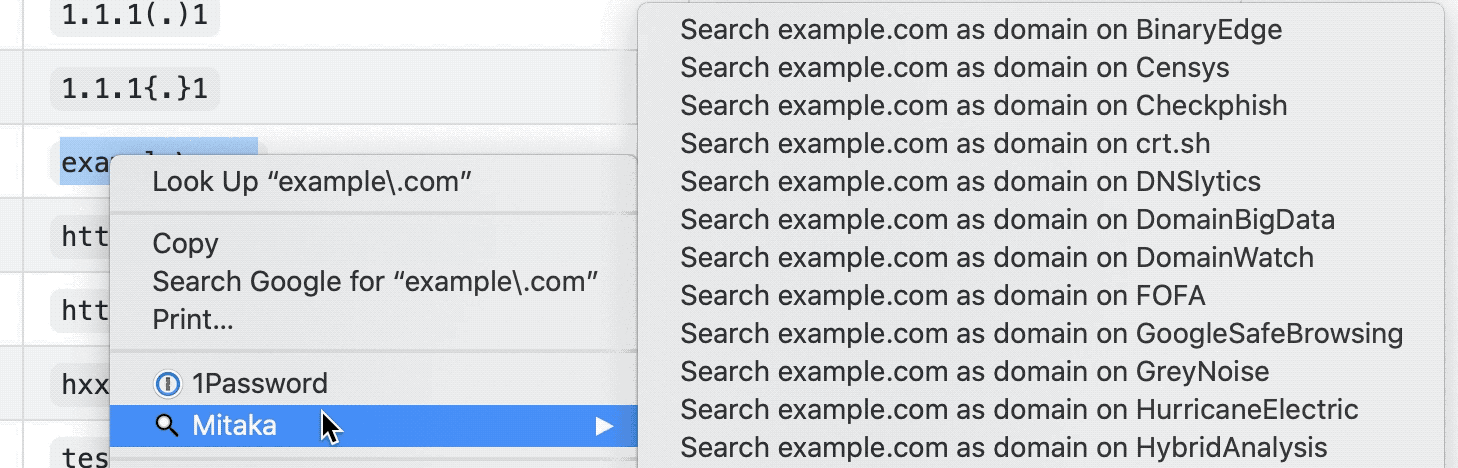 ninoseki/mitaka
Browser extension for OSINT search and IoC analysis. Auto-detects and refangs indicators of compromise, then queries 65+ threat intelligence and…
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT