

yowie
 joda32/yowie
Finds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
defensive-toolsdns-analysisdns-subdomain-enumeration+9
2
joda32/yowieFinds the SaaS services an organisation subscribes to, using only externally observable data. Built for shadow IT discovery.
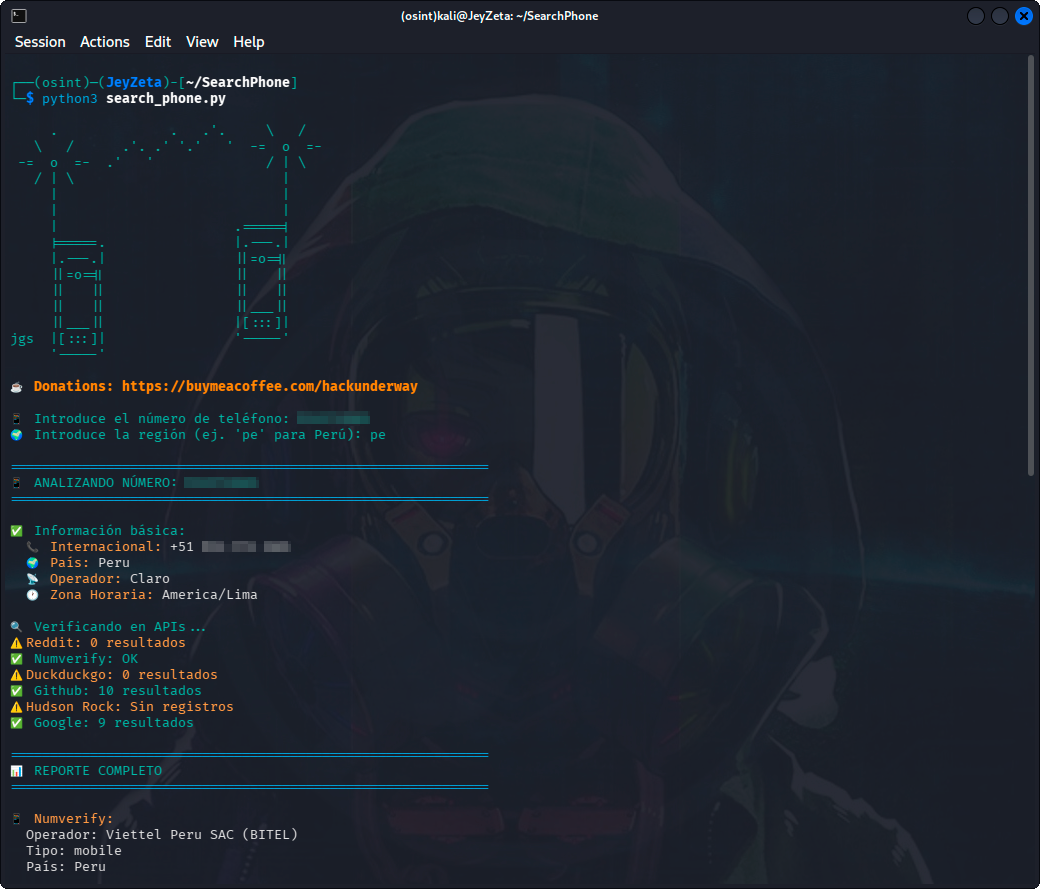 hackunderway/searchphone
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 timborin0/log4j-dork-scanner
A script to search, scrape and scan for Apache Log4j CVE-2021-44228 affected files using Google dorks
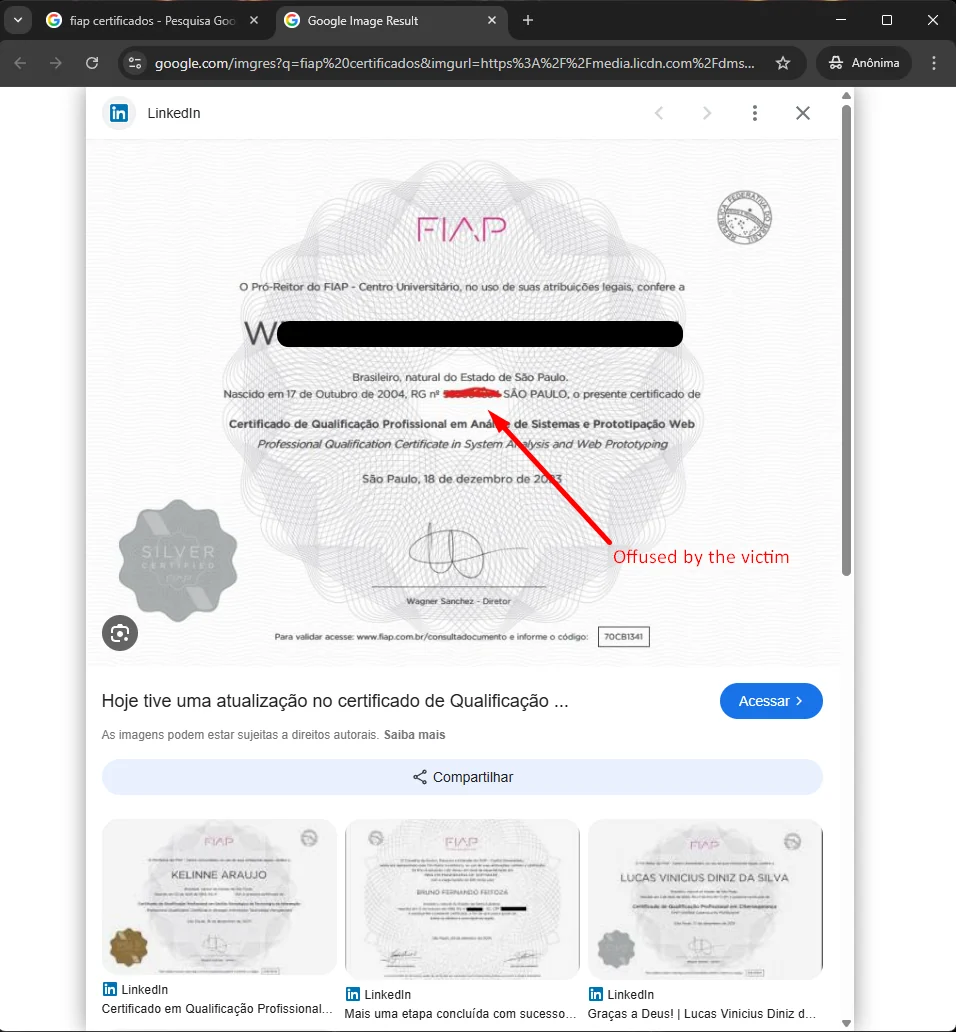 rrespxwnss/cve-2026-36374
Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 soufianetahiri/anxun-isoon
I-SOON/Anxun leak related stuff
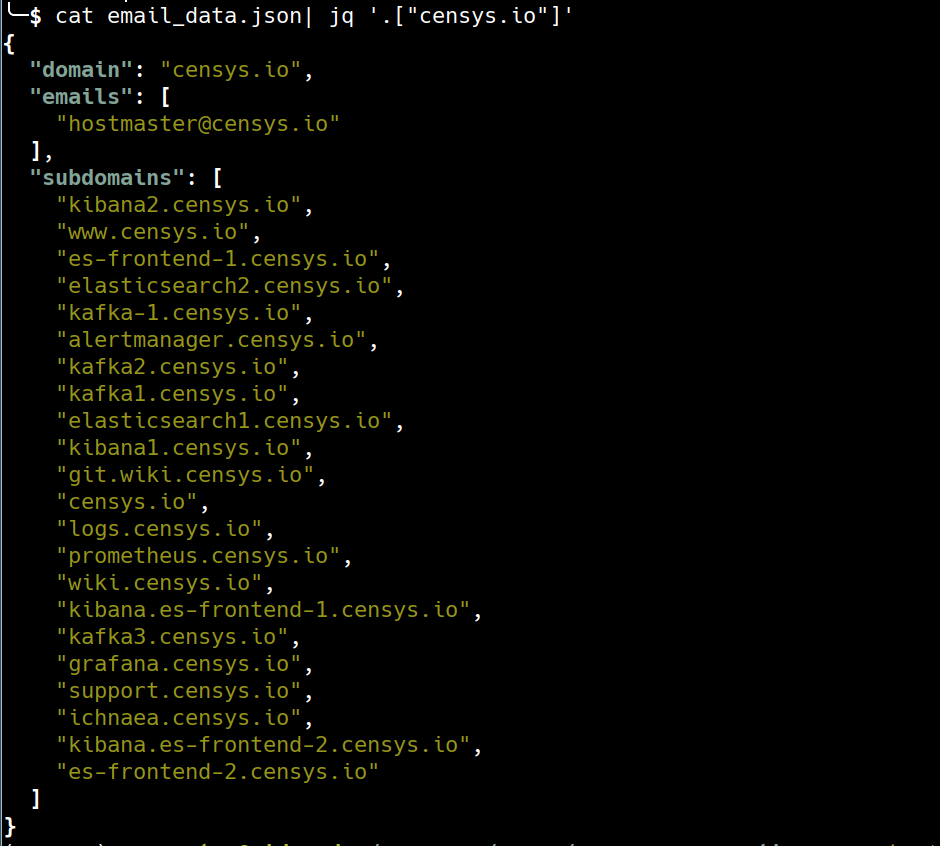 0xbharath/censys-enumeration
A script to extract subdomains/emails for a given domain using SSL/TLS certificate dataset on Censys
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 1an0rmus/tekdefense
Open Development projects for TekDefense
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration
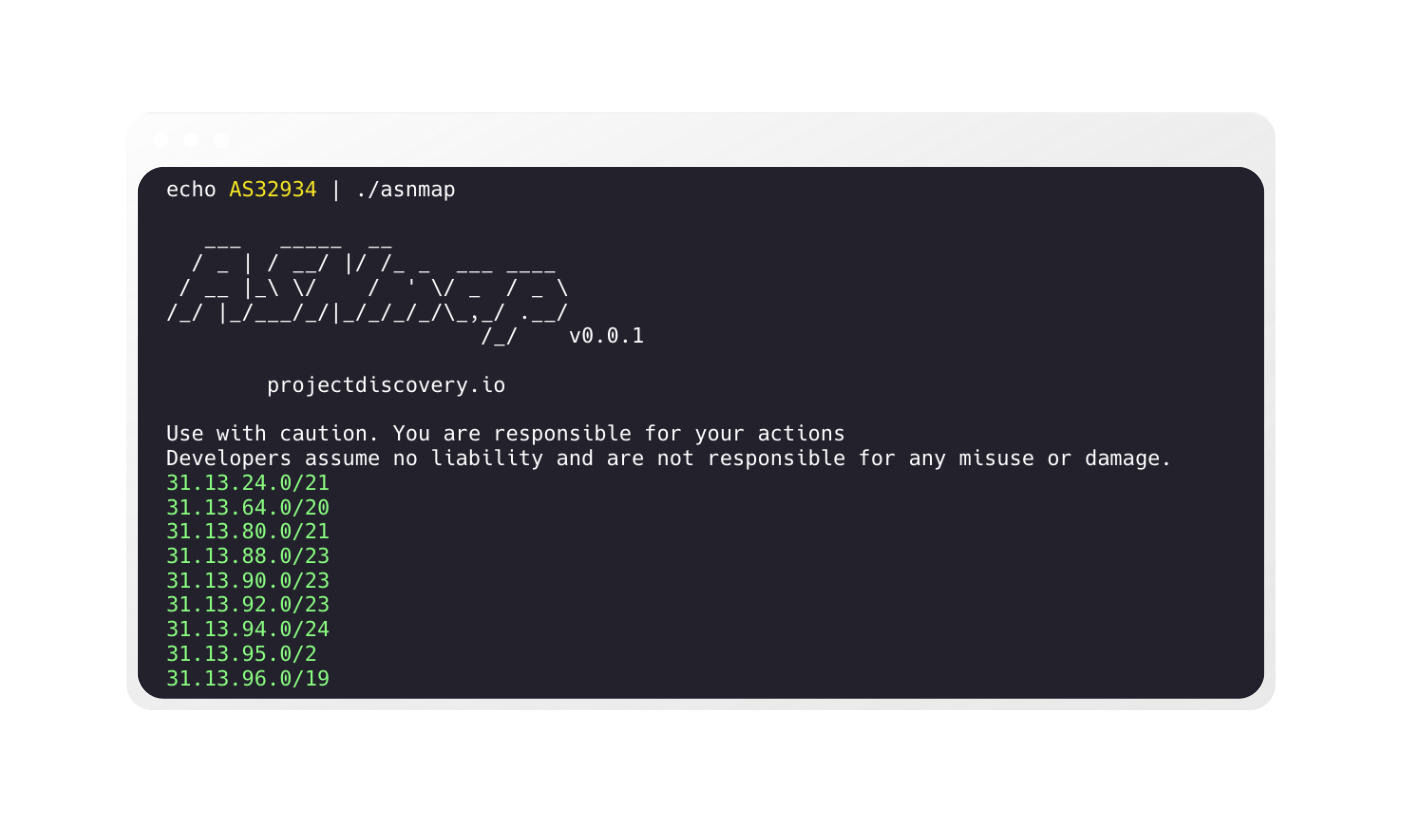 projectdiscovery/asnmap
Go CLI and Library for quickly mapping organization network ranges using ASN information.
 staaldraad/fastfluxanalysis
Scripts to detect Fast-Flux and DGA using DNS query responses
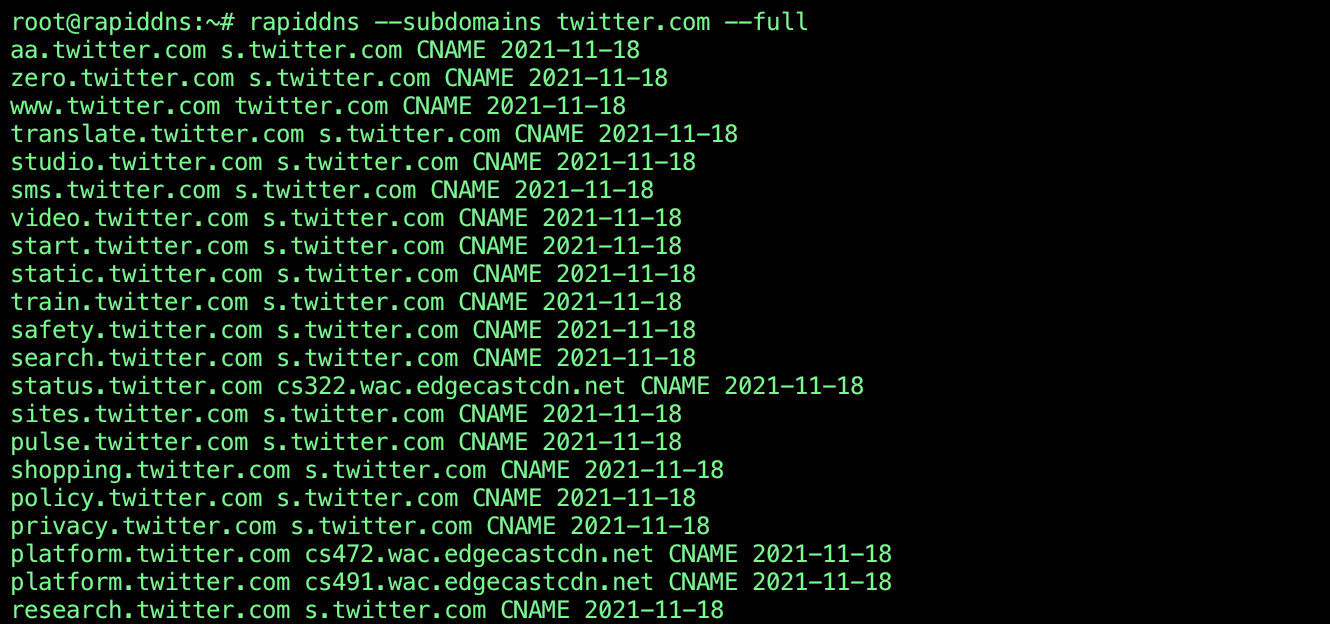 nullt3r/rapiddns
Rapidly enumerate subdomains and domains using rapiddns.io.
 w1ld3r/smbghost_scanner
Advanced scanner for CVE-2020-0796 - SMBv3 RCE