
citrix-2025
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
digital-forensicsforensicsincident-response+2
55
ncsc-nl/citrix-2025Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 yami0x777/belsen_group-et-exploitation-de-la-cve-2022-40684
Analyzes a dark web leak of 15,000+ Fortinet devices compromised via CVE-2022-40684, providing IOCs, impacted versions, and a Python script to…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 lgandx/pcredz
This tool extracts Credit card numbers, NTLM(DCE-RPC, HTTP, SQL, LDAP, etc), Kerberos (AS-REQ Pre-Auth etype 23), HTTP Basic, SNMP, POP, SMTP, FTP,…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 mlgualtieri/ntlmrawunhide
NTLMRawUnhide.py is a Python3 script designed to parse network packet capture files and extract NTLMv2 hashes in a crackable format. The following…
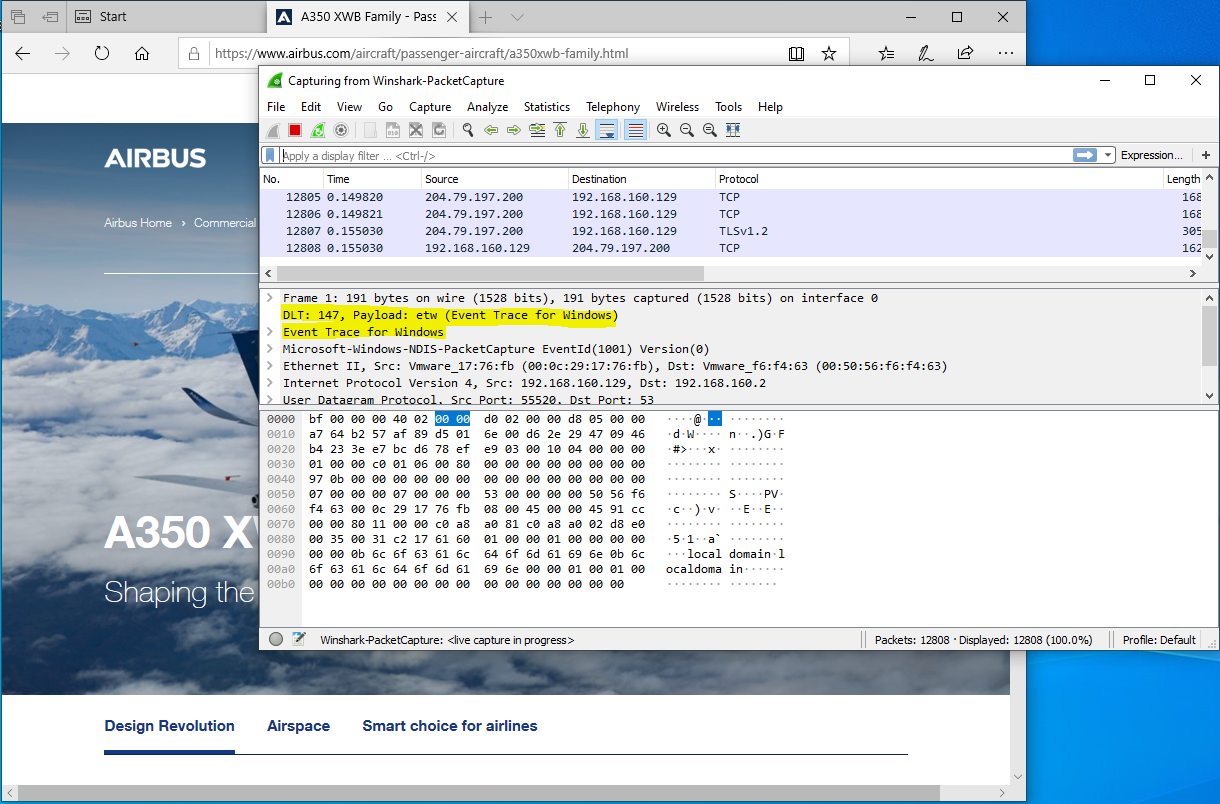 airbus-cert/winshark
A wireshark plugin to instrument ETW
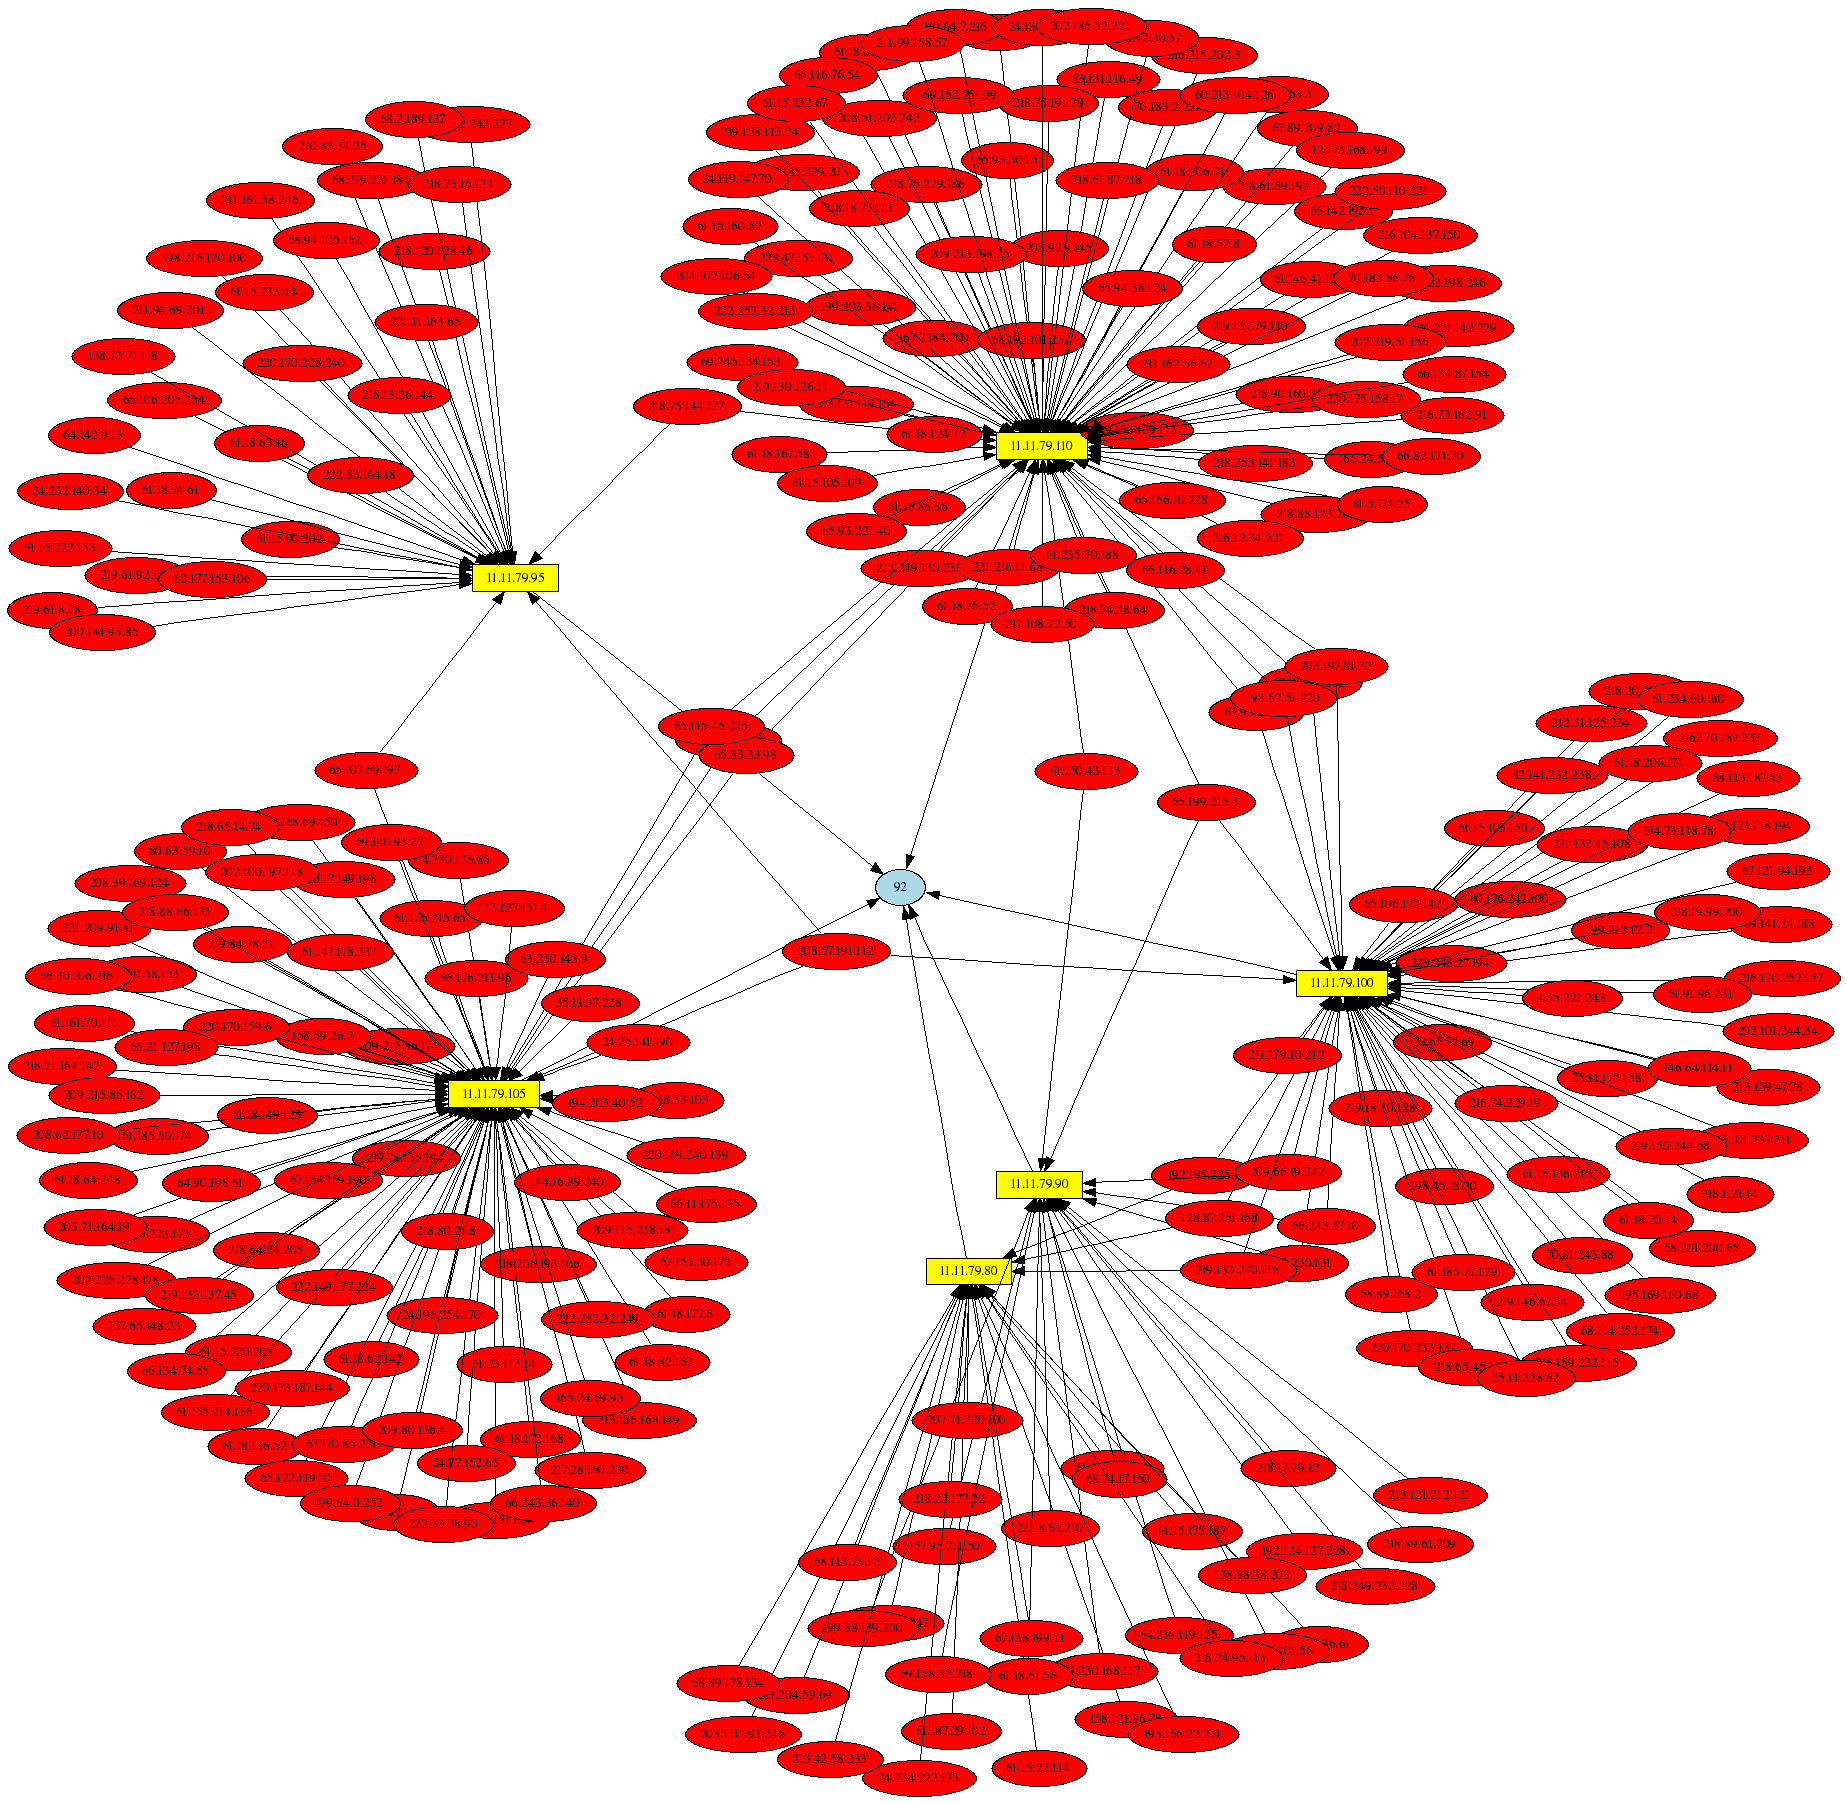 mrash/psad
psad: Intrusion Detection and Log Analysis with iptables
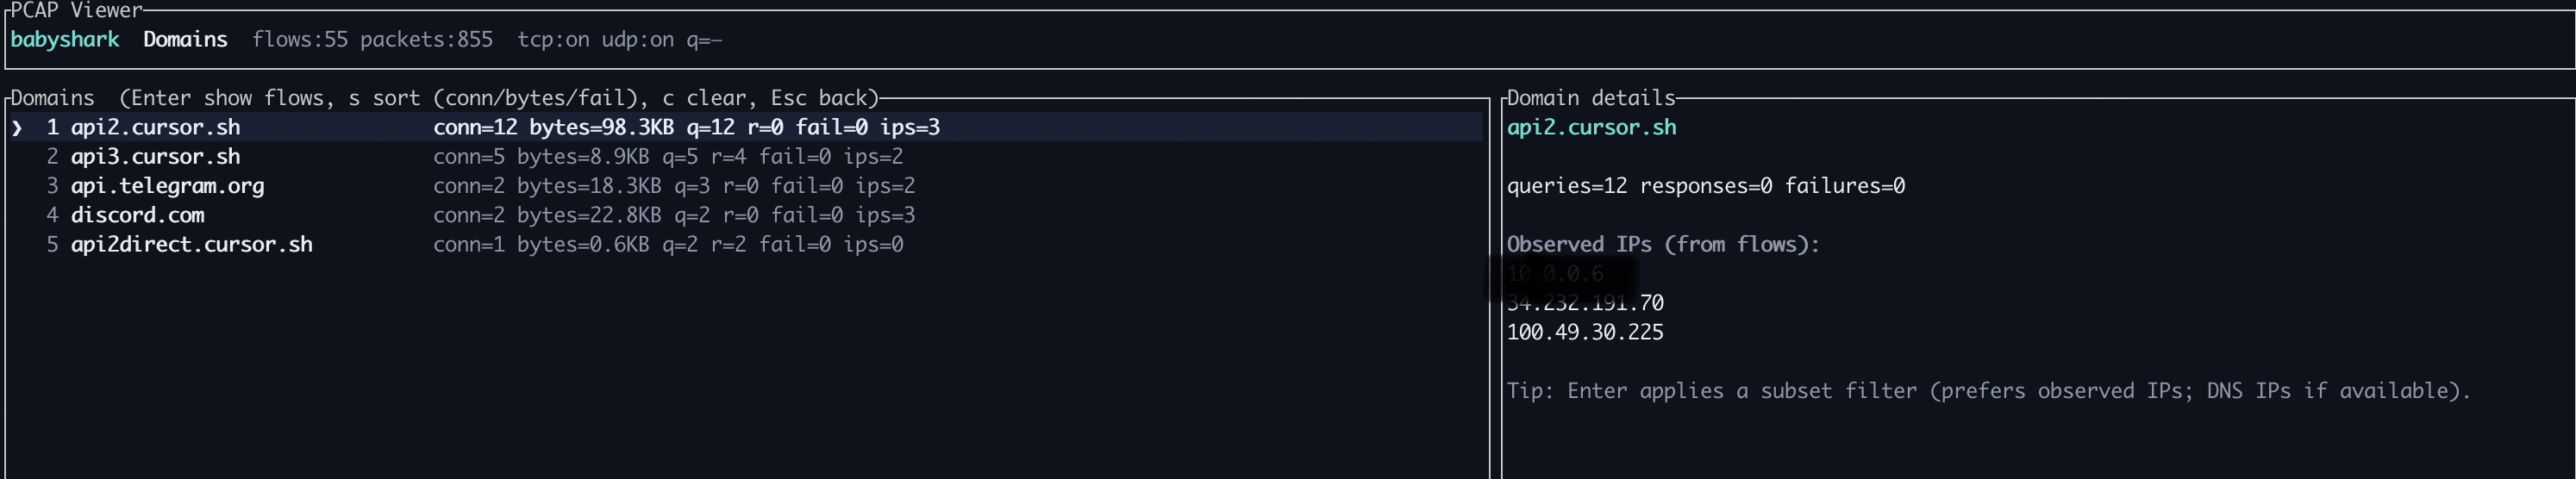 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 mhils/honeyproxy
This project is now part of @mitmproxy.