BIT-EternalBlue-for-macOS_Linux

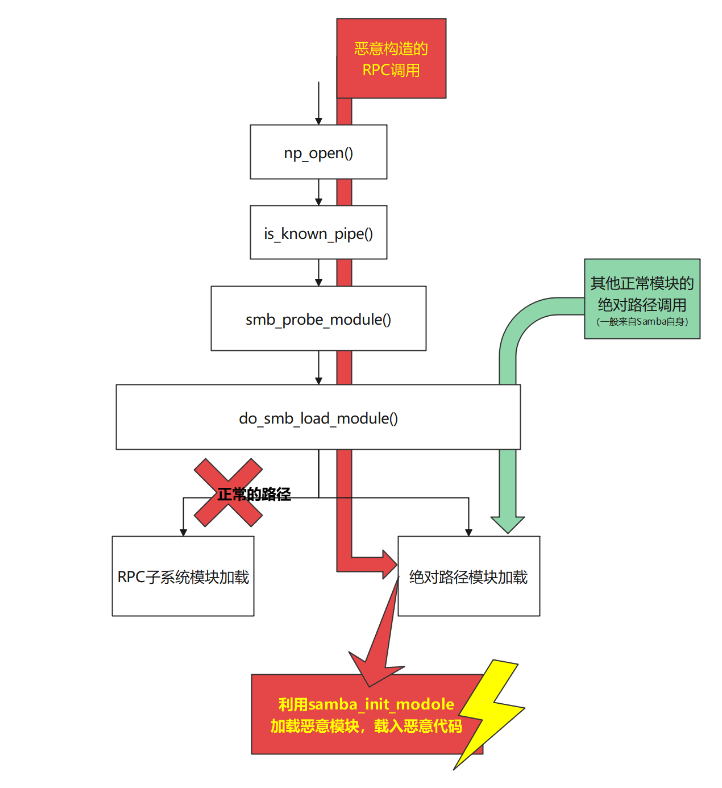
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…

Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…

Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…

Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…

BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide

Python scanner that checks hosts for the OpenSSH regreSSHion vulnerability (CVE-2024-6387)

Check if your provider is blocking you!

CVE-2024-6387 exploit

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

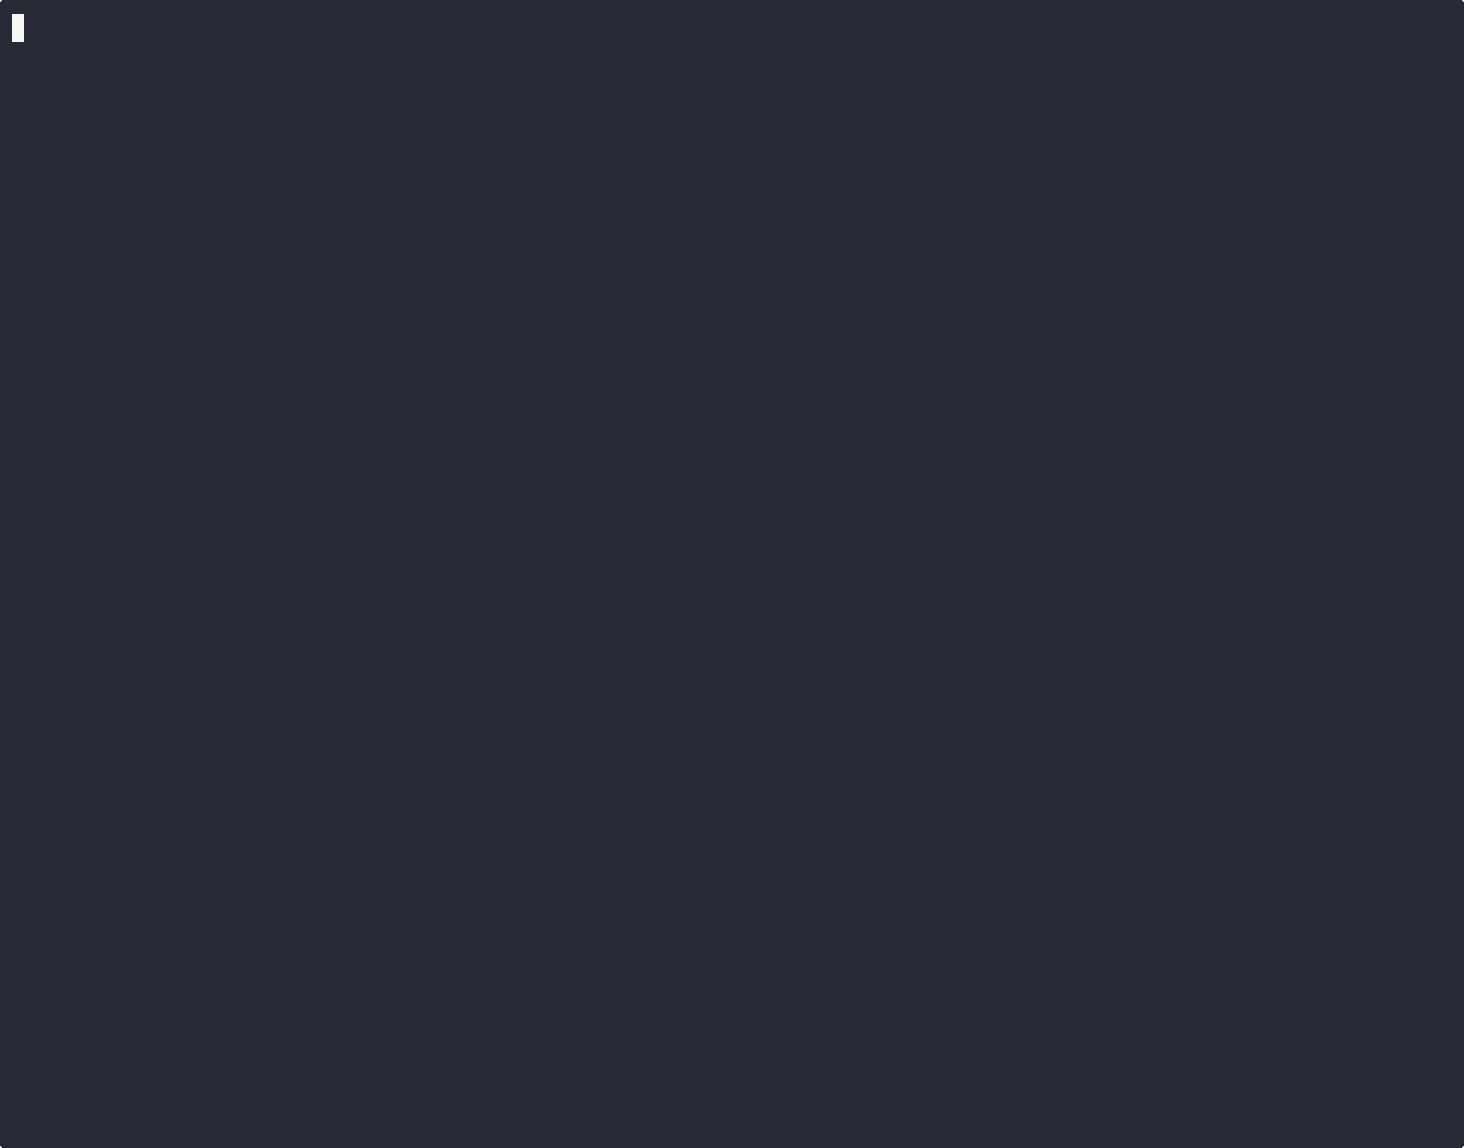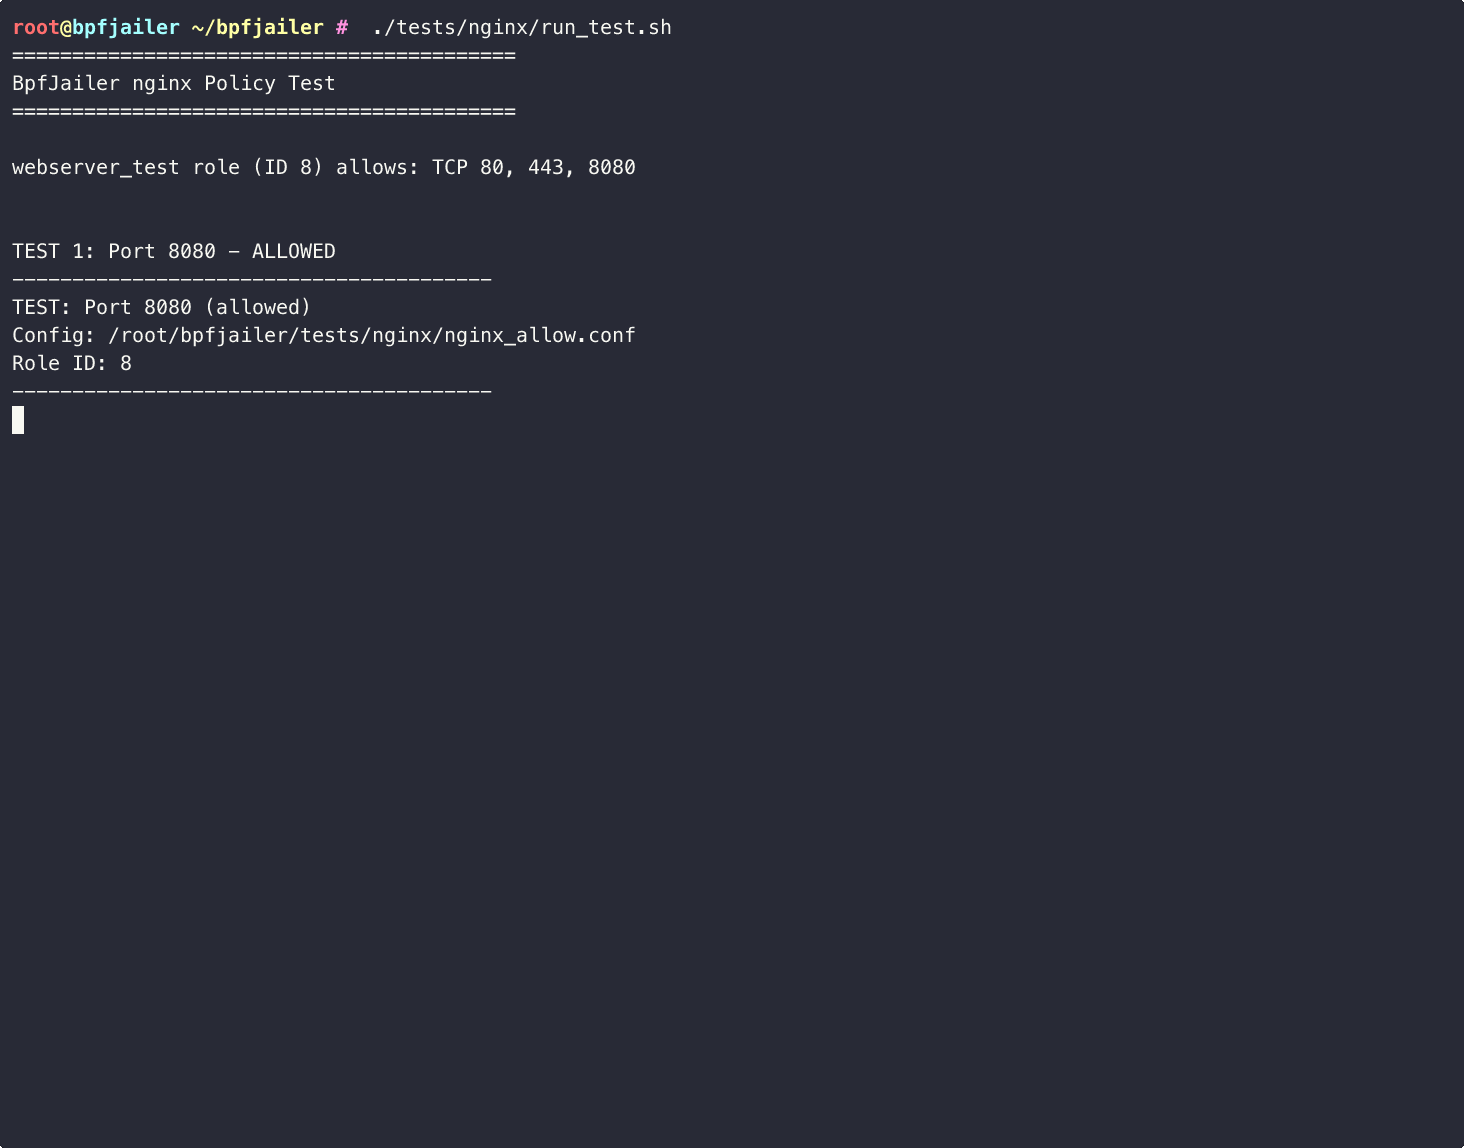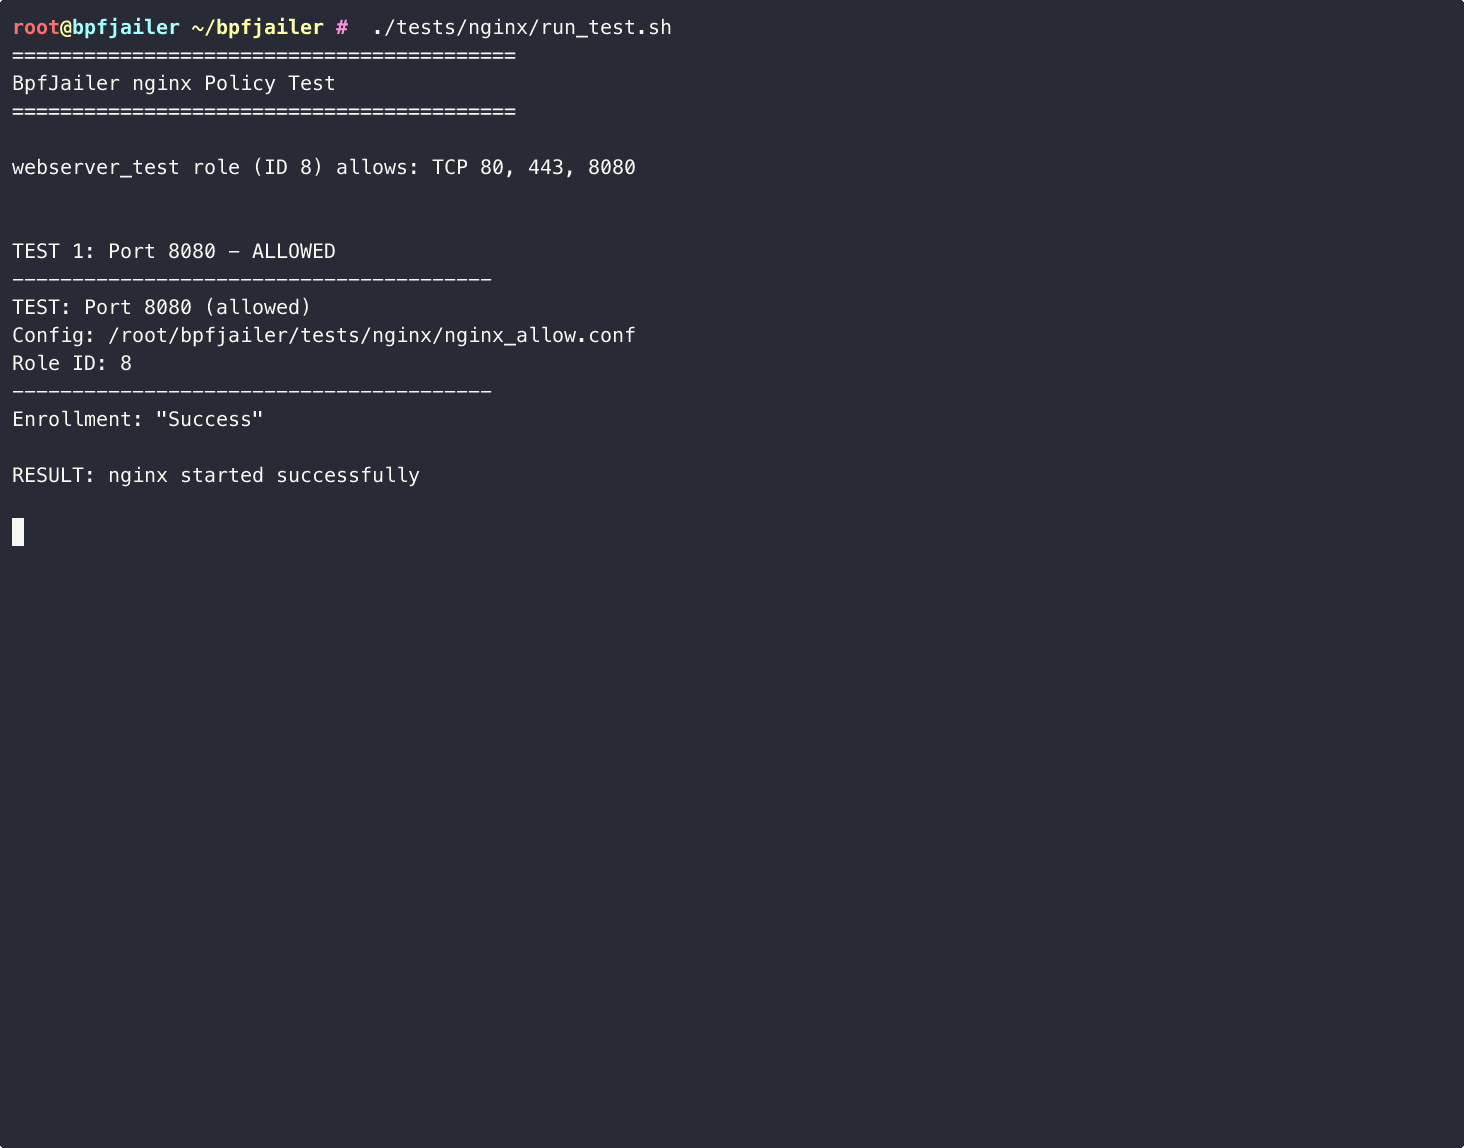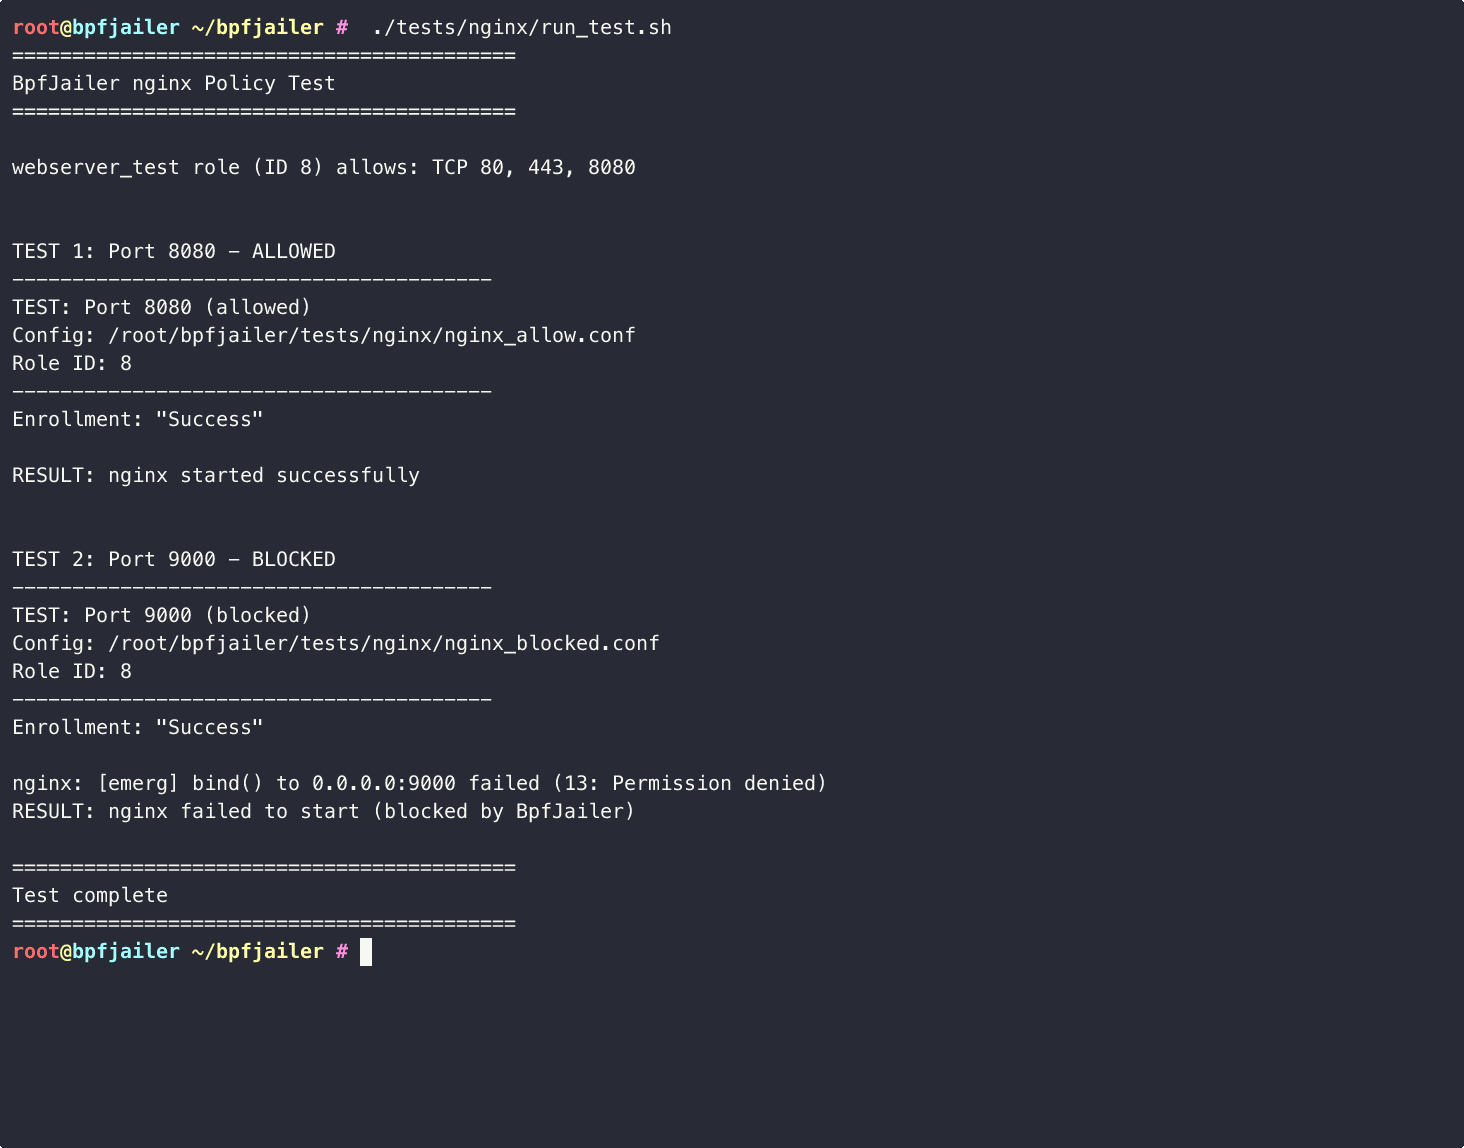
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…

Like Envoy xDS, but for eBPF filters

Docker-based exploit for CVE-2018-10933, a libssh authentication bypass vulnerability, targeting SSH services on port 2222 for penetration testing.

Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.

A simple python tool based on Impacket that tests servers for various known NTLM vulnerabilities

Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network

Low Interaction Mobile Honeypot

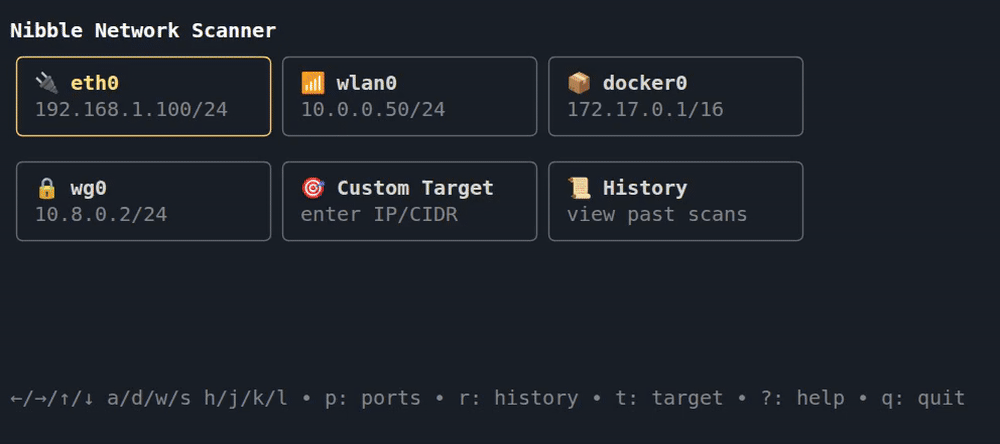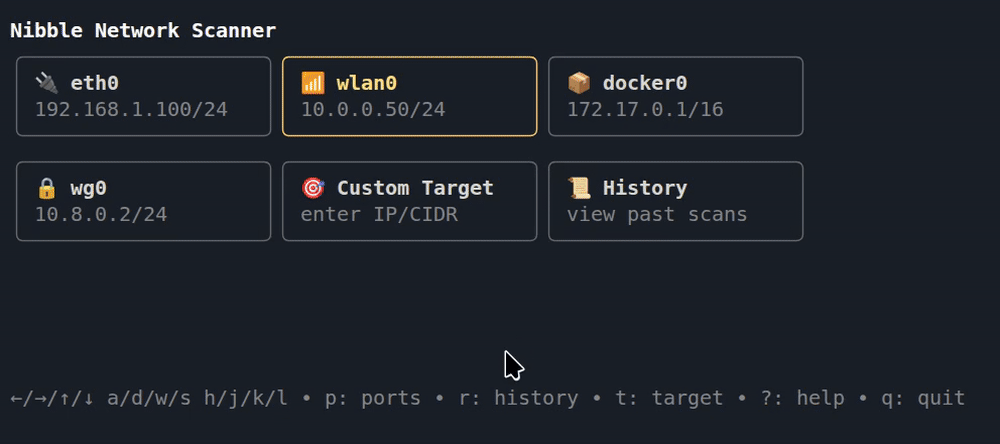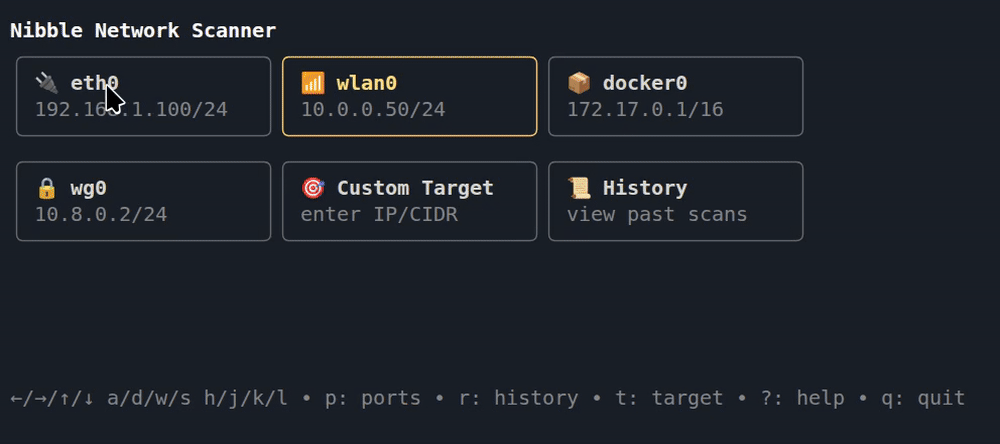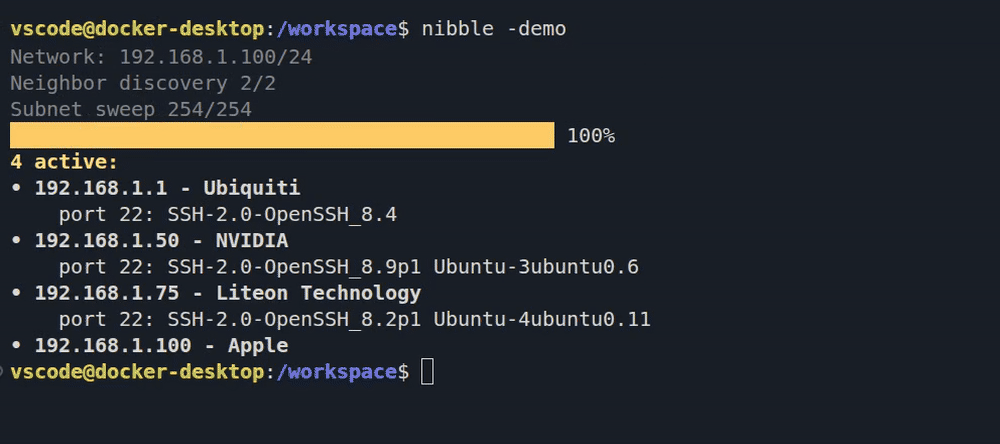
easy to use network scanner, with a clickable tui interface