Multi-VLAN-Enterprise-Network-Vulnerability-Assessment

Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…

Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…

Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…

Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…

Test for SSL heartbeat vulnerability (CVE-2014-0160)

Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).

Qualitative TVRA for multi-VLAN enterprise lab scoring stored XSS and EternalBlue via CVSS v3.0 with ZAP, Nessus, and Wireshark evidence.

This repository contains the scanner component for Greenbone Community Edition.

Easy automated vulnerability scanning, reporting and analysis

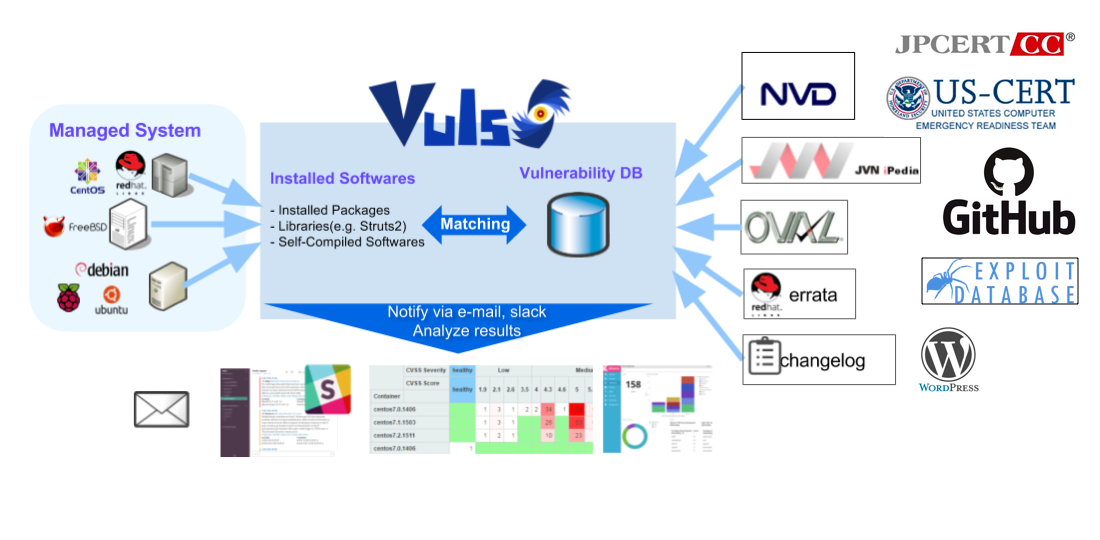
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices

Fast SSL/TLS scanner that discovers supported cipher suites, protocols, and vulnerabilities (Heartbleed, POODLE, CRIME) with certificate chain…

A quick scanner for the CVE-2019-0708 "BlueKeep" vulnerability.

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

This Python script checks for the CVE-2024-6387 vulnerability in OpenSSH servers. It supports multiple IP addresses, URLs, CIDR ranges, and ports.…

Go-based scanner for Apache Tomcat AJP file read/inclusion vulnerability (CVE-2020-1938). Detects and exploits Ghostcat to read arbitrary files or…

Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…

System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…

Deploys a critical patch for F5 BIG-IP iControl REST vulnerability CVE-2026-07219, with validation and deployment tracking for production…

A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…